
rpi-hunter
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
exploitationinformation-gatheringnetwork-security+2
busescanfly/rpi-hunterAuto discover and exploit LAN raspberry pi's
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 riftsandroses/cve-2024-50986
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
 seclabresearchbv/cve-2022-34718-poc
Python-based proof-of-concept exploit for CVE-2022-34718, a remote code execution vulnerability in IPv6 on Windows, using Scapy to craft and send…
 ahhh/reverse_dns_shell
A python reverse shell that uses DNS as the c2 channel
 urbanesec/zackattack
Unveiled at DEF CON 20, NTLM Relaying to ALL THE THINGS!
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 syss-research/outis
outis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…
 jeanback1/cve-2025-2304-exploit
Python exploit script for CVE-2025-2304, a mass assignment privilege escalation in Camaleon CMS. Automates CSRF token parsing and role parameter…
 k3ystr0k3r/cve-2026-24061
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 zux0x3a/dns-black-cat
Multi platform toolkit for an interactive DNS shell commands exfiltration, by using DNS-Cat you will be able to execute system commands in shell mode…
 safarchand/cve-2024-25641
PoC for CVE-2024-25641 Authenticated RCE on Cacti v1.2.26
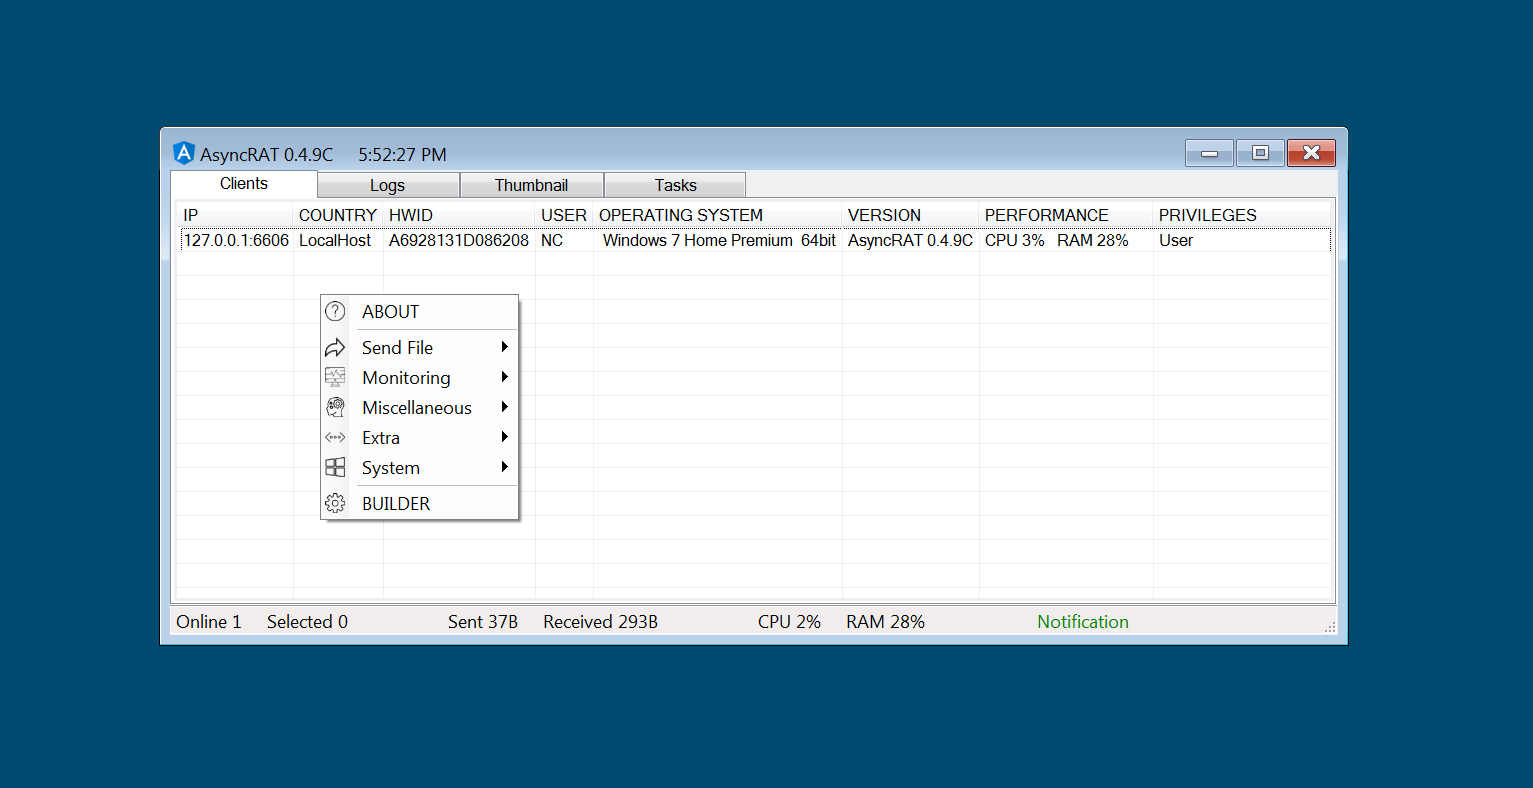 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.