
ezXSS
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
information-gatheringpayload-generationpenetration-testing+2
2.3k
ssl/ezxssBlind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 k4nfr3/cve-2024-9474
Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
 thomaspatzke/log4pot
A honeypot for the Log4Shell vulnerability (CVE-2021-44228).
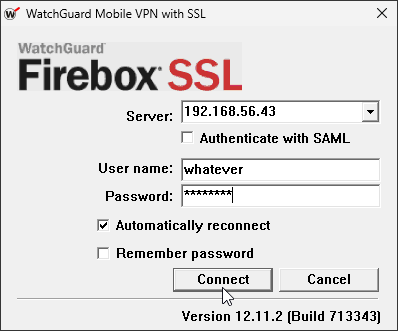 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 ill-deed/crushftp-cve-2024-4040-illdeed
Exploit for CVE-2024-4040 – Authentication bypass in CrushFTP via CrushAuth cookie and AWS-style header spoofing. Stealthy Python PoC with secure…
 0x13-bytezer0/cve-2024-21762
Detects and exploits CVE-2024-21762 pre-authentication RCE in FortiGate SSL VPN, featuring baseline validation, automatic exploitation, ROP…
 w3bw/cve-2024-27956-rce-file-package
Exploit scripts and scanner for CVE-2024-27956, a WordPress plugin vulnerability, including a modified exploit with SSL verification bypass.
 abrewer251/cve-2024-21762_fortinet_poc
Proof-of-concept scanner targeting CVE-2024-21762 in FortiOS SSL VPN’s /remote/hostcheck_validate endpoint with reverse shell payload delivery.
 ssl/scan4log4j
Python script that sends CVE-2021-44228 log4j payload requests to url list
 daboquan/cve-2020-14645
Java-based exploit for CVE-2020-14645 targeting Oracle WebLogic T3 protocol with JNDI injection for remote code execution.