

xssearch
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
crawlerinformation-gatheringpayload-generation+9
6
affolter-engineering/xssearchRust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 urbanesec/zackattack
Unveiled at DEF CON 20, NTLM Relaying to ALL THE THINGS!
 izzz0/cve-2023-27372-poc
Python proof-of-concept for detecting CVE-2023-27372 in SPIP CMS. Scans single or multiple URLs for the vulnerability and outputs results to terminal…
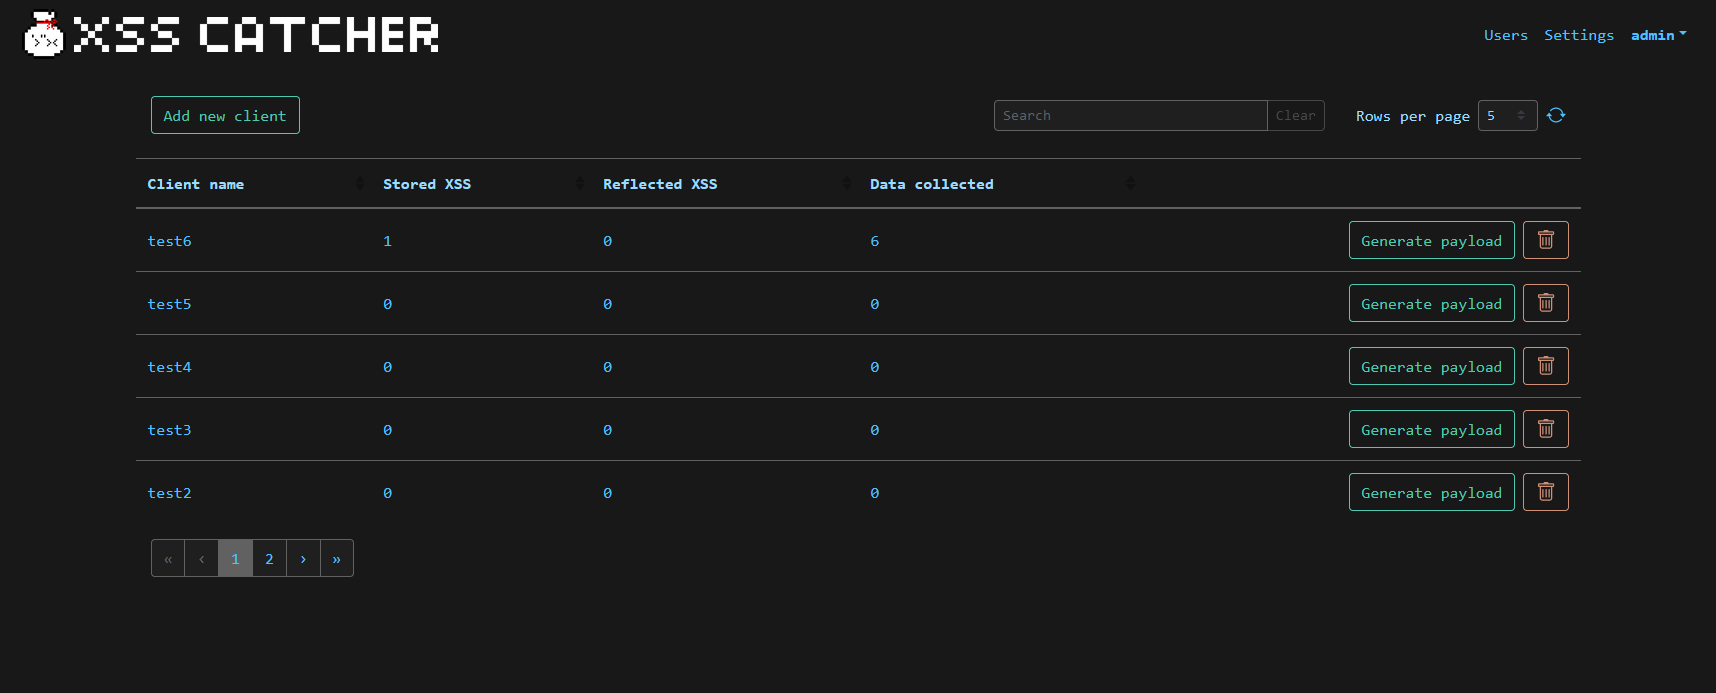 daxakahackerman/xss-catcher
A blind XSS detection and XSS data capture framework
 ethicalhackingplayground/wordlistgen
Generates target specific word lists for Fuzzing with fuff
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
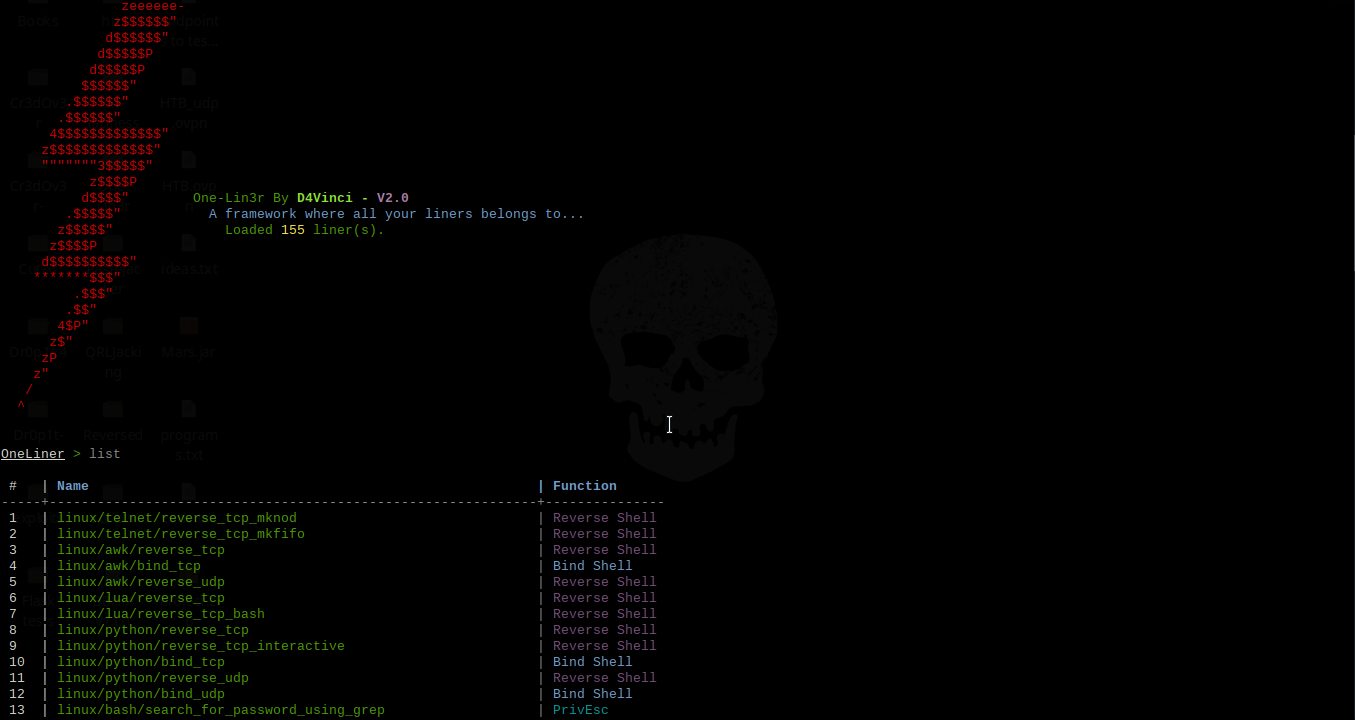 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 kljunowsky/cve-2022-42889-text4shell
Proof-of-concept exploit for CVE-2022-42889 (Text4Shell) in Apache Commons Text, with manual and mass exploitation scripts using script, URL, and DNS…
 wireghoul/htshells
Self contained htaccess shells and attacks
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 nullarray/roothelper
A Bash script that downloads and unzips scripts that will aid with privilege escalation on a Linux system.