
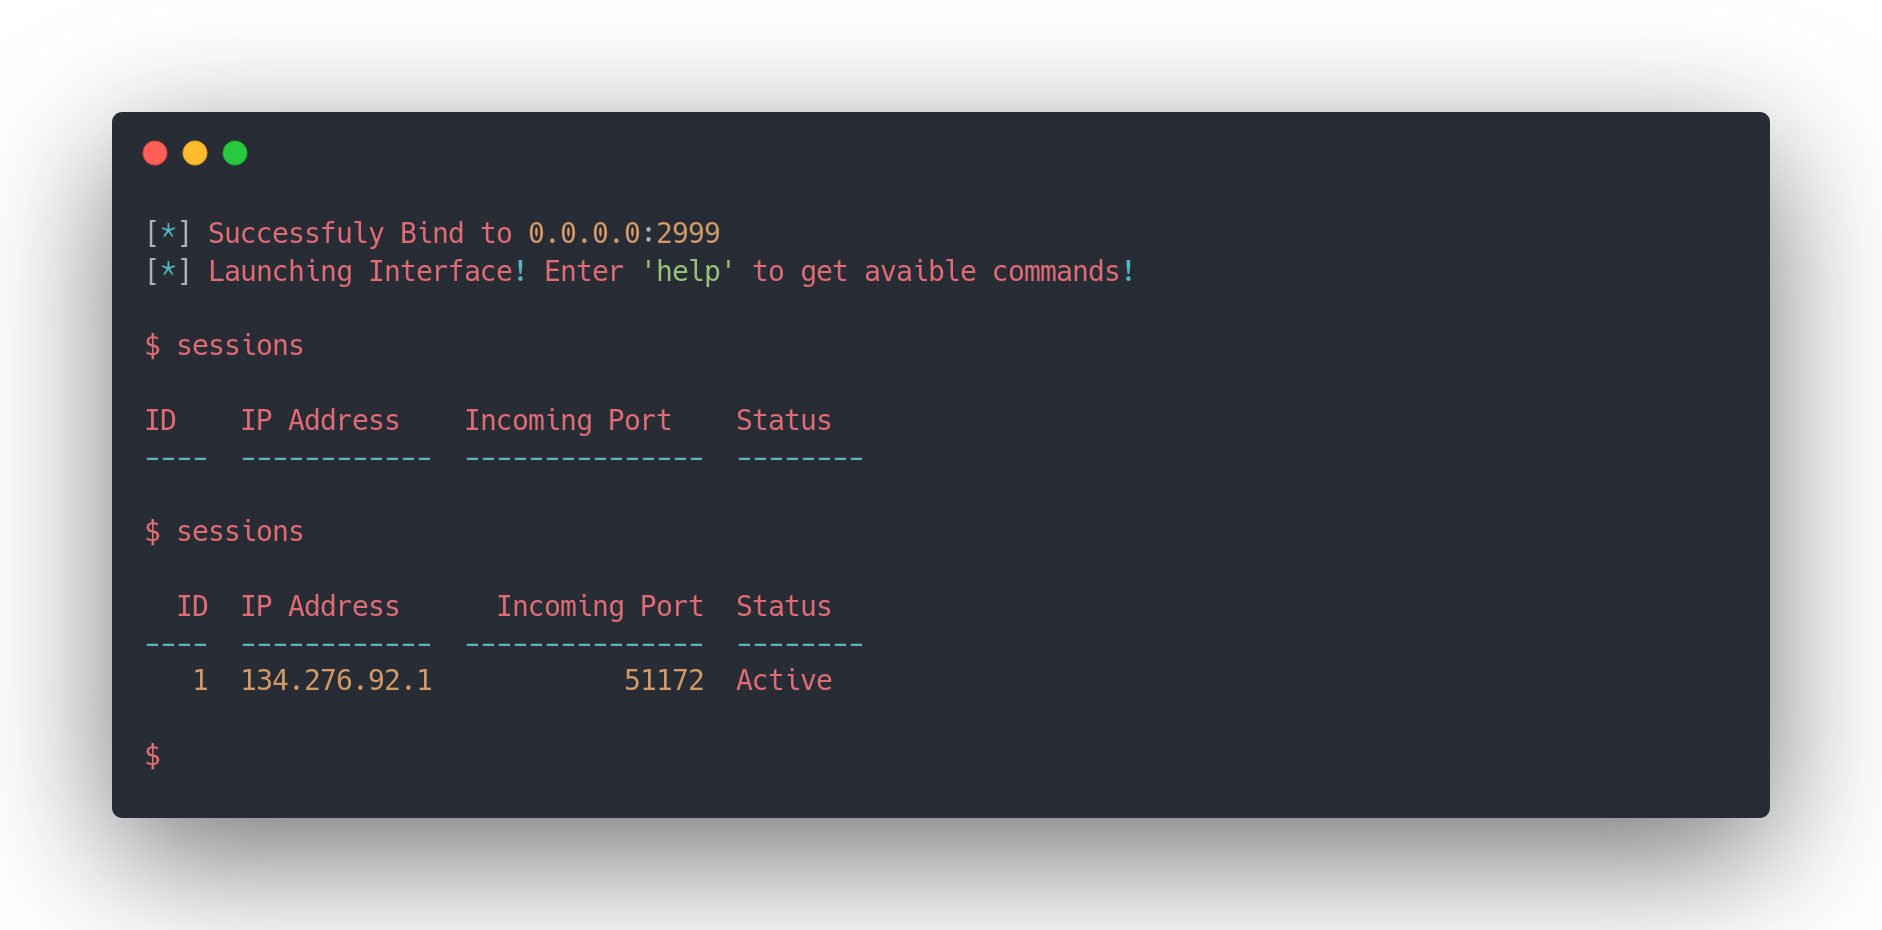
SillyRAT
 hash3lizer/sillyrat
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️
command-and-controlpayload-generationpost-exploitation+1
9433 years ago
hash3lizer/sillyratA Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
 calebstewart/cve-2021-1675
Pure PowerShell implementation of CVE-2021-1675 Print Spooler Local Privilege Escalation (PrintNightmare)
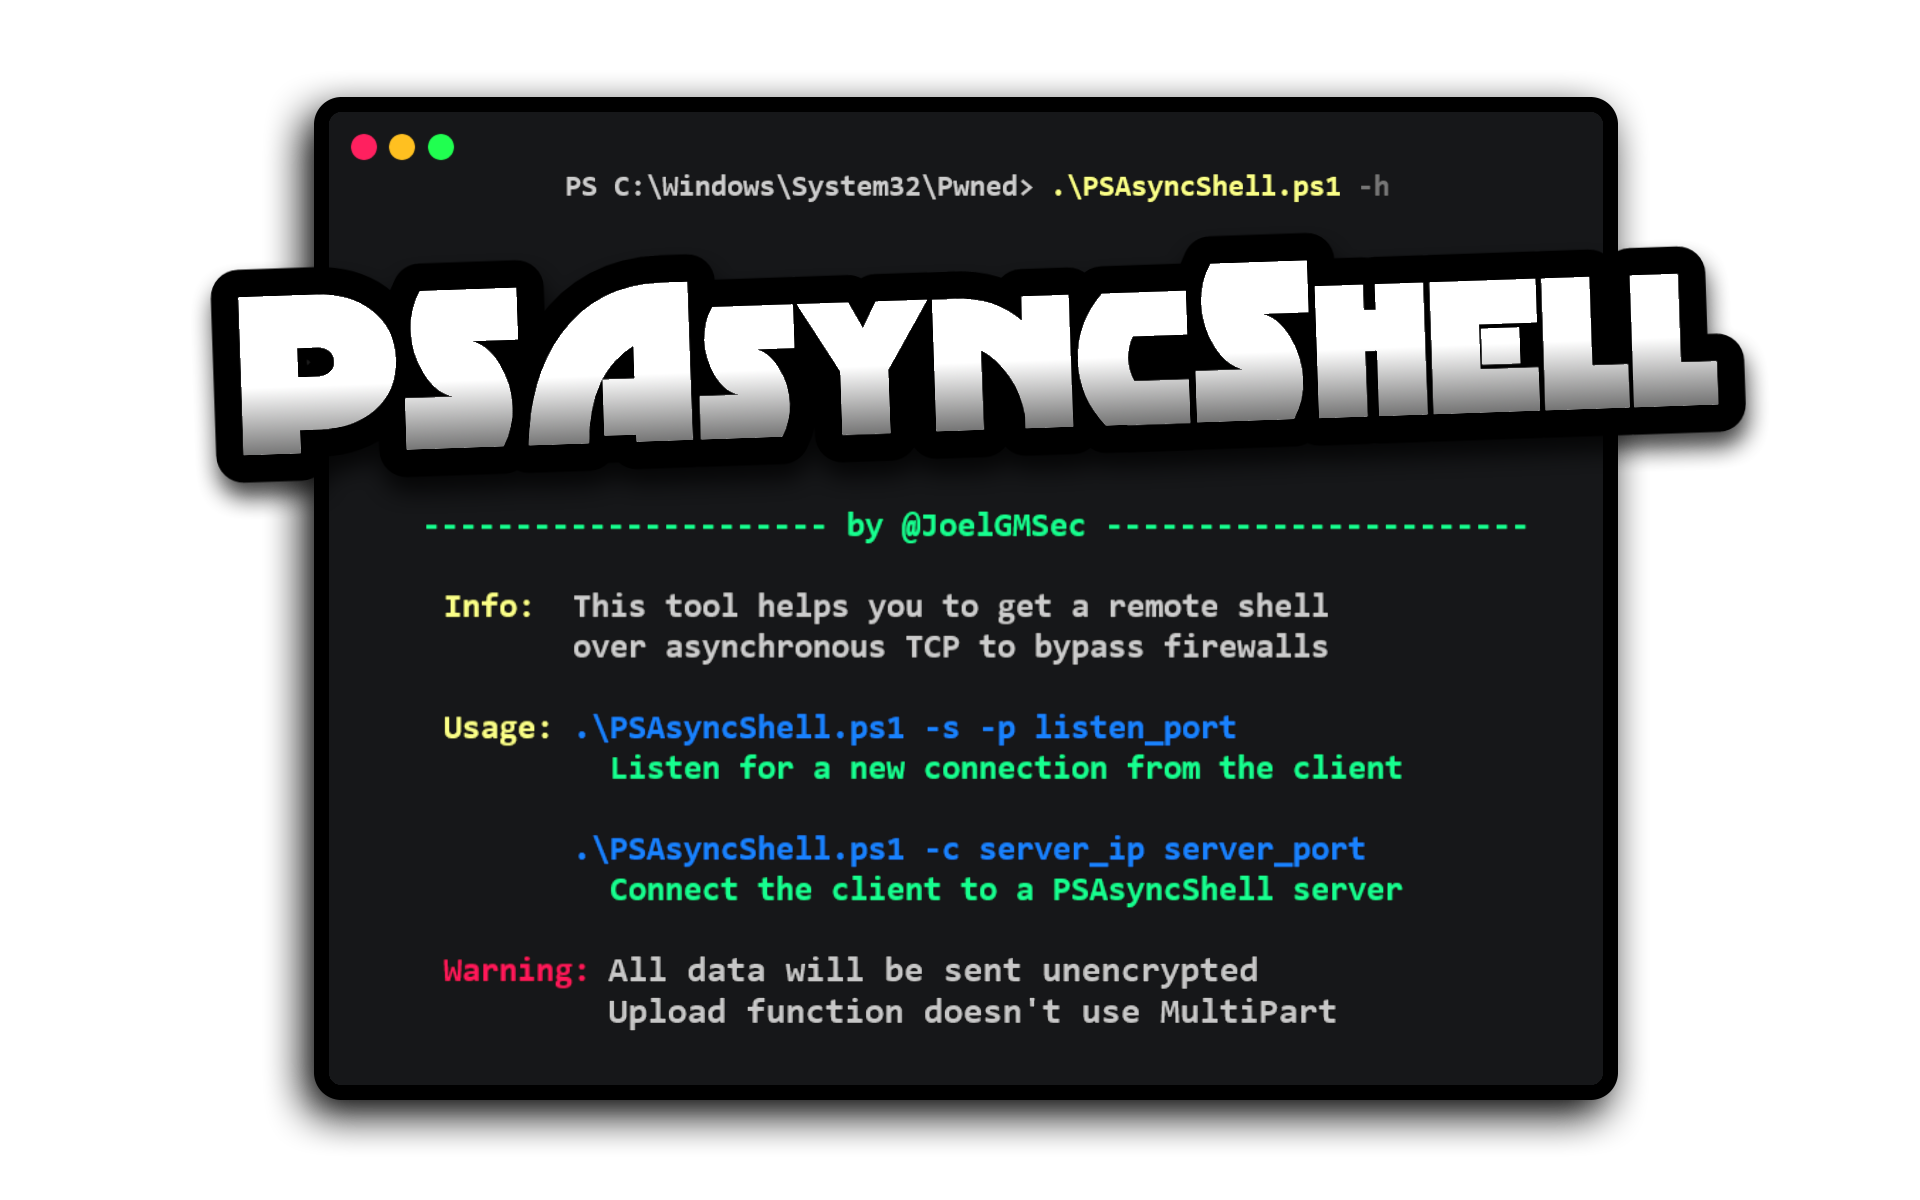 joelgmsec/psasyncshell
Asynchronous TCP reverse shell in pure PowerShell that bypasses firewalls via non-blocking I/O, with command history, file upload/download, and…
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
 alexandre-lavoie/python-log4rce
An All-In-One Pure Python PoC for CVE-2021-44228
 abady0x1/cve-2021-32819
SquirrellyJS mixes pure template data with engine configuration options through the Express render API. By overwriting internal configuration…
 dotpy-hax/log4py
pythonic pure python RCE exploit for CVE-2021-44228 log4shell
 lavirudilshan/cve-2023-5360-exploit-with-native-libraries
CVE-2023-5360 PoC: Unauthenticated arbitrary file upload leading to RCE in Royal Elementor Addons (≤ 1.3.78), written in pure Python.