
GreeDoS_V2
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
exploitationnetwork-securitypayload-generation+4
188 months ago
mrechofi/greedos_v2A Multi-vector DoS tool for Cybersecurity Red Teamers' .
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 nathanlopez/stitch
Python Remote Administration Tool (RAT)
 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 pimps/cve-2017-1000486
Primefaces <= 5.2.21, 5.3.8 or 6.0 - Remote Code Execution Exploit
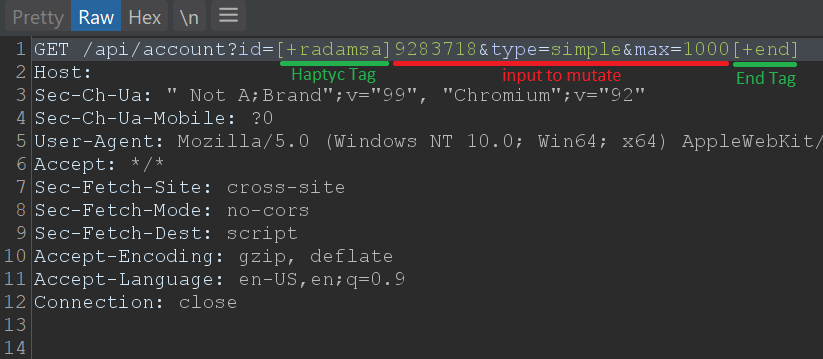 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 jasmoon99/embedded-pdf
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 badb33f/apache-log4j-poc
Proof of Concept of apache log4j LDAP lookup vulnerability. CVE-2021-44228
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 aron-tn/mega-bot
[NEW] : Mega Bot ☣ Scanner & Auto Exploiter
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…
 omarothmann/embedded-backdoor-connection
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 wyatu/cve-2018-20250
exp for https://research.checkpoint.com/extracting-code-execution-from-winrar