

SSTImap
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
code-analysiscommand-and-controldynamic-code-analysis+6
vladko312/sstimapAutomatic SSTI detection tool with interactive interface
 michaelweber/macrome
Excel Macro Document Reader/Writer for Red Teamers & Analysts
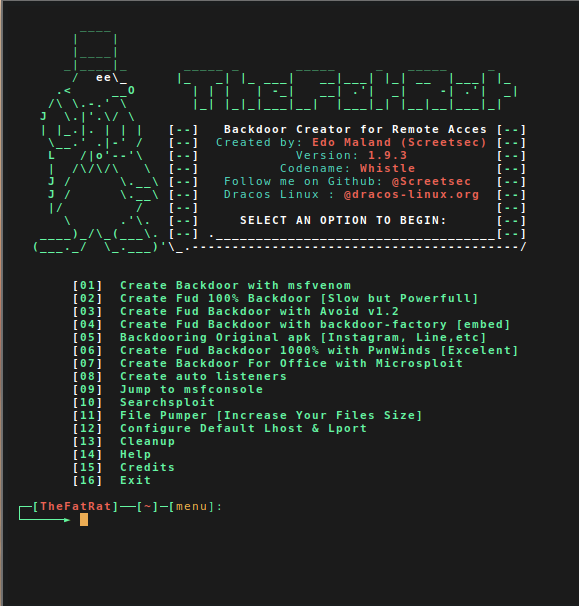 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 jas502n/cve-2019-11581
Atlassian JIRA Template injection vulnerability RCE
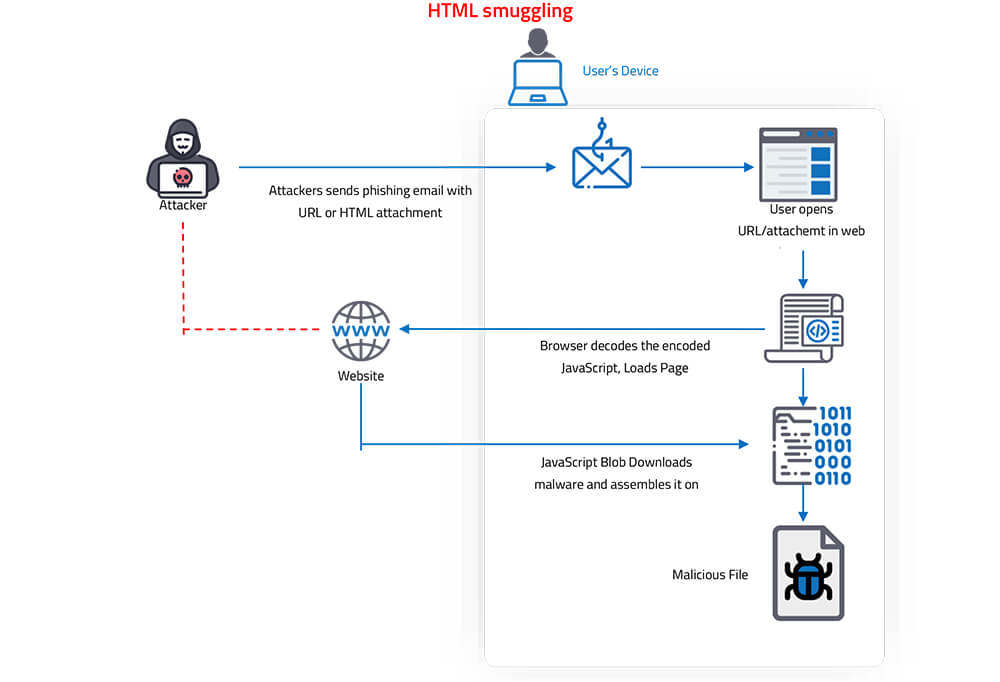 de3vil/htmlsmuggling
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 rippsec/cve-2025-24893-xwiki-ssti-rce
CVE-2025-24893 – XWiki SSTI unauthenticated RCE exploit (HackTheBox CTF)
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
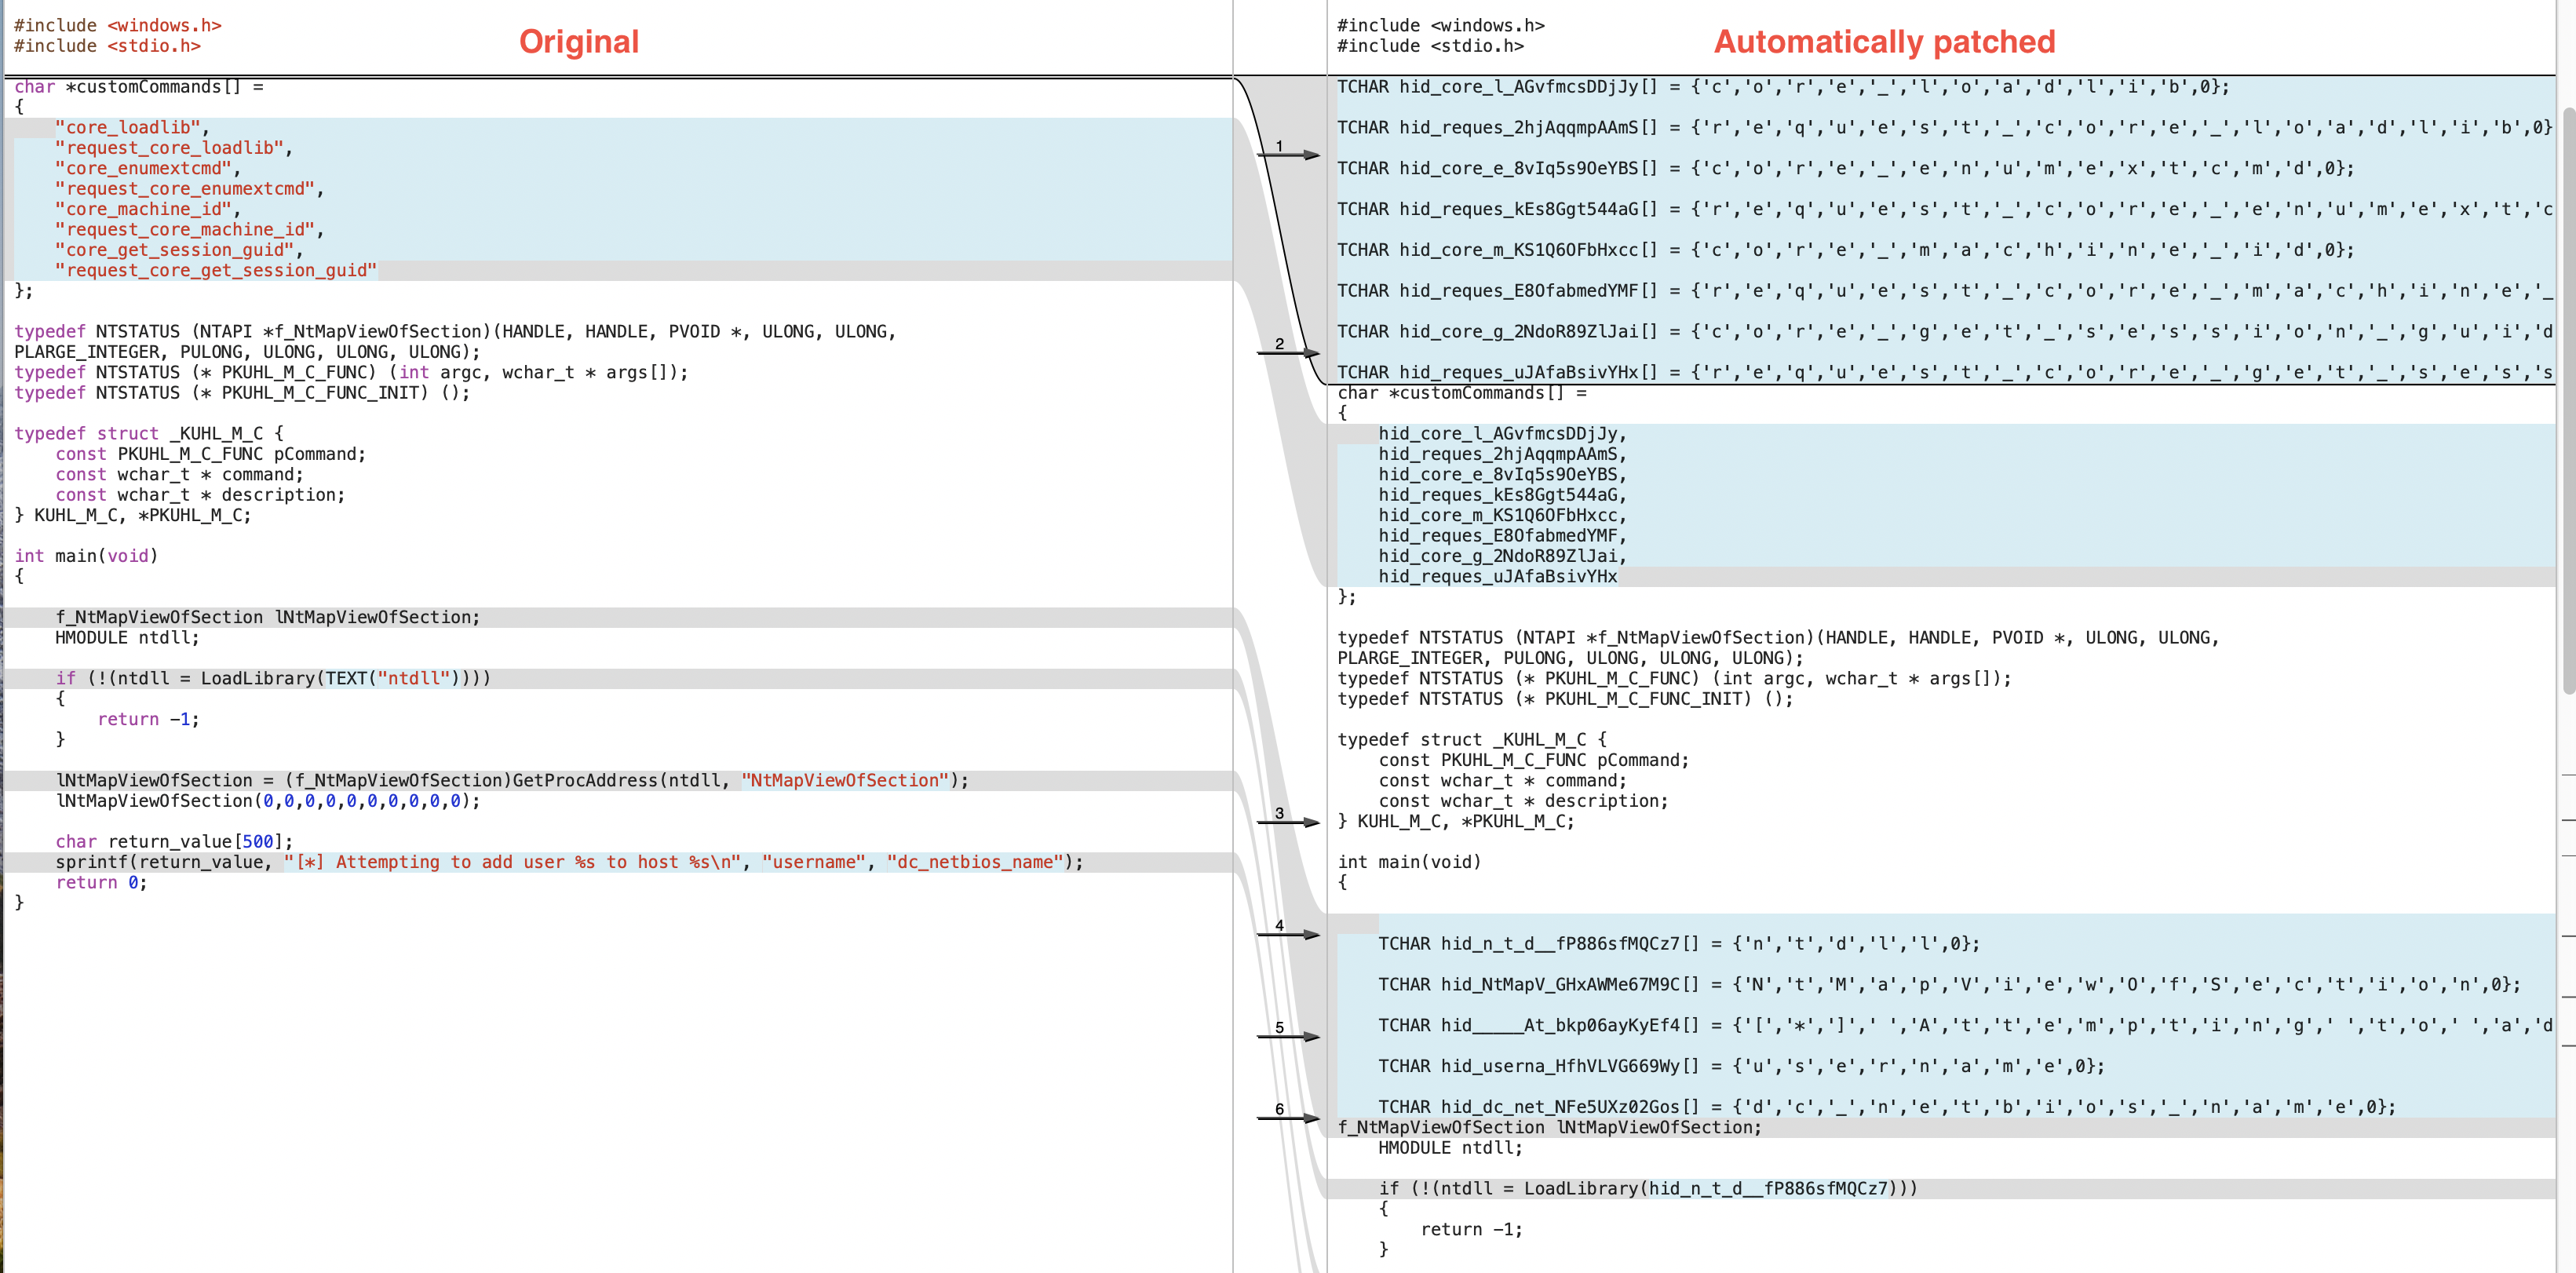 scrt/avcleaner
C/C++ source obfuscator for antivirus bypass
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
 mario1234/js-driveby-download-cve-2006-4777
malware del lado del cliente de explotacion de vulnerabilidad de internet explorer 6.0 SP1 en windows xp SP2. No requiere de consentimiento por parte…
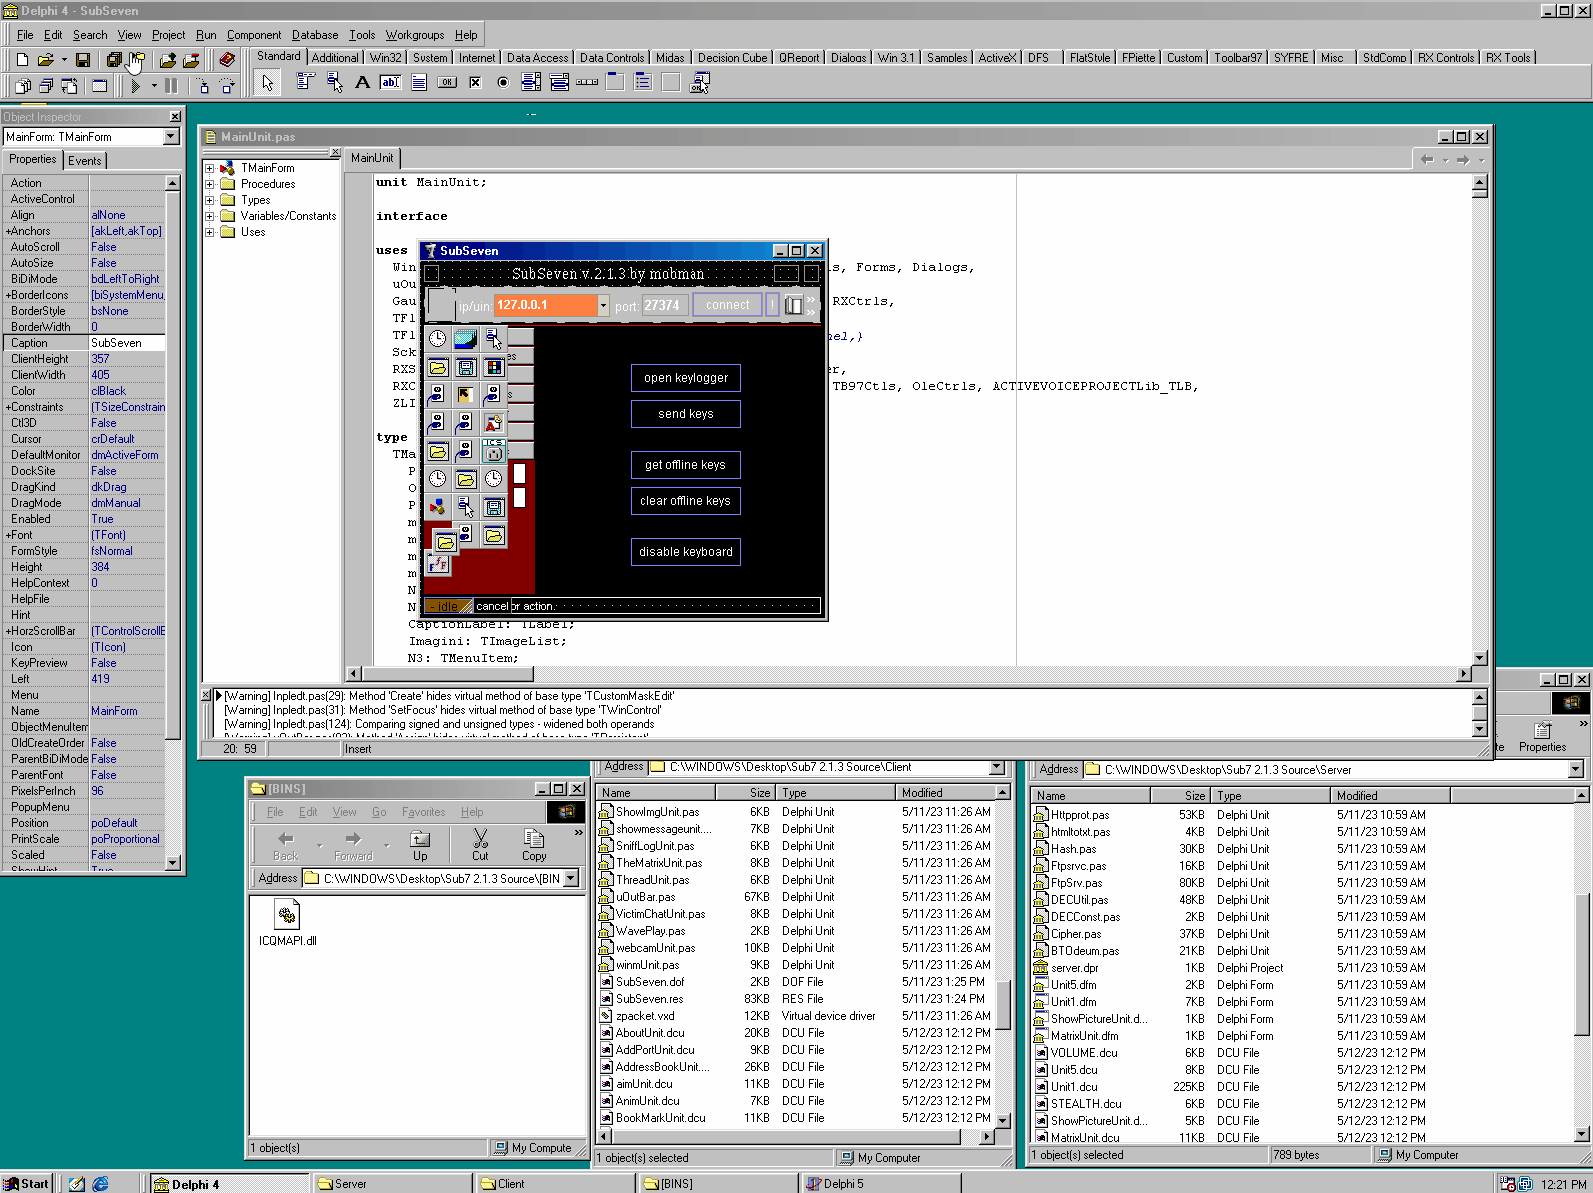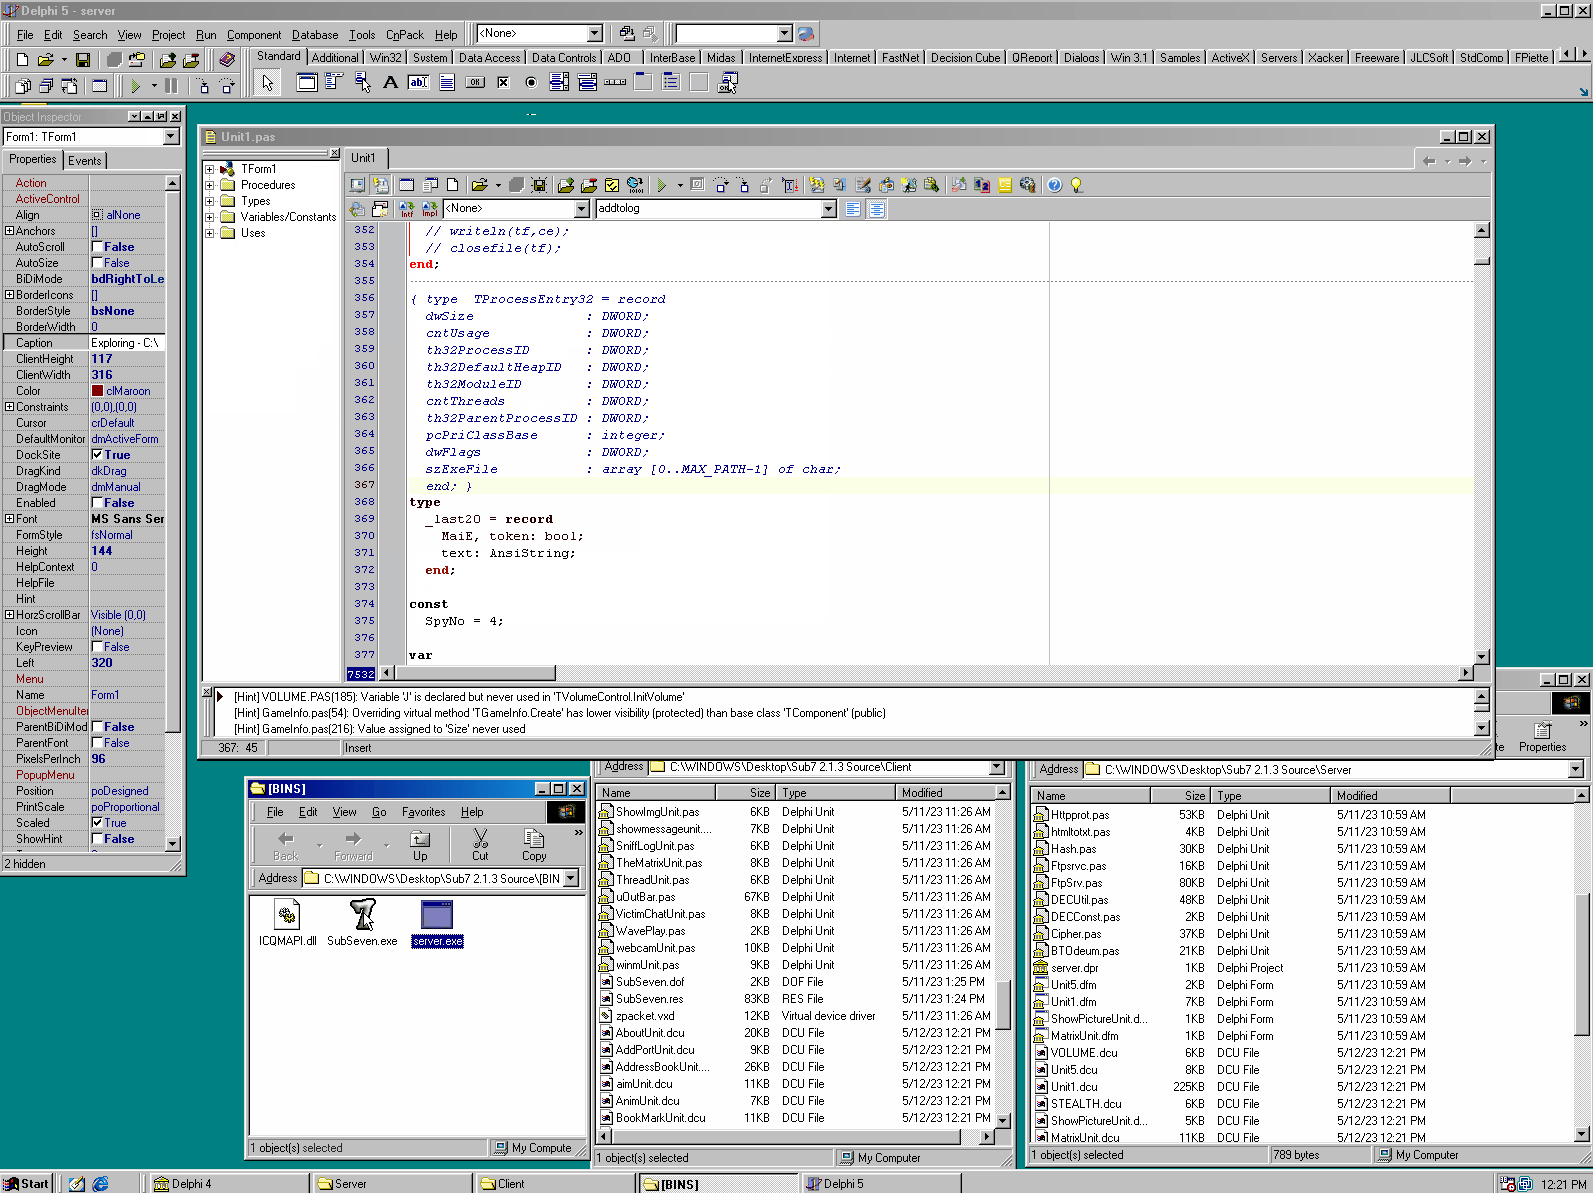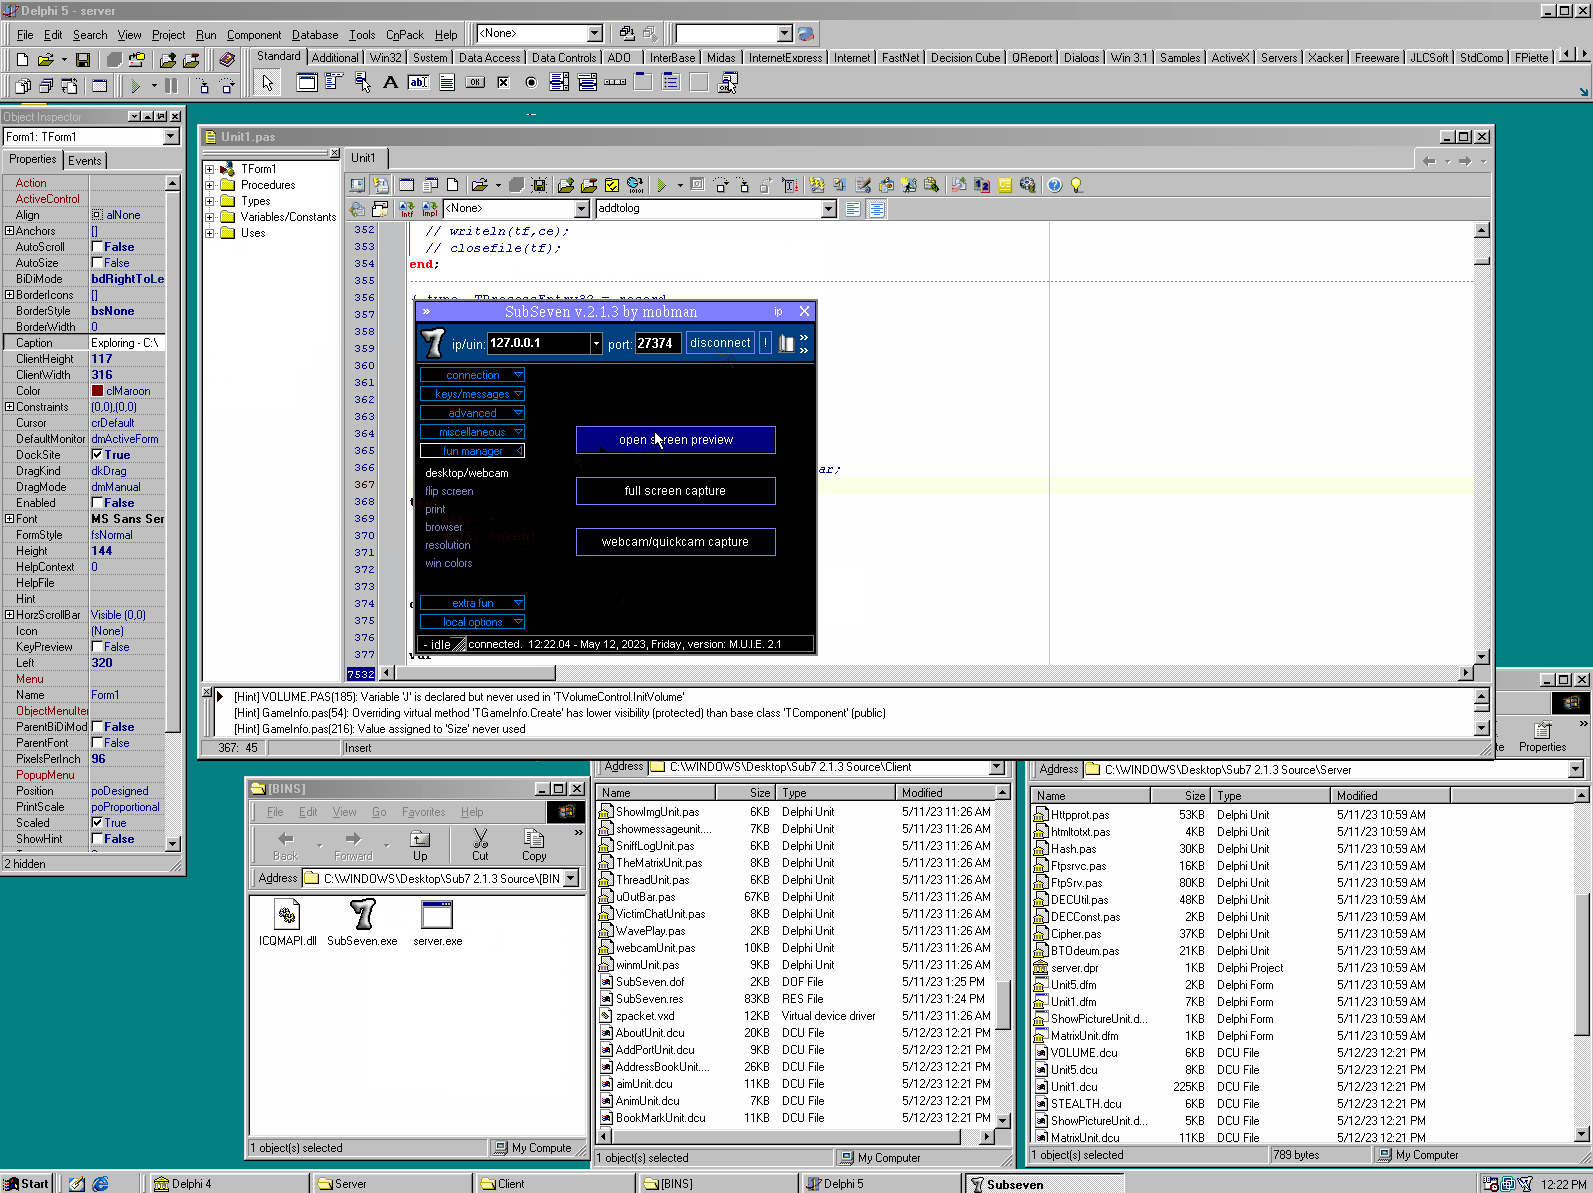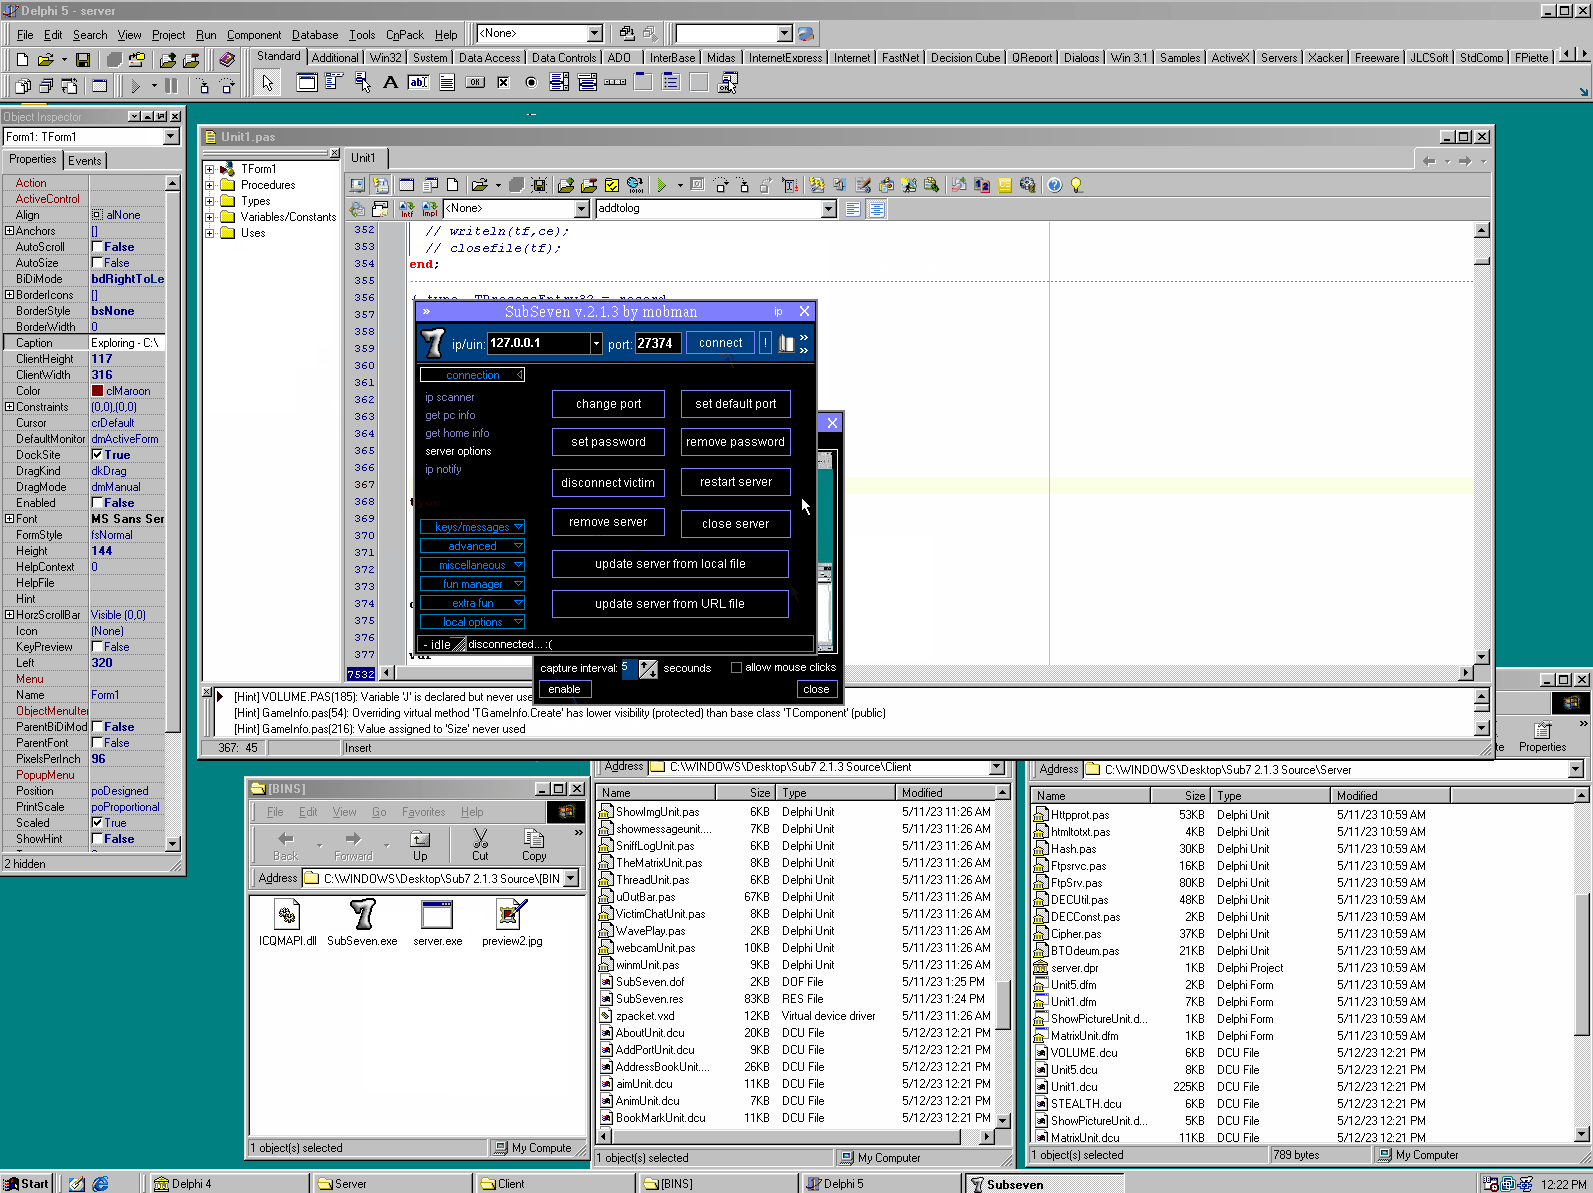
 illwill/sub7
Source code for SubSeven 2.1.3
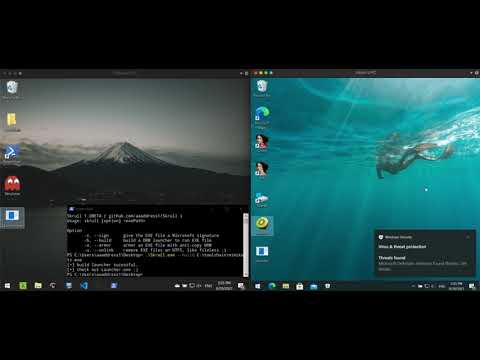 aaaddress1/skrull
Generates anti-copy malware launchers using Process Ghosting to bypass AV/EDR signature scanning and prevent automatic sample submission. Supports…
 darnabin/cve-2022-36446-webmin-rce
Authenticated remote code execution exploit for Webmin < 1.997 via the Software Package Updates module. Injects arbitrary commands as root through an…
 ungabunga-ctf/cve-2023-26039
CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.