
CVE-2023-38831
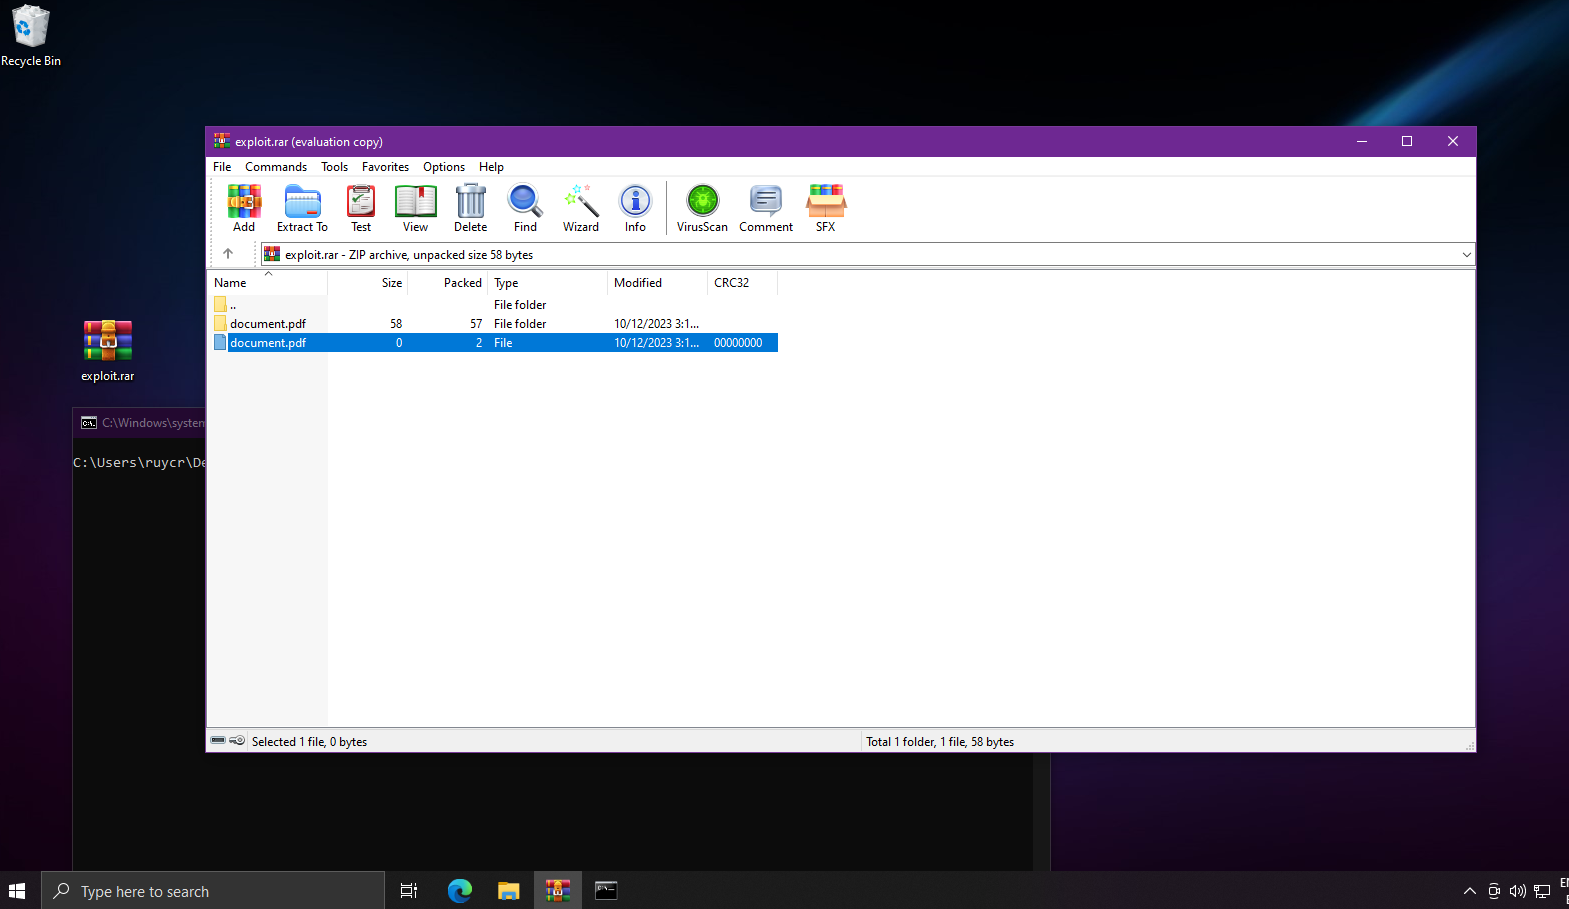
 ruycr4ft/cve-2023-38831
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
exploitationpayload-generationpenetration-testing+3
1
ruycr4ft/cve-2023-38831Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
 izzz0/cve-2023-27372-poc
Python proof-of-concept for detecting CVE-2023-27372 in SPIP CMS. Scans single or multiple URLs for the vulnerability and outputs results to terminal…
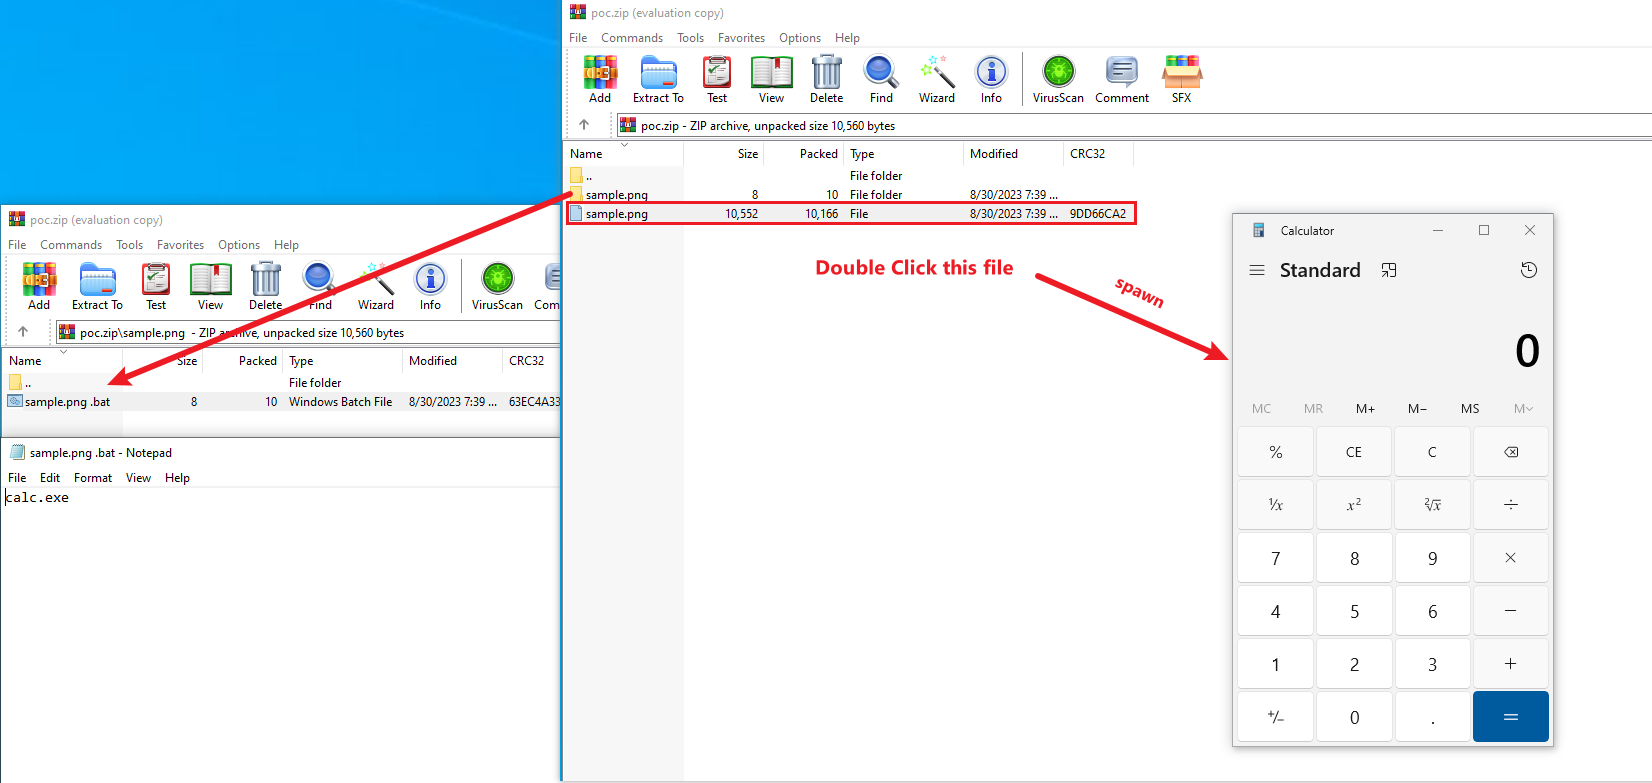 z3r0sw0rd/cve-2023-38831-poc
Proof-of-Concept for CVE-2023-38831 Zero-Day vulnerability in WinRAR
 abbisqq/cve-2023-24610
This is a proof of concept for CVE-2023-24610
 xpltive/cve-2023-50564
Pluck-CMS v4.7.18 RCE exploit
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…
 dwisiswant0/cve-2023-50164-poc
Proof of Concept for Path Traversal in Apache Struts ("CVE-2023-50164")
 horizon3ai/vrealizeloginsightrce
POC for RCE using vulnerabilities described in VMSA-2023-0001
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 blindma1den/cve-2023-46818-exploit
This is my own exploit for CVE-2023-46818 happy hacking!
 ccievoice2009/cve-2023-46604
Exploit for CVE-2023-46604 in Apache ActiveMQ, enabling remote code execution via crafted XML payloads and reverse shell establishment.
 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 tiepologian/cve-2023-23397
Proof of Concept for CVE-2023-23397 in Python
 bardlaudian/cve-2023-49070
Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
 groppoxx/cve-2023-52076-poc
PoC exploit for CVE-2023-52076 - zip-slip path traversal in Atril/Xreader (MATE/Cinnamon) enabling arbitrary file write and RCE via crafted EPUB.…
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP