
phantom-frida
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
android-securitybinary-analysisdynamic-analysis-sandboxing+7
388
theqmaks/phantom-fridaBuild anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
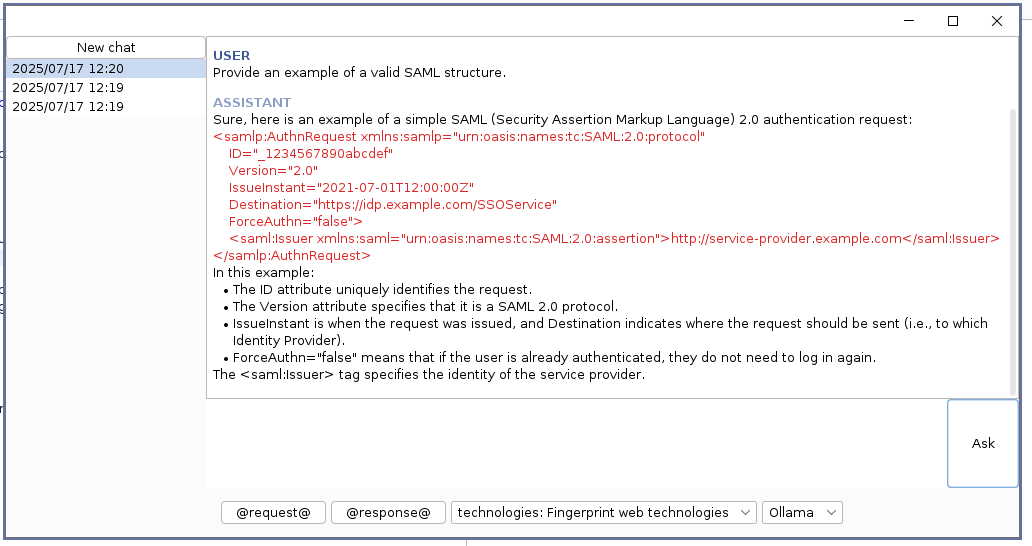 synacktiv/hopla
HopLa Burp Suite Extender plugin - Brings AI capabilities, autocompletion support, and a set of useful payloads to Burp Suite
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 sighook/pixload
Image Payload Creating/Injecting tools
 tulungagungcyberlink/cve-2019-11932
Double-Free BUG in WhatsApp exploit poc.
 d4em0n/exrop
Automated ROP chain generator for x86-64 binaries using symbolic execution. Supports register/memory writes, function calls, syscalls, badchar…
 dorkerdevil/cve-2019-11932
double-free bug in WhatsApp exploit poc
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
 grn-bogo/cve-2023-23397
Python script to create a message with the vulenrability properties set
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 code-developers/cve-2020-11932
Proof-of-concept exploit for CVE-2020-11932, a double-free vulnerability in WhatsApp GIF processing, enabling remote code execution via crafted .gif…
 rub-nds/metadata-attacker
A tool to generate media files with malicious metadata
 projectorbug/cve-2020-11932
Double-Free BUG in WhatsApp exploit poc.
 buiduchoang24/cve-2023-33733
This project aims at re-analyzing and PoC about CVE-2023-33733. Reportlab up to v3.6.12 allows attackers to execute arbitrary code via supplying a…
 afifudinmtop/cve-2009-3103
Exploit for CVE-2009-3103, a Windows SMB remote code execution vulnerability, with a Python script and Metasploit handler for reverse shell.
 kossatzd/log4j-cve-2021-44228-test
demo project to highlight how to execute the log4j (CVE-2021-44228) vulnerability