

SysWhispers3
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
defensive-toolsexploitationids-ips-evasion+5
1.6k2 years ago
klezvirus/syswhispers3SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 xnuvers007/cve-2023-21716
RTF Crash POC Python 3.11 Windows 10
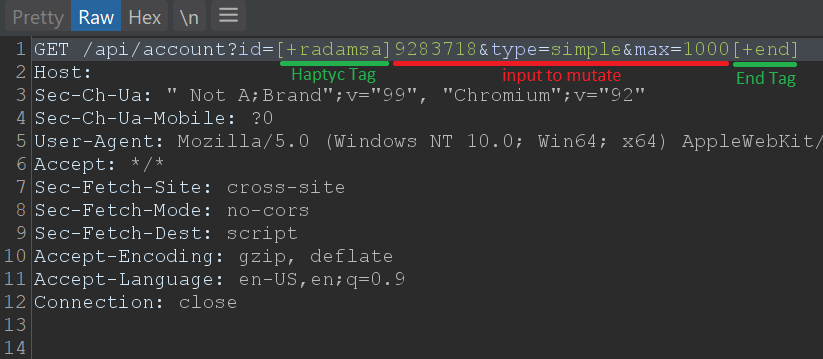 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 trerb/markdown-exfil-tester
Black-box test whether an LLM chatbot is vulnerable to markdown/HTML exfil (CVE-2025-32711 class). Spins up a sink, sends payloads, renders in…
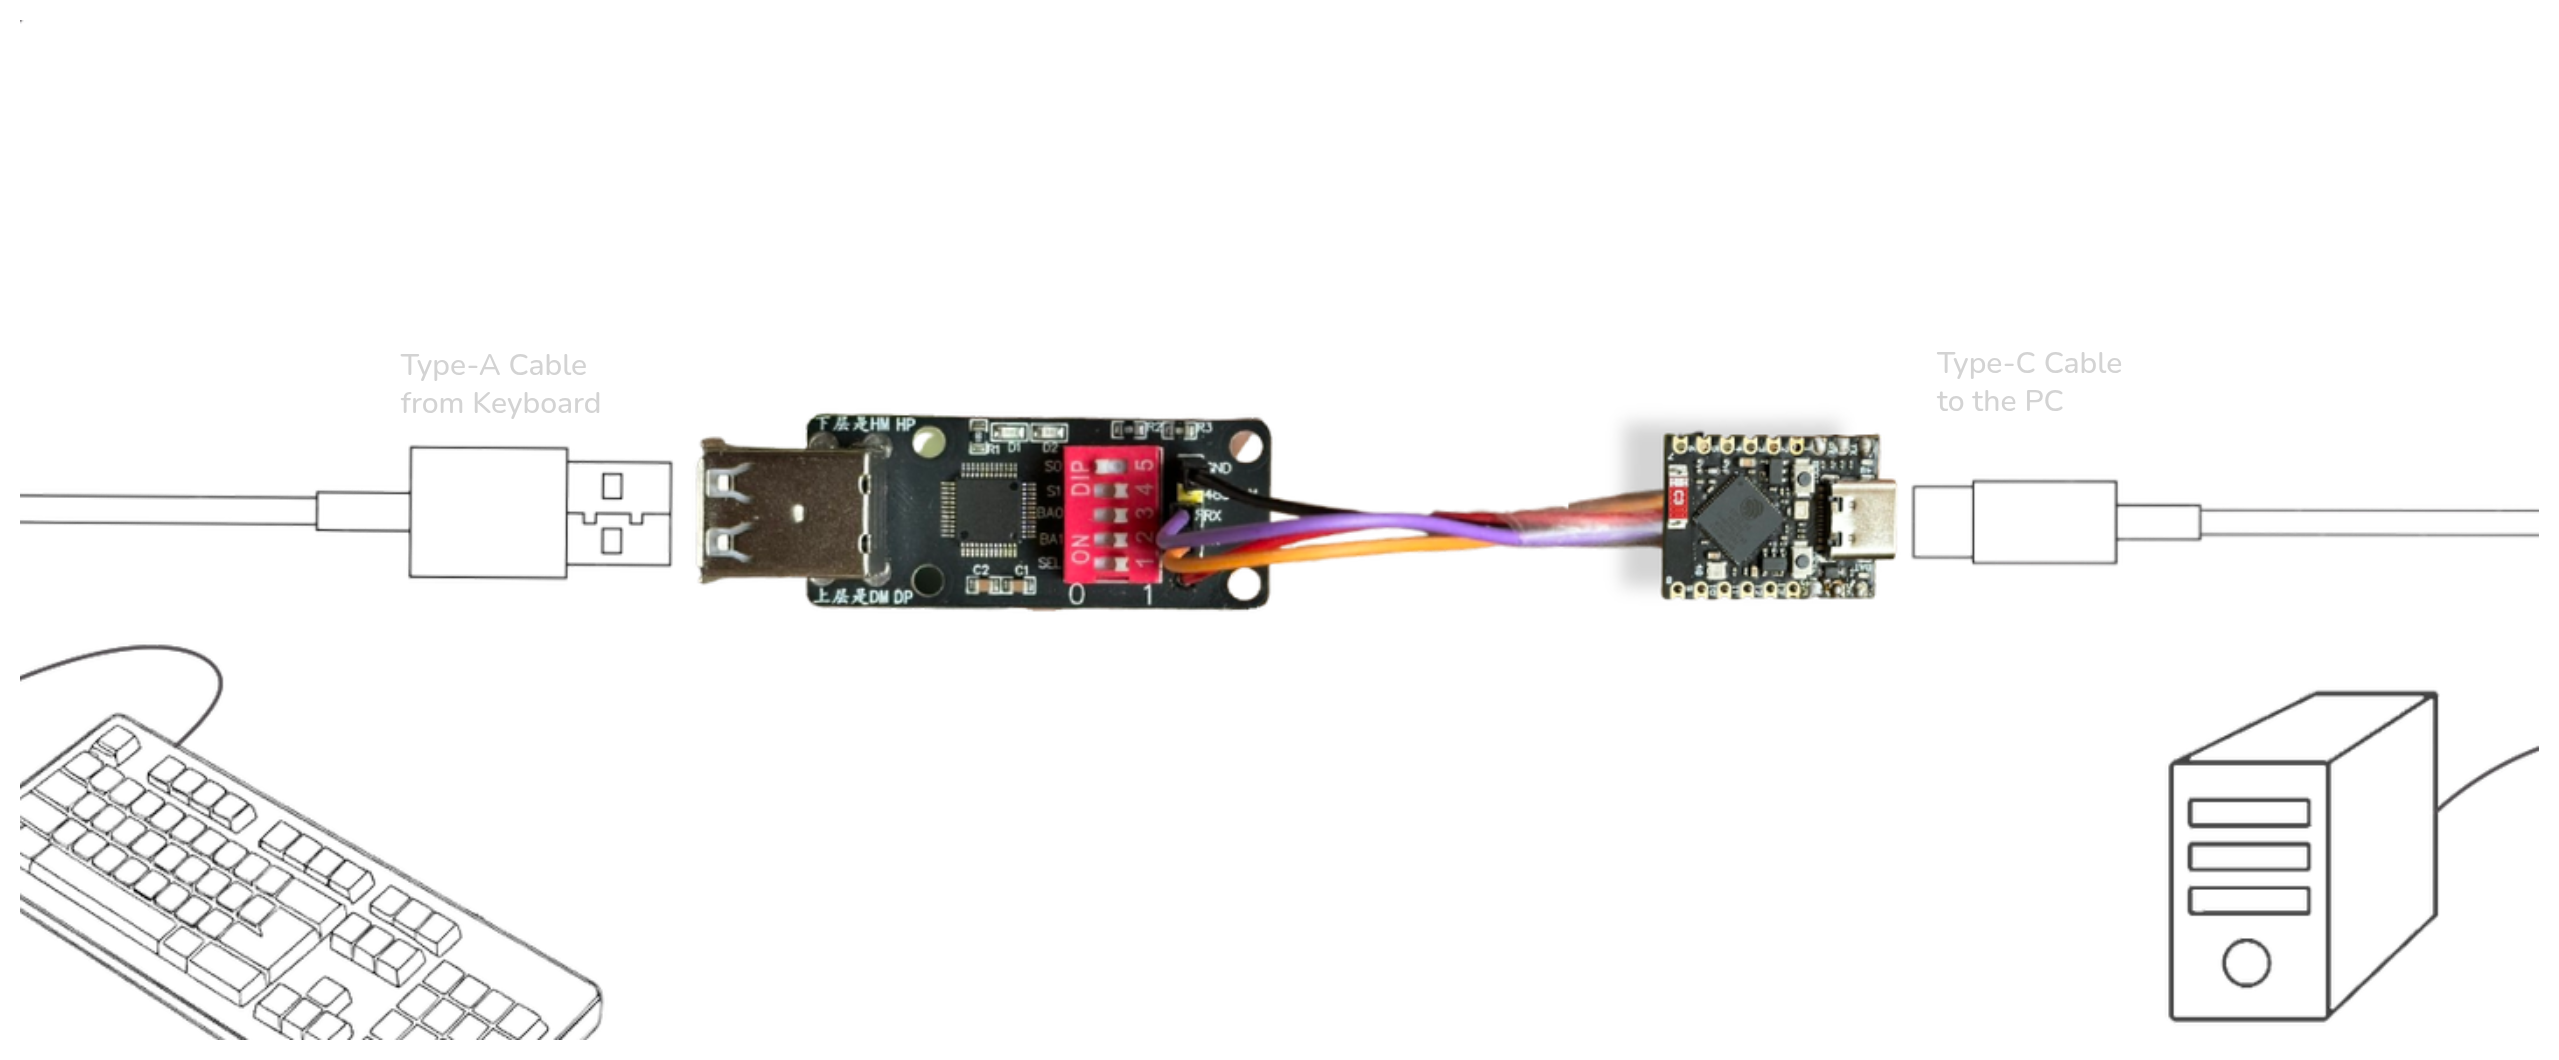 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 r3n3r0/cve-2026-0049
PoC and analysis of a zero-click DoS in Android's DNG SDK, with crafted DNG samples, an NDK crash harness, and UBSan/IntSan reproduction of the…
 realstatus/cve-2026-47858
Proof-of-concept exploit for unauthenticated JMX RCE in Spring Tools live information mode, using MLet remote class loading to execute arbitrary…
 captain-woof/cve-2017-12629
Remote code execution occurs in Apache Solr before 7.1 with Apache Lucene before 7.1 by exploiting XXE in conjunction with use of a Config API…
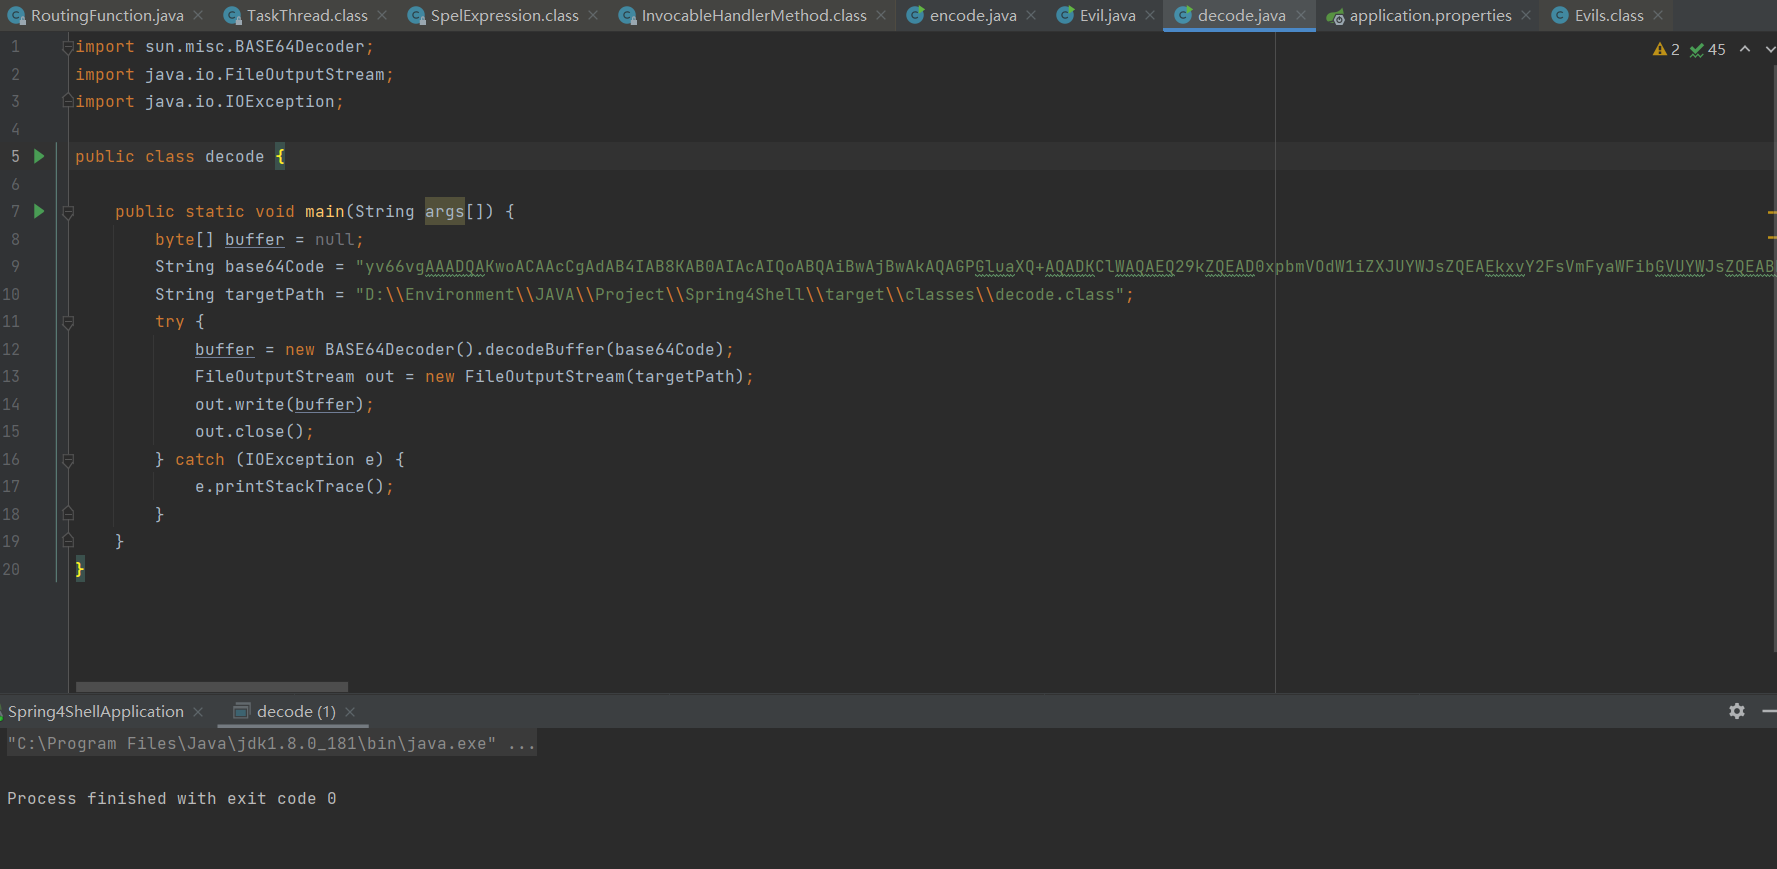 al1ex/javadere
Class to base64 String,base64 String to class
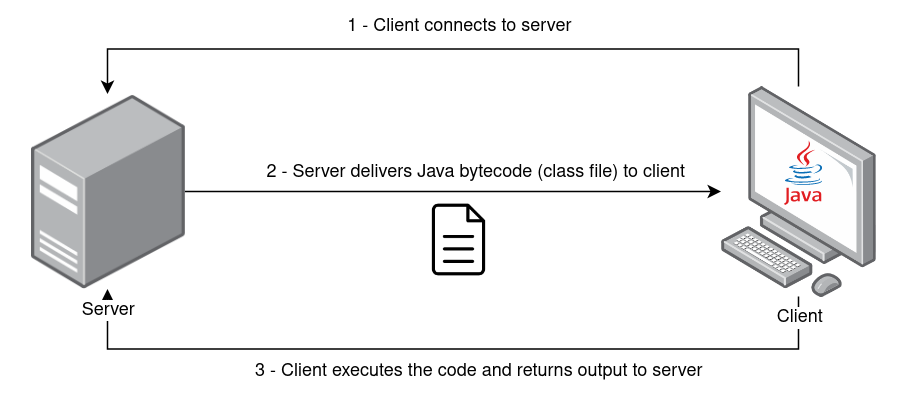 joaovarelas/java-remote-class-loader
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…
 kphongagsorn/adobe-flash-cve2018-15982
Metasploit module and Python script to generate SWF payloads exploiting CVE-2018-15982, a use-after-free vulnerability in Adobe Flash Player enabling…
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 hosch3n/fastjsonvulns
Exploit for Fastjson 1.2.80 CVE-2022-25845 enabling AspectJ file read and Groovy remote class loading for RCE.
 mikispag/rosettaflash
A tool for manipulating SWF files, leveraging zlib to craft alphanumeric-only valid SWF files in order to allow CSRF with SOP bypass thanks to JSONP…
 cckuailong/cve-2022-40146_exploit_jar
Java-based exploit for Apache Batik SSRF to RCE (CVE-2022-40146) with payload generation via jar and ecmascript, enabling remote class loading…
 xattam1/adobe-flash-exploits_17-18
Converted Metasploit exploits for Adobe Flash vulnerabilities CVE-2015-3090, CVE-2015-3105, CVE-2015-5119, and CVE-2015-5122 to a Python3 script.
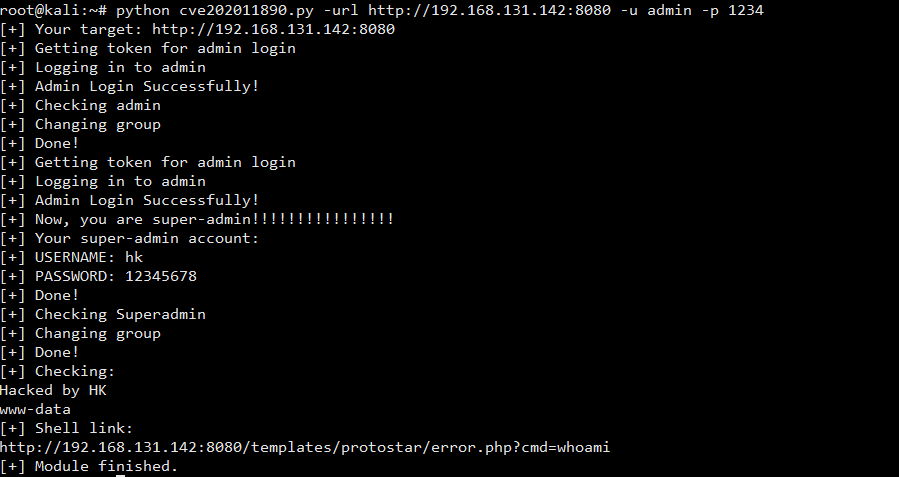 hoangkien1020/cve-2020-11890
CVE-2020-11890: Improper input validations in the usergroup table class could lead to a broken ACL configuration to RCE
 jas502n/cve-2018-15982_exp_ie
Exploit generator for CVE-2018-15982 (Adobe Flash Player) that produces SWF and HTML files for remote code execution via crafted Flash objects.