
rpi-hunter
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
exploitationinformation-gatheringnetwork-security+2
busescanfly/rpi-hunterAuto discover and exploit LAN raspberry pi's
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
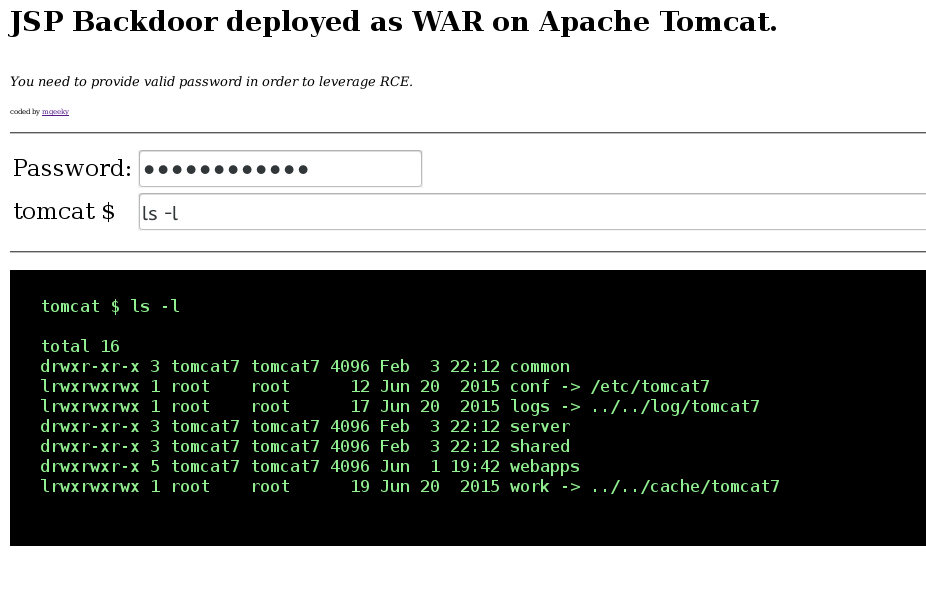 mgeeky/tomcatwardeployer
Apache Tomcat auto WAR deployment & pwning penetration testing tool.
 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…
 aron-tn/mega-bot
[NEW] : Mega Bot ☣ Scanner & Auto Exploiter
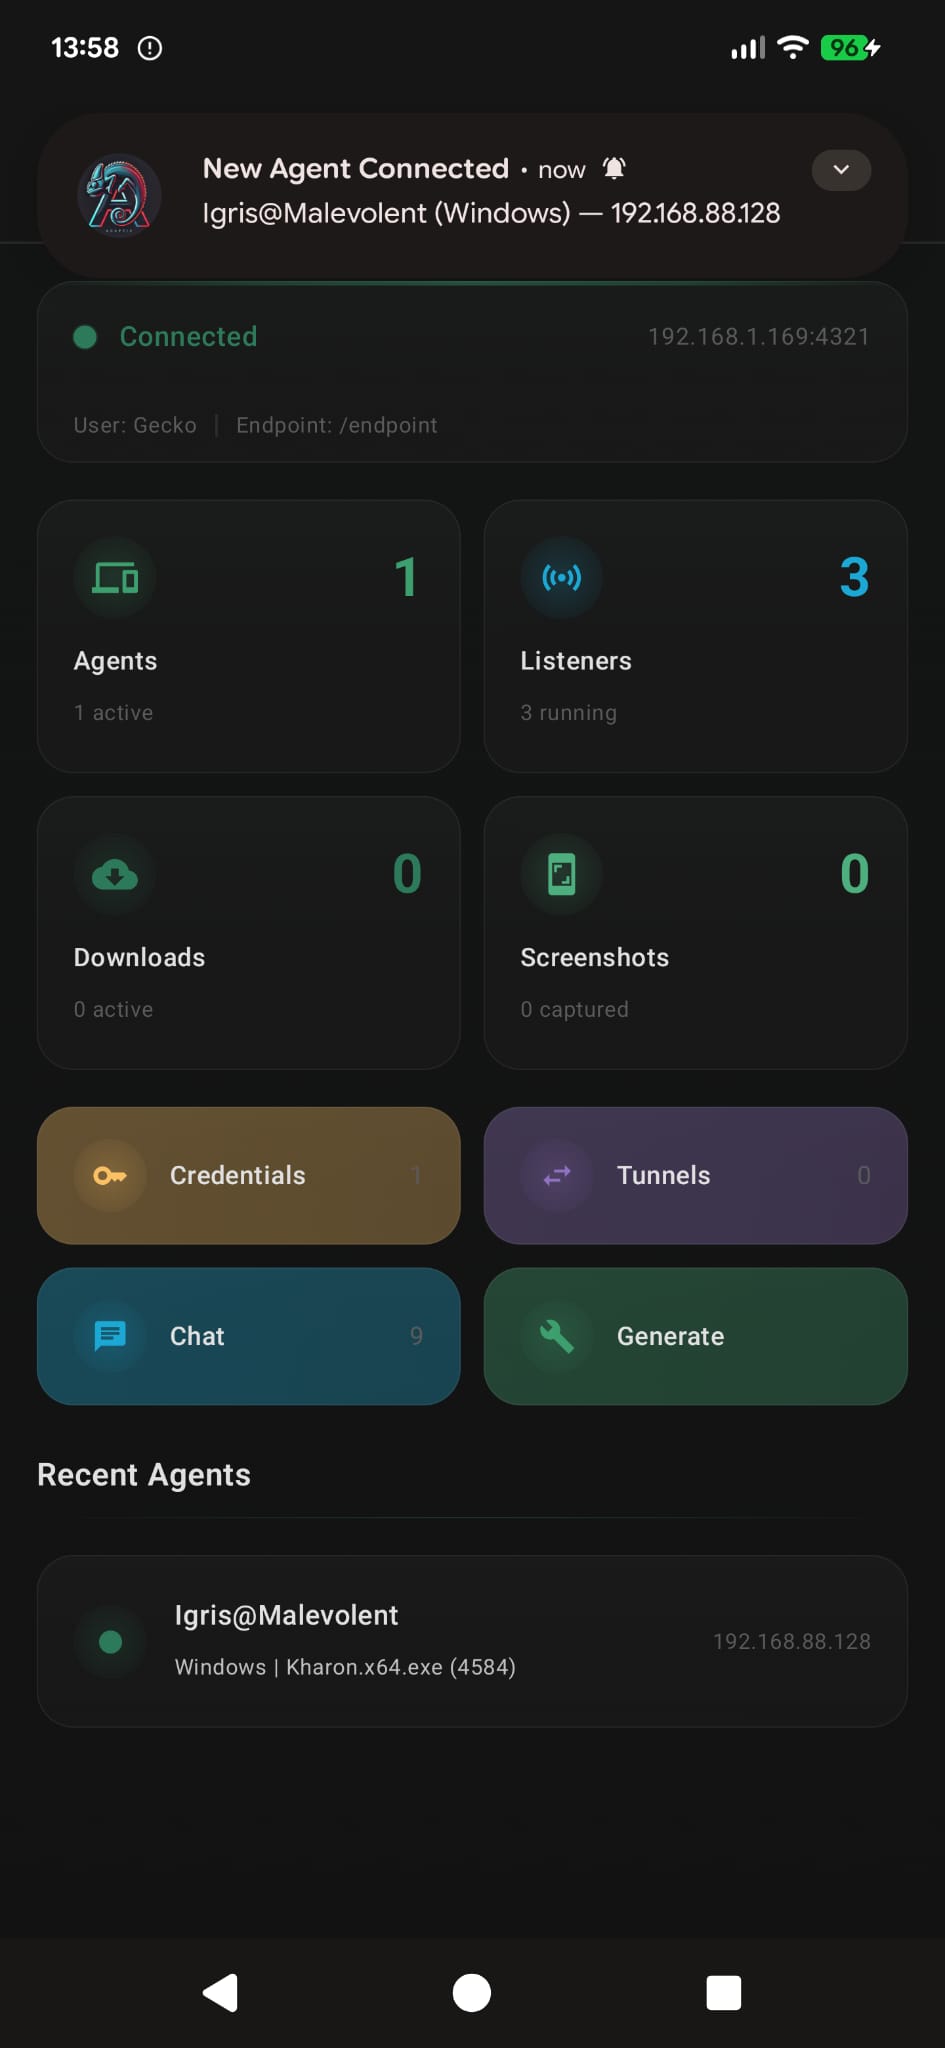 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 randomrobbiebf/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 kaxm23/cve-2025-55182-auto-scanner
CVE-2025-55182 Auto Scanner - Improved Version For authorized CTF/testing purposes only
 nu11secur1ty/sh1mazu
Meterpreter auto exploit program
 yt1g3r/cve-2020-0688_exp
CVE-2020-0688_EXP Auto trigger payload & encrypt method
 d4ytox/cve-2021-21425
CVE-2021-21425 - GravCMS 1.10.7 Unauthenticated RCE via Scheduler. Improved exploit with CLI args and auto base64 encoding.
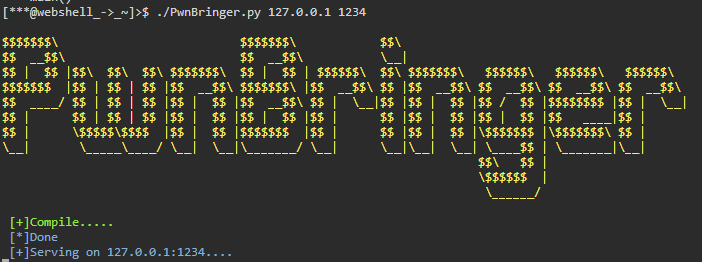 g01d3nw01f/cve-2021-4034
Automates the compilation and serving of the PwnKit exploit for CVE-2021-4034, enabling local privilege escalation on vulnerable Linux systems.
 sagsooz/cve-2023-5360
CVE-2023-5360 Auto Shell Upload WordPress Royal Elementor 1.3.78 Shell Upload
 j4k0m/cve-2018-11235
Automated creation of malicious Git repositories to exploit CVE-2018-11235, a remote code execution vulnerability in Git submodules.
 d0n601/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 nxploited/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 speatx/chamilolms-cve-2023-4220
CVE-2023-4220 — Unauthenticated file upload RCE in Chamilo LMS ≤ 1.11.24. OSCP-style and auto exploit.
 phankz/worpress-cve-2023-5360
Automated shell upload exploit for CVE-2023-5360 targeting WordPress Royal Elementor plugin, enabling remote code execution via crafted payloads.