

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 trinib/zorg-jailbreak-prompt-text
Bypass restricted and censored content on AI chat prompts 😈
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
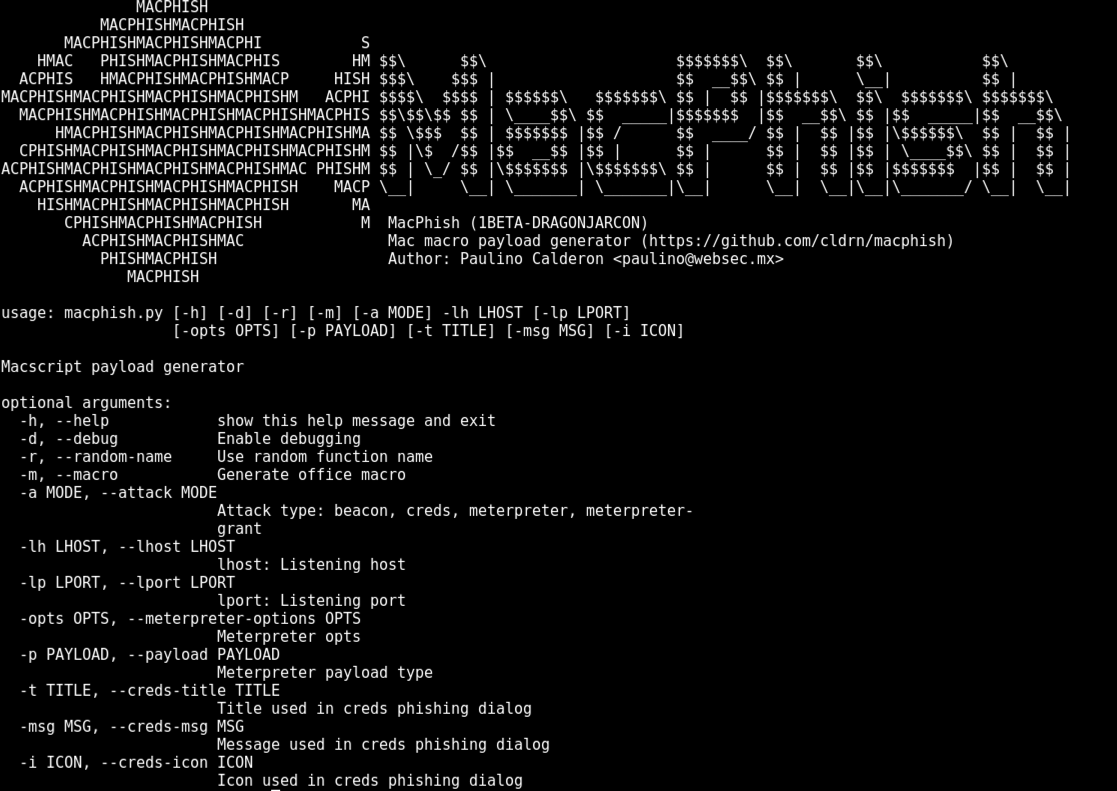 cldrn/macphish
Generates malicious Office for Mac macros with beacon, credential harvesting, and meterpreter payloads for phishing and exploitation testing on macOS.
 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
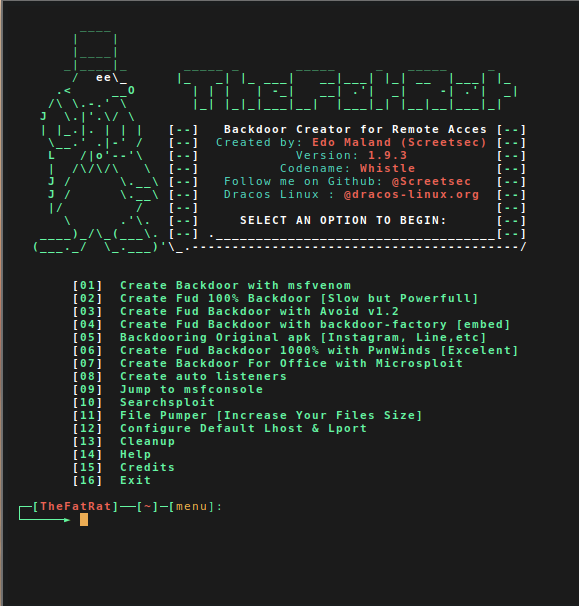 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
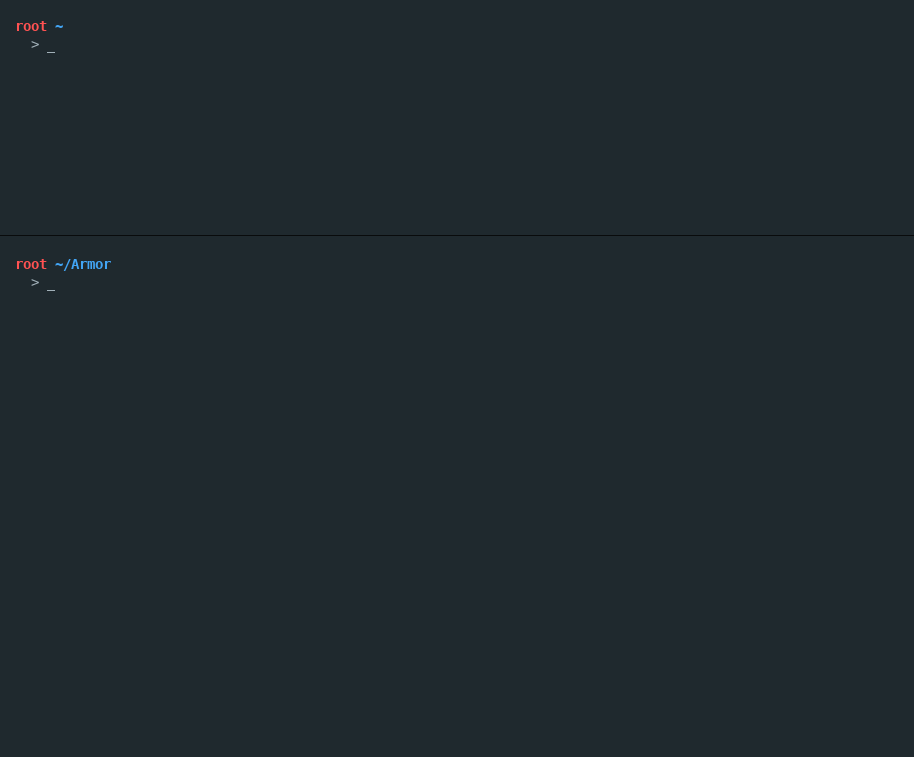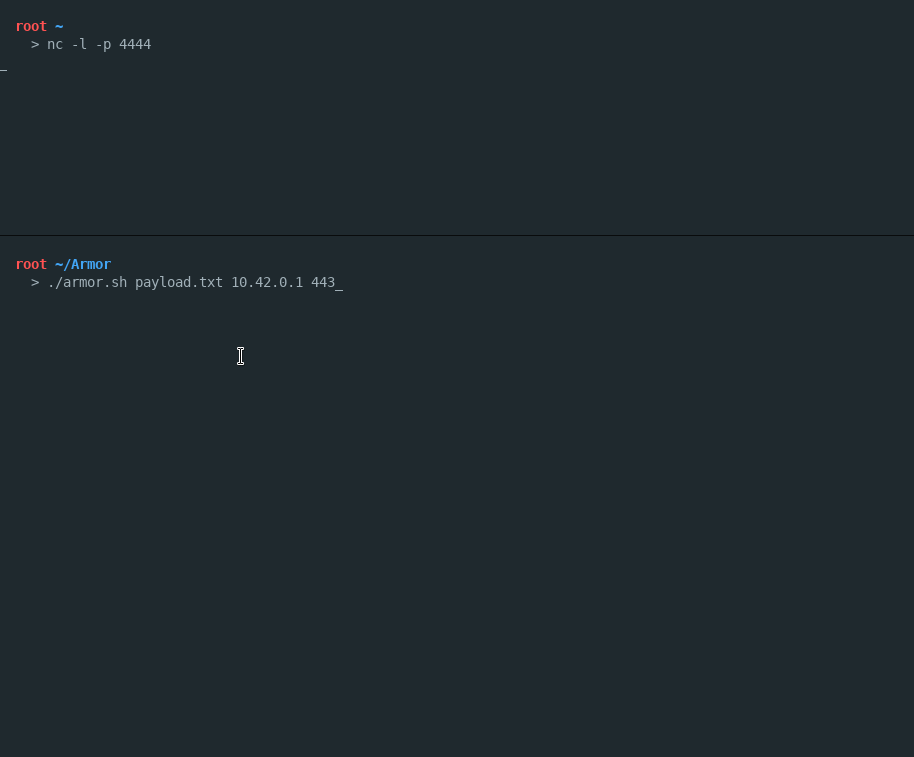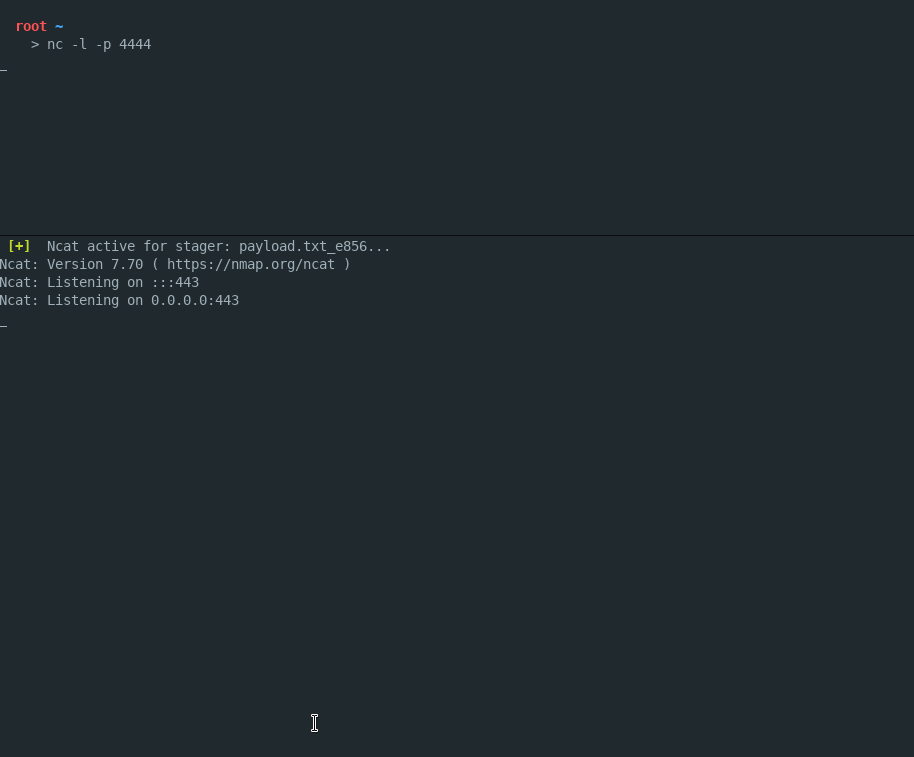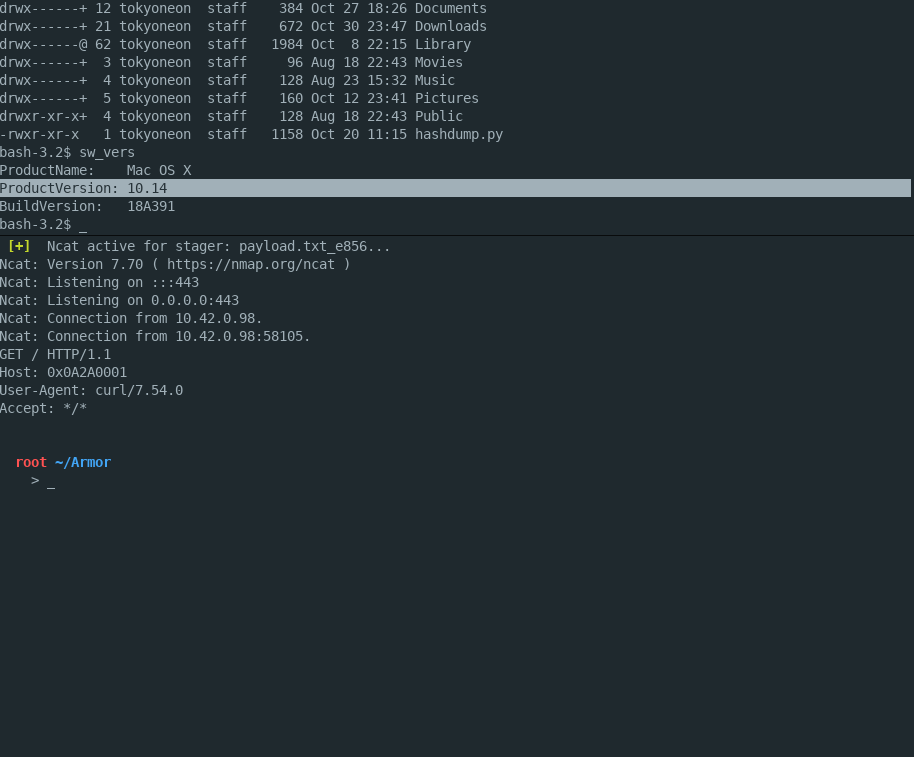 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
 imeneallouche/follina-attack-cve-2022-30190-
this is a demo attack of FOLLINA exploit , a vulnerability that has been discovered in May 2022 and stood unpatched until June 2022
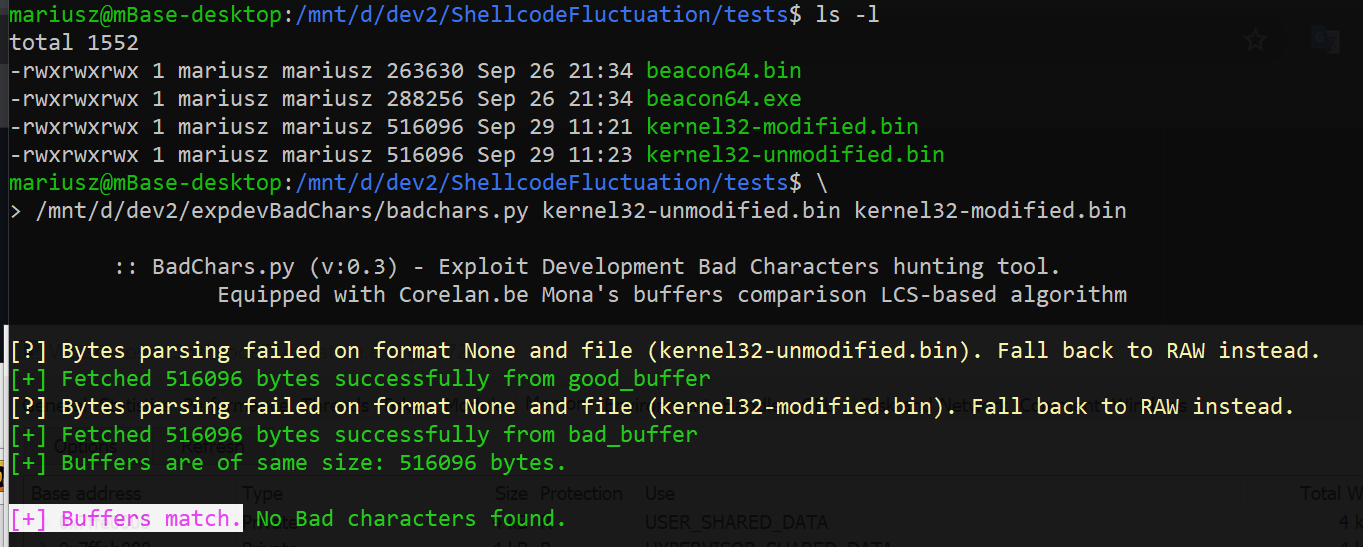 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 hatriot/clusterd
application server attack toolkit