

CVE-2024-45590-PoC
 evillm/cve-2024-45590-poc
Proof-of-concept exploit for CVE-2024-45590, demonstrating unauthenticated remote code execution in a WordPress plugin via arbitrary file upload.…
educationexploitationpayload-development+3
evillm/cve-2024-45590-pocProof-of-concept exploit for CVE-2024-45590, demonstrating unauthenticated remote code execution in a WordPress plugin via arbitrary file upload.…
 r0otk3r/cve-2024-25600
Python-based exploit for CVE-2024-25600 targeting Bricks Builder WordPress plugin RCE. Automates nonce extraction, payload injection, and arbitrary…
 itsismarcos/exploit-cve-2026-1357
Exploit for CVE-2026-1357 in WordPress WPVivid plugin, enabling remote code execution via crafted AES-encrypted payloads and directory traversal to…
 randomrobbiebf/cve-2026-28134
JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution
 whattheslime/file-away-exploit
Remote code execution exploit scripts for the WordPress File-Away plugin (CVE-2025-2512 & CVE-2025-2539)
 madexploits/cve-2026-14483
CVE-2026-14483 POC EXPLOIT BY MADEXPLOITS
 0xcyp1337/cve-2026-57811
Exploits CVE-2026-57811, an unauthenticated RCE in Realtyna Organic IDX + WPL Real Estate WordPress plugin, enabling shell upload and command…
 0xcyp1337/cve-2026-82222-massexploit
Exploit tool for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports single-target and batch exploitation with…
 xxconi/cve-2026-3296
CVE-2026-3296 is a CVSS 9.8 Critical unauthenticated PHP Object Injection vulnerability in the Everest Forms WordPress plugin
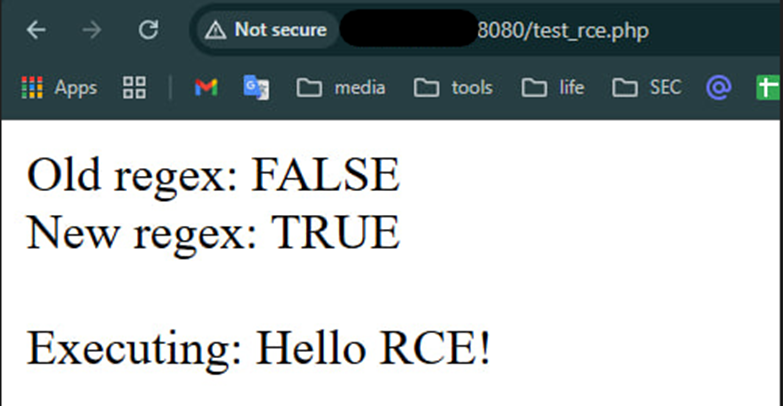 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…