

cve-2025-64446-fortiweb-exploit
 an5i/cve-2025-64446-fortiweb-exploit
Security research tool for detecting and testing CVE-2025-64446 (FortiWeb Path Traversal RCE vulnerability)
educationexploitationpayload-development+5
1
an5i/cve-2025-64446-fortiweb-exploitSecurity research tool for detecting and testing CVE-2025-64446 (FortiWeb Path Traversal RCE vulnerability)
 madan301/cve-2024-2054
Proof-of-concept exploit for CVE-2024-2054, demonstrating insecure deserialization RCE in Artica-Proxy administrative web application. Includes…
 fairyming/cve-2019-11043
Proof-of-concept exploit for CVE-2019-11043, a PHP-FPM underflow vulnerability, built on the pocsuite framework for automated web application…
 abdurahmon3236/cve-2024-5246
Proof-of-concept Python script demonstrating authenticated remote code execution in NETGEAR ProSAFE Network Management System via vulnerable Apache…
 tranphuc2005/cve-2017-9822
Detailed analysis and proof-of-concept exploit for CVE-2017-9822, an XXE/insecure deserialization vulnerability in DotNetNuke CMS leading to remote…
 0x1nsomnia/cve-2022-36067-vm2-poc-webapp
Proof-of-concept web application demonstrating CVE-2022-36067, a vm2 sandbox escape, enabling remote code execution by uploading exploit code to a…
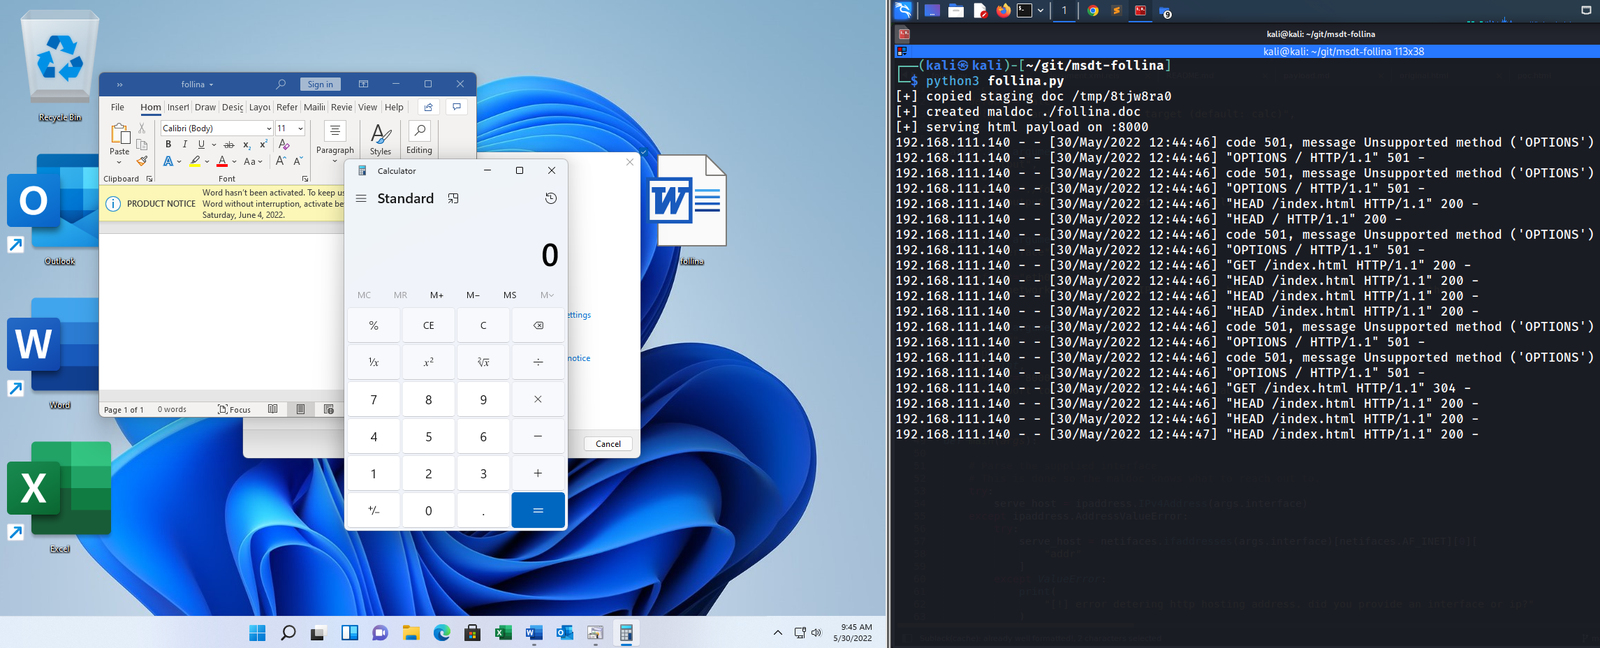 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 contrast-security-oss/spring-kafka-poc-cve-2023-34040
POC for Spring Kafka Deserialization Vulnerability CVE-2023-34040
 george0papasotiriou/cve-2025-14174-chrome-zero-day
Proof-of-concept exploit for CVE-2025-14174, a use-after-free in Chrome's V8 engine. Includes JavaScript PoC and HTML embed for identifying the…
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.
 sangsenimanwartefak/cve-2026-45034
PoC exploit for PHPSpreadsheet's phar:// deserialization vulnerability, bypassing prohibitWrappers to achieve remote code execution on vulnerable PHP…
 absholi7ly/jspdf-object-injection
CVE-2026-25755 A critical PDF Object Injection vulnerability in jsPDF allows attackers to inject arbitrary PDF objects through the addJS() function,…
 kiks7/cve-2020-6468-chrome-exploit
JavaScript-based exploit for Chrome V8 vulnerability CVE-2020-6468, with a d8 shell script and an HTML-based Chrome target.
 dottak/cve-2024-56278
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…
 mzfr/liffy
Local file inclusion exploitation tool
 randomrobbiebf/cve-2026-28134
JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution
 azefzafyoussef/cve-2026-33229
Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.
 y4er/cve-2020-2555
Weblogic com.tangosol.util.extractor.ReflectionExtractor RCE