
ghost
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
command-and-controleducationmalware-analysis+5
1.1k8 years ago
ahxr/ghostLightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 smgorelik/windows-rce-exploits
The exploit samples database is a repository for **RCE** (remote code execution) exploits and Proof-of-Concepts for **WINDOWS**, the samples are…
 ajinabraham/xenotix-python-keylogger
Xenotix Python Keylogger for Windows.
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 janoglezcampos/rust_syscalls
Single stub direct and indirect syscalling with runtime SSN resolving for windows.
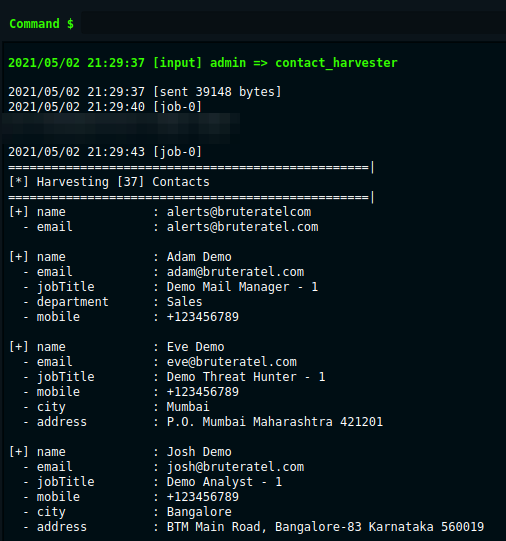 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
 bw3ll/jop_rocket
This framework enables user to discover JOP gagdets and can automate building a complete JOP chain to bypass DEP. JOP ROCKET is the ultimate solution…
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
 fenalik/cve-2021-1732
CVE-2021-1732 local privilege escalation exploit for Windows 10, with research and proof-of-concept code targeting kernel-mode vulnerabilities.
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 sinsinology/cve-2022-26503
Proof-of-concept exploit for CVE-2022-26503, a local privilege escalation vulnerability in Veeam Agent for Windows via .NET deserialization, enabling…
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 coactionbrittlemaidenhair51/coactionbrittlemaidenhair51.github.io
Explore and validate CVE-2026-42978 PoC with an integrated AI security tool, multi-protocol terminal, and autonomous agent suite for Windows Push…
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
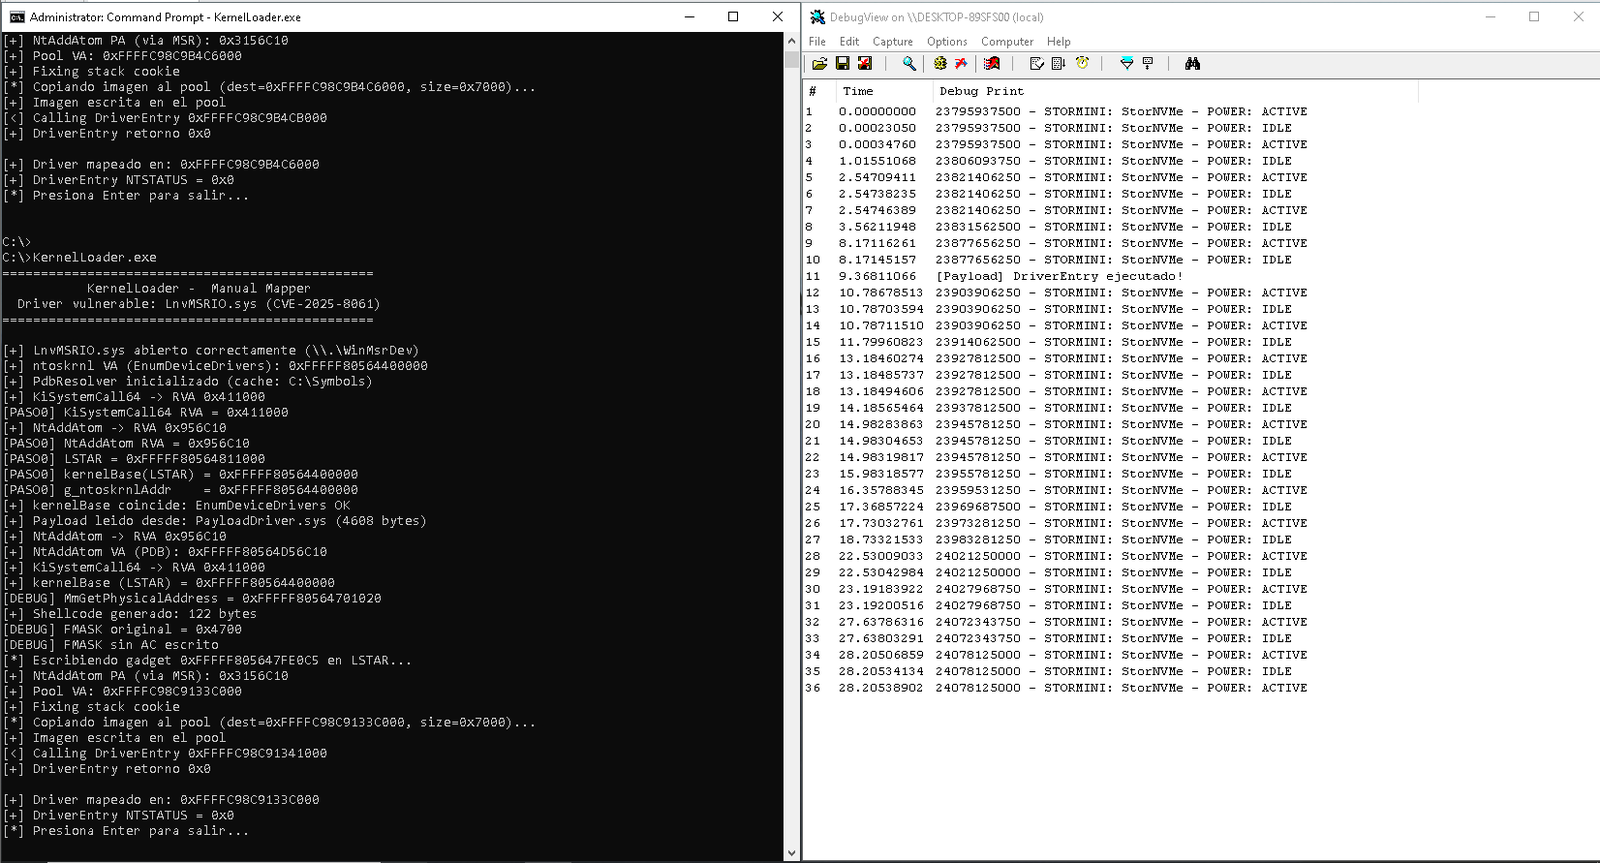 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…