

weaponised-XSS-payloads
 hakluke/weaponised-xss-payloads
XSS payloads designed to turn alert(1) into P1
exploitationpayload-developmentpayload-generation+3
hakluke/weaponised-xss-payloadsXSS payloads designed to turn alert(1) into P1
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
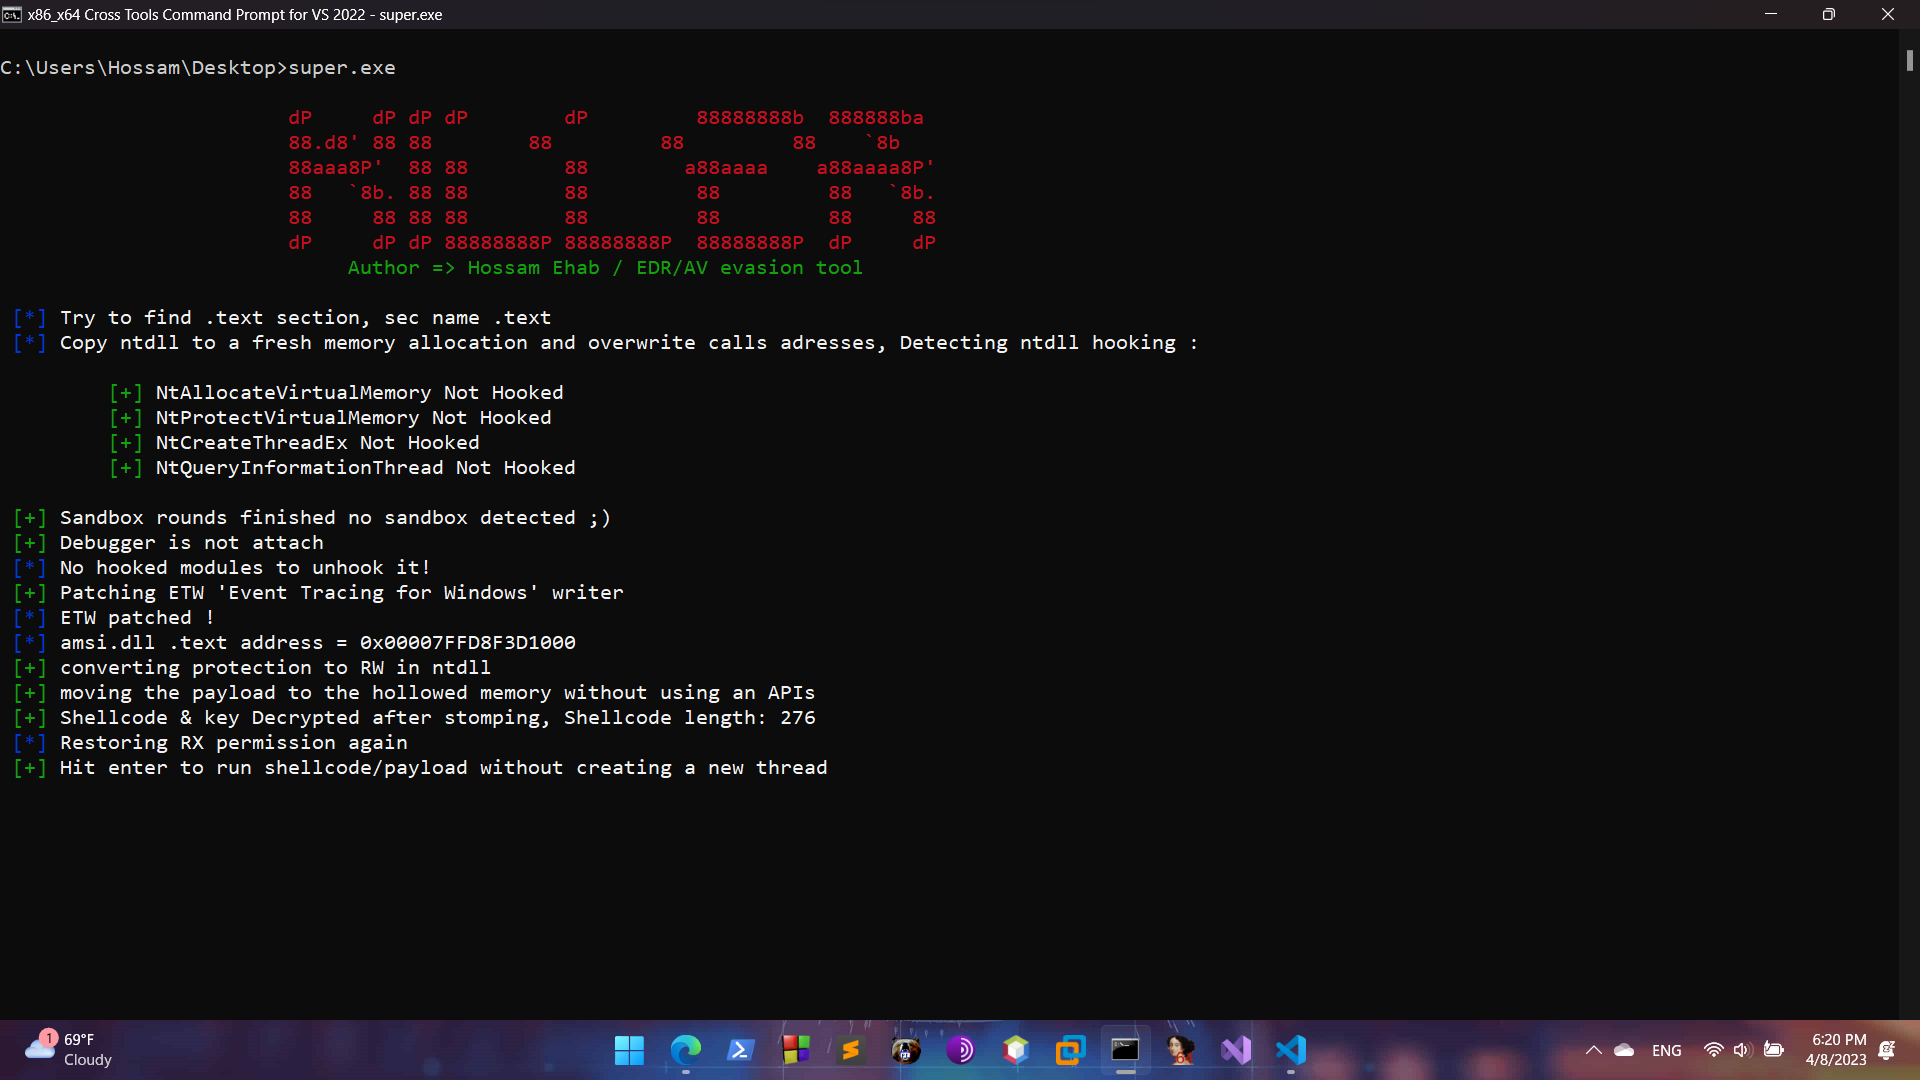 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
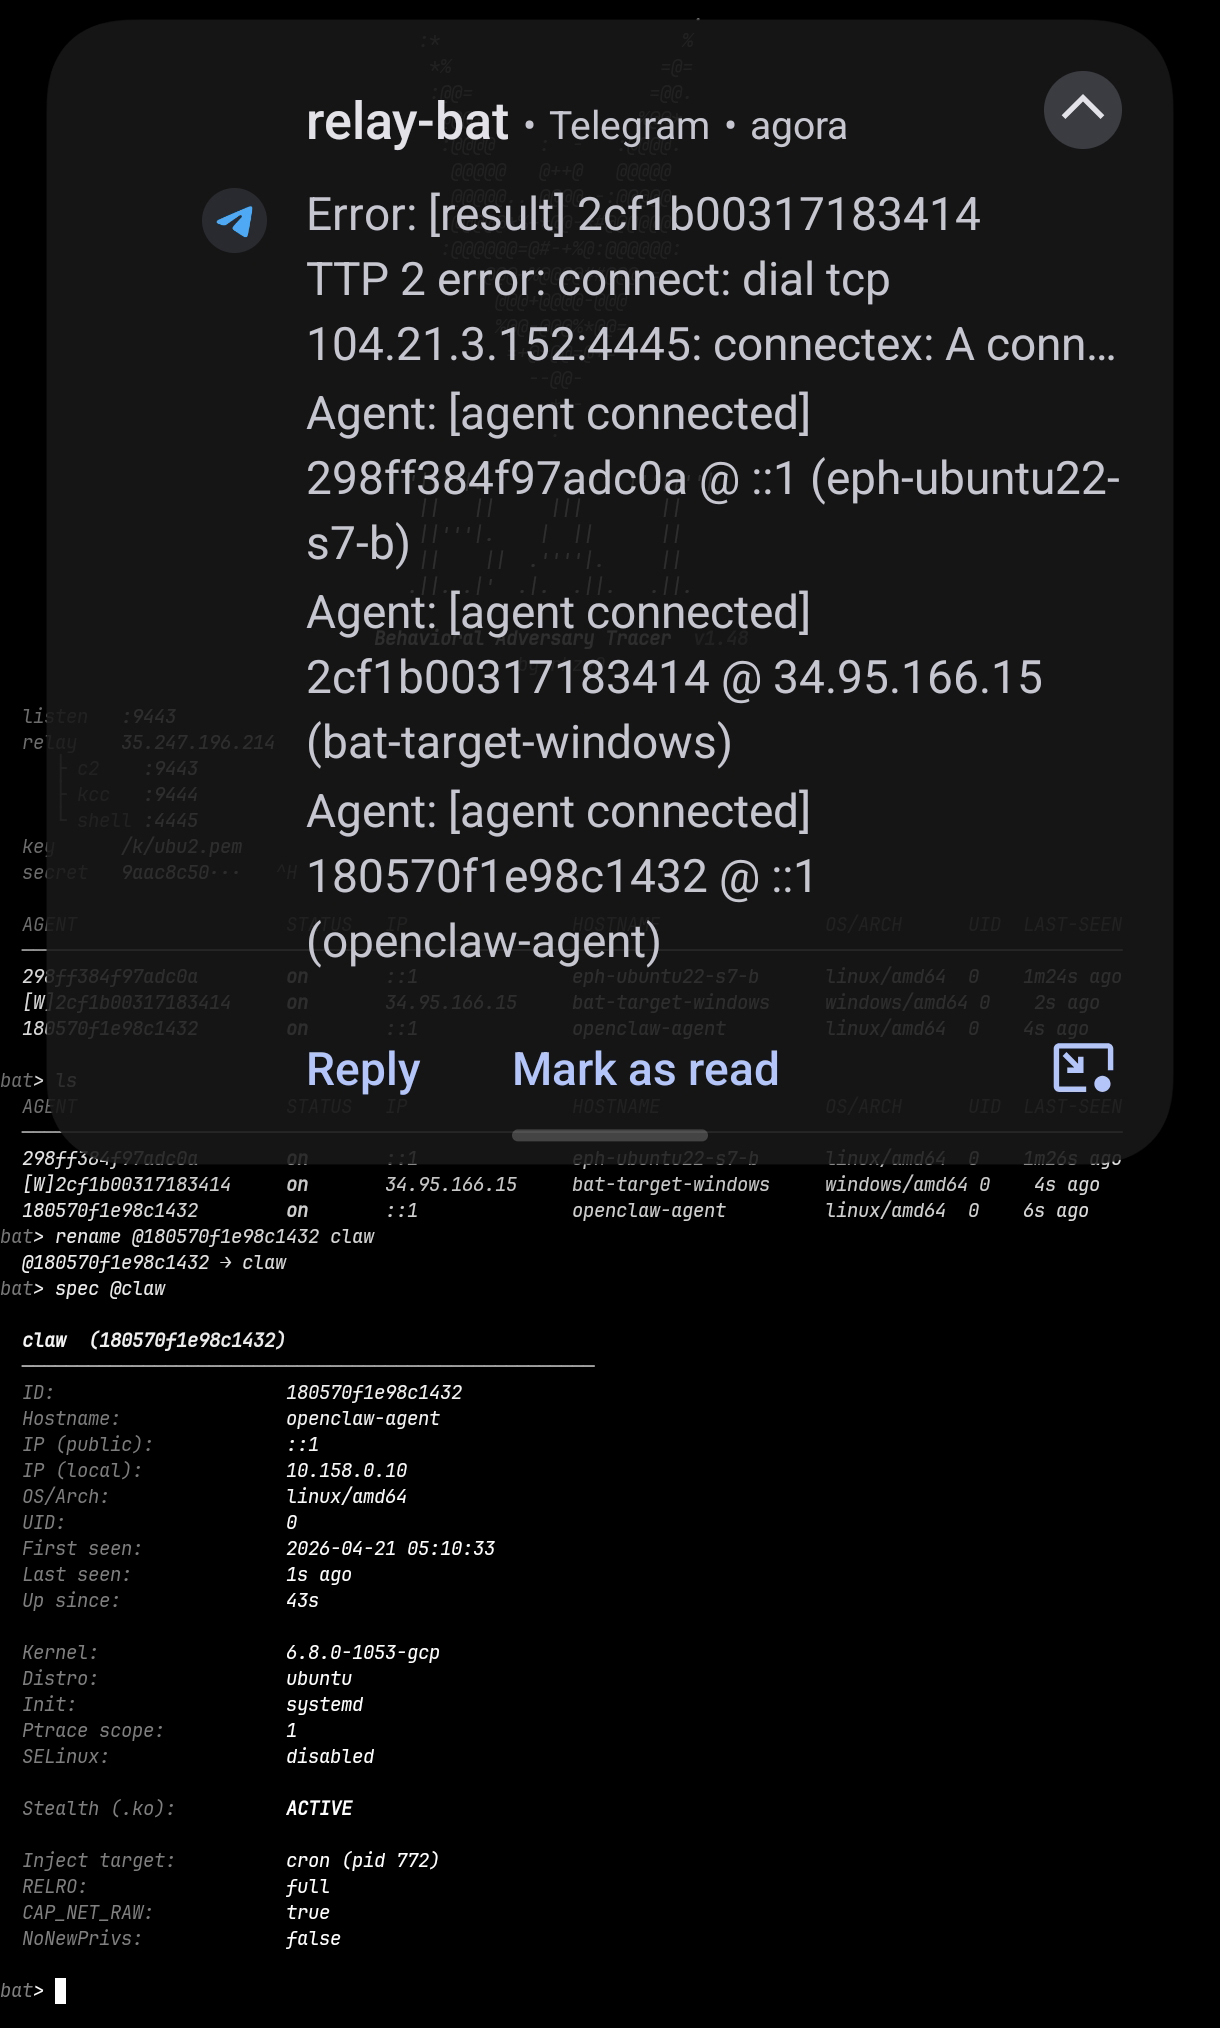 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
 d0rb/cve-2023-38545
This script is designed to exploit a heap buffer overflow vulnerability in a socks5 proxy server.
 rbowes-r7/manageengine-auditad-cve-2022-28219
Proof-of-concept exploit for CVE-2022-28219 targeting ManageEngine AuditAD. Ruby-based remote code execution trigger designed for security testing…
 exfil0/cve-2025-32756-poc
Designed for Demonstration of Deep Exploitation.
 kjdfklha/cve-2024-2961_poc
Proof-of-concept exploit for CVE-2024-2961, demonstrating a remote code execution vulnerability in PHP's iconv function. Designed for security…
 lu3ky13/alternative-approach-reverse-shell-callback-test-invokeai-rce
This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…
 darrynb89/cve-2004-1561
Python port of a Metasploit exploit targeting CVE-2004-1561 for remote code execution. Designed for penetration testing and vulnerability validation…
 dedsec-47/metasploit-exploits-cve-2023-6710
Welcome to the Metasploit Exploits Repository, your go-to resource for a comprehensive collection of cutting-edge exploits designed for penetration…
 josemariamicoli/log4shell-poc
**Log4Shell PoC is a high-fidelity exploitation environment designed to replicate the CVE-2021-44228 vulnerability.** It provides a containerized…
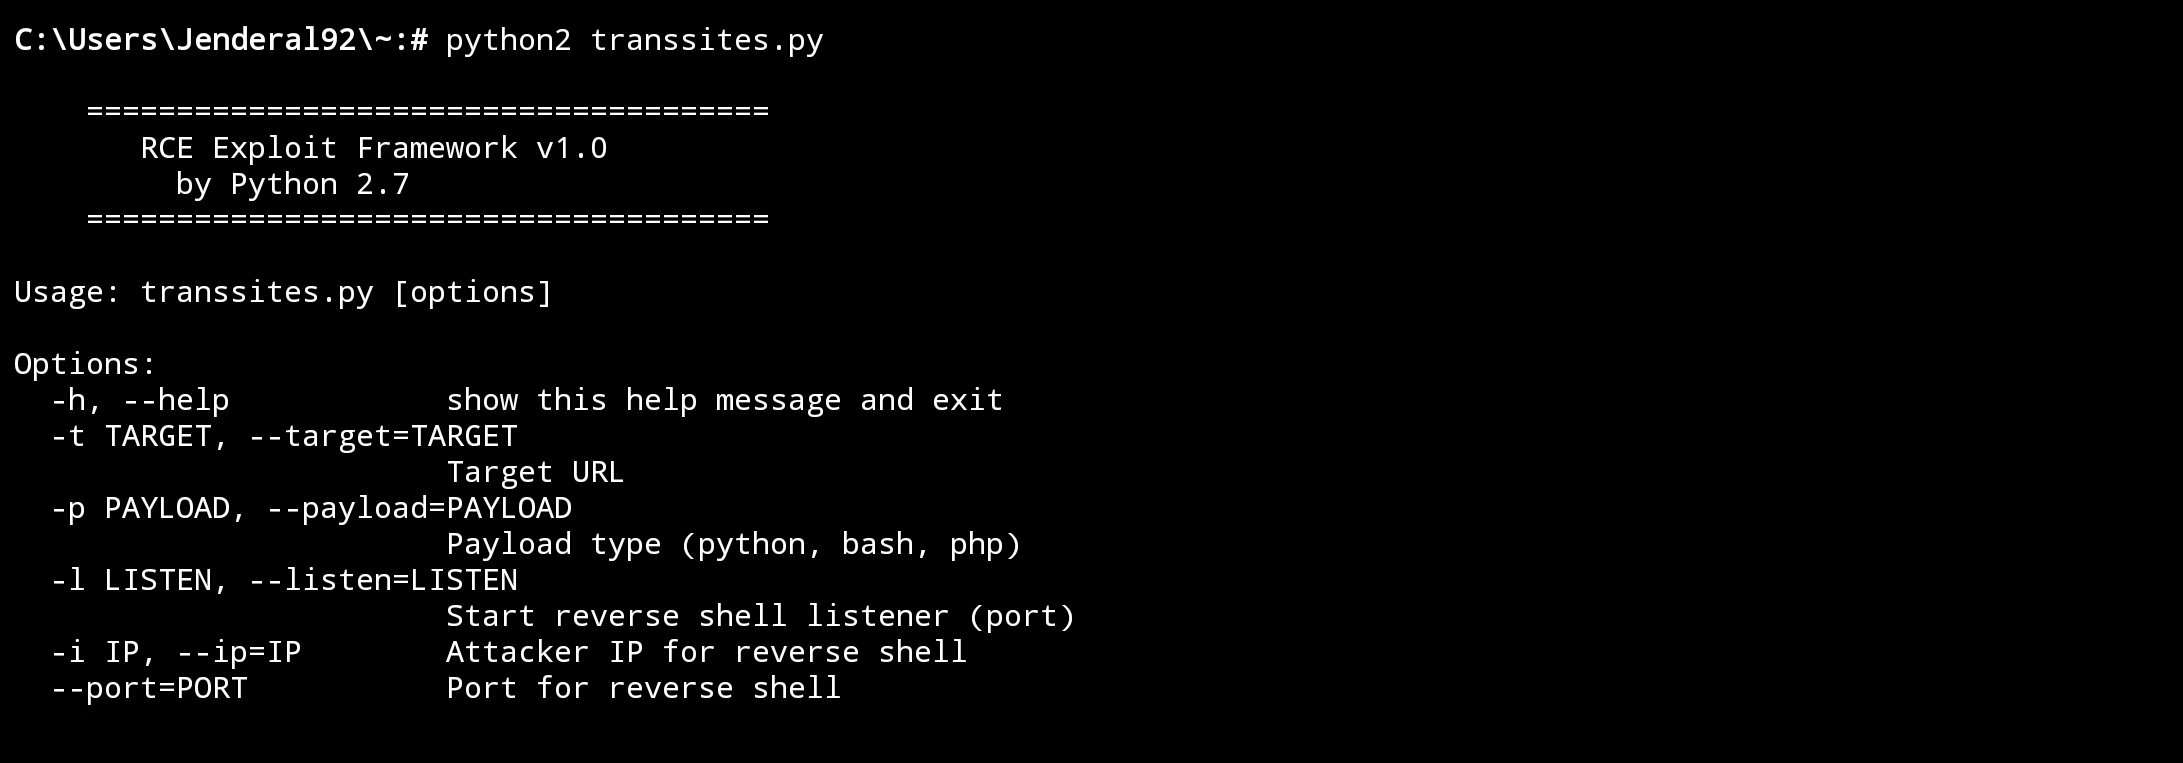 jenderal92/rce-exploit-framework
This framework is designed to assist penetration testers or developers in understanding the mechanics of remote code execution (RCE) exploitation.
 denchief1/cve-2017-7269
C# implementation of CVE-2017-7269 exploit for Microsoft IIS WebDAV remote code execution. Designed for penetration testing and vulnerability…
 rastating/wordpress-exploit-framework
A Ruby framework designed to aid in the penetration testing of WordPress systems.
 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.