

Invoke-CradleCrafter
 danielbohannon/invoke-cradlecrafter
PowerShell Remote Download Cradle Generator & Obfuscator
command-and-controldefensive-toolspayload-development+3
854
danielbohannon/invoke-cradlecrafterPowerShell Remote Download Cradle Generator & Obfuscator
 virtualalllocex/payload-download-cradles
This are different types of download cradles which should be an inspiration to play and create new download cradles to bypass AV/EPP/EDR in context…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
 0xhaggis/cve-2021-44168
A download of code without integrity check vulnerability in the "execute restore src-vis" command of FortiOS before 7.0.3.
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 calumhutton/cve-2022-22965-poc_payara
Proof-of-concept exploit for CVE-2022-22965 in Payara/Glassfish, demonstrating arbitrary file download via web root manipulation. Includes Docker…
 edubr2020/rp_import_rce
Proof-of-concept exploit for RealPlayer arbitrary file download and directory traversal leading to remote code execution via Import() method.
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 defhacks/cve-2021-4034
Rust implementation of the CVE-2021-4034 pkexec privilege escalation exploit, with scripts to download and unpack a vulnerable pkexec for testing.
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
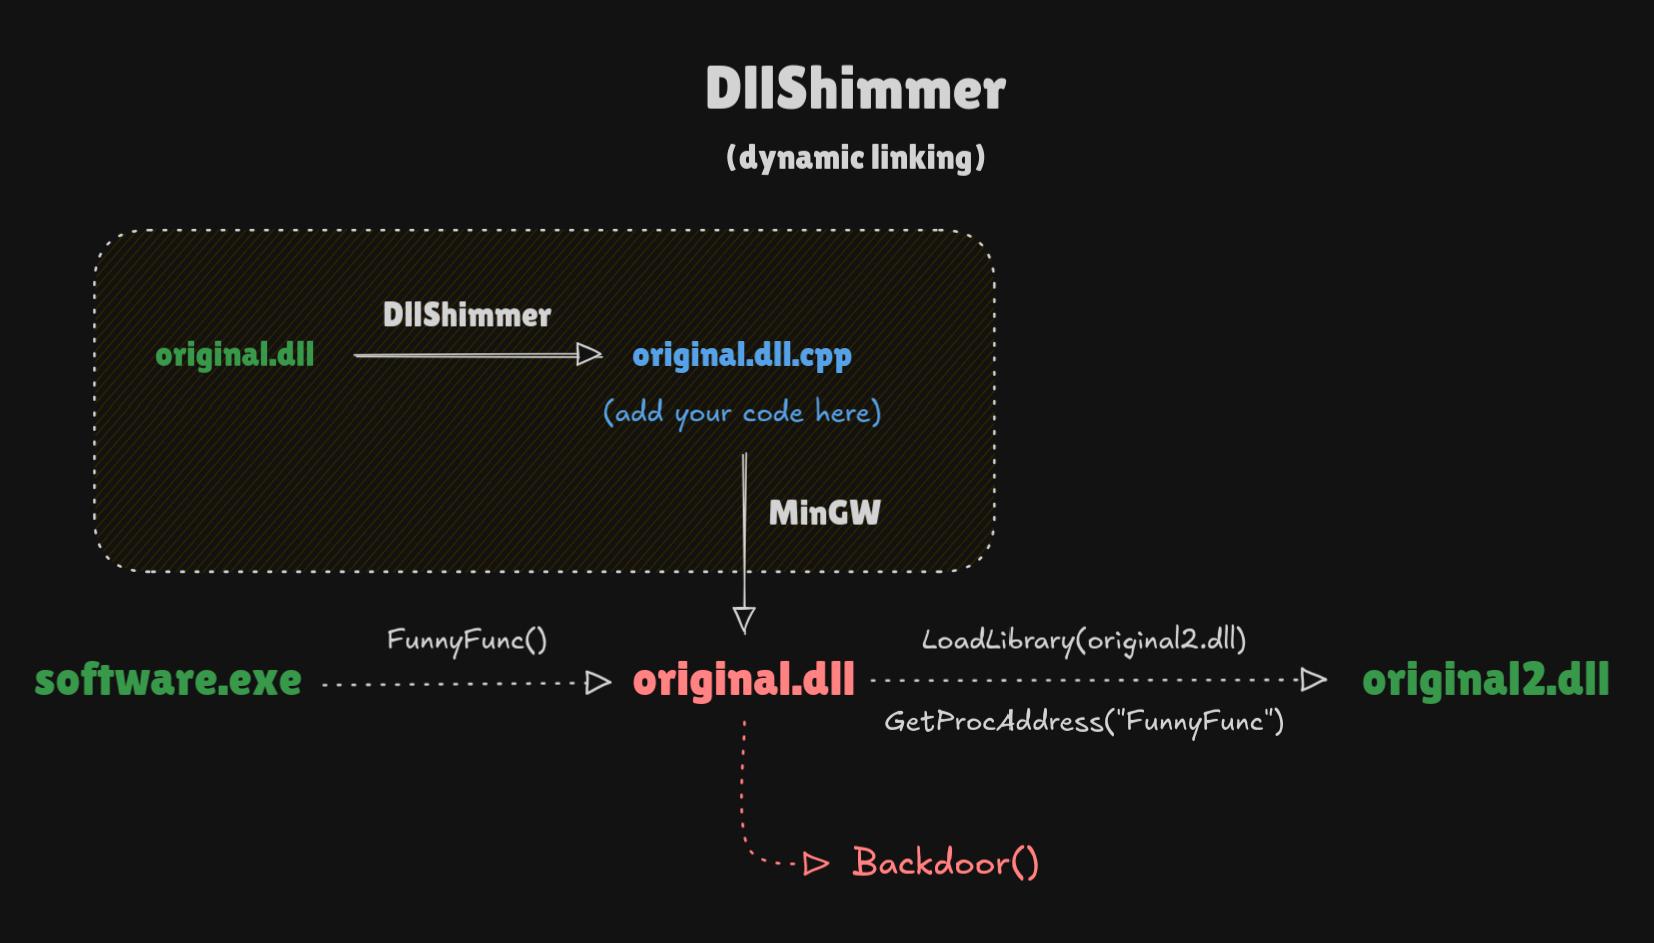 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 w01fh4cker/cve-2025-30406
Exploit for CVE-2025-30406
 bo0l3an/cve-2024-49112-poc
CVE-2024-49112 LDAP RCE PoC and Metasploit Module
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node