metasploit_in_termux

Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…

Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…

Proof of concept for CVE-2022-1364 against Alibaba's UC Browser

Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…

Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.

Novell ZENworks Mobile Management - LFI RCE

Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration

The patching of Android kernel and Android system

Patching and hooking the Linux kernel with only a stripped Linux kernel image.

KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499

Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…

Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…

Python script to inject existing Android applications with a Meterpreter payload.

Android Remote Access Trojan

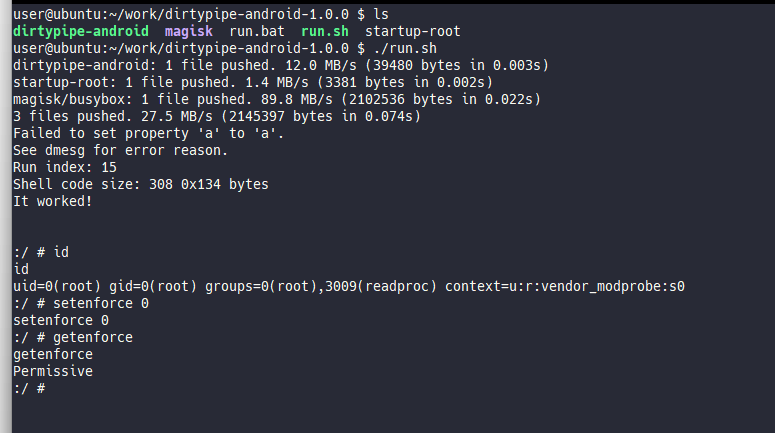
Dirty Pipe root exploit for Android (Pixel 6)

My first Android app: Launch Fusée Gelée payloads from stock Android (CVE-2018-6242)

A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models