
MacroShop
 khr0x40sh/macroshop
Collection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.
payload-developmentpayload-generationpenetration-testing+2
408
khr0x40sh/macroshopCollection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 kushiro45/metabase-cve-2023-38646
Repo contains the PoC and steps to reproduce cve 2023-38646
 silentsignal/cve-2023-30990
CVE-2023-30990 exploits
 ravss/eaton-ups-companion-exploit
This repository details CVE-2020-6650, a vulnerability I discovered within Eaton's UPS Companion. All users should upgrade to v1.06 immediately or…
 d3vn0mi/cve-2025-60787-poc
Python PoC for CVE-2025-60787, authenticated OS command injection RCE in motionEye <= 0.43.1b4 via unsanitized image_file_name config
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 otofoto/cve-2010-5230
Multiple untrusted search path vulnerabilities in MicroStation 7.1 allow local users to gain privileges via a Trojan horse (1) mptools.dll, (2)…
 brianwrf/wordpress_4.9.8_rce_poc
A simple PoC for WordPress RCE (author priviledge), refer to CVE-2019-8942 and CVE-2019-8943.
 ally-petitt/cve-2024-48990-exploit
My exploit for CVE-2024-48990. Full details of how I made this are on my blog.
 azefzafyoussef/cve-2026-33229
Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.
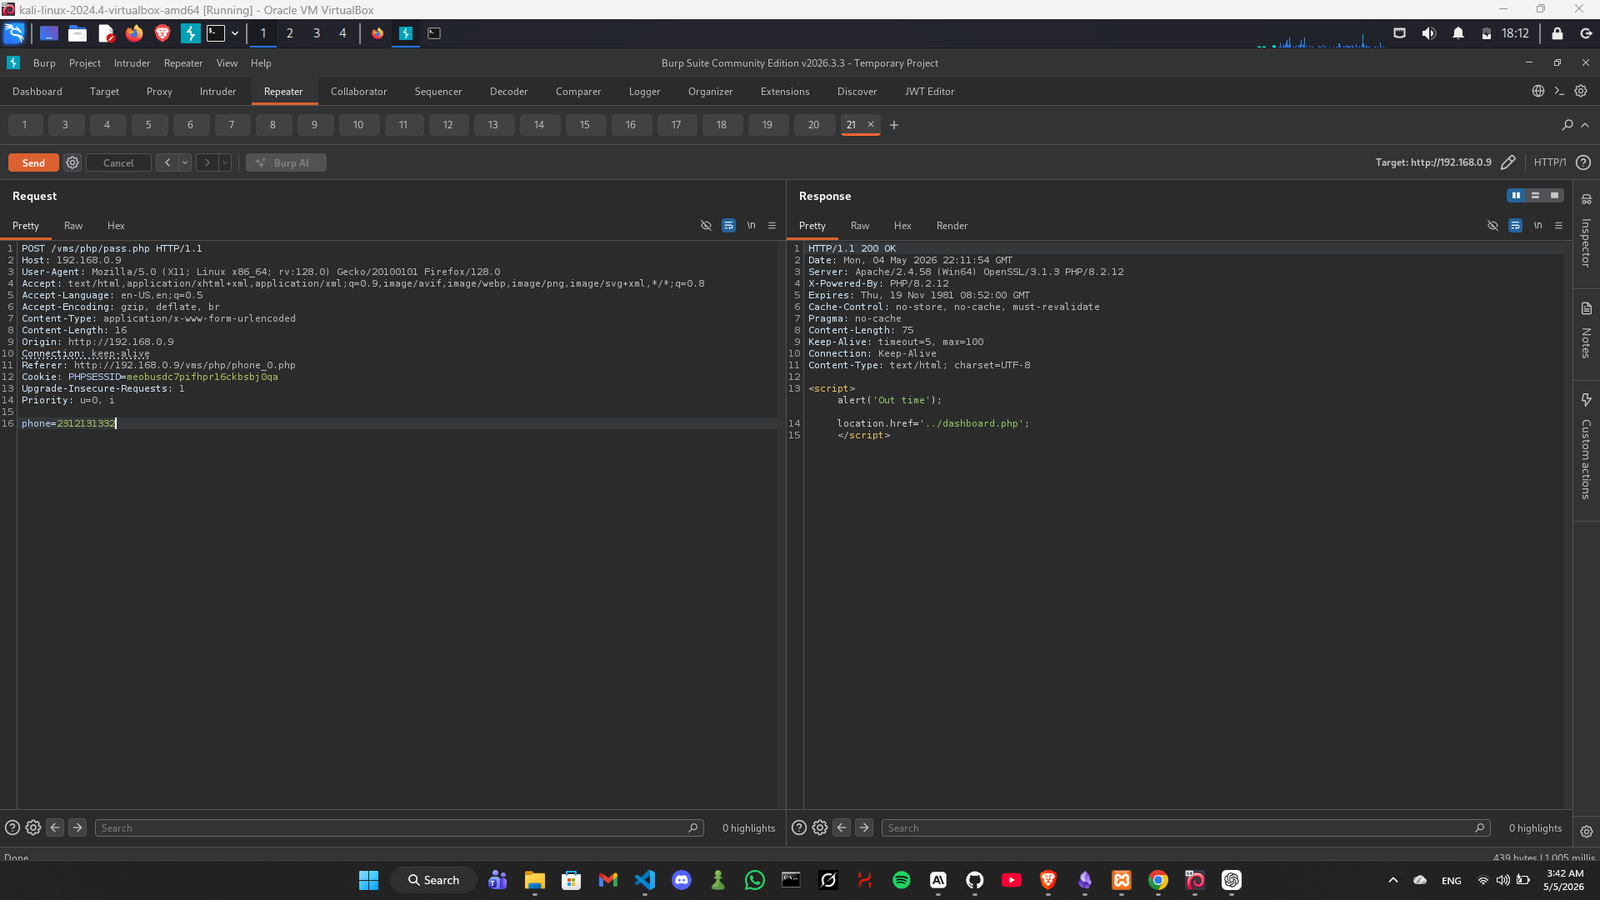 xmyronn/cve-2026-10170-rce
Proof-of-concept demonstrating SQL injection and unrestricted file upload chained to achieve remote code execution in Visitor Management System 1.0,…
 machevalia/cve-2024-0692-solarwinds-sem-rce
Proof-of-concept exploit for CVE-2024-0692 targeting SolarWinds SEM, developed from penetration testing research to demonstrate remote code execution.
 codewhitesec/httpremotingobjrefleak
Additional resources for leaking and exploiting ObjRefs via HTTP .NET Remoting (CVE-2024-29059)
 whattheslime/file-away-exploit
Remote code execution exploit scripts for the WordPress File-Away plugin (CVE-2025-2512 & CVE-2025-2539)
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073
 jarrettgohxz/cve-research
A repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…