

twittor
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
command-and-controlexploitationpayload-development+4
paulsec/twittorA fully featured backdoor that uses Twitter as a C&C server
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 algo7/bluekeep_cve-2019-0708_poc_to_exploit
An Attempt to Port BlueKeep PoC from @Ekultek to actual exploits
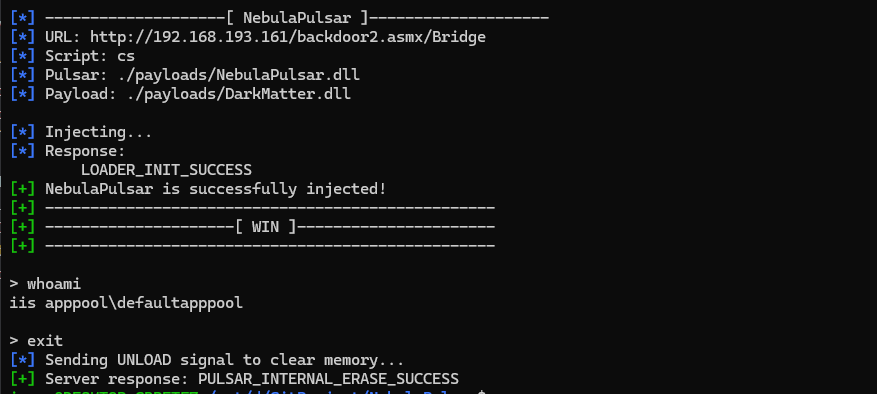 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 baktistr/cve-2025-62726-poc
This is a proof-of-concept demonstration for CVE-2025-62726, created for educational purposes as part of a class project. Part of CMU Course : 18-739…
 threatexpress/malleable-c2
Cobalt Strike Malleable C2 Design and Reference Guide
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 niokagi/react-cve-2025-55182
Test & Analyze the CVE-2025-55182 vulnerability within Next.js Server Actions
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 bend0us/dexloader
A demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 oscerd/cve-2026-33453
Reproducer for CVE-2026-33453: Apache Camel camel-coap header injection to RCE via camel-exec
 oscerd/cve-2026-27172
Reproducer for CVE-2026-27172: Apache Camel camel-consul ConsulRegistry Java deserialization (RCE)