

donut
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
exploitationids-ips-evasionmemory-forensics+7
4.7k
thewover/donutGenerates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
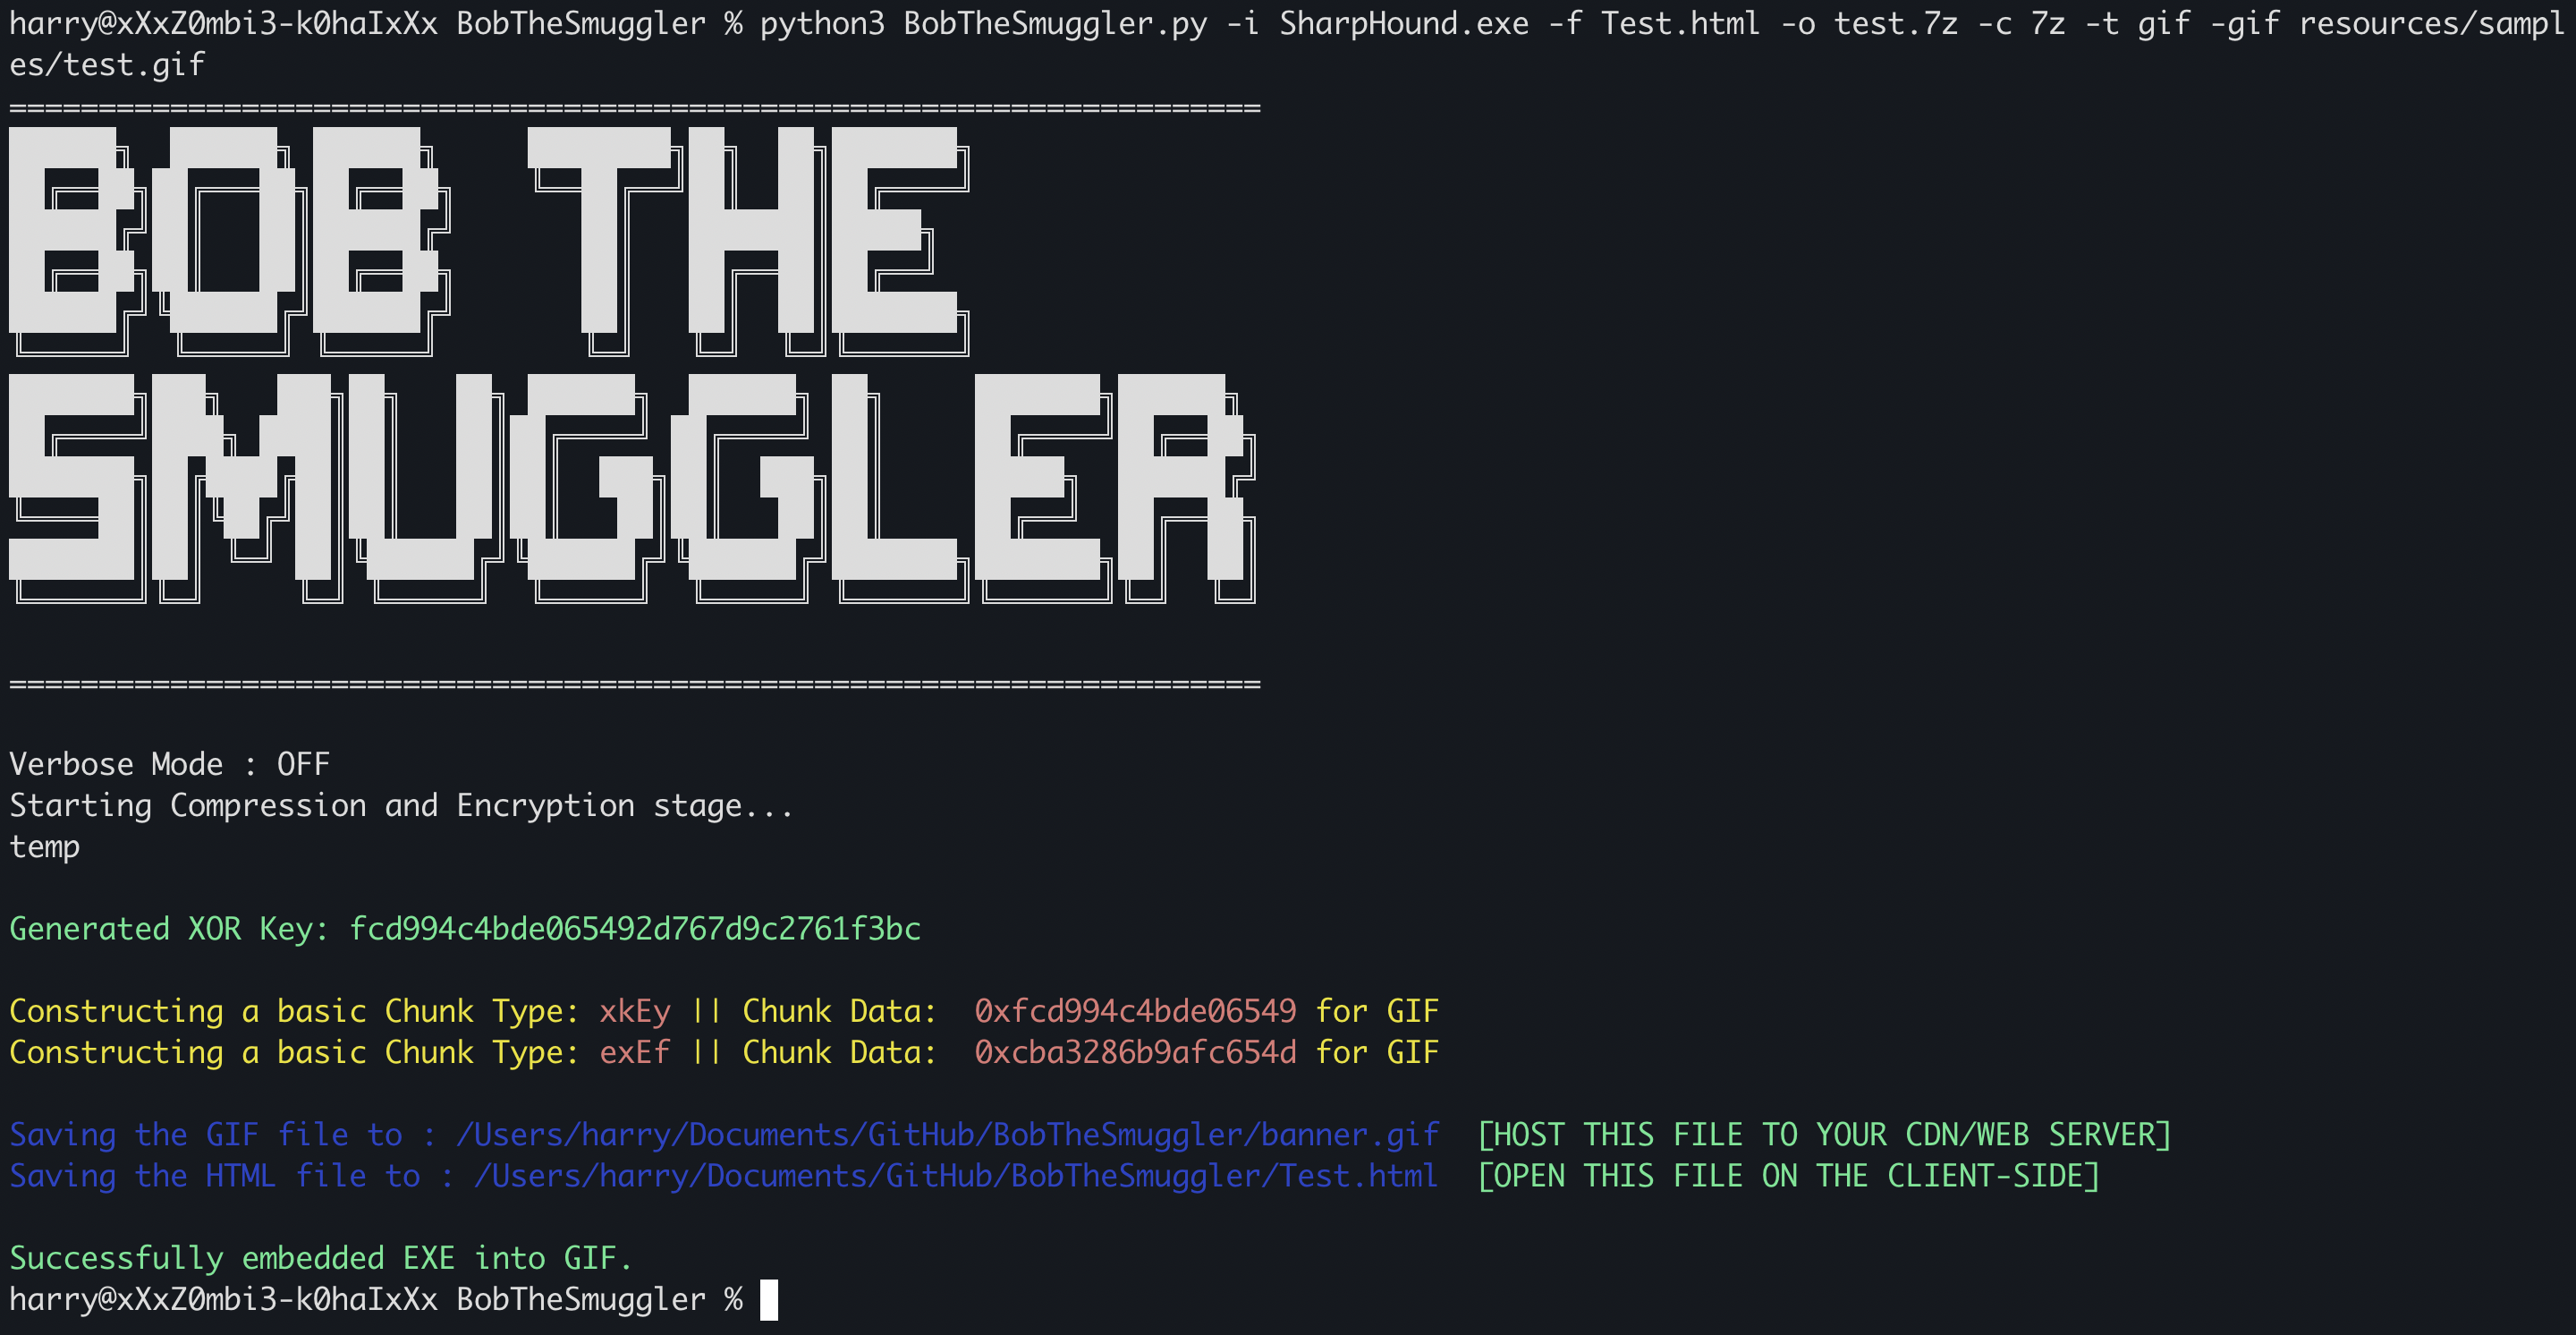 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 hacksysteam/cve-2023-21608
Proof-of-concept exploit for CVE-2023-21608, a Use-After-Free vulnerability in Adobe Acrobat Reader enabling remote code execution via crafted PDF…
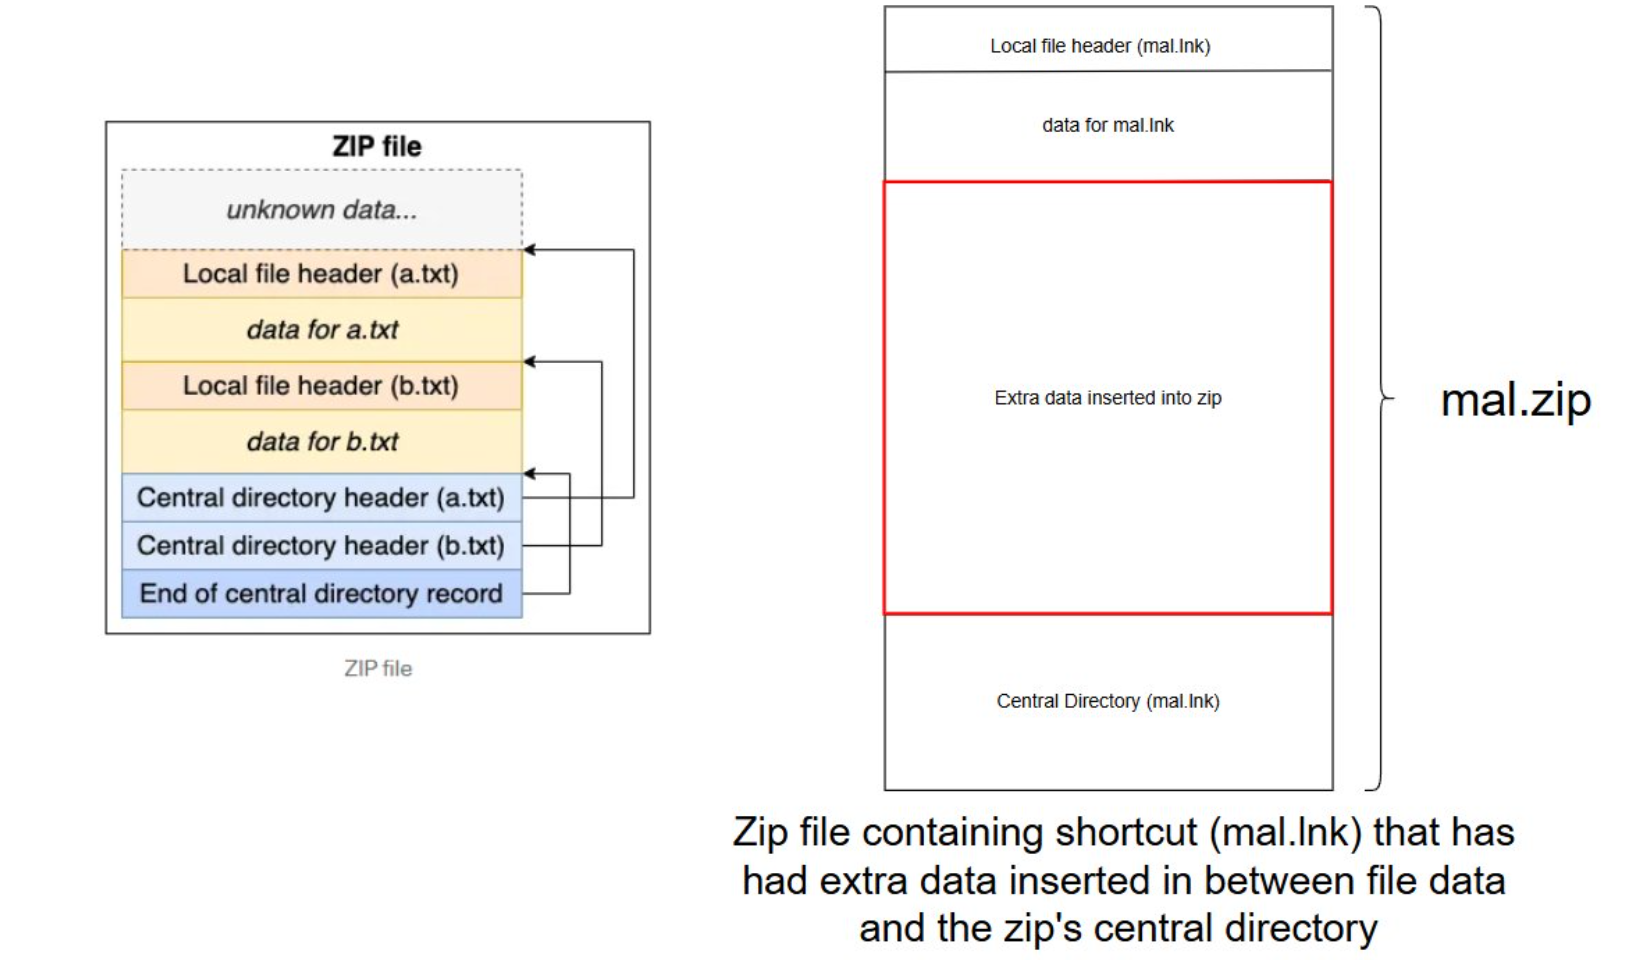 octoberfest7/zip_smuggling
Python3 utility for creating zip files that smuggle additional data for later extraction
 j00sean/cve-2022-44666
Technical write-up and proof-of-concept for CVE-2022-44666, a Windows Contacts syslink control href attribute escape vulnerability enabling remote…
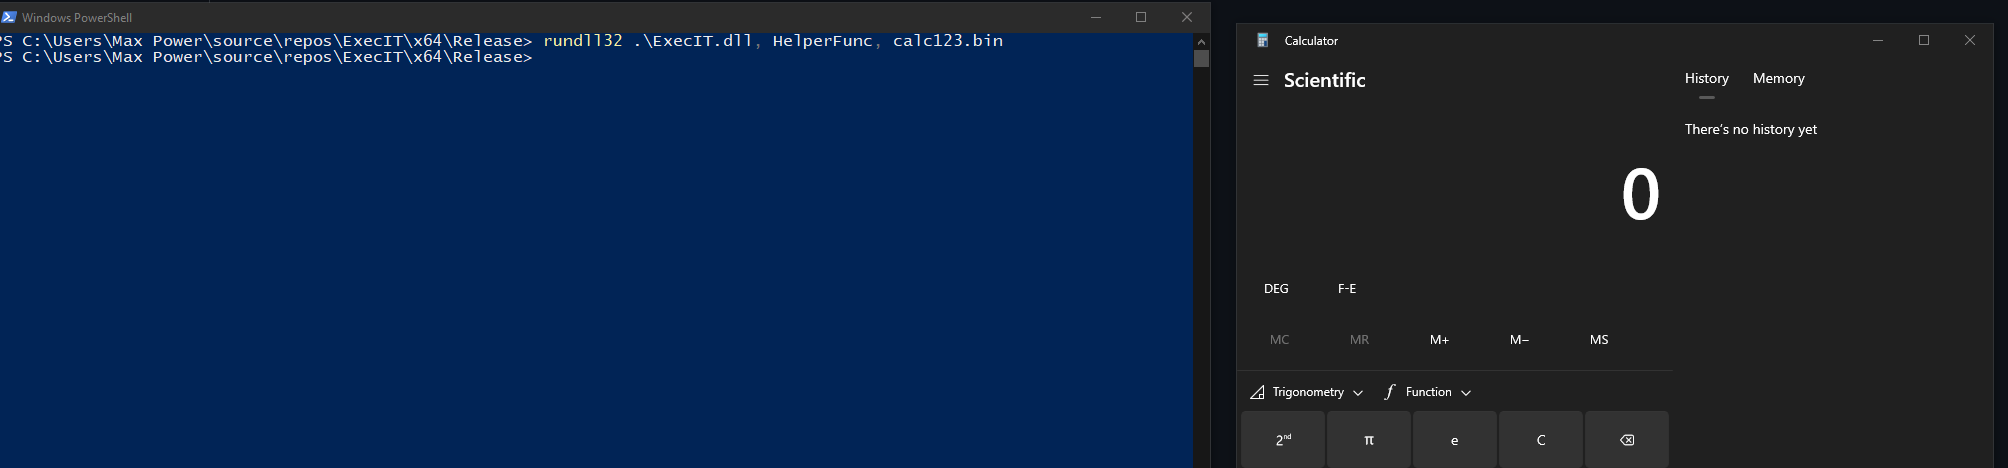 florylsk/execit
Execute shellcode files with rundll32
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 sec-consult/aggrokatz
Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
 lorentzenman/payday
Payload generator that uses Metasploit and Veil. Takes IP address as input and calls Veil. Use msfvenom to create payloads and writes resource…
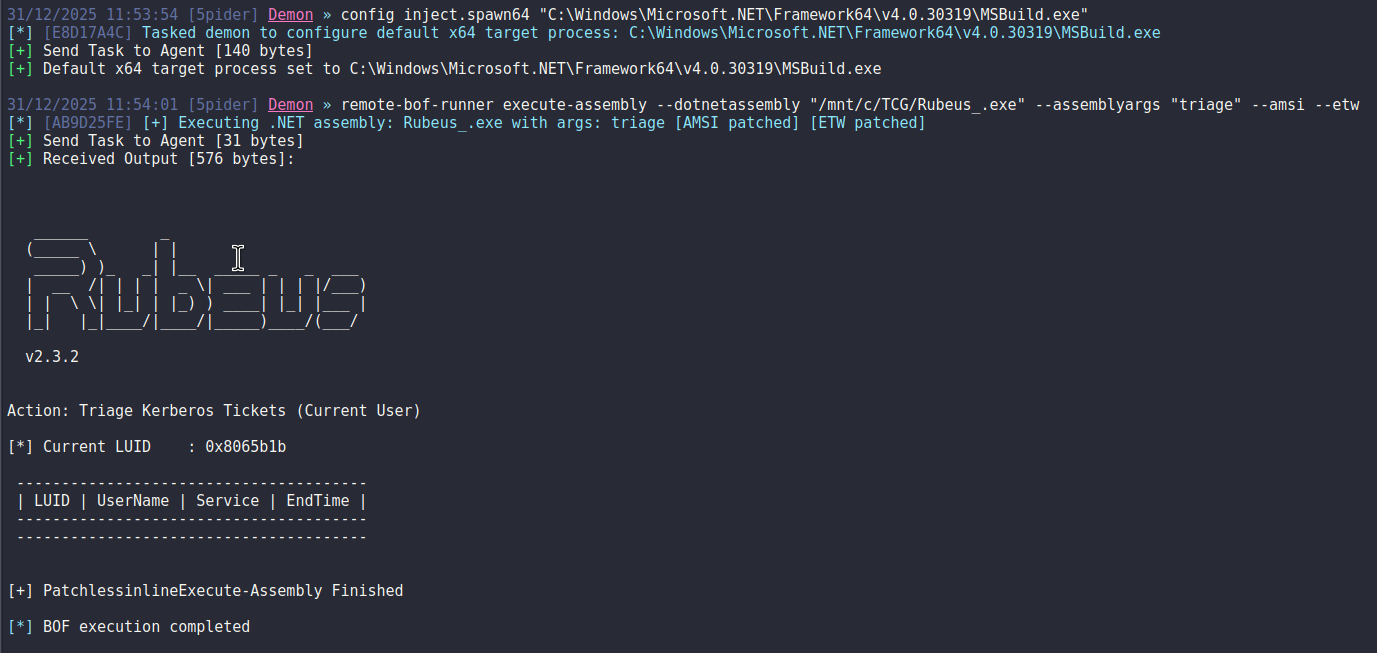 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.