
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
3626 results
geacon preview

geacon

GitHubdarkr4y/geacon

Practice Go programming and implement CobaltStrike's Beacon in Go

command-and-controlexploit-frameworkspayload-development+2
1.3k
5 years ago
SmmBackdoor preview

SmmBackdoor

GitHubcr4sh/smmbackdoor

First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
exploitationfirmware-analysishardware-hacking+4
6322 years ago
WTSRM2 preview

WTSRM2

GitHubrad9800/wtsrm2

Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…
ids-ips-evasionpayload-developmentred-teaming
1633 years ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
binary-analysiseducationlabs-practice+6
1581 year ago
CVE-2018-7600-Drupalgeddon2-RCE preview

CVE-2018-7600-Drupalgeddon2-RCE

GitHubshams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce

Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…

educationexploitationlabs-practice+5
1 month ago
CVE-2025-55182 preview

CVE-2025-55182

GitHubsubhdotsol/cve-2025-55182

This project provides a fully functional demonstration of CVE-2025-55182 (React2Shell) - a critical Remote Code Execution vulnerability in React…
command-and-controleducationexploitation+5
29 months ago
DLL_Injection_On_VLC preview

DLL_Injection_On_VLC

GitHubkobukovui/dll_injection_on_vlc

DLL Injection and CVE-2010-3124
binary-exploitationeducationexploitation+2
12 years ago
CVE-2026-21508_POC preview

CVE-2026-21508_POC

GitHub0xc4r/cve-2026-21508_poc

Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…

binary-exploitationexploitationpayload-development+2
297 months ago
Lime-RAT preview
Archived

Lime-RAT

GitHubnyan-x-cat/lime-rat

LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
command-and-controlcryptographydata-exfiltration+7
1.1k7 years ago
Stealth-Kid-RAT preview

Stealth-Kid-RAT

GitHubartbitrage/stealth-kid-rat

Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
command-and-controleducationpayload-development+3
245 years ago
CVE-2019-12180 preview

CVE-2019-12180

GitHub0x-nope/cve-2019-12180

Advisory and proof of concept for CVE-2019-12180, demonstrating arbitrary Groovy code execution in SoapUI and ReadyAPI via malicious project files.
code-analysisexploitationpayload-development+3
46 years ago
CVE-2023-6401 preview

CVE-2023-6401

GitHubmekitoci/cve-2023-6401

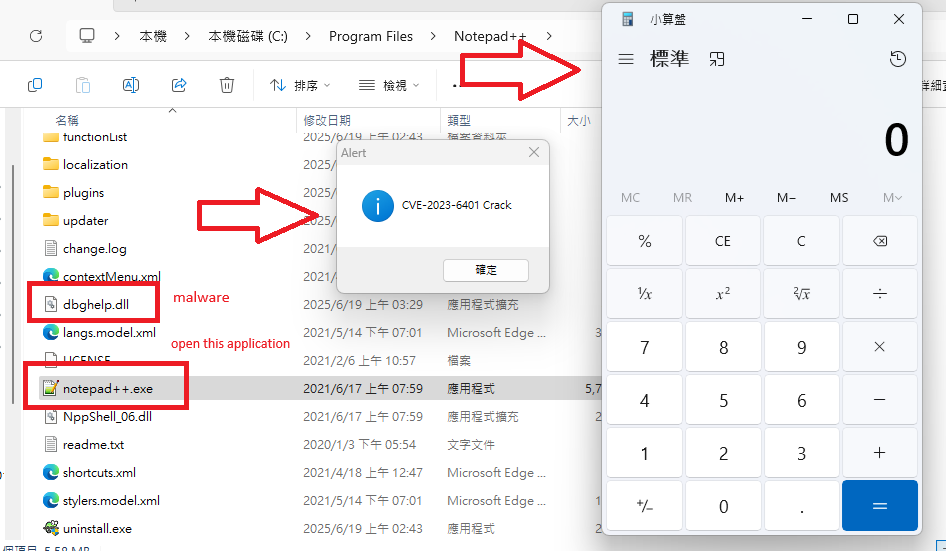
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…
binary-exploitationeducationexploitation+2
1 year ago
malleable-c2 preview

malleable-c2

GitHubthreatexpress/malleable-c2

Cobalt Strike Malleable C2 Design and Reference Guide
command-and-controlcurated-resourceseducation+4
1.8k2 years ago
DSCourier_BOF preview

DSCourier_BOF

GitHuboctoberfest7/dscourier_bof

BOF POC of the DSCourier project / invoking WinGet via COM

command-and-controlexploitationlateral-movement+5
905 months ago
POC-IngressNightmare-CVE-2025-1974 preview

POC-IngressNightmare-CVE-2025-1974

GitHubbiitts/poc-ingressnightmare-cve-2025-1974

Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.

container-securityexploitationpayload-development+3
1 year ago
redamon preview

redamon

GitHubsamugit83/redamon

An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…

ai-securityexploit-frameworkslateral-movement+8
2.5k1 day ago
twittor preview

twittor

GitHubpaulsec/twittor

A fully featured backdoor that uses Twitter as a C&C server
command-and-controlexploitationpayload-development+4
81111 years ago
NullGate preview

NullGate

GitHub0xsch1zo/nullgate

Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.

adversarial-attackencryption-decryption-toolspayload-development+3
1681 year ago
Previous12…100Next