APTs-Adversary-Simulation

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

PoCs and tools for investigation of Windows process execution techniques

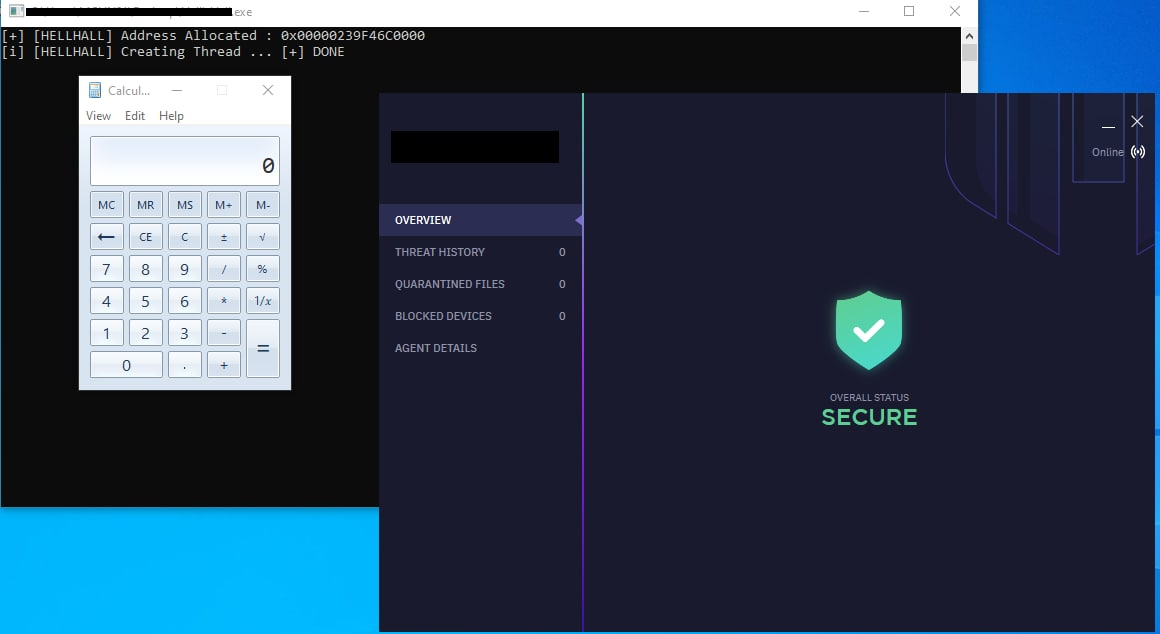
C++ self-Injecting dropper based on various EDR evasion techniques.

Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…

Adversary Emulation Framework

Automated Adversary Emulation Platform

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Adversary simulation and Red teaming platform with AI

Loading Remote AES Encrypted PE in memory , Decrypted it and run it

During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…

Performing Indirect Clean Syscalls

Threadless Process Injection using remote function hooking.

An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

This repo contains C/C++ snippets that can be handy in specific offensive scenarios.

Evasion kit for Cobalt Strike

A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…