BIT-EternalBlue-for-macOS_Linux

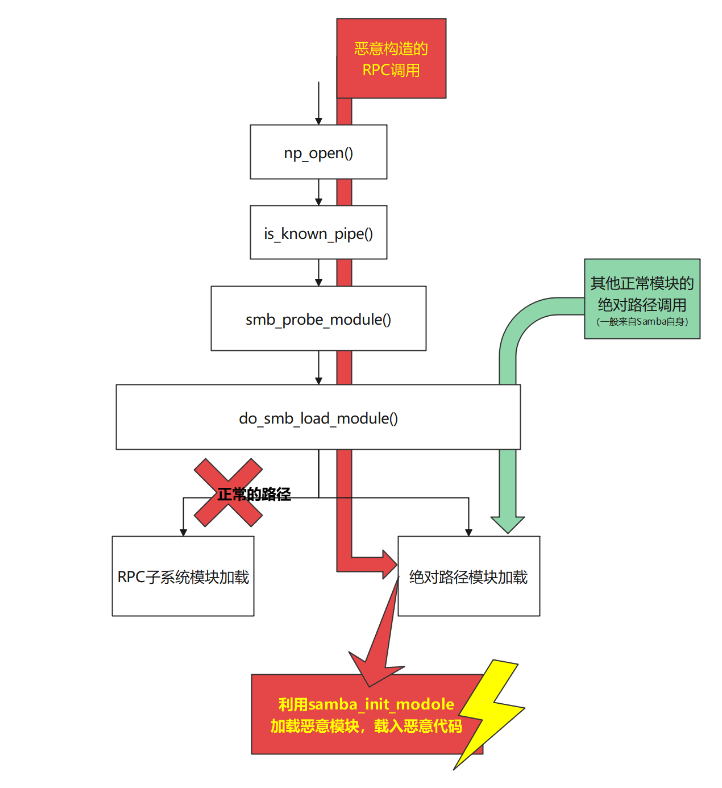
Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…

Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…

Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…

Data-only local privilege escalation exploit for Linux kernel io_uring CVE-2024-0582, using sprayed file structures and ext4_file_operations hooks to…

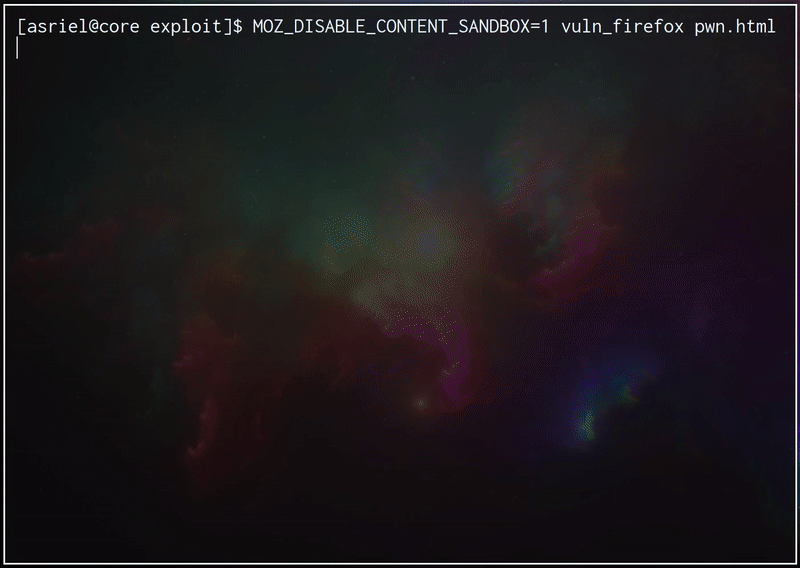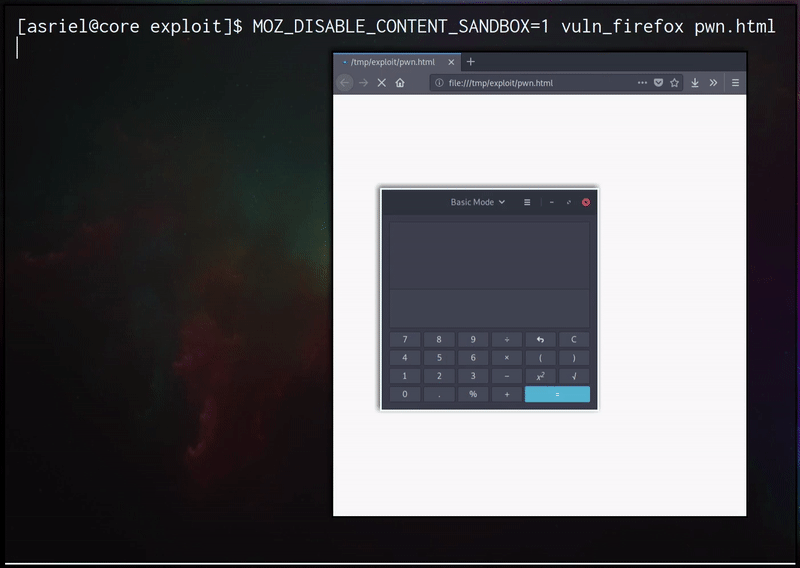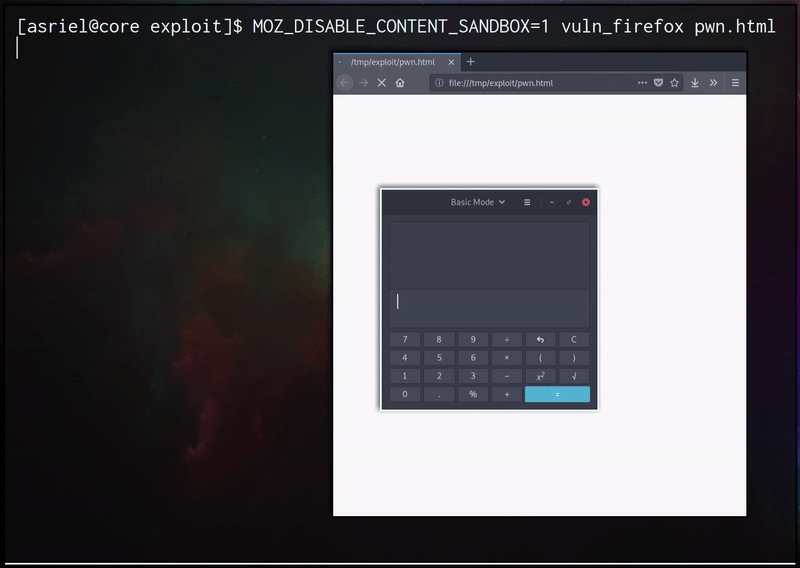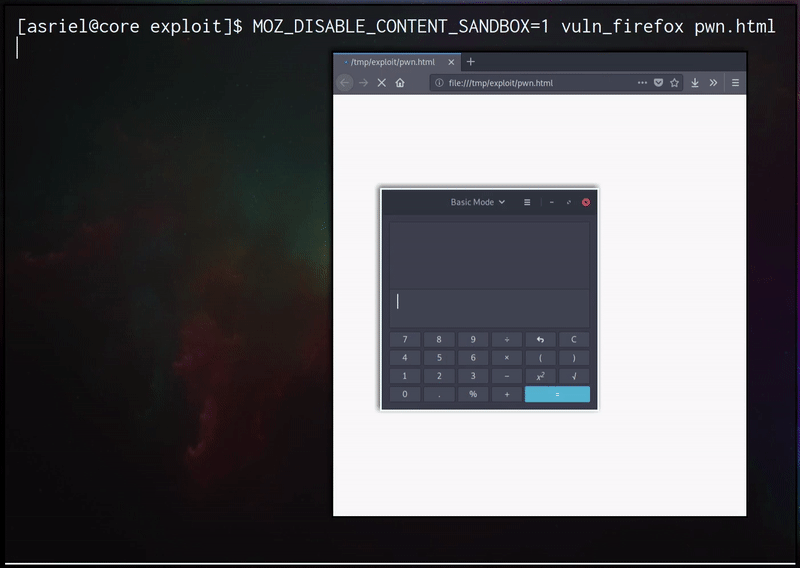
CVE-2018-12386 - Firefox Sandboxed RCE Exploit for Linux (Firefox <v62.0.3)

CVE-2018-12386 - Firefox Sandboxed RCE Exploit for Linux (Firefox <v62.0.3)

Proof-of-concept exploit for Linux kernel CVE-2026-31431, leveraging AF_ALG sockets to escalate privileges to root via payload injection and shell…

Educational Go implementation of a Linux syscall-based exploit for CVE-2026-31431, demonstrating payload crafting and PTY upgrade techniques for…

Sudo Baron Samedit Exploit

Exploit for CVE-2021-4034 (PwnKit) that leverages a race condition in pkexec to escalate privileges to root on Linux systems.

Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.

Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…

Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying

Proof-of-concept exploit for CVE-2024-0582, a Linux kernel vulnerability. Leverages io_uring for buffer manipulation, KASLR leak, and privilege…

Go implementation of the PwnKit Linux Local Privilege Escalation exploit (CVE-2021-4034)

Proof-of-concept exploit for CVE-2015-1805, a Linux kernel vulnerability enabling local privilege escalation via a race condition in the pipe buffer…

ARM32 Linux kernel privilege escalation exploit for CVE-2026-43499 (GhostLock futex UAF) targeting Huawei Watch 4 Pro with multiple exploitation…

Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.

PoC shell exploit for CVE-2026-31431 (copy_fail) — Linux LPE via AF_ALG + splice page-cache overwrite. Single-shot, no race condition, kernel…