
CVE-2025-5548
 elrajiii/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0
binary-exploitationdebuggerseducation+8
elrajiii/cve-2025-5548Buffer overflow in FreeFloat FTP Server 1.0
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 kaleth4/cve-2025-60751
Technical analysis and professional exploit for CVE-2025-60751, a stack-based buffer overflow in GeographicLib. Includes a pwntools-based Ret2Libc…
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
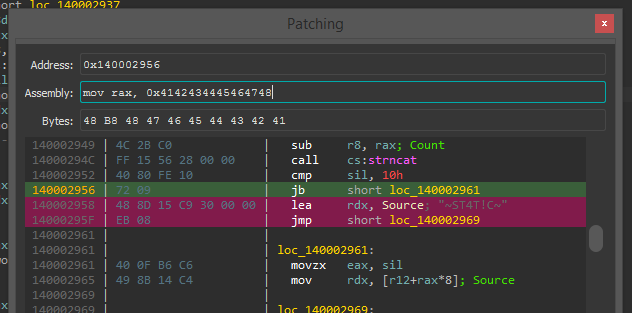 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
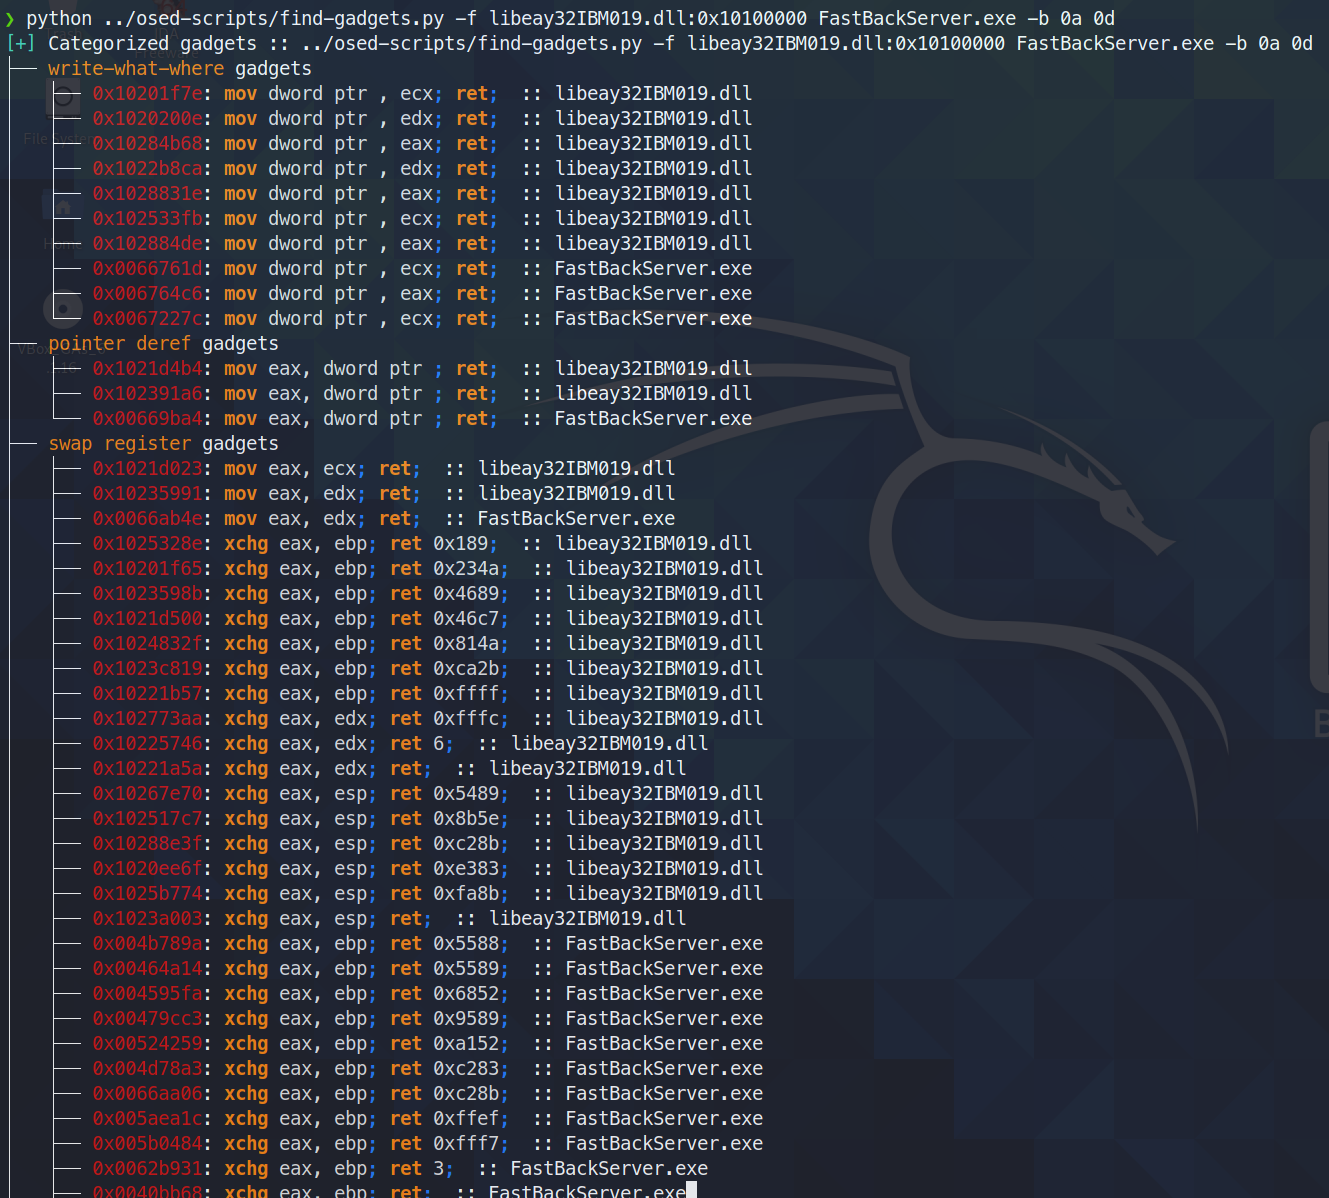 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…

 t00sh/rop-tool
A tool to help you write binary exploits
 lloydlabs/wsb-detect
wsb-detect enables you to detect if you are running in Windows Sandbox ("WSB")
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode