
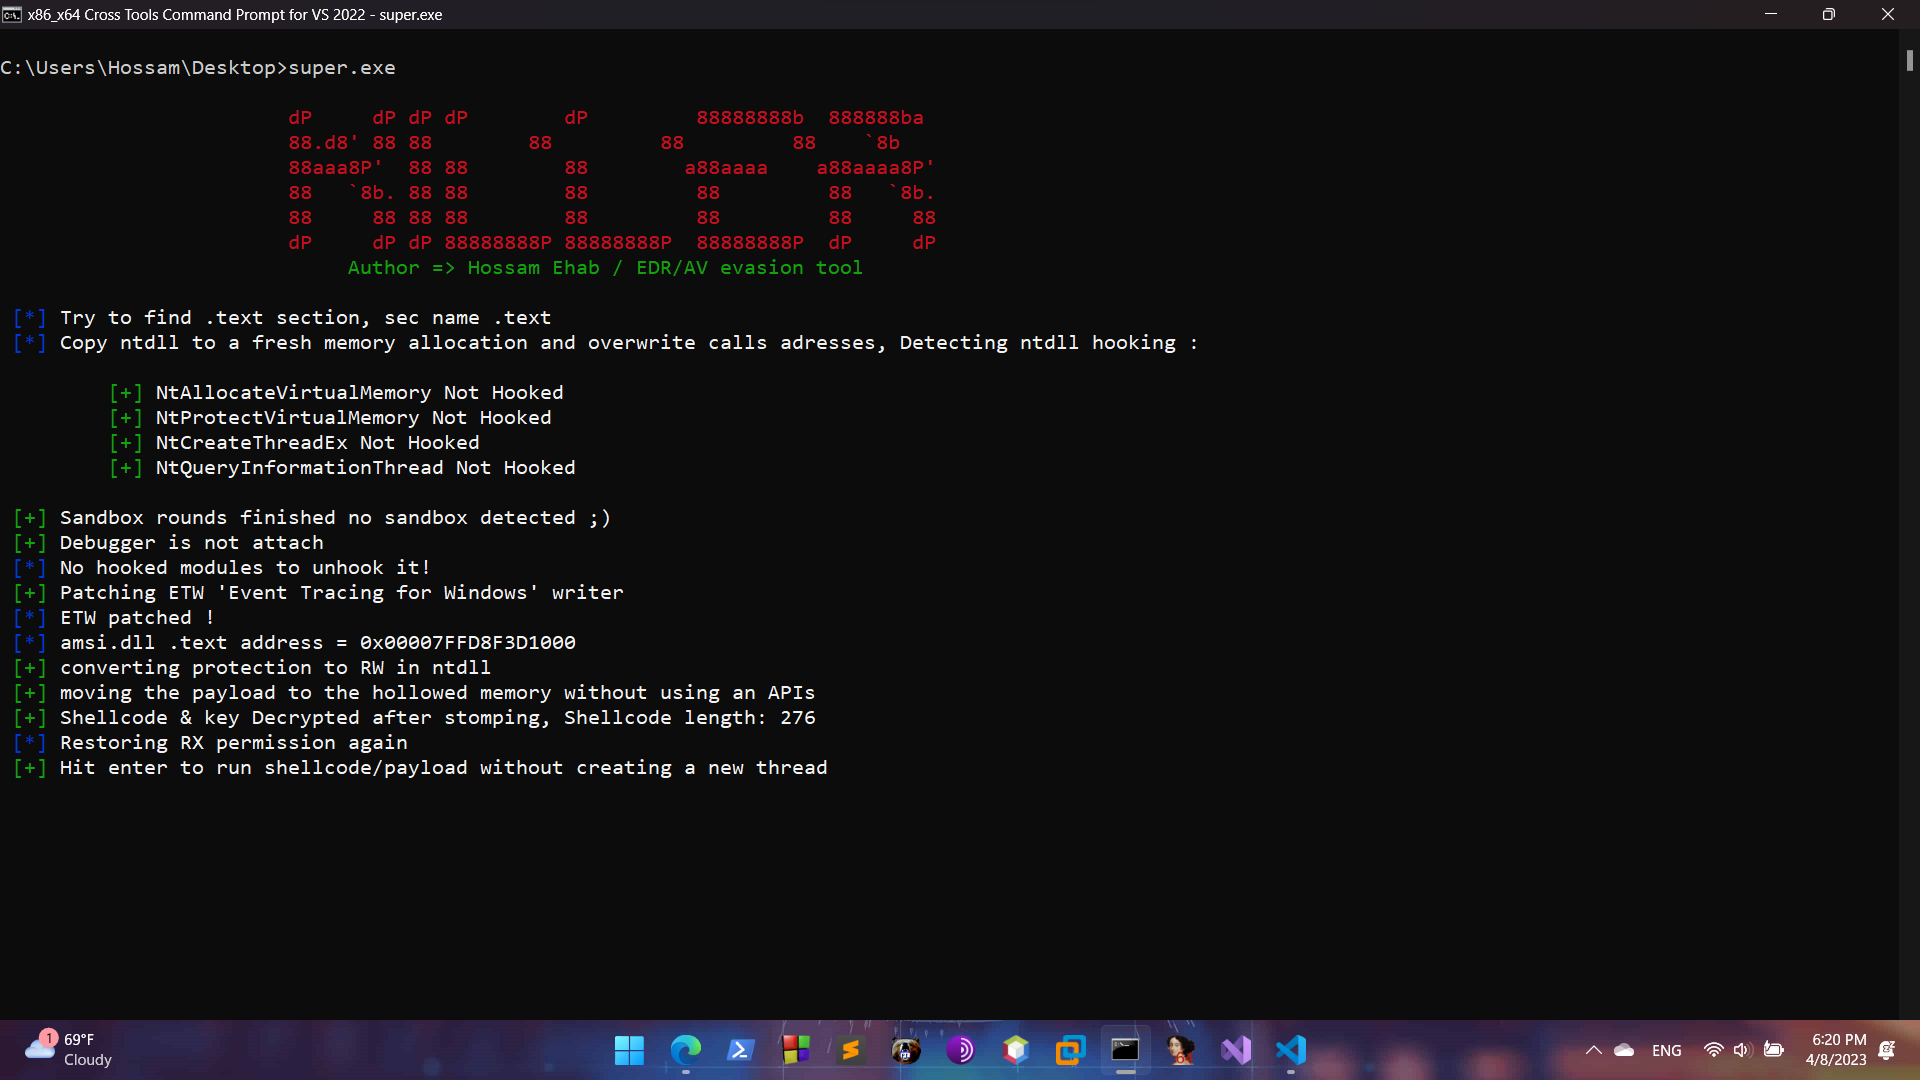
Killer
 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
anti-boteducationexploitation+4
8432 years ago
0xhossam/killerKiller is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 romanc9/gui-poc-test
A testing tool for CobaltStrike-RCE:CVE-2022-39197; Weblogic-RCE:CVE-2023-21839; MinIO:CVE-2023-28432
 wra7h/flavortown
Various ways to execute shellcode
 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
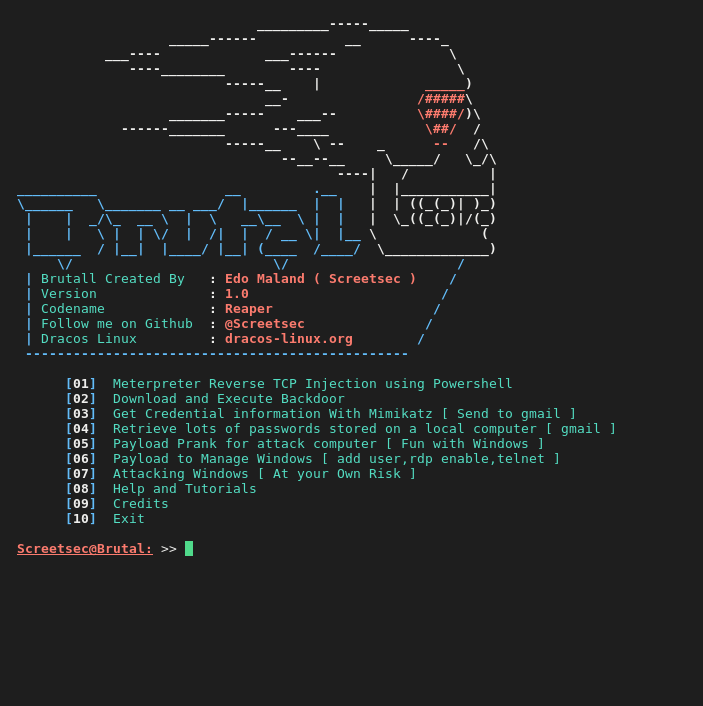 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 forrest-orr/exploitdev
Various tools, PoCs and experiments related to my blog at https://www.forrest-orr.net/
 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 bkup/slackshell
PowerShell to Slack C2
 0xqrx/vulnerabilityresearch
Collection of vulnerability research write-ups and proof-of-concept exploit scripts for educational and research purposes.
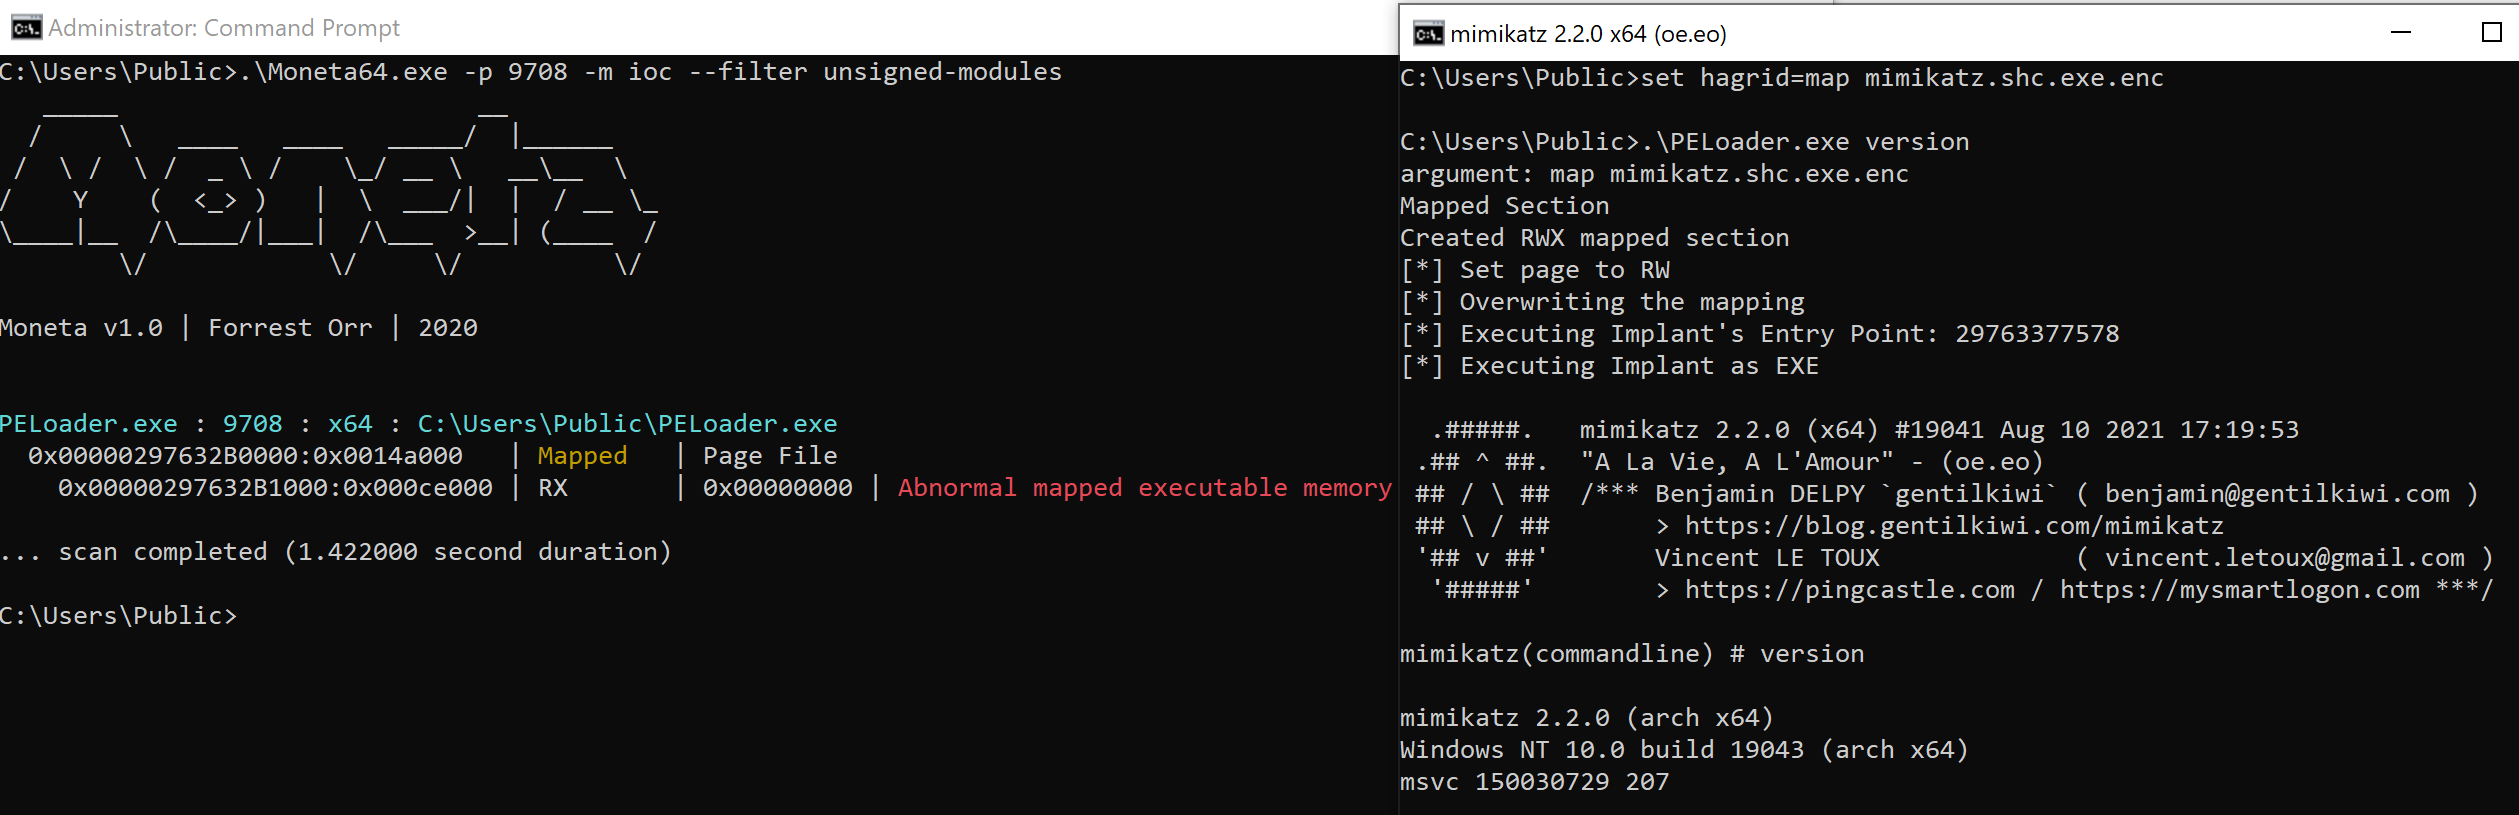 hagrid29/peloader
PE loader with various shellcode injection techniques
 harness-security-labs/cve-2025-55182-checker
Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…
 oscerd/process-injection-playground
A collection of samples and material related to process injection
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 byt3bl33d3r/pymalleablec2
Python interpreter for Cobalt Strike Malleable C2 Profiles. Allows you to parse, build and modify them programmatically.
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE
 hussienmisbah/exploits
Repository containing exploit scripts for various CVEs, targeting web applications, binaries, and network services, suitable for penetration testing…