

gef
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k
hugsy/gefGEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 rkx1209/cve-2014-1303
CVE-2014-1303 (WebKit Heap based BOF) proof of concept for Linux
 outflanknl/evilclippy
A cross-platform assistant for creating malicious MS Office documents. Can hide VBA macros, stomp VBA code (via P-Code) and confuse macro analysis…
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
 tgies/copy-fail-c
Cross-platform C port of the Copy Fail Linux LPE (CVE-2026-31431). Disclosed 2026-04-29 by Theori / Xint.
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 vulnquest58/dirtyclone-exploit
CVE-2026-46331 — Linux Kernel Local Privilege Escalation TC pedit + IPsec TEE Page Cache Corruption · Affected kernels: ≤ 6.12.9
 geniuszly/cve-2024-0582
Proof-of-concept exploit for CVE-2024-0582, a Linux kernel vulnerability. Leverages io_uring for buffer manipulation, KASLR leak, and privilege…
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 4xura/cve-2026-31431-copy-fail
Research artifacts, PoC scripts, and lab assets for the Copy Fail Linux local privilege escalation writeup on https://4xura.com/binex/kernel/copy-fail
 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
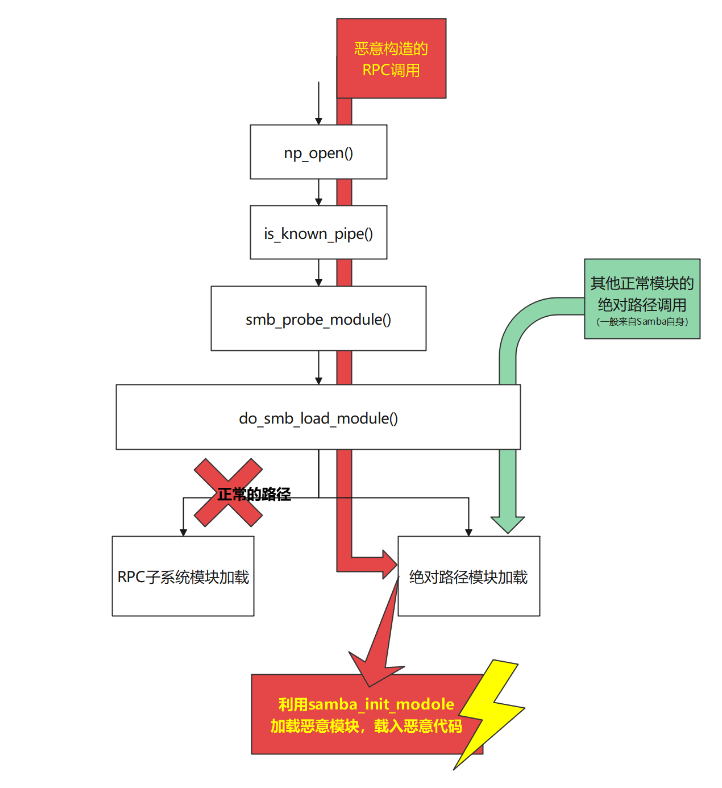 i-rinka/bit-eternalblue-for-macos_linux
Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…
 boos4721/copyfail-rs
Rust exploit for CVE-2026-31431, a Linux kernel page-cache write primitive via AF_ALG splice, enabling privilege escalation to root through…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…