
CVE-2023-2033
 mistymntncop/cve-2023-2033
JavaScript exploit targeting CVE-2023-2033 for proof-of-concept testing and vulnerability validation in web applications.
exploitationpayload-developmentpenetration-testing+2
64
mistymntncop/cve-2023-2033JavaScript exploit targeting CVE-2023-2033 for proof-of-concept testing and vulnerability validation in web applications.
 hussienmisbah/exploits
Repository containing exploit scripts for various CVEs, targeting web applications, binaries, and network services, suitable for penetration testing…
 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
 randomrobbiebf/wp-file-manager
wp-file-manager RCE
 open-flaw/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 targeting Next.js and React applications. Demonstrates vulnerability exploitation in web frameworks for…
 0xh7ml/cve-2026-27626-poc
OliveTin is a self-hosted web UI for exposing predefined shell commands to end users. This repository contains a proof-of-concept demonstrating two…
 mr-xn/cve-2021-42342
Proof-of-concept exploit for CVE-2021-42342, a remote code execution vulnerability in GoAhead web server, demonstrating LD_PRELOAD injection via CGI…
 thelostworldfree/cve-2020-7961-payloads
Deserialization of Untrusted Data in Liferay Portal prior to 7.2.1 CE GA2 allows remote attackers to execute arbitrary code via JSON web services…
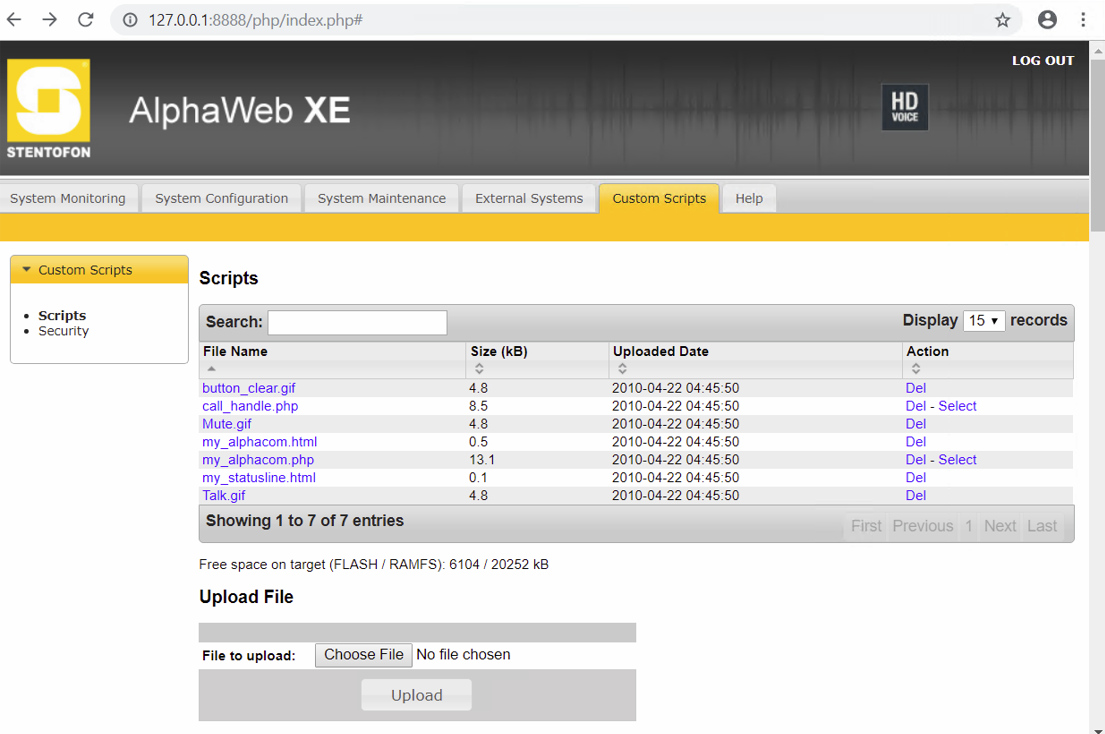 ricardojoserf/cve-2021-40845
AlphaWeb XE, the embedded web server running on AlphaCom XE, has a vulnerability which allows to upload PHP files leading to RCE once the…
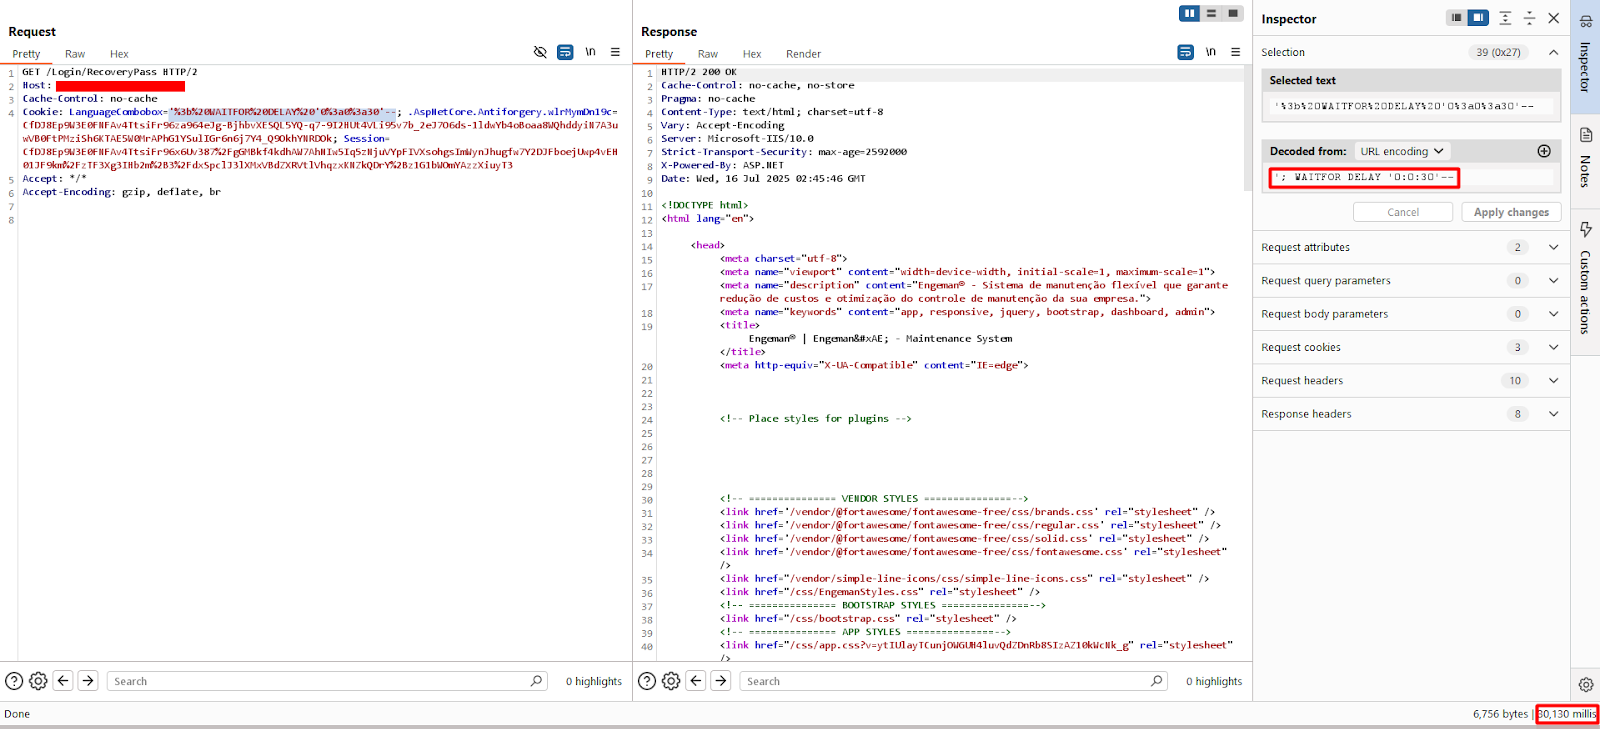 m3m0o/engeman-web-language-combobox-sqli
Proof of concept for exploitation of the vulnerability described in CVE-2025-8220, which concerns the possibility of SQL Injection during the…
 calumhutton/cve-2022-22965-poc_payara
Proof-of-concept exploit for CVE-2022-22965 in Payara/Glassfish, demonstrating arbitrary file download via web root manipulation. Includes Docker…
 0x1nsomnia/cve-2022-36067-vm2-poc-webapp
Proof-of-concept web application demonstrating CVE-2022-36067, a vm2 sandbox escape, enabling remote code execution by uploading exploit code to a…
 fairyming/cve-2019-11043
Proof-of-concept exploit for CVE-2019-11043, a PHP-FPM underflow vulnerability, built on the pocsuite framework for automated web application…
 sangsenimanwartefak/cve-2026-45034
PoC exploit for PHPSpreadsheet's phar:// deserialization vulnerability, bypassing prohibitWrappers to achieve remote code execution on vulnerable PHP…
 kuri119/cve-2022-22965-spring4shell
Exploit for CVE-2022-22965 (Spring4Shell) enabling remote code execution on unpatched Spring Framework applications via crafted HTTP requests.
 harness-security-labs/cve-2025-55182-checker
Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…
 ll104567/cve-2023-5966
Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…